
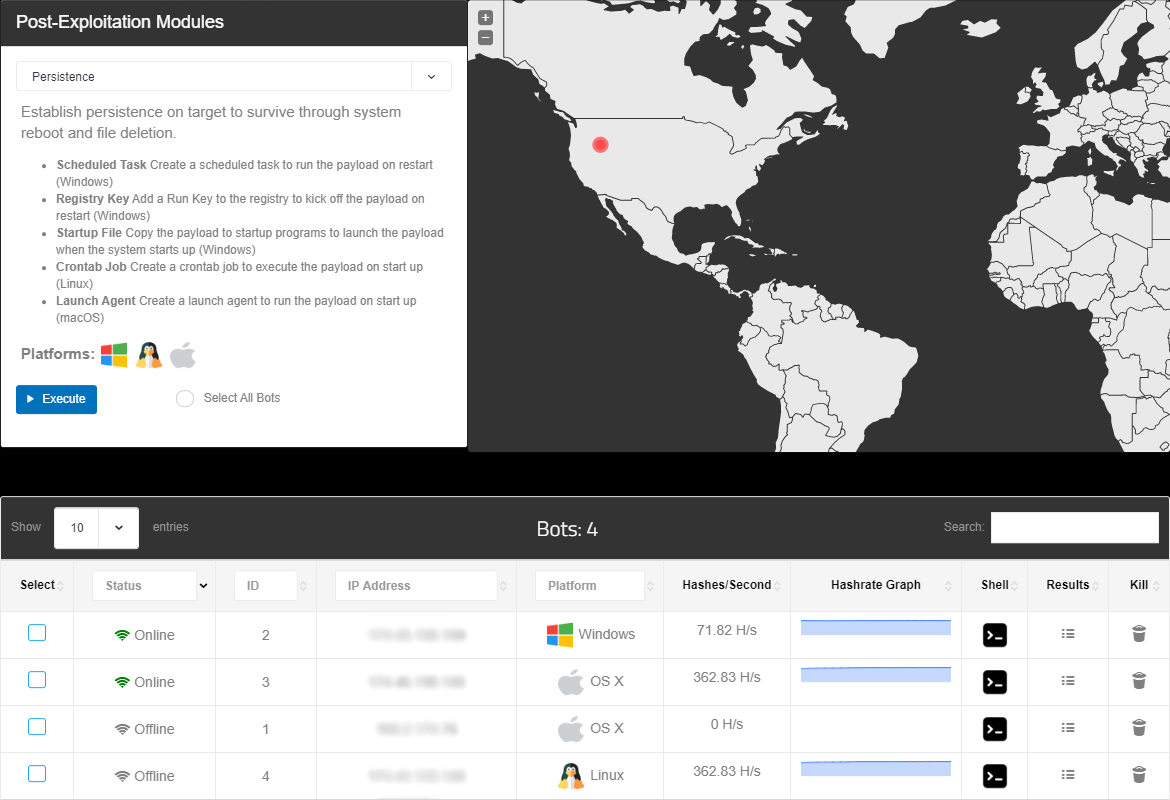
byob
 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
command-and-controleducationpacket-sniffing-analysis+6
9.5k2 years ago
malwaredllc/byobAn open-source post-exploitation framework for students, researchers and developers.
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 cryptogenic/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 al1ex/windowselevation
Windows Elevation(持续更新)
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
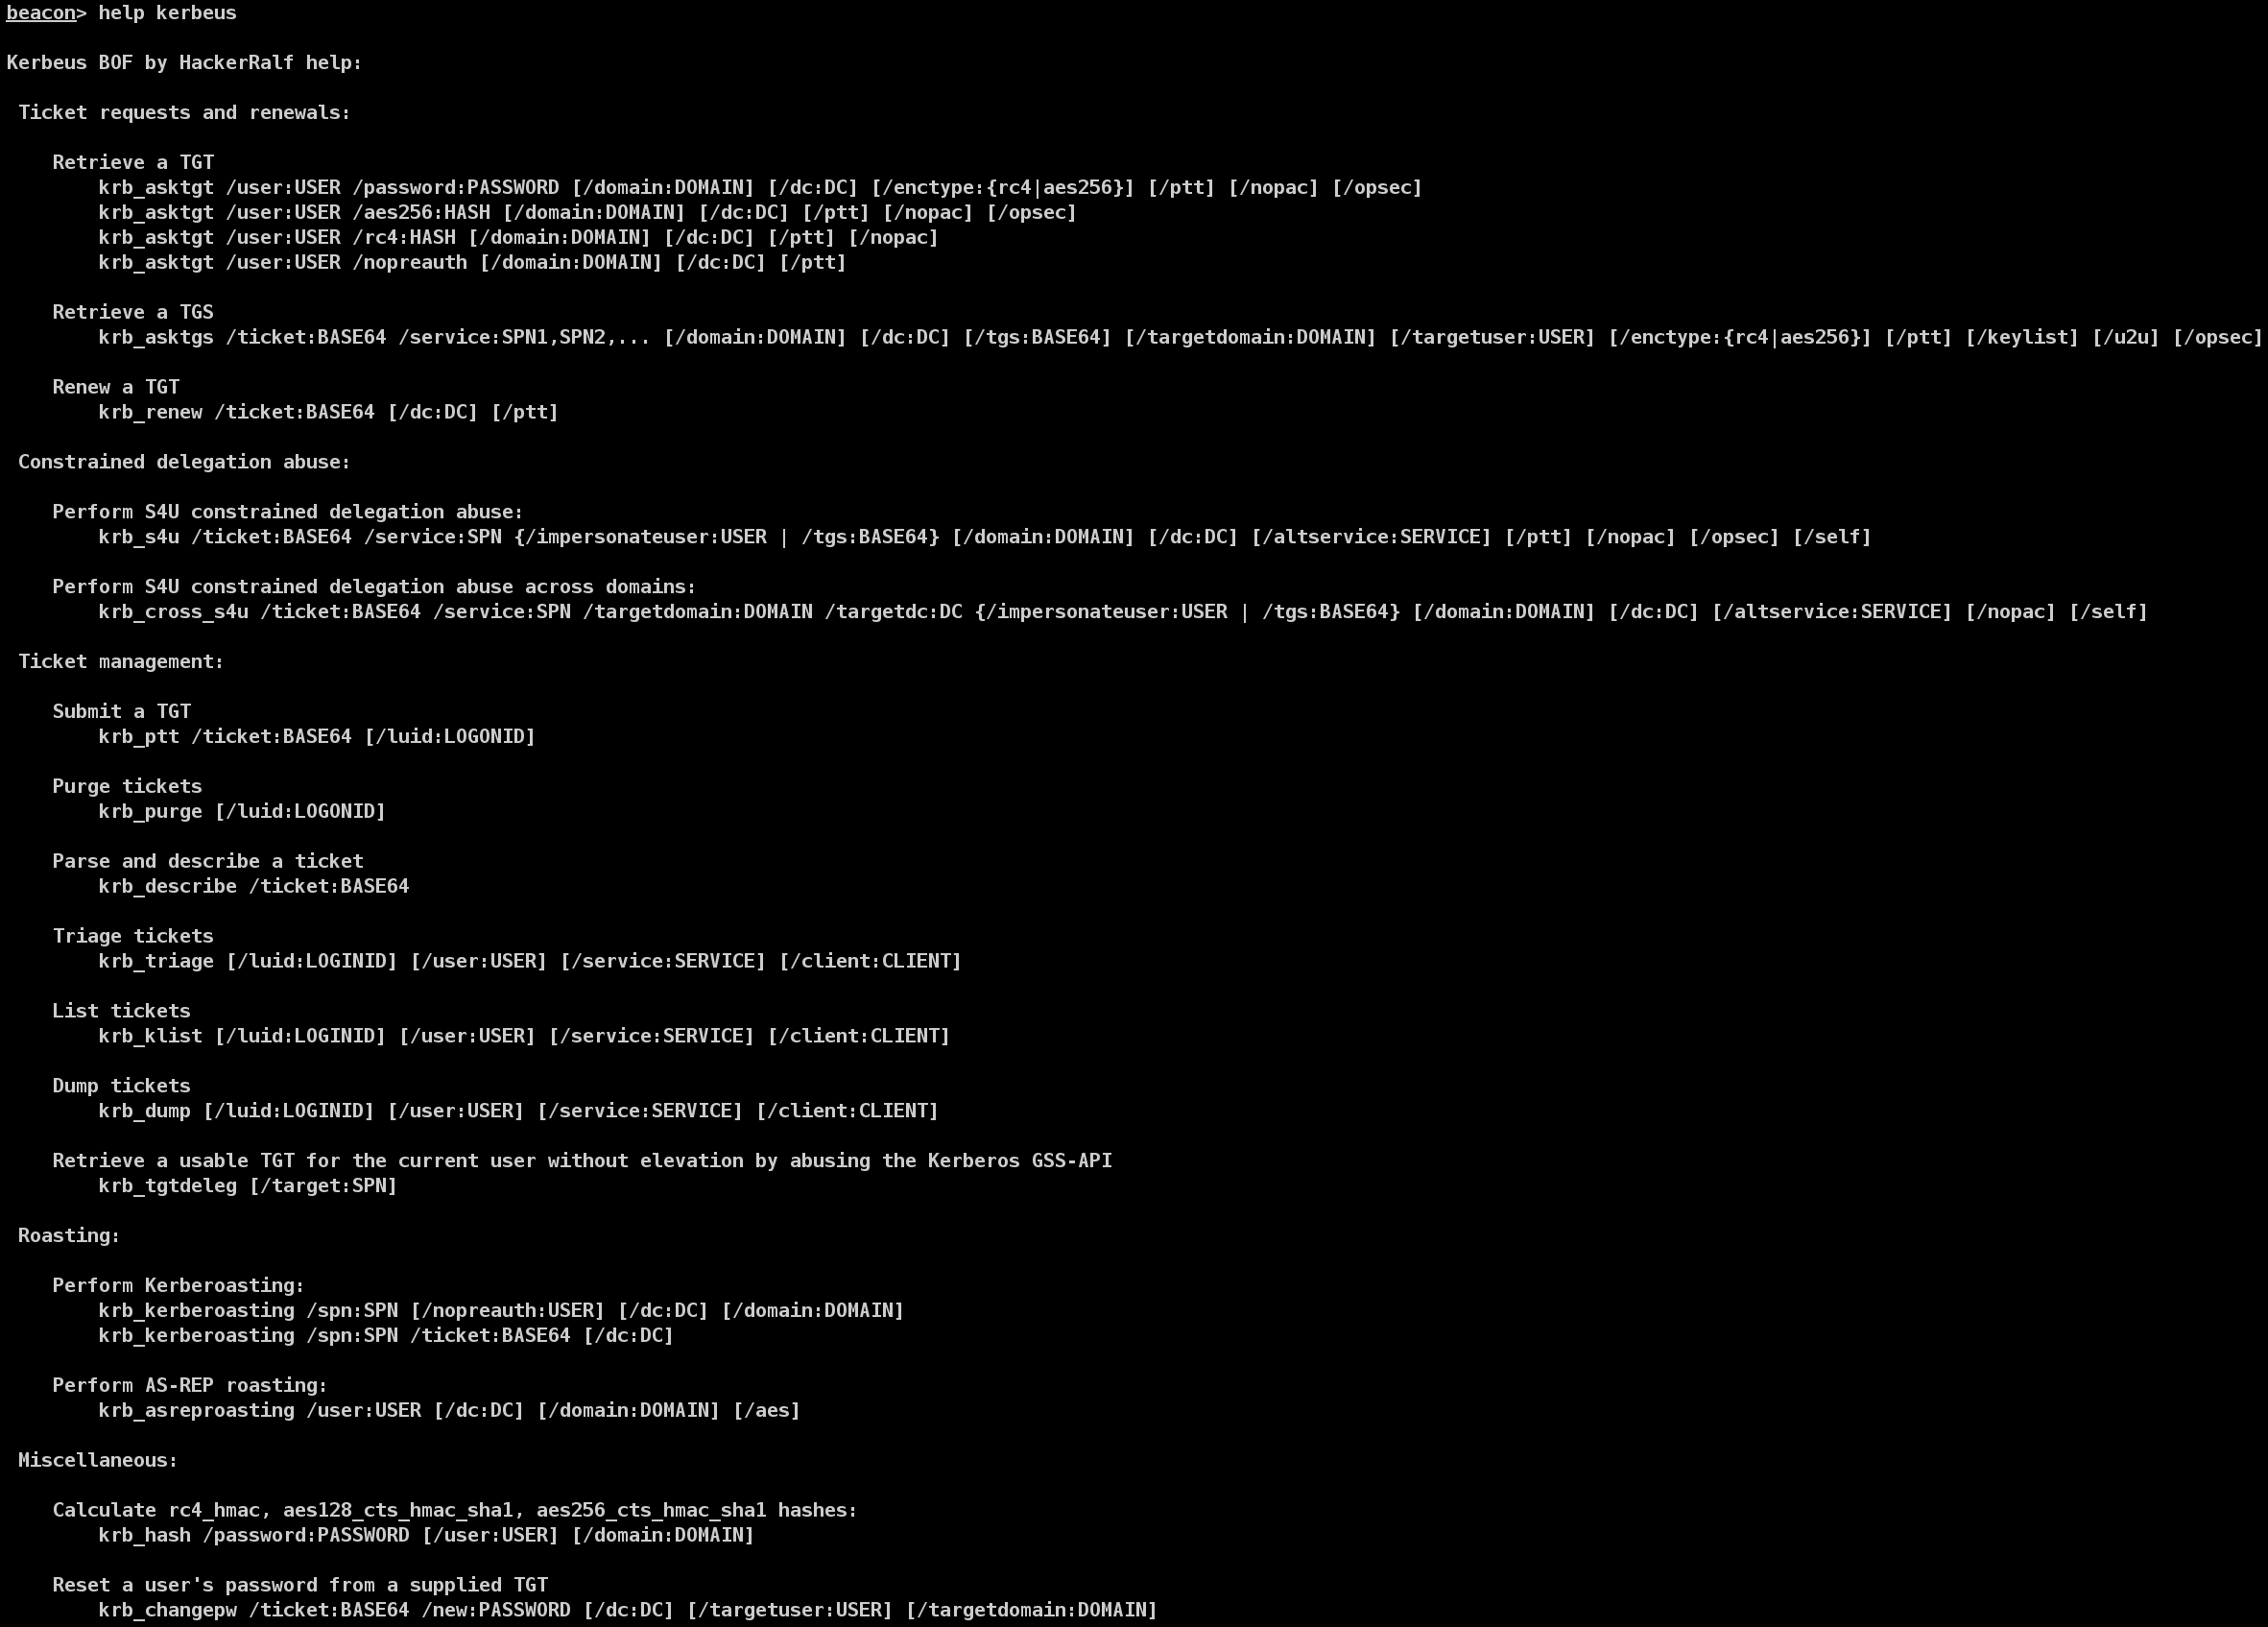 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 al1ex/linuxeelvation
Linux Eelvation(持续更新)
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
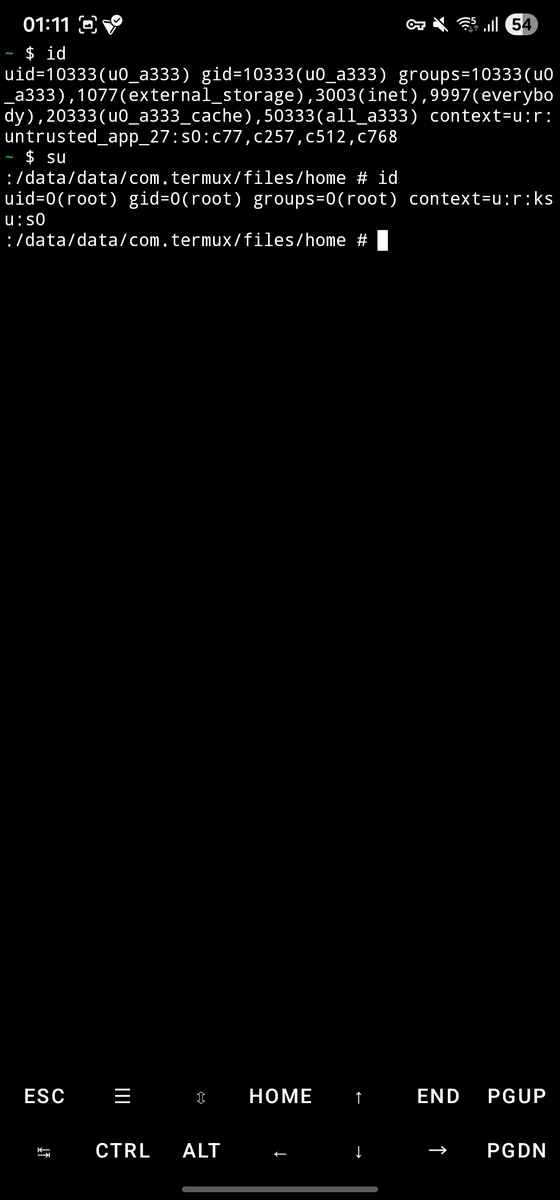 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
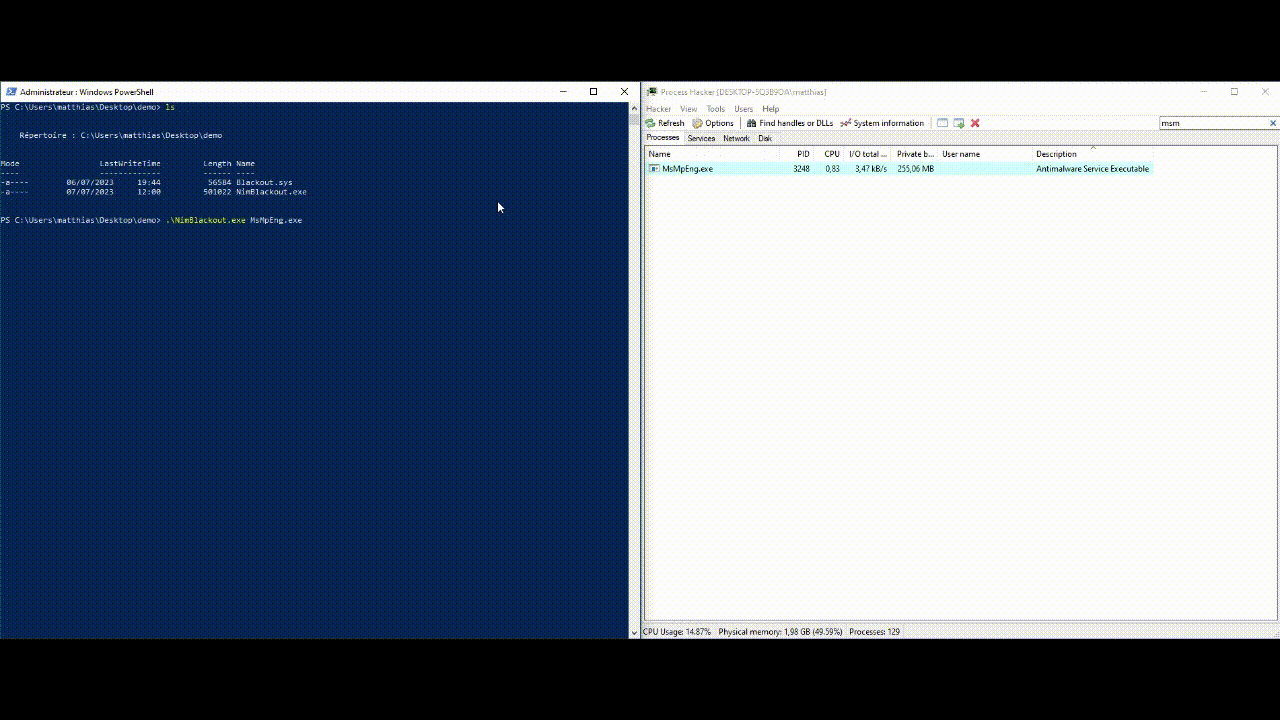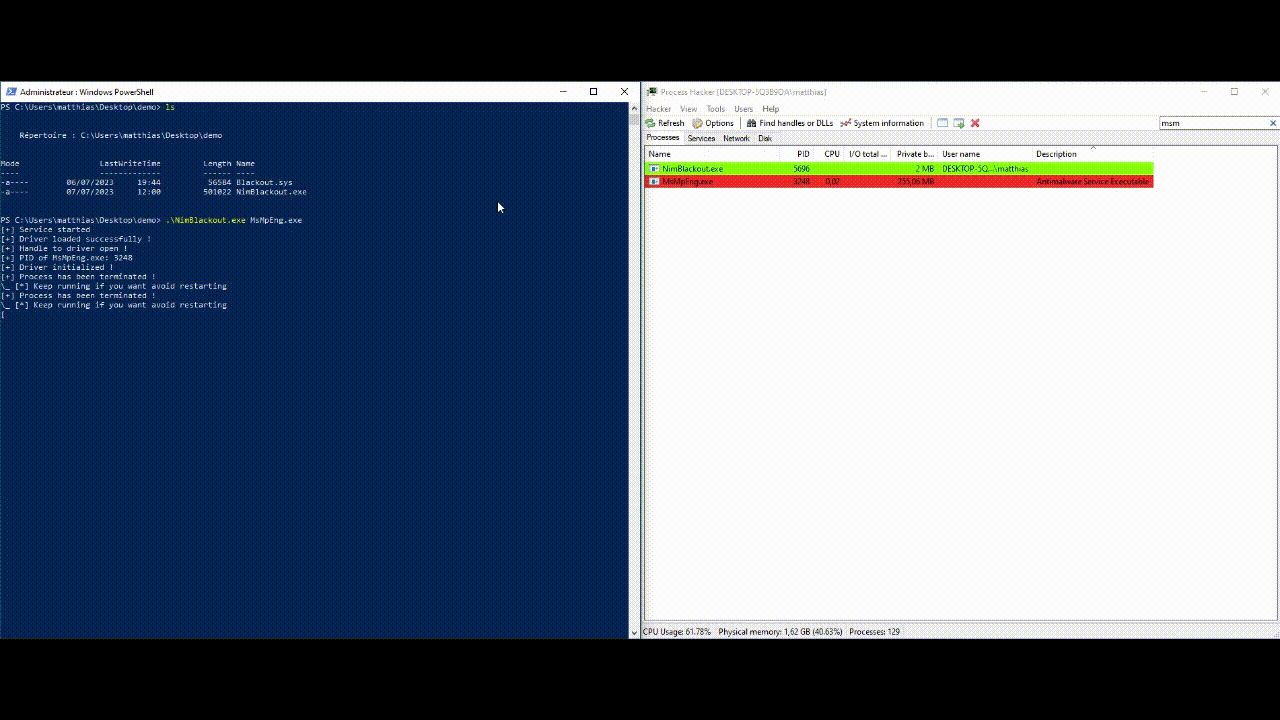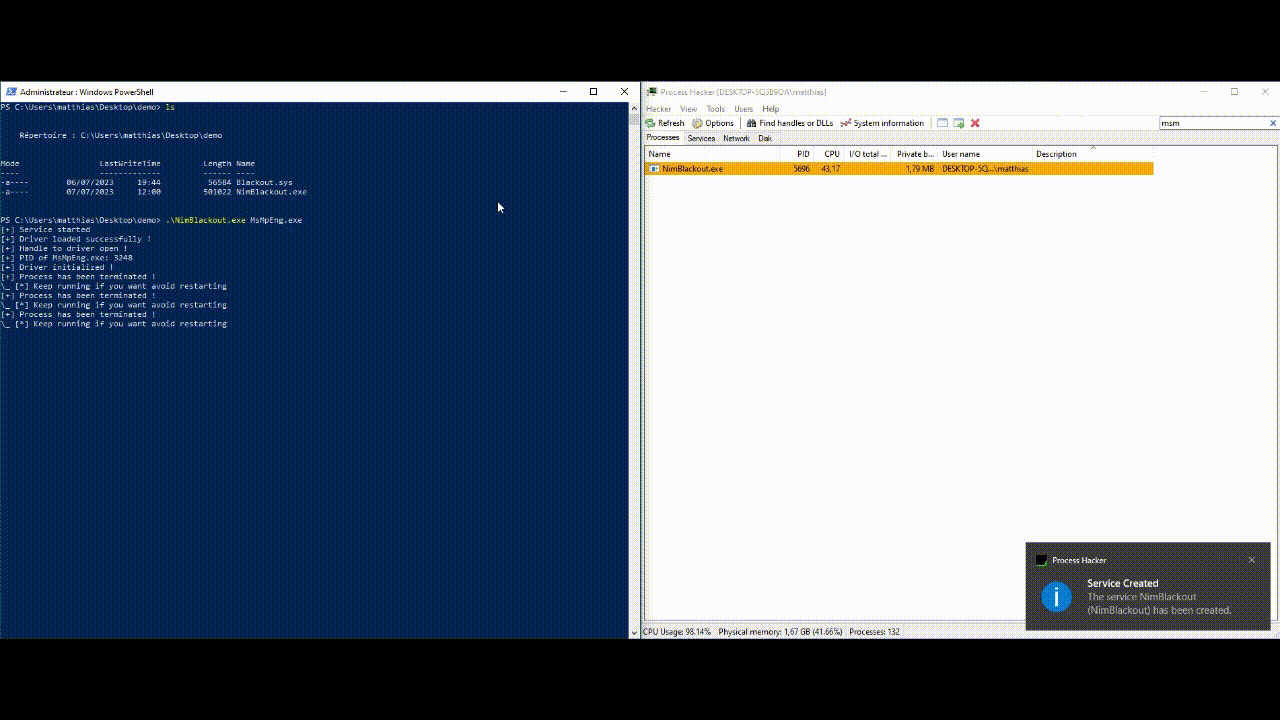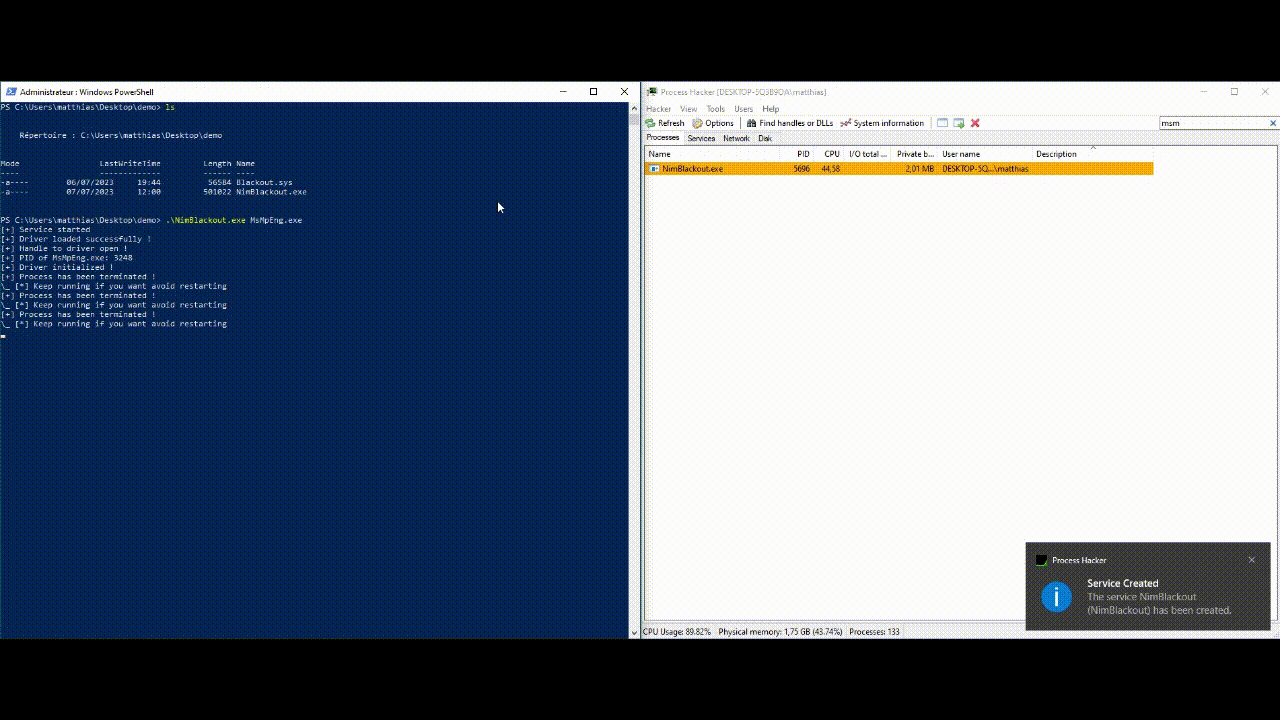 helixo32/nimblackout
Kill AV/EDR leveraging BYOVD attack
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.