
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
112 results
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…

exploitationmemory-forensicspayload-development+4
89
25 days ago
AmdRyzenMasterCheat preview

AmdRyzenMasterCheat

GitHubekknod/amdryzenmastercheat

Exploit tool leveraging CVE-2020-12928 (AMD RyzenMaster driver) for game memory manipulation and anti-cheat bypass on Windows 10 with AMD Ryzen CPUs.

exploitationhardware-securitymemory-forensics+3
625 years ago
CVE-2021-40449 preview

CVE-2021-40449

GitHubhakivvi/cve-2021-40449

Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…

binary-exploitationexploitationmemory-forensics+4
474 years ago
POC-CVE-2023-32233 preview

POC-CVE-2023-32233

GitHuboferchen/poc-cve-2023-32233

Use-After-Free in Netfilter nf_tables when processing batch requests CVE-2023-32233
binary-exploitationexploitationmemory-forensics+4
533 years ago
CredsHunter preview

CredsHunter

GitHubblacksnufkin/credshunter

PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
binary-exploitationexploitationmemory-forensics+2
374 months ago
dtrace-memaccess_cve-2020-27949 preview

dtrace-memaccess_cve-2020-27949

GitHubseemoo-lab/dtrace-memaccess_cve-2020-27949

Proof-of-concept exploit for CVE-2020-27949, demonstrating arbitrary memory read/write in macOS processes via DTrace fasttrap ioctl without elevated…

binary-exploitationexploitationmemory-forensics+3
335 years ago
CVE-2026-31431 preview

CVE-2026-31431

GitHubjuanbindez/cve-2026-31431

Copy Fail - CVE-2026-31431
binary-exploitationexploitationmemory-forensics+4
263 months ago
PPPoEject preview

PPPoEject

GitHubmanizada/pppoeject

Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
binary-exploitationexploitationmemory-forensics+4
811 days ago
CVE-2023-20564 preview

CVE-2023-20564

GitHubntgabrielgomes/cve-2023-20564

Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
binary-exploitationexploitationhardware-security+4
208 months ago
CVE-2016-5195 preview

CVE-2016-5195

GitHubwhu-enjoy/cve-2016-5195

这里保留着部分脏牛漏洞的利用代码
binary-exploitationexploitationmemory-forensics+2
109 years ago
CVE-2020-28018 preview

CVE-2020-28018

GitHubdorkerdevil/cve-2020-28018

Exploit for Exim Use-After-Free (CVE-2020-28018) achieving remote code execution via memory corruption primitives, including arbitrary read/write and…
binary-exploitationexploitationmemory-forensics+4
75 years ago
CVE-2026-46215-exploit-linux-7.0-uaf-stable preview

CVE-2026-46215-exploit-linux-7.0-uaf-stable

GitHubbluedragonsecurity/cve-2026-46215-exploit-linux-7.0-uaf-stable

CVE-2026-46215 DRM GEM UAF Exploit for Linux 7.0 - The first working PoC for linux kernel 7 use after free- by Antonius (sw0rdm4n, w1sdom, ev1lut10n)

binary-exploitationexploitationmemory-forensics+2
52 months ago
CVE-2024-1065 preview

CVE-2024-1065

GitHubkuzeyardabulut/cve-2024-1065

Proof-of-concept exploit for CVE-2024-1065, demonstrating page cache exploitation via a use-after-free in the ARM Mali GPU kernel driver to achieve…
binary-exploitationexploitationmemory-forensics+4
53 months ago
CVE-2026-29923 preview

CVE-2026-29923

GitHubsmarttfoxx/cve-2026-29923

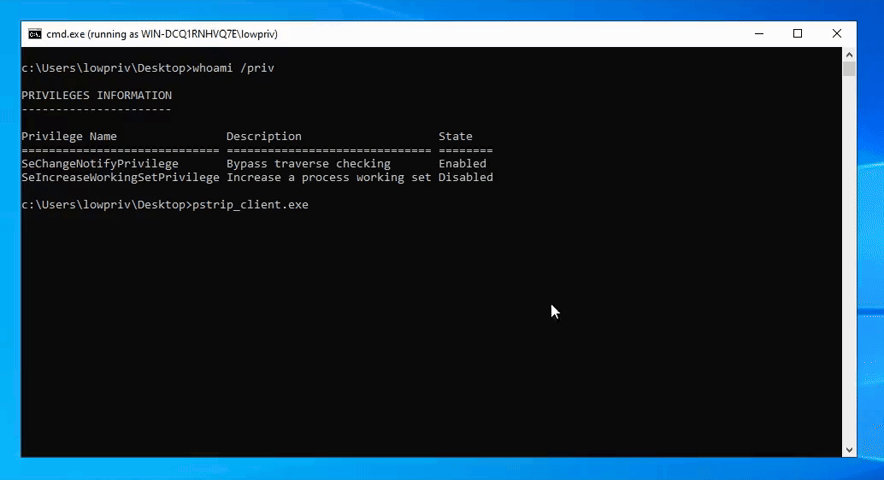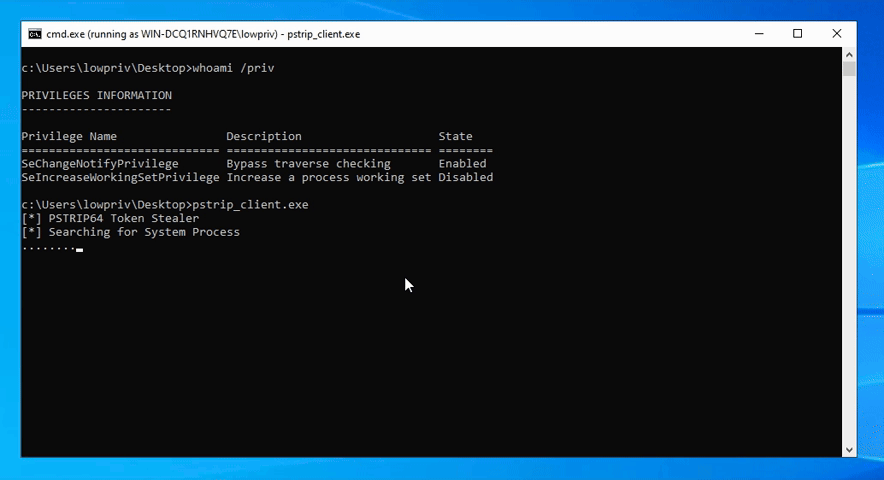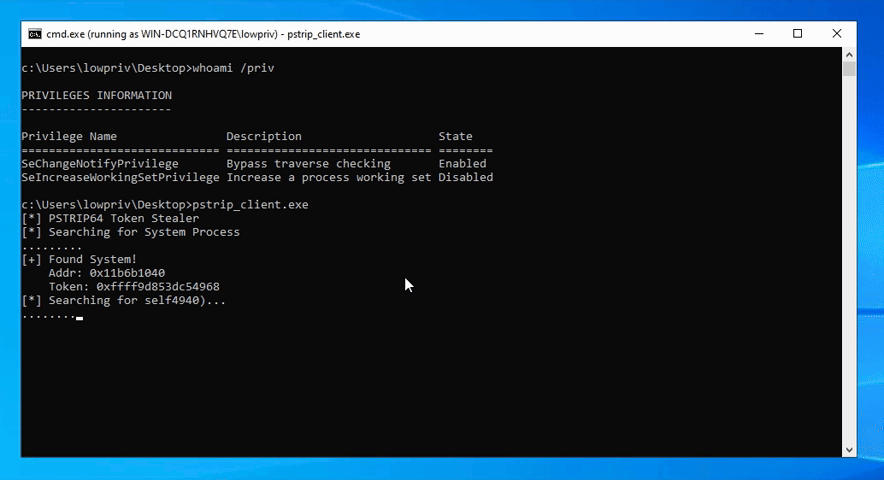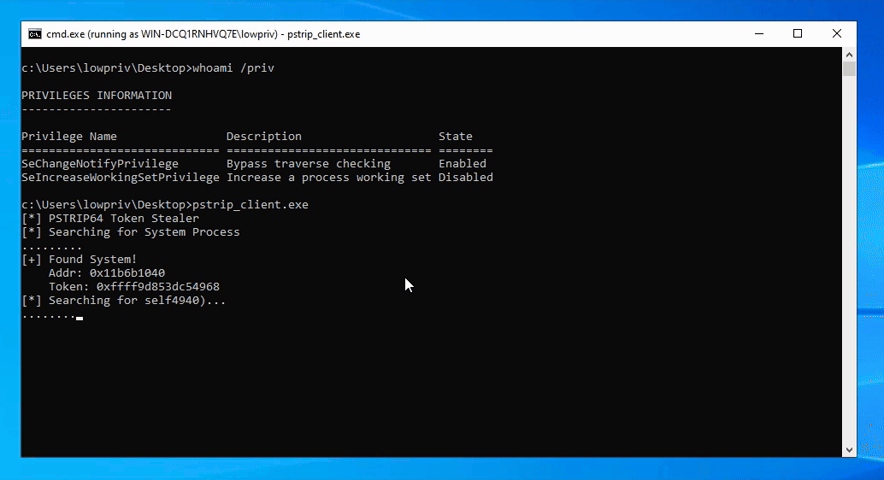
The pstrip64.sys kernel driver exposes an IOCTL that allows low-privileged users to map arbitrary ranges of physical memory into their own virtual…
binary-exploitationexploitationmemory-forensics+3
45 months ago
CVE-2026-23111 preview

CVE-2026-23111

GitHub0xblackash/cve-2026-23111

CVE-2026-23111
binary-exploitationexploitationmemory-forensics+2
43 months ago
CVE-2023-36407 preview

CVE-2023-36407

GitHubpwndorei/cve-2023-36407

PoC - CVE-2023-36407
binary-exploitationexploitationmemory-forensics+2
52 years ago
MSRMapper preview

MSRMapper

GitHubull0a/msrmapper

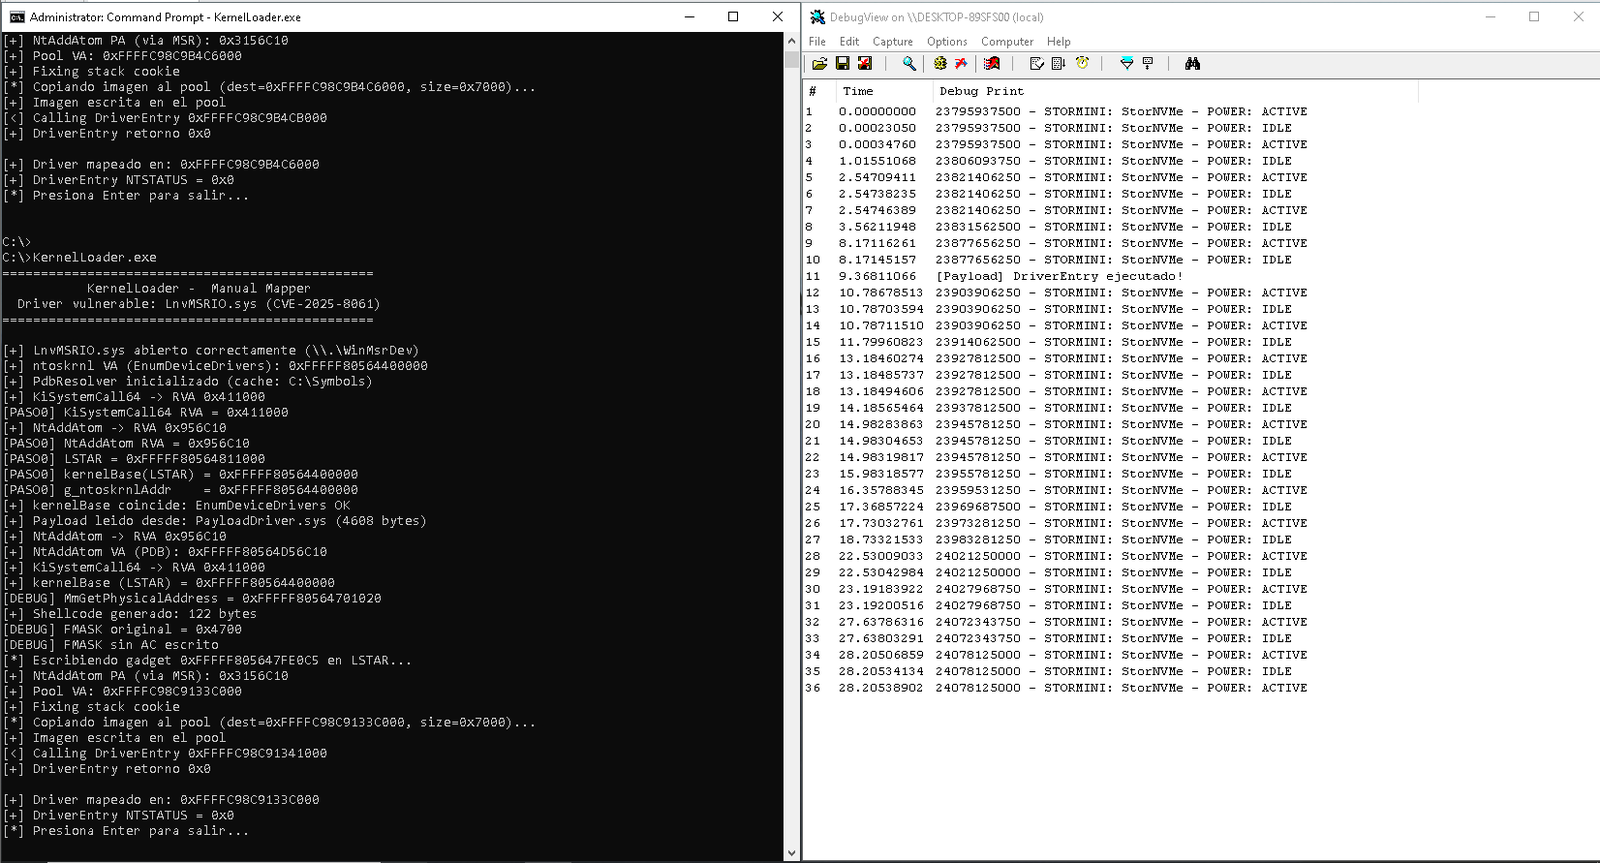
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
binary-exploitationexploitationmemory-forensics+6
112 days ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…

defensive-toolsmalware-analysismemory-forensics+3
22 years ago
Previous1234567Next