
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
88 results
CVE-2025-56383 preview

CVE-2025-56383

GitHubnewcomrade12211/cve-2025-56383

DLL hijacking to rev shell

binary-exploitationexploitationpayload-development+2
10 years ago
CVE-2021-34527 preview

CVE-2021-34527

GitHubcyb3rpeace/cve-2021-34527

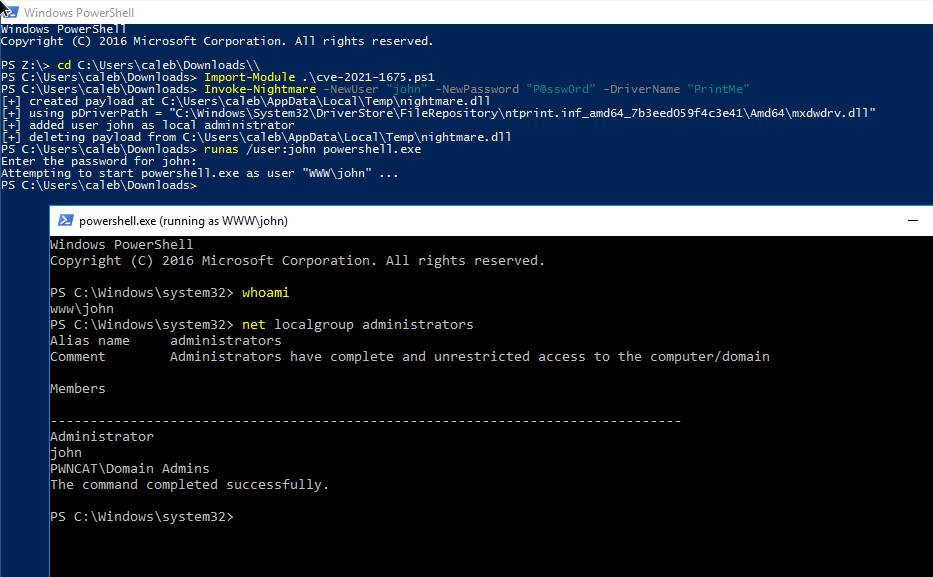
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
binary-exploitationexploitationpayload-generation+4
14 years ago
CompMgmtLauncher_DLL_UACBypass preview

CompMgmtLauncher_DLL_UACBypass

GitHubhackerhouse-opensource/compmgmtlauncher_dll_uacbypass

CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive

exploitationpersistence-mechanismspost-exploitation+2
1099 months ago
iscsicpl_bypassUAC preview

iscsicpl_bypassUAC

GitHubhackerhouse-opensource/iscsicpl_bypassuac

UAC bypass for x64 Windows 7 - 11
exploitationpayload-developmentpost-exploitation+2
8489 months ago
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

Dumping LSASS with a duplicated handle from custom LSA plugin
post-exploitationprivilege-escalationred-teaming
2074 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubthomasgeens/cve-2021-1675

PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…

binary-exploitationexploitationpayload-development+2
35 years ago
CVE-2021-1675-CVE-2021-34527 preview

CVE-2021-1675-CVE-2021-34527

GitHubwhoami-chmod777/cve-2021-1675-cve-2021-34527

PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
binary-exploitationexploitationpayload-development+2
12 years ago
RunAsWinTcb preview

RunAsWinTcb

GitHubtastypepperoni/runaswintcb

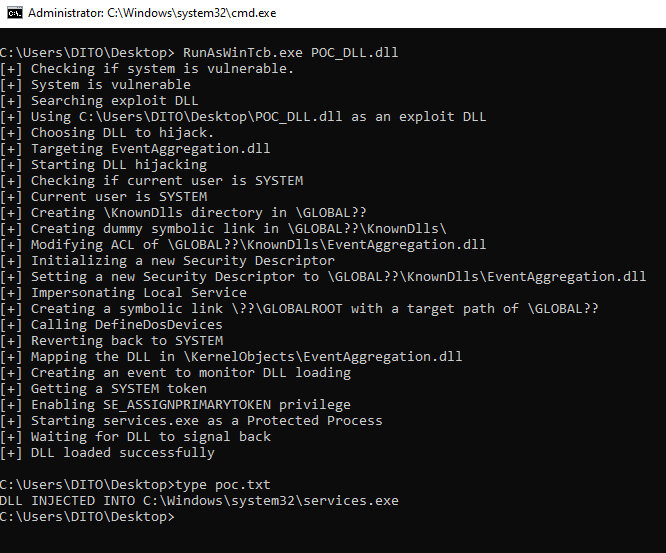
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
exploitationids-ips-evasionpost-exploitation+2
1384 years ago
QuickAssist_UAC_Bypass preview

QuickAssist_UAC_Bypass

GitHubr41n3rzuf477/quickassist_uac_bypass

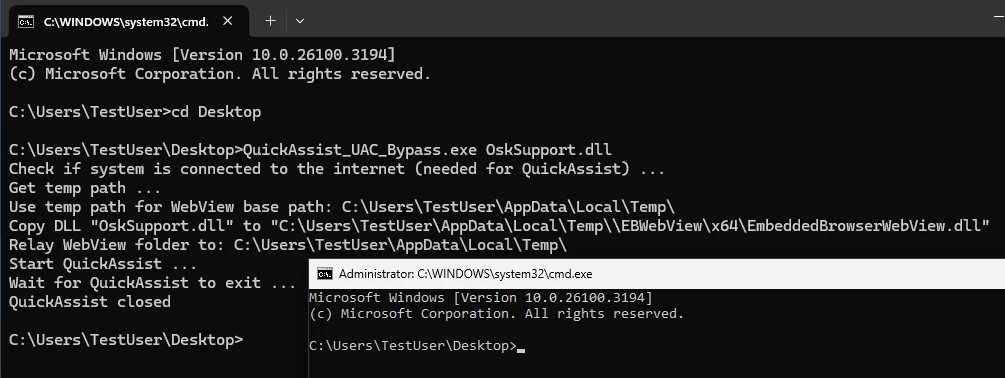
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
defensive-toolsexploitationpayload-development+4
2443 months ago
DropSpawn_BOF preview

DropSpawn_BOF

GitHuboctoberfest7/dropspawn_bof

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
binary-exploitationexploitationpayload-development+4
2873 years ago
IDiagnosticProfileUAC preview

IDiagnosticProfileUAC

GitHubwh04m1001/idiagnosticprofileuac

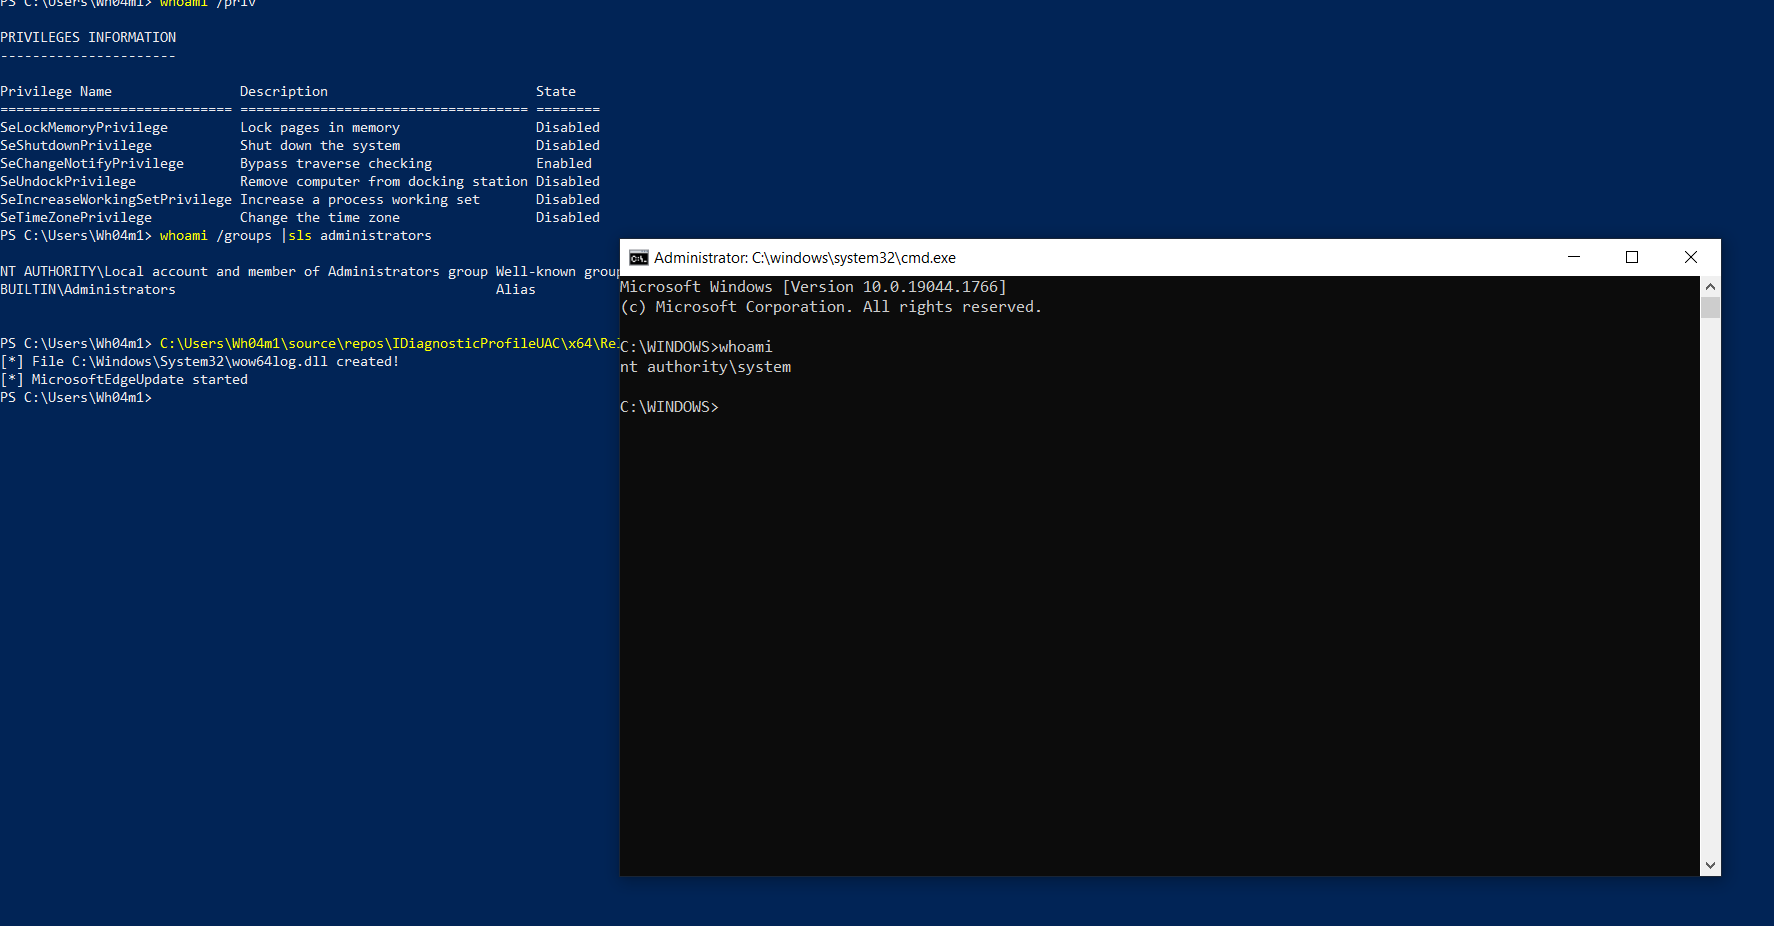
Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…

exploitationpenetration-testingpost-exploitation+2
1844 years ago
gluegate preview

gluegate

GitHubsbousseaden/gluegate

Memory API proxy via signed mozglue.dll

defensive-toolsids-ips-evasionmemory-forensics+2
394 months ago
CVE-2023-41772 preview

CVE-2023-41772

GitHubr41n3rzuf477/cve-2023-41772

Windows privilege escalation exploit for CVE-2023-41772 (UIFuckUp) that elevates non-admin users to SYSTEM on Windows 10 (1809+) and 11 via a crafted…
binary-exploitationexploitationpenetration-testing+2
142 years ago
CVE-2026-66804-CrossDevice-LPE preview

CVE-2026-66804-CrossDevice-LPE

GitHubdavidcarliez/cve-2026-66804-crossdevice-lpe

Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
binary-exploitationexploitationprivilege-escalation+1
162 months ago
CVE-2024-6769 preview

CVE-2024-6769

GitHubfortra/cve-2024-6769

Technical writeup and PoC for CVE-2024-6769, chaining DLL hijacking with activation cache poisoning to escalate from medium to high integrity on…
binary-exploitationeducationexploitation+3
782 years ago
uac-a-mola preview

uac-a-mola

GitHubtelefonica/uac-a-mola

Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…
defensive-toolsexploit-frameworkspenetration-testing+1
1075 years ago
CVE-2026-50343-InstallService-EoP preview

CVE-2026-50343-InstallService-EoP

GitHubrat5ak/cve-2026-50343-installservice-eop

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
binary-exploitationeducationexploitation+3
483 months ago
TeamViewer_Permissions_Hook_V1 preview

TeamViewer_Permissions_Hook_V1

GitHubgellin/teamviewer_permissions_hook_v1

A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.

educationexploitationlateral-movement+5
3108 years ago
Previous12345Next