
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
88 results
UACElevator preview

UACElevator

GitHubmalwaretech/uacelevator

Passive UAC elevation using dll infection

exploitationpayload-developmentpost-exploitation+2
7311 years ago
CVE-2024-31771 preview

CVE-2024-31771

GitHubrestdone/cve-2024-31771

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…

binary-exploitationexploitationlateral-movement+4
2 years ago
ncloader preview

ncloader

GitHubnccgroup/ncloader

A session-0 capable dll injection utility
exploitationpenetration-testingprivilege-escalation+1
768 years ago
microsoft-cve-2021-1675 preview
Archived

microsoft-cve-2021-1675

GitHubthalpius/microsoft-cve-2021-1675

Proof-of-concept C# exploit for CVE-2021-1675 (Windows Print Spooler elevation of privilege), accepting custom driver and DLL paths for targeted…
exploitationpenetration-testingprivilege-escalation
3 months ago
CVE-2024-34329 preview

CVE-2024-34329

GitHubpamoutaf/cve-2024-34329

Proof-of-concept exploit for a local privilege escalation vulnerability in Datacard XPS Card Printer Driver via insecure file permissions and DLL…
binary-exploitationexploitationlateral-movement+2
2 years ago
TrustJack preview

TrustJack

GitHubjfmaes/trustjack

Yet another PoC for https://www.wietzebeukema.nl/blog/hijacking-dlls-in-windows
exploitationpersistence-mechanismspost-exploitation+2
1436 years ago
PhantomCtx preview

PhantomCtx

GitHubr3xmax/phantomctx

Activation Context Hijacking Evasion Tool
binary-exploitationexploitationpayload-development+3
3064 months ago
clrinject preview

clrinject

GitHubjonatan1024/clrinject

Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
exploitationlateral-movementpenetration-testing+3
2377 years ago
DLHell preview

DLHell

GitHubsynacktiv/dlhell

Local & remote Windows DLL Proxying
exploitationlateral-movementpayload-development+3
1722 years ago
CVE-2022-26809 preview

CVE-2022-26809

GitHubauduongxuan/cve-2022-26809

Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
exploitationlateral-movementpenetration-testing+3
74 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubpuckiestyle/cve-2021-1675

Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
exploitationlateral-movementpayload-generation+3
15 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubedsonjt81/cve-2021-1675

Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
exploitationlateral-movementpayload-generation+3
3 years ago
maalik preview
Archived

maalik

GitHubquantumcore/maalik

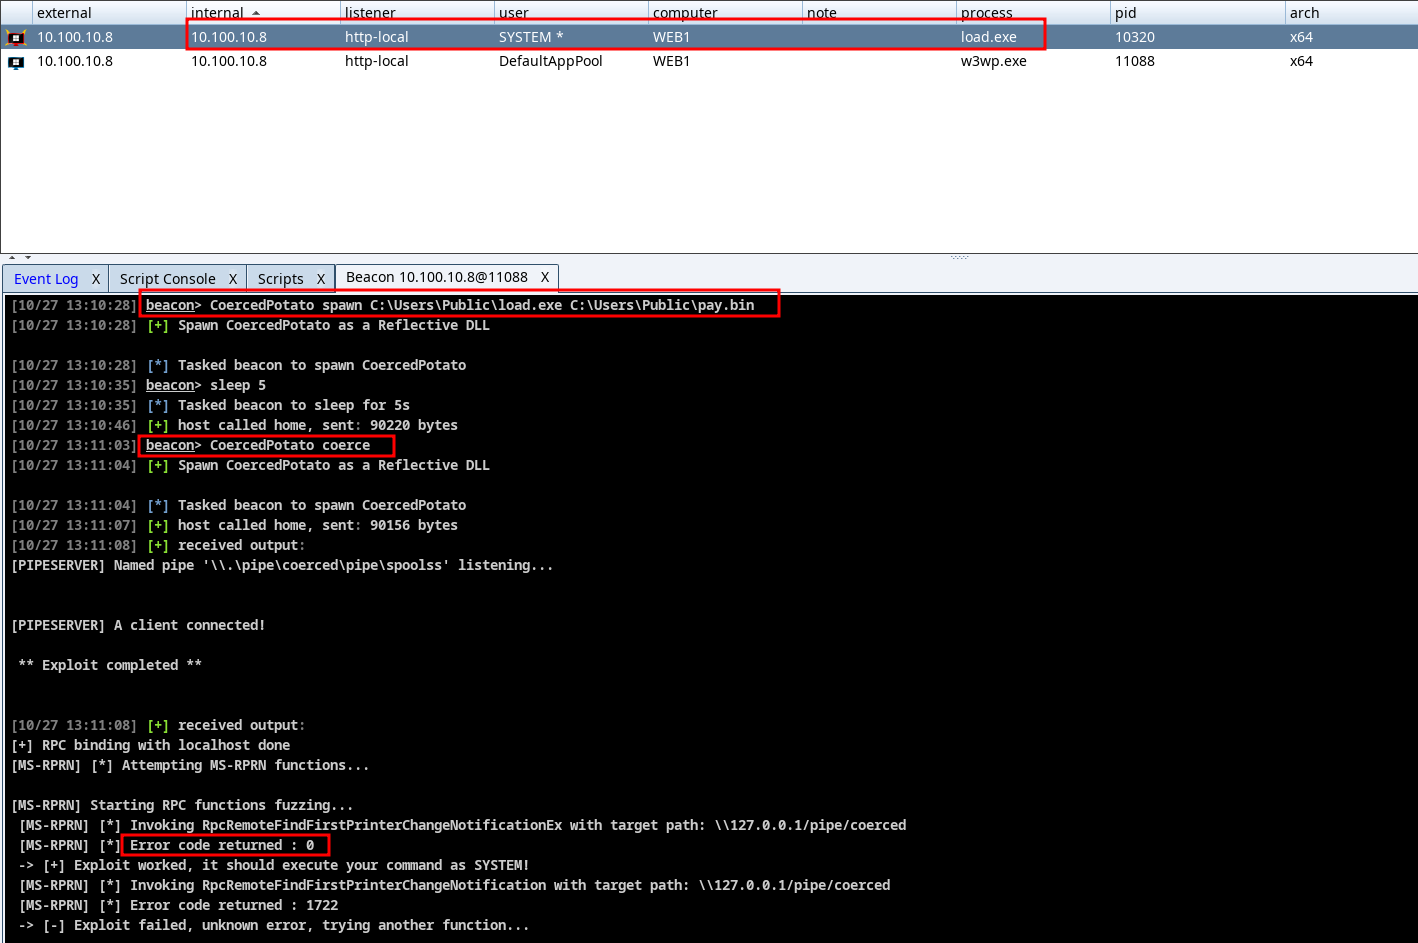
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
command-and-controlexploitationlateral-movement+6
945 years ago
CoercedPotatoRDLL preview

CoercedPotatoRDLL

GitHubsokarepo/coercedpotatordll

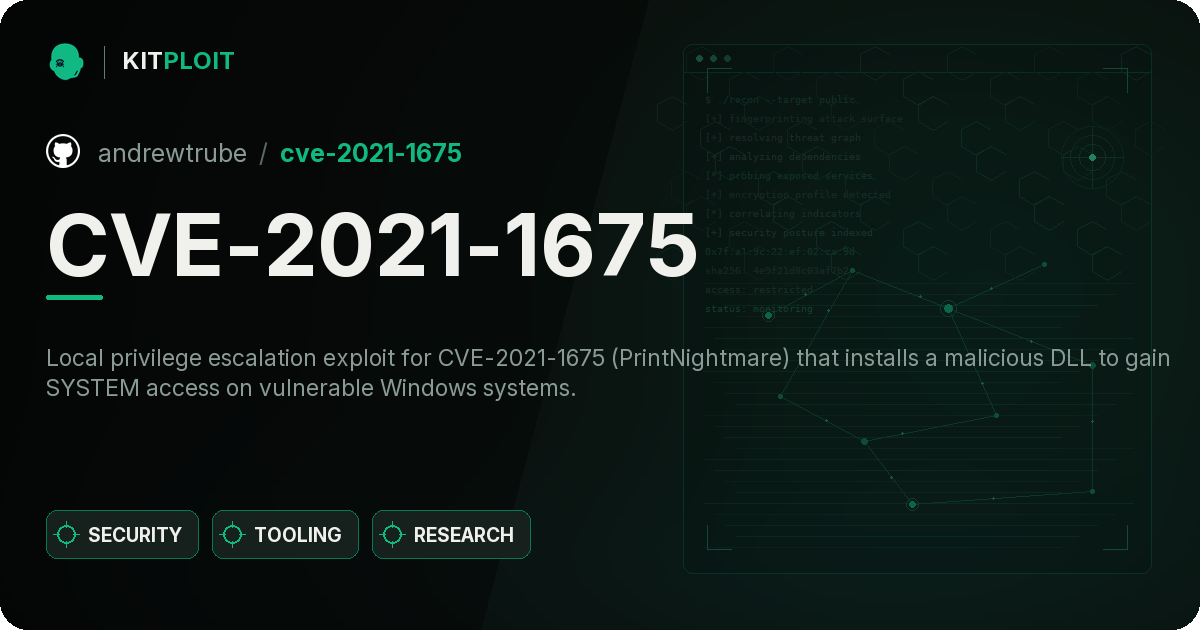
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
exploitationpayload-developmentpenetration-testing+4
2272 years ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubandrewtrube/cve-2021-1675

Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…

exploitationexploit-frameworkspayload-development+3
54 years ago
cve-2021-34527 preview

cve-2021-34527

GitHubhackerhouse-opensource/cve-2021-34527

CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation

binary-exploitationexploitationpayload-development+3
239 months ago
CVE-2021-34527 preview

CVE-2021-34527

GitHubjohnhammond/cve-2021-34527

PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
binary-exploitationexploitationpayload-generation+4
3235 years ago
SCCM-CVE-2026-47301-Remote-Code-Execution-Exploit preview

SCCM-CVE-2026-47301-Remote-Code-Execution-Exploit

GitHubomribaso/sccm-cve-2026-47301-remote-code-execution-exploit

Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…

exploitationpayload-developmentpenetration-testing+3
1082 months ago
Previous12345Next