
Azur3Alph4
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
cloud-securityinformation-gatheringpenetration-testing+3
63
hyd3sec/azur3alph4PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
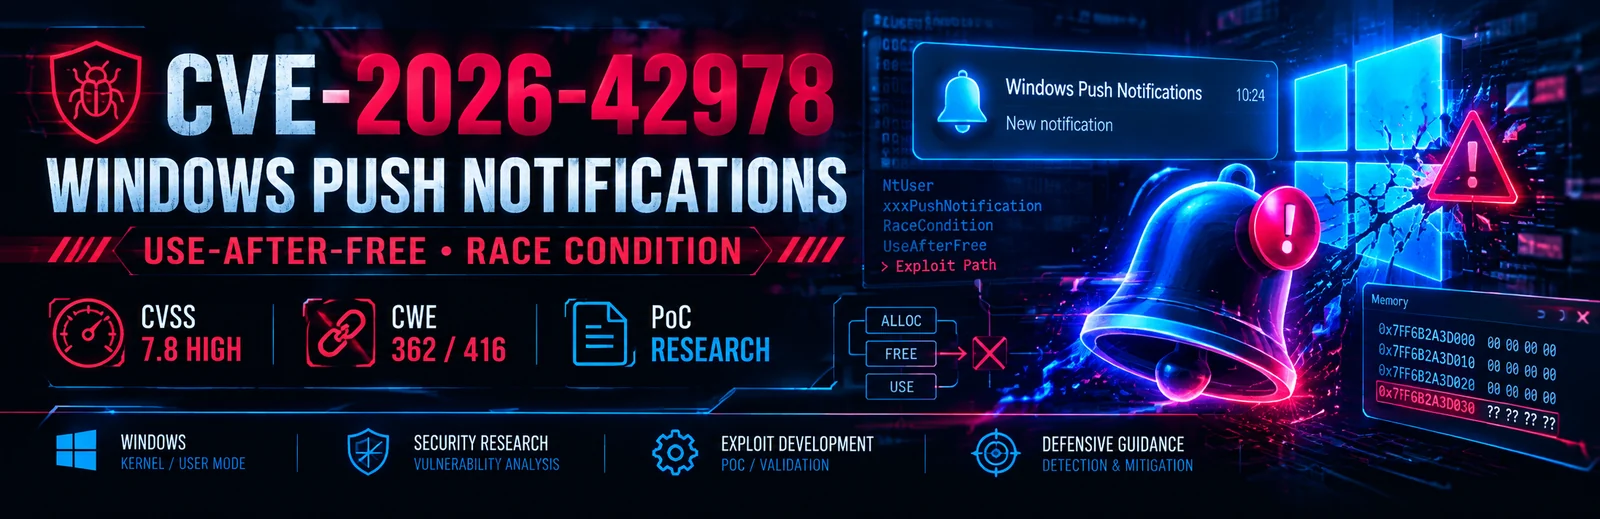 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 danaepp/pwncat_pwnkit
pwncat module that automatically exploits CVE-2021-4034 (pwnkit)
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
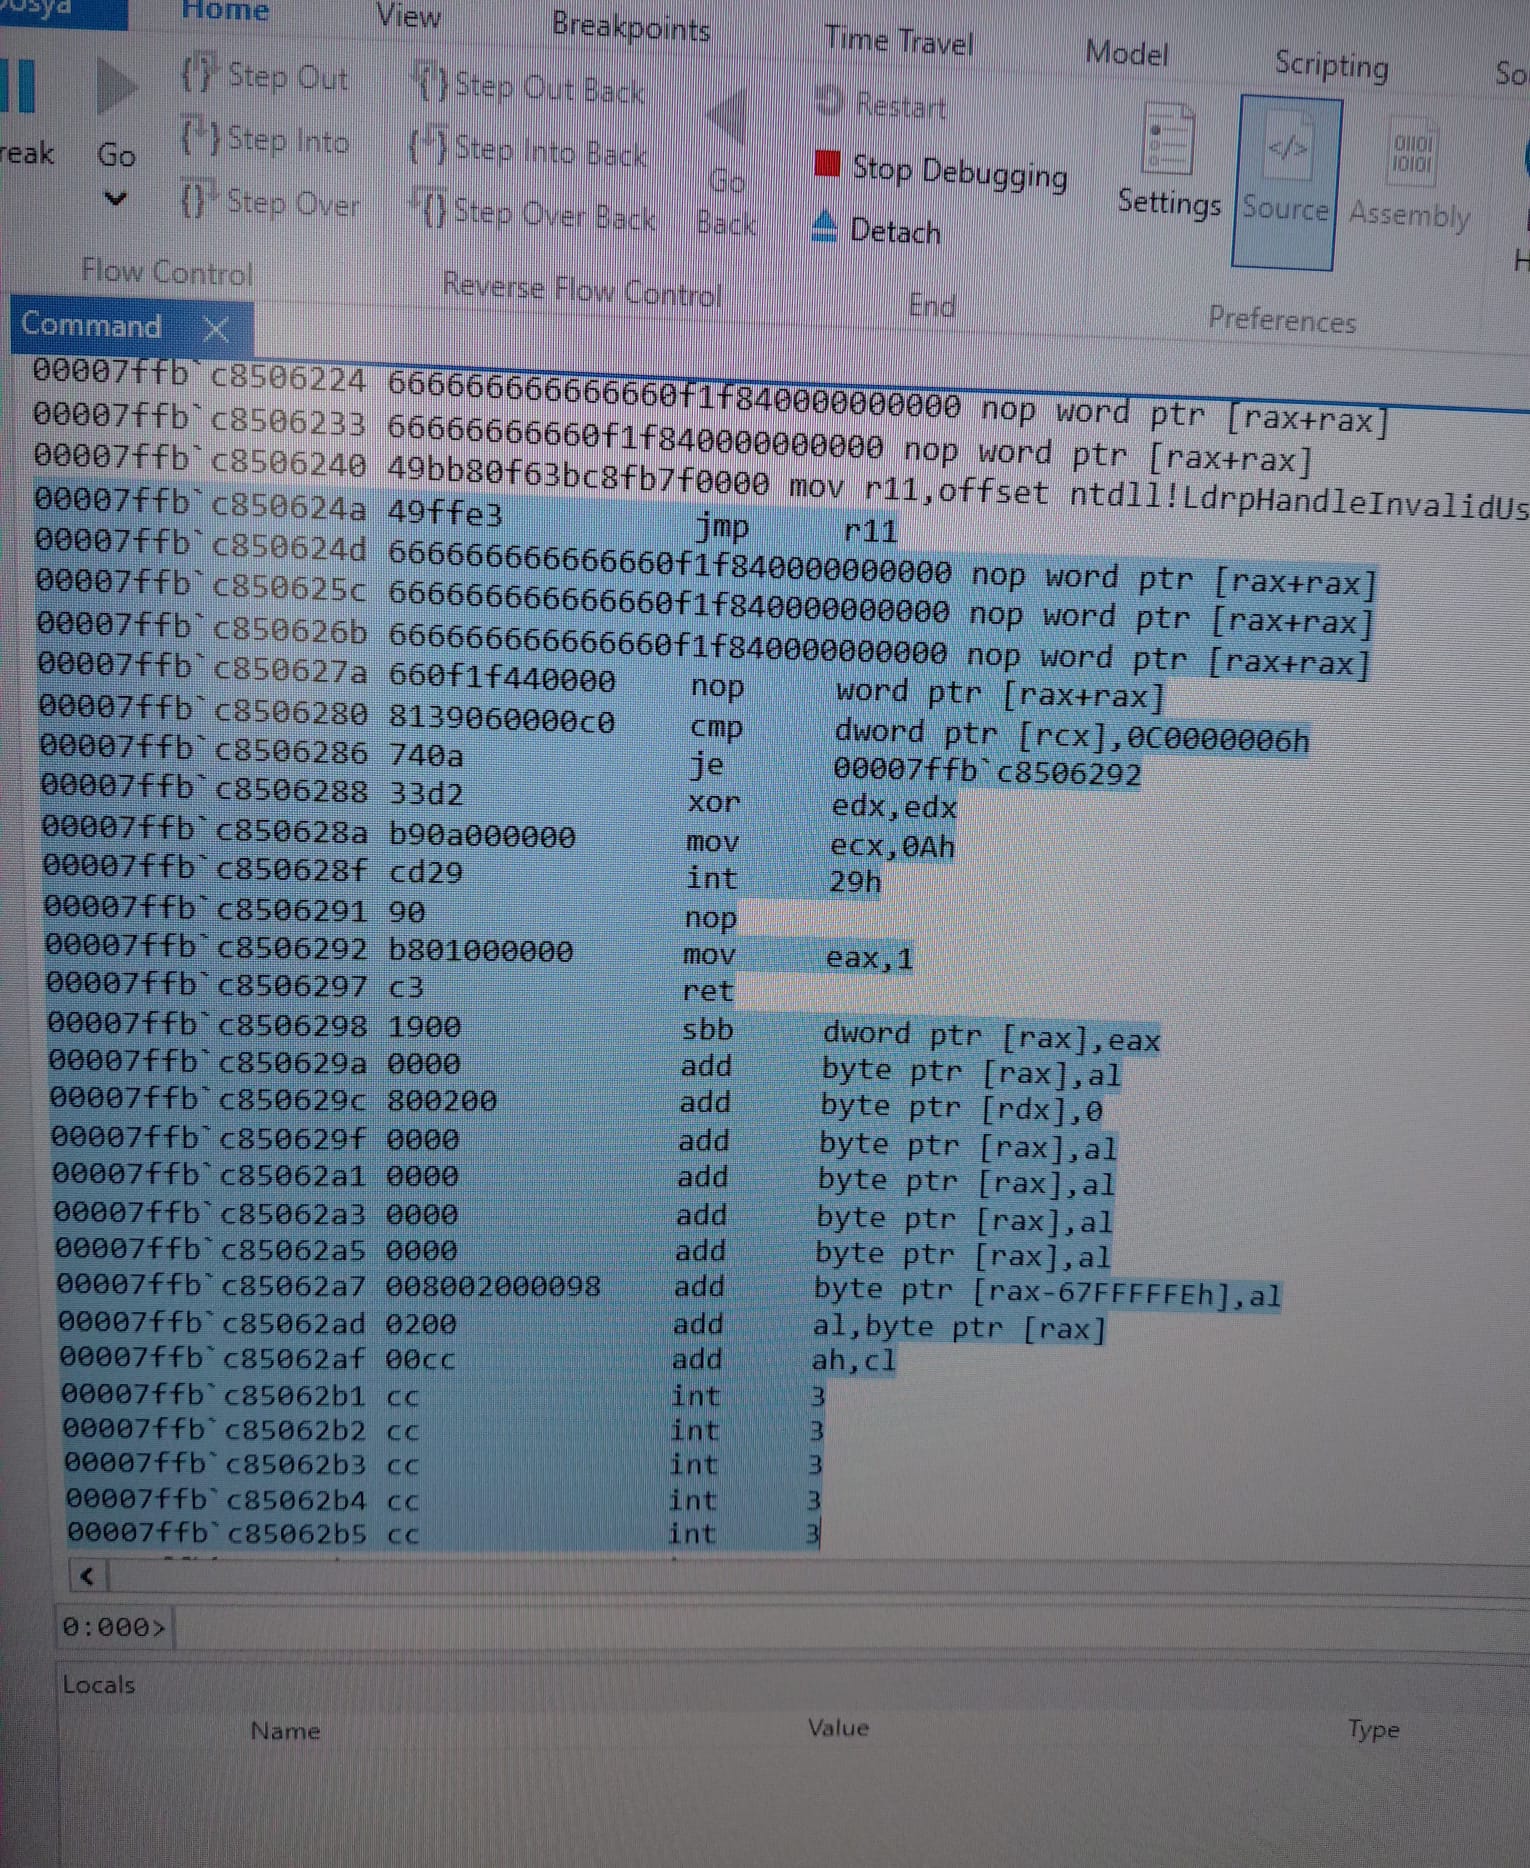 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 jeboo/bypasslkm
Using CVE-2013-6282 to bypass Samsung kernel module authentication
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 danaepp/pwncat_dirtypipe
pwncat module that automatically exploits CVE-2022-0847 (dirtypipe)
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
 mrk336/cve-2025-42957-sap-s-4hana-under-siege
CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 voltaireyoung/cve-2024-31719----ami-aptio-5-vulnerability
Demonstrates a local access control bypass in AMI Aptio 5 NvLock module, allowing modification of NVRAM variables including administrator password,…
 dixyes/fuck_cve_2026_31431
Kernel module exploiting CVE-2026-31431 to bypass system stop mechanisms, with configurable fake implementation for testing on non-stoppable machines.
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…