
Archived
SSH-Snake
 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
information-gatheringlateral-movementnetwork-mapping+5
 sinsinology/cve-2023-34039
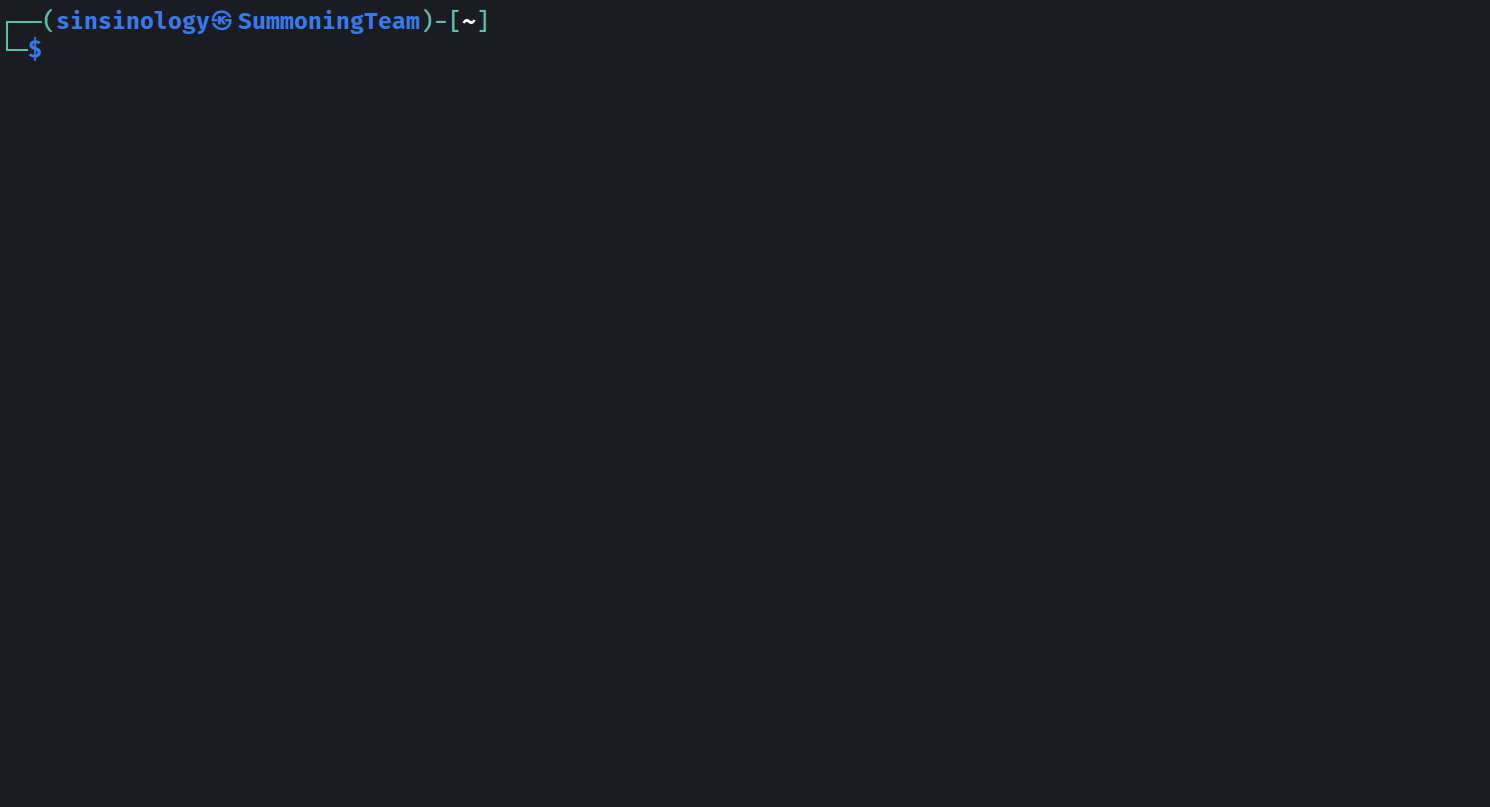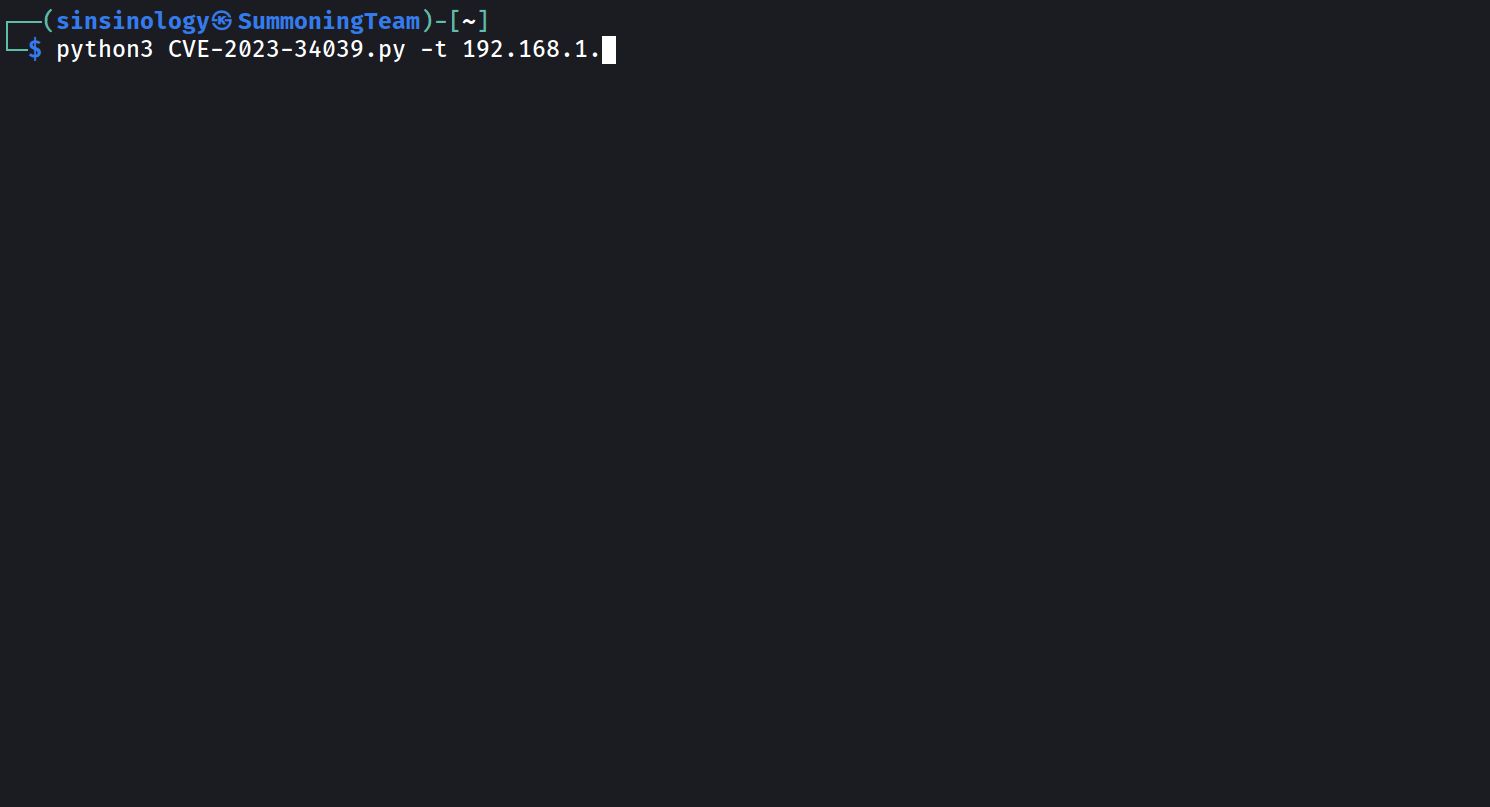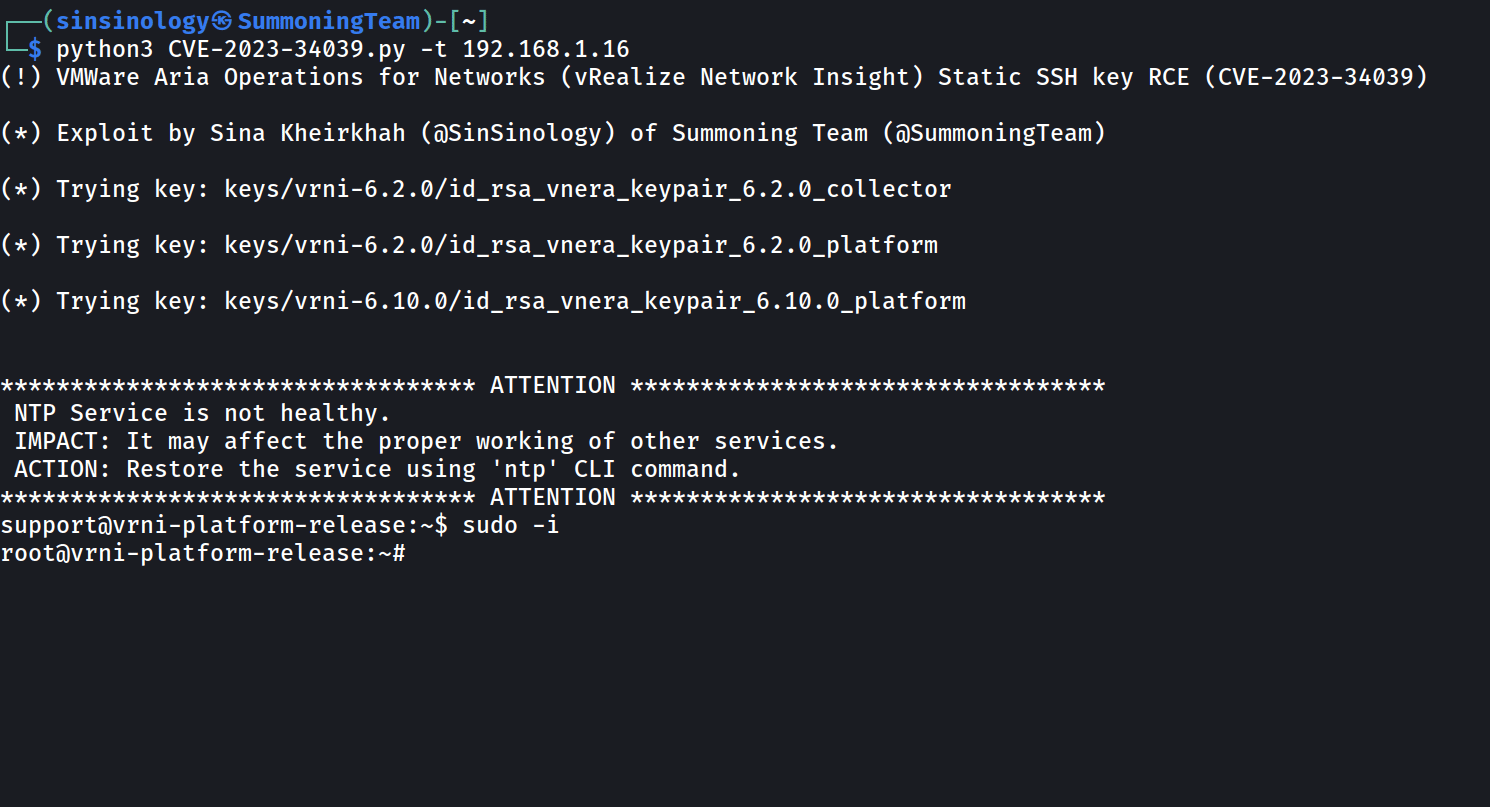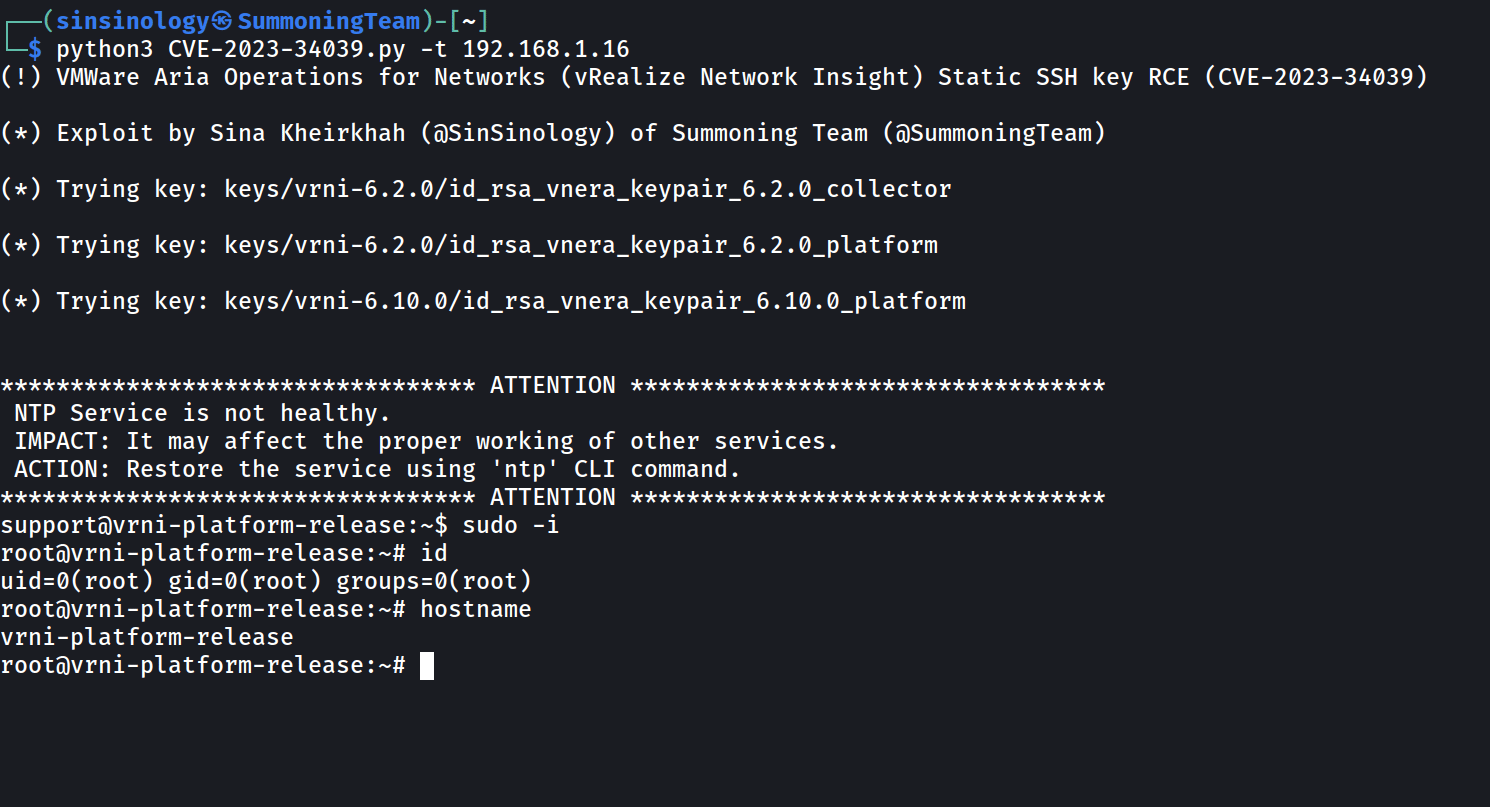
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
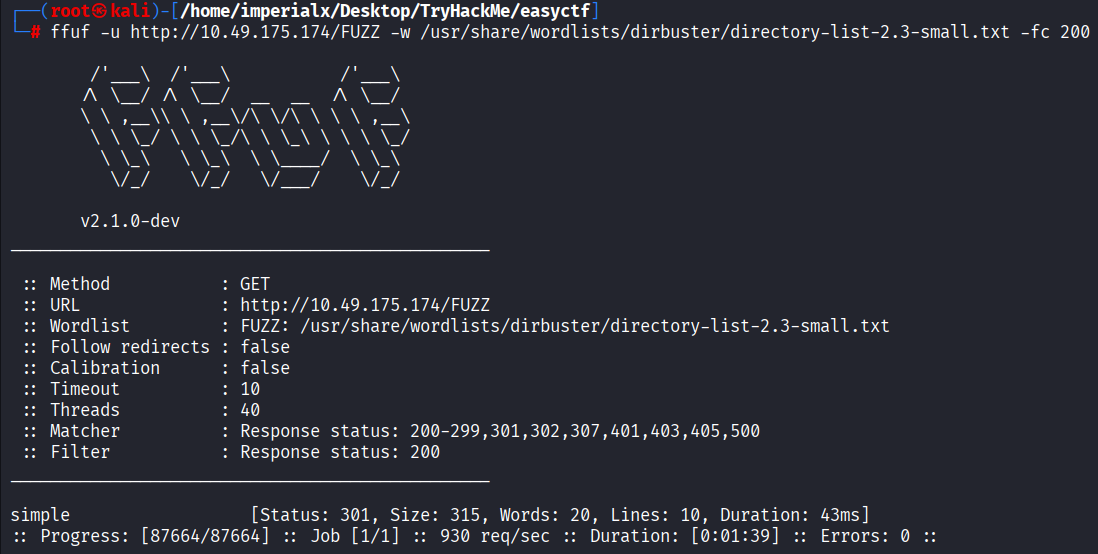 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
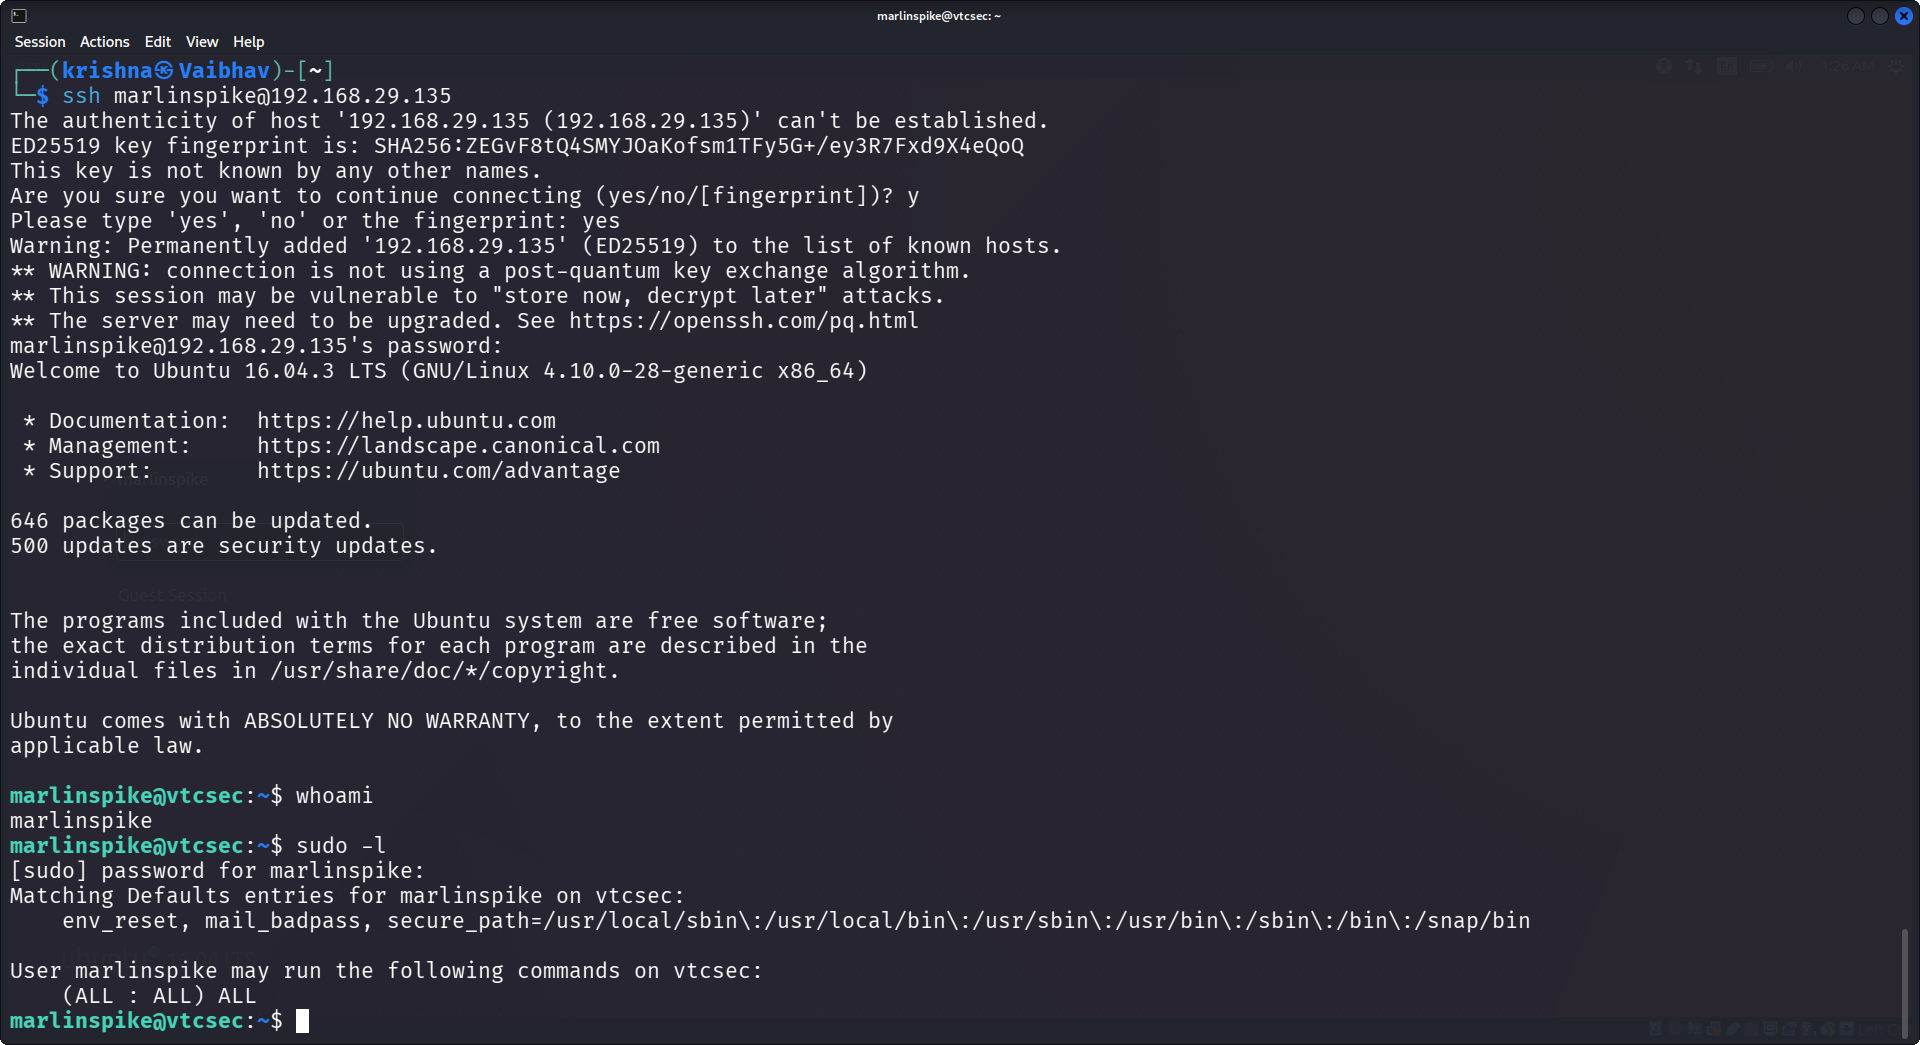 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 mustafa1986/cve-2024-22274-rce
Go-based exploit for CVE-2024-22274 that creates a new user via SSH and provides a root shell on the target machine for authorized penetration…
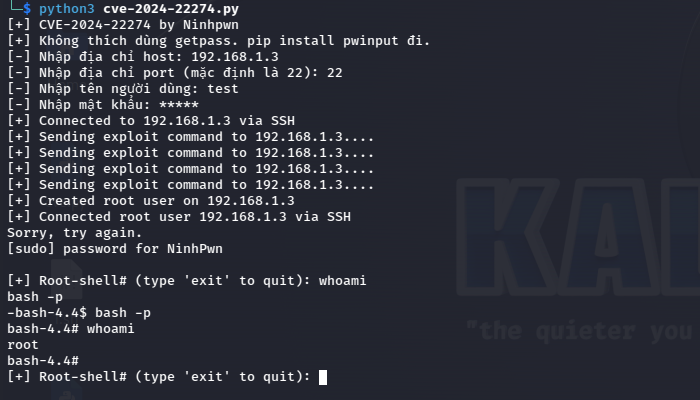 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
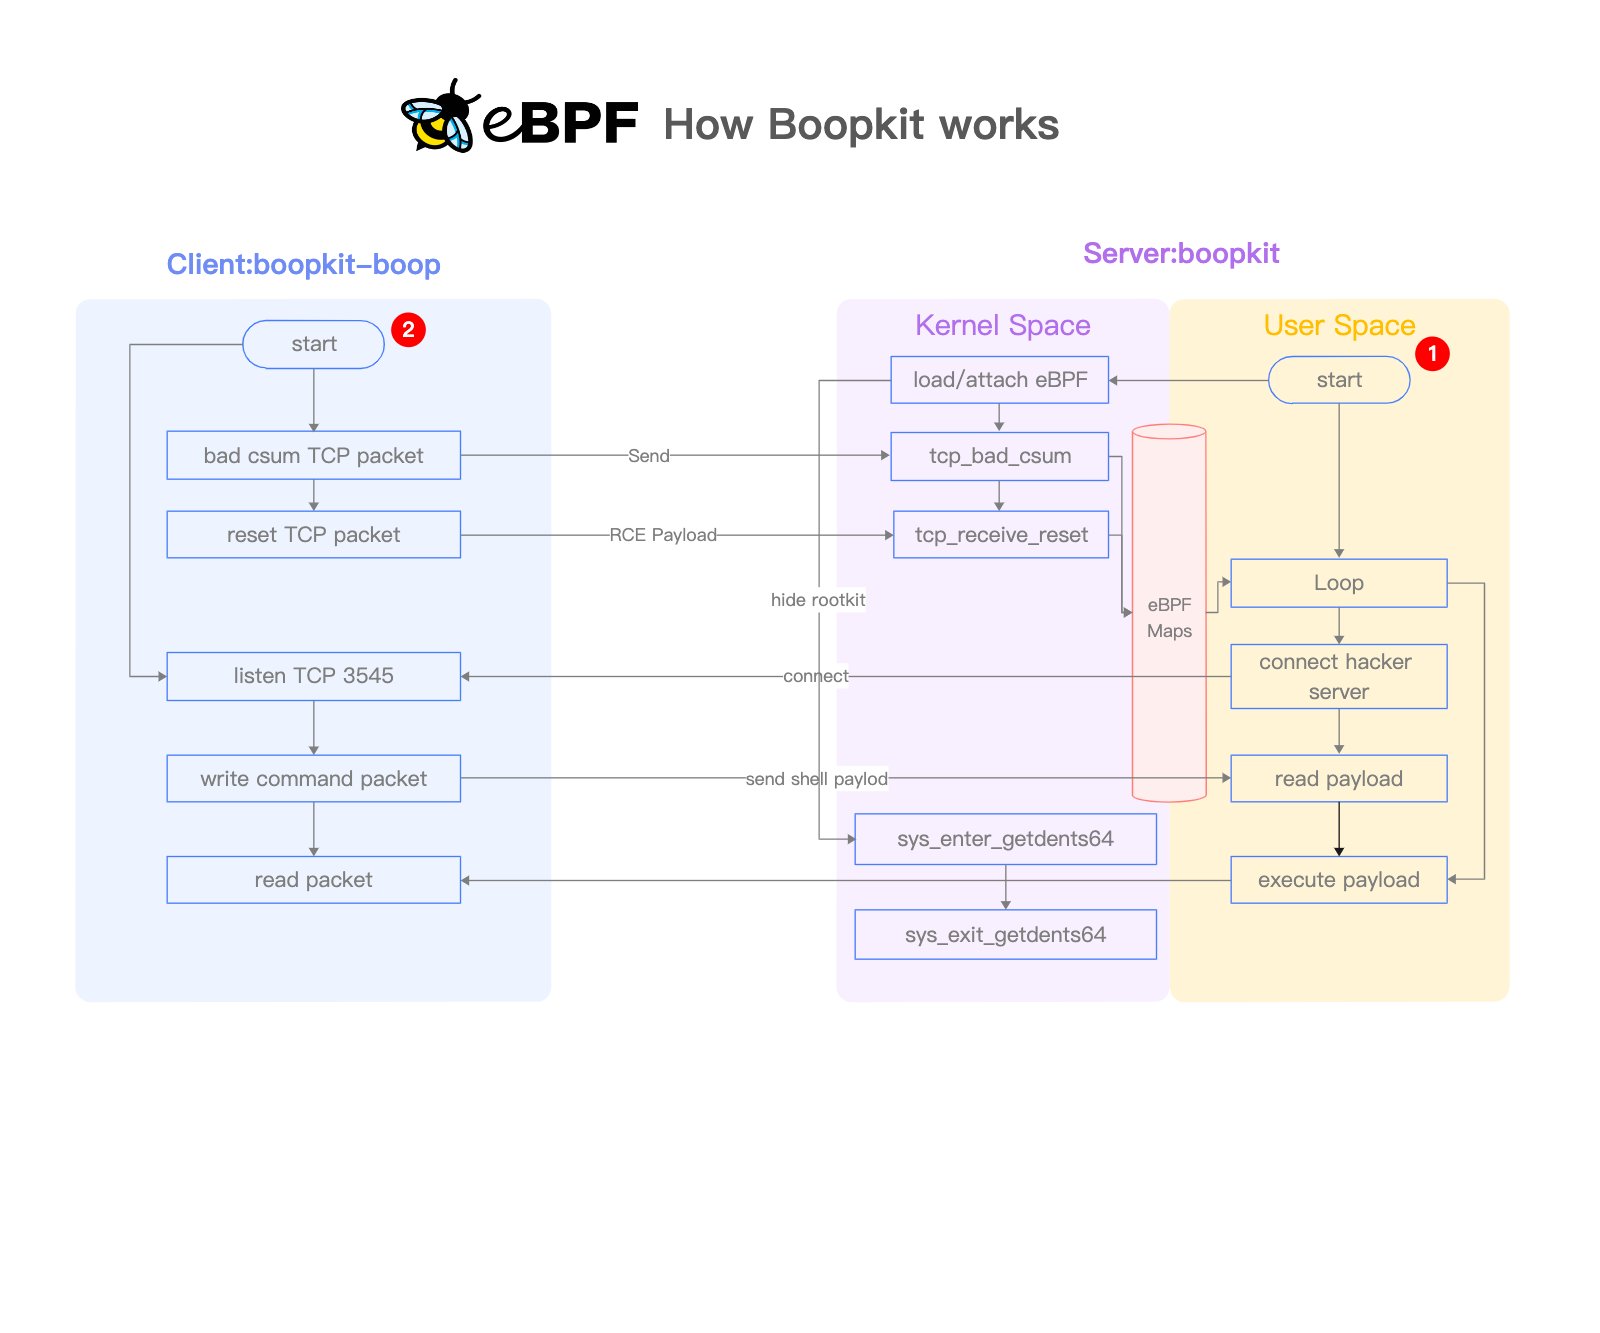 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 matlink/cve-2018-17961
Exploit for CVE-2018-17961 targeting evince to bypass execute-only permissions and achieve privilege escalation via ~/.bashrc injection.
 m0r4a/cve-2026-6018-9-local-privilege-escalation-chain
Exploit chain for local privilege escalation on SUSE Linux, chaining PAM environment injection and a udisks2 race condition to obtain a root shell.
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 syedhafiz1234/cve-2023-34039
CVE-2023-34039