

Certify
 ghostpack/certify
C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
authentication-authorizationexploitationpenetration-testing+3
2.0k
ghostpack/certifyC# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 phillips321/adaudit
Powershell script to do domain auditing automation
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
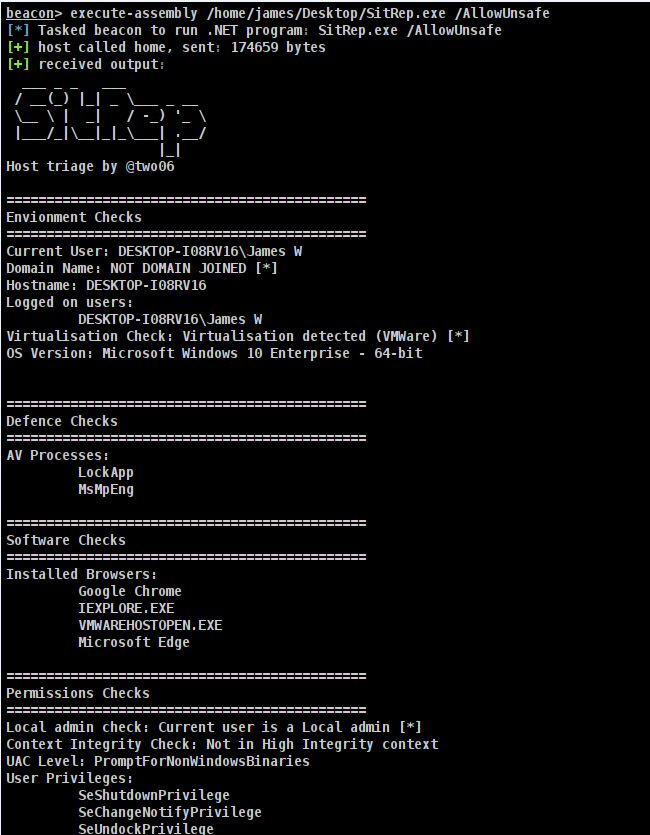 mdsecactivebreach/sitrep
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…
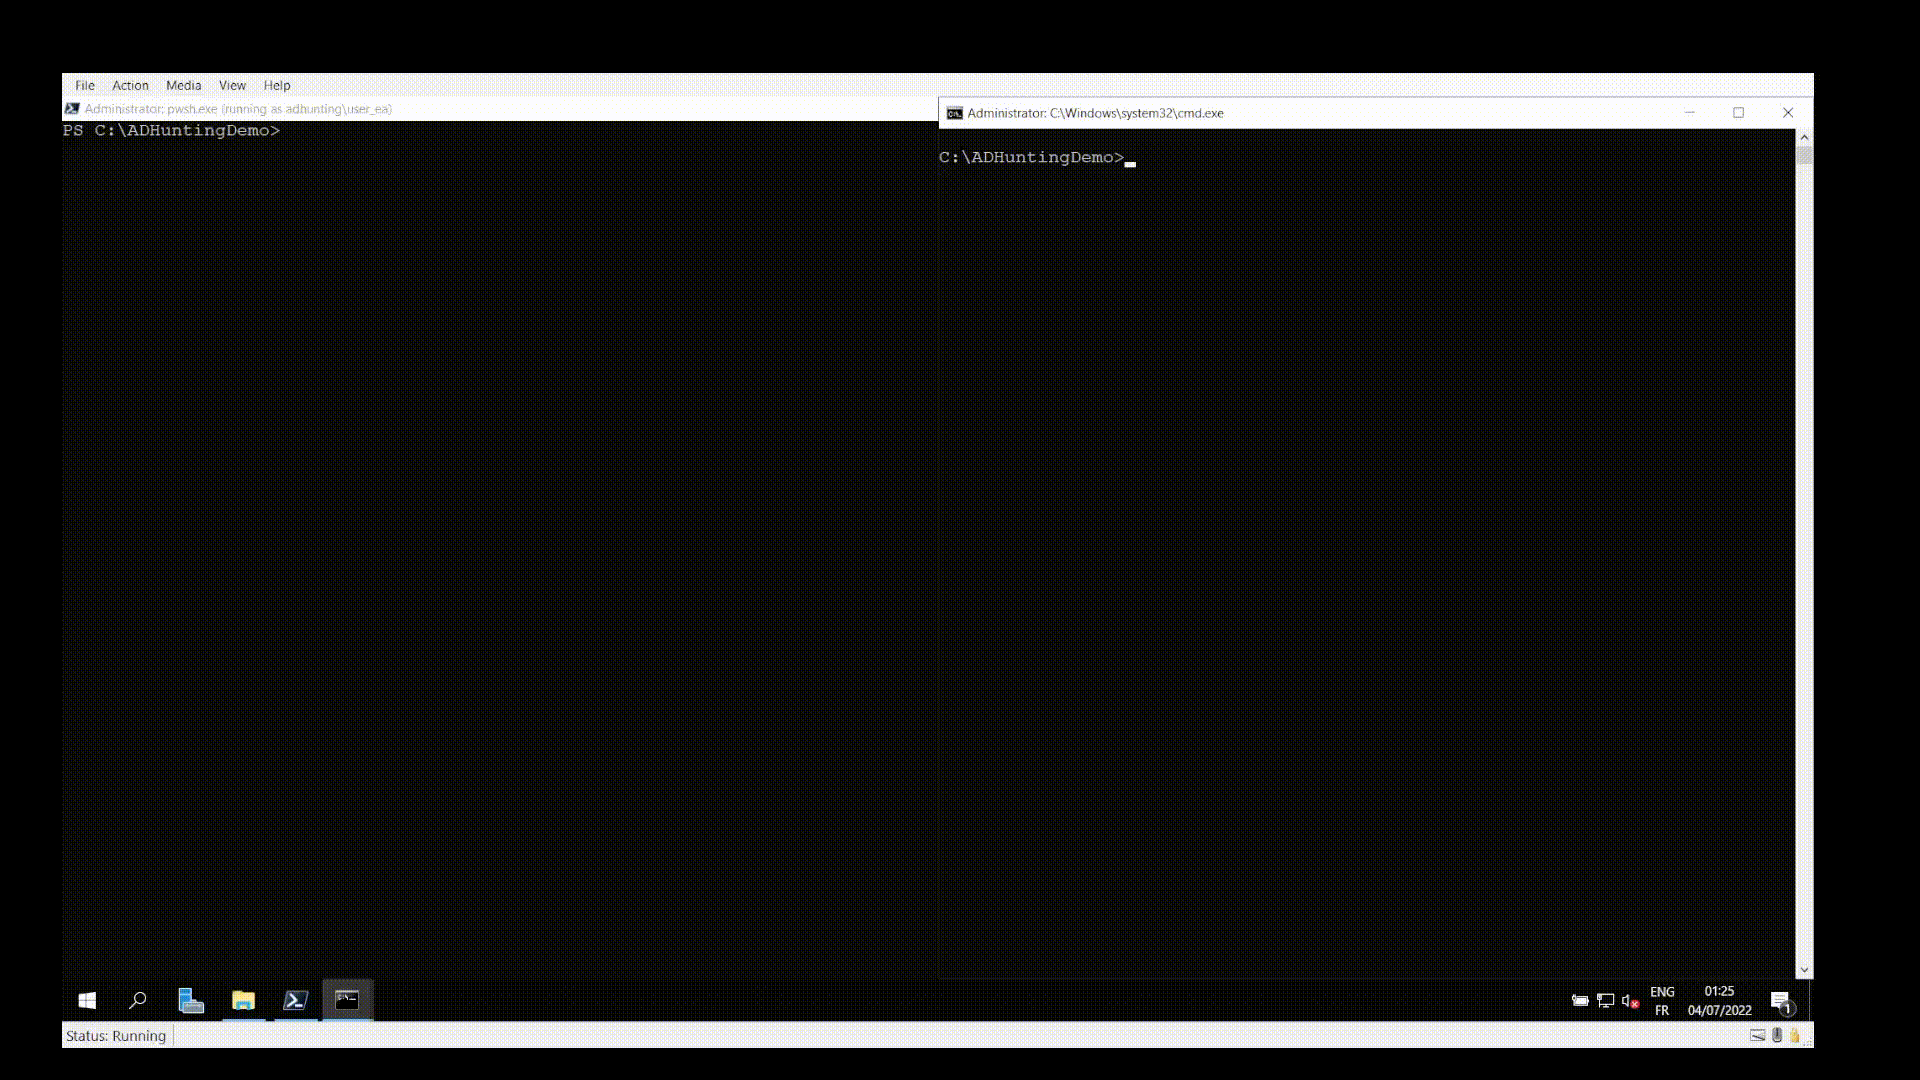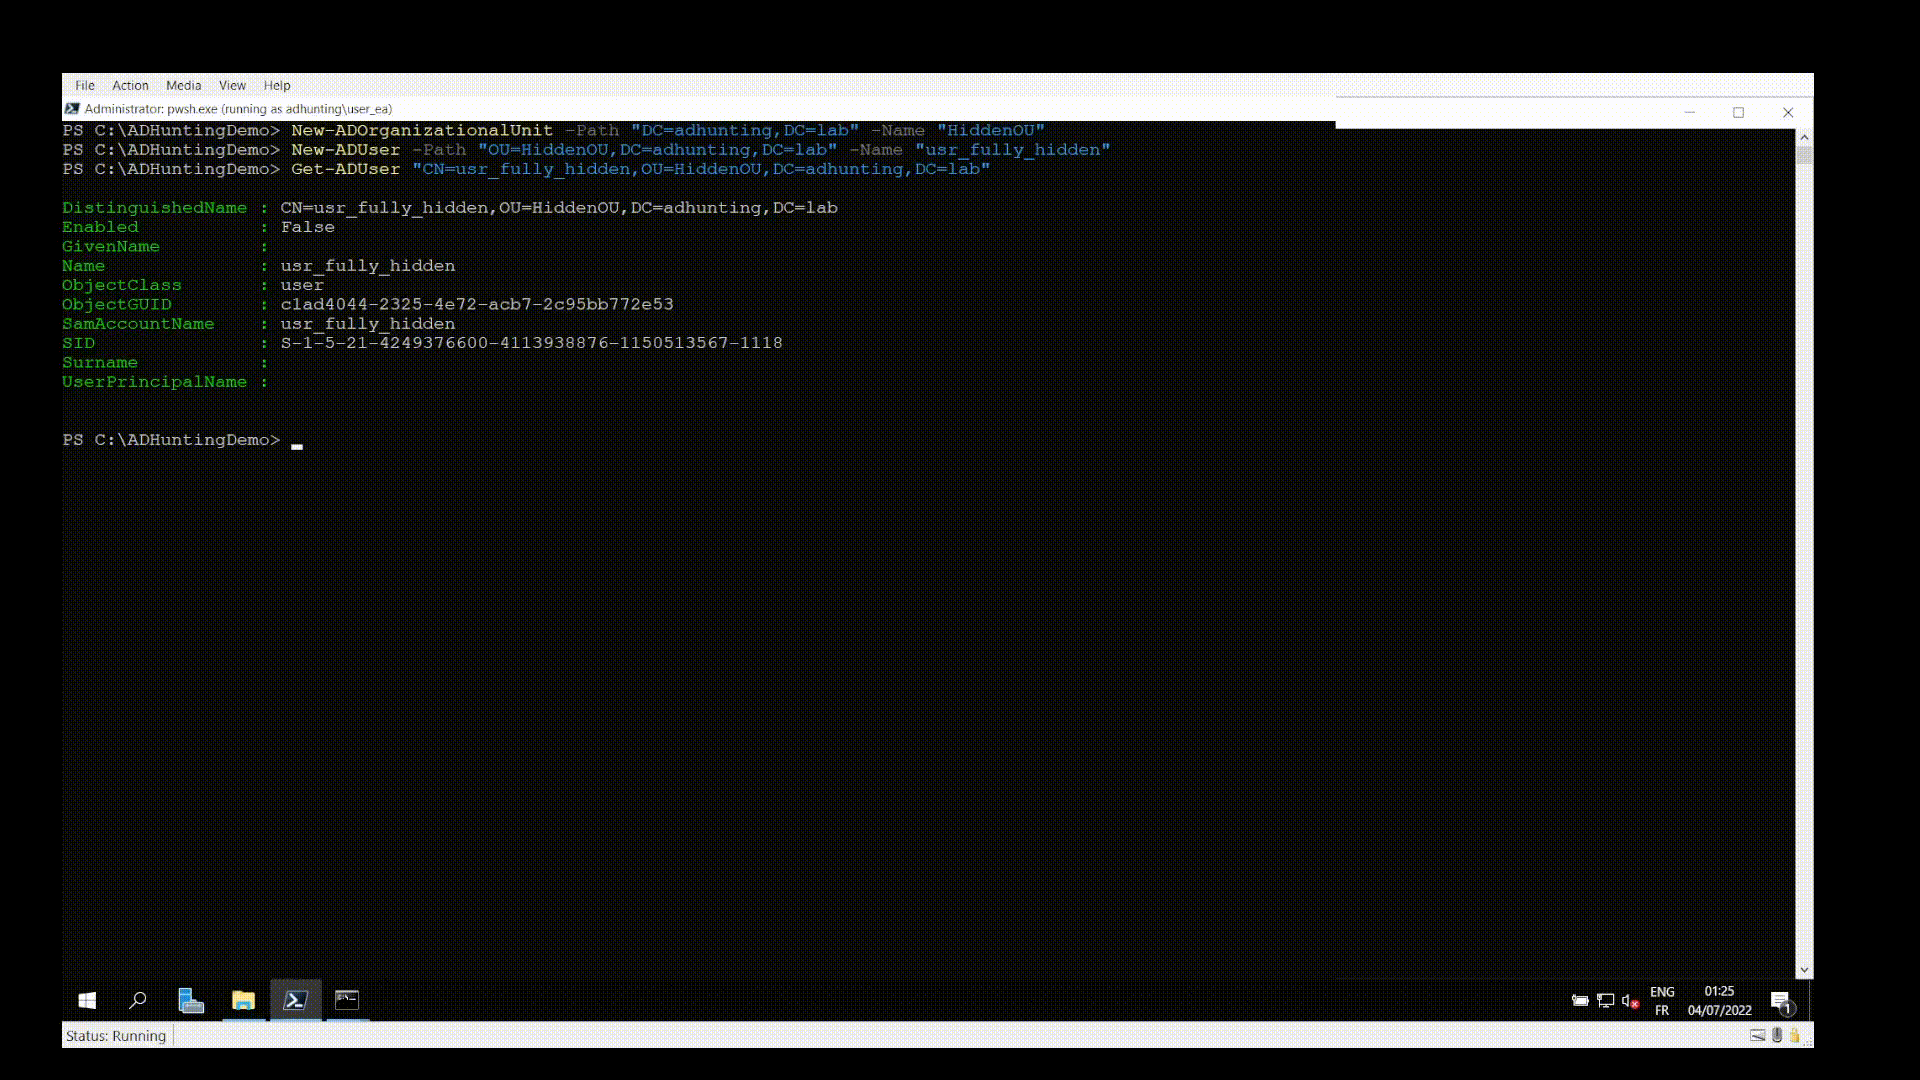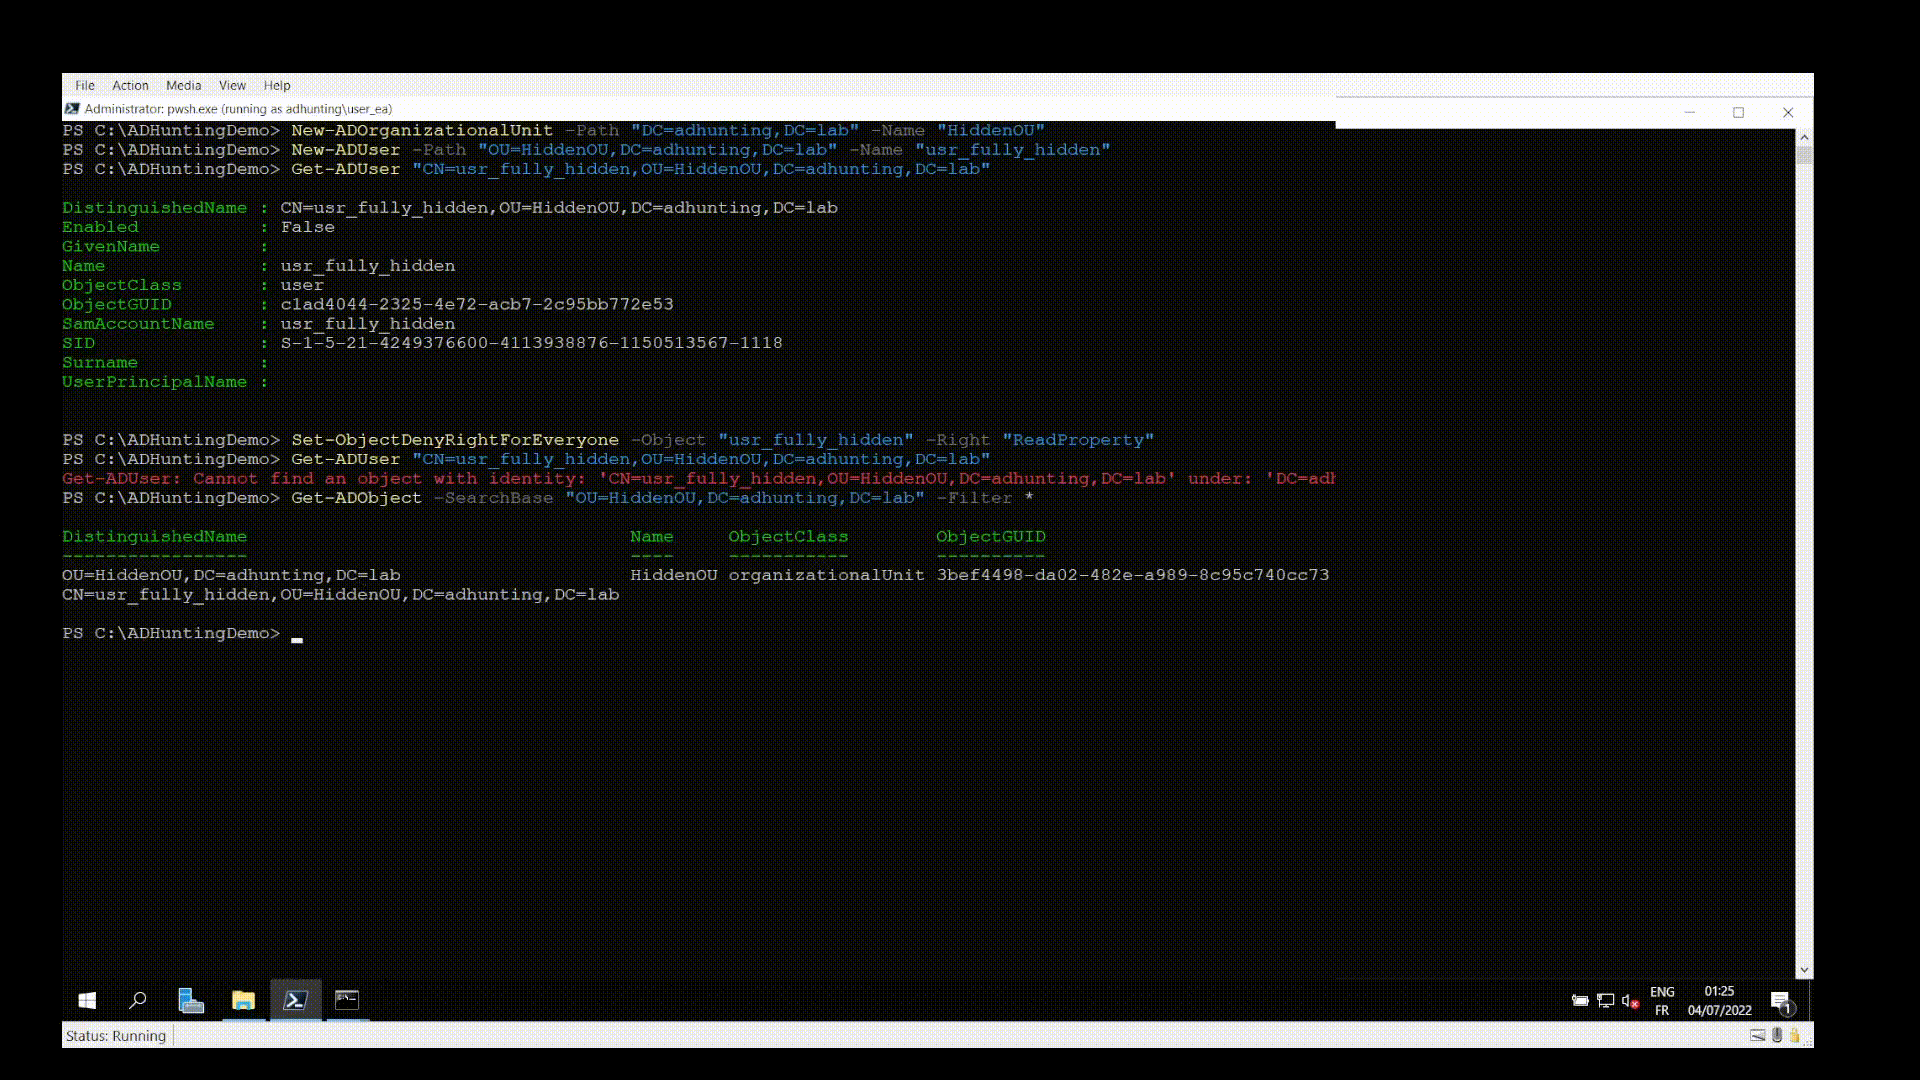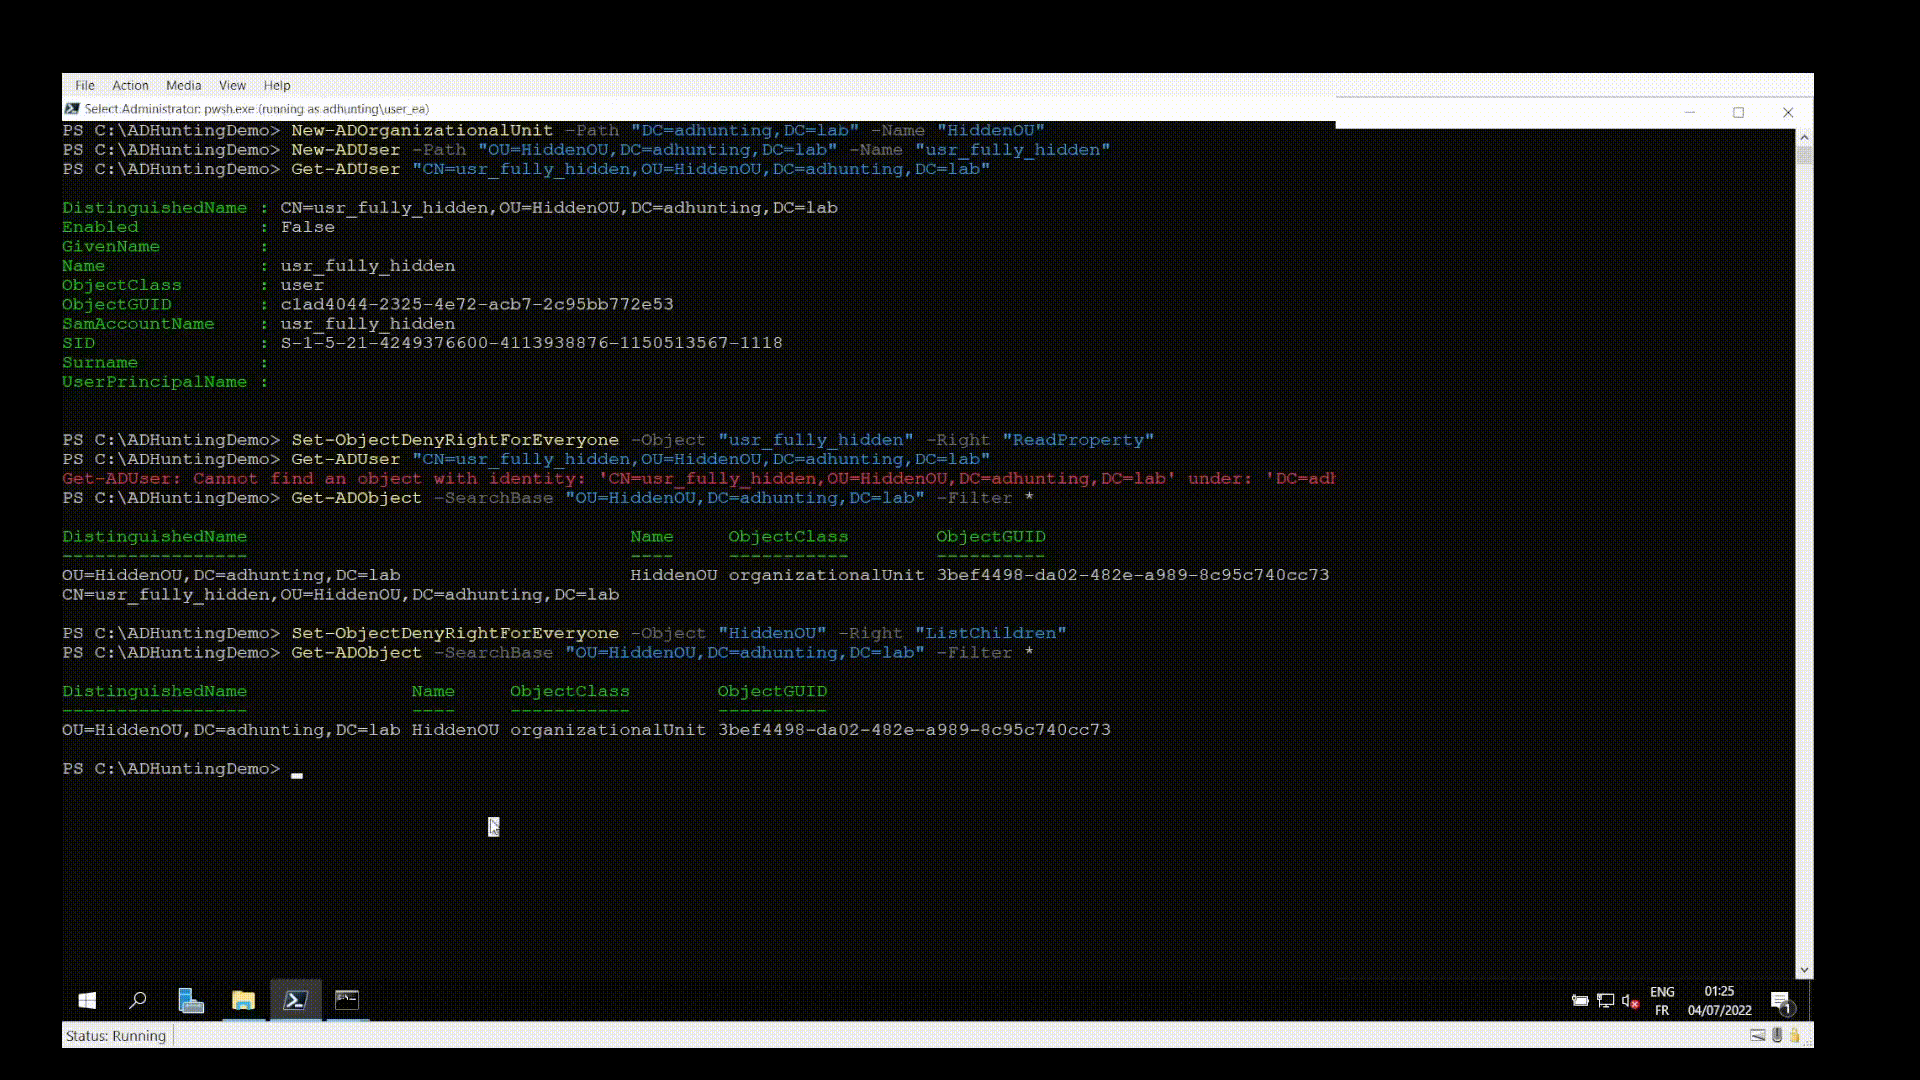 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
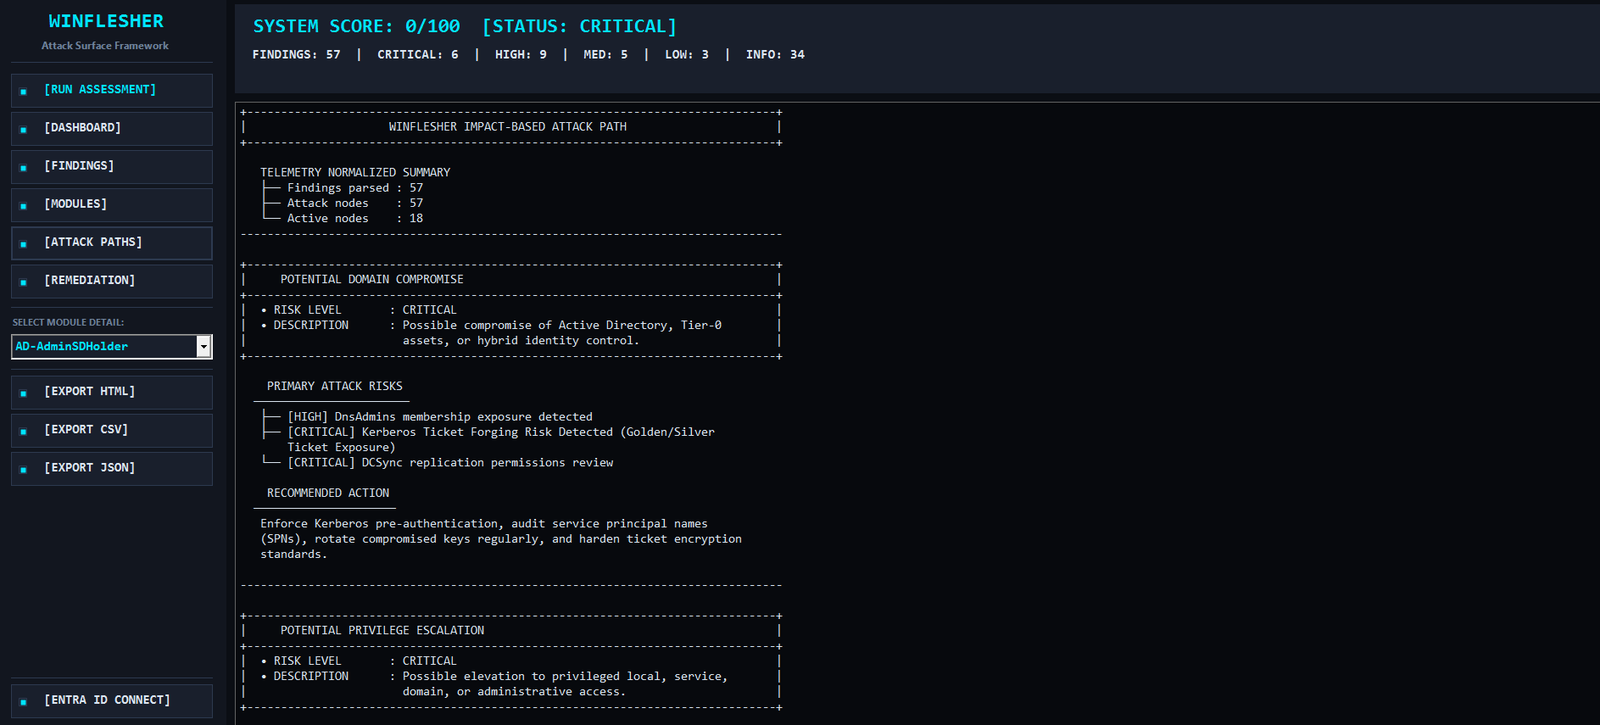 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
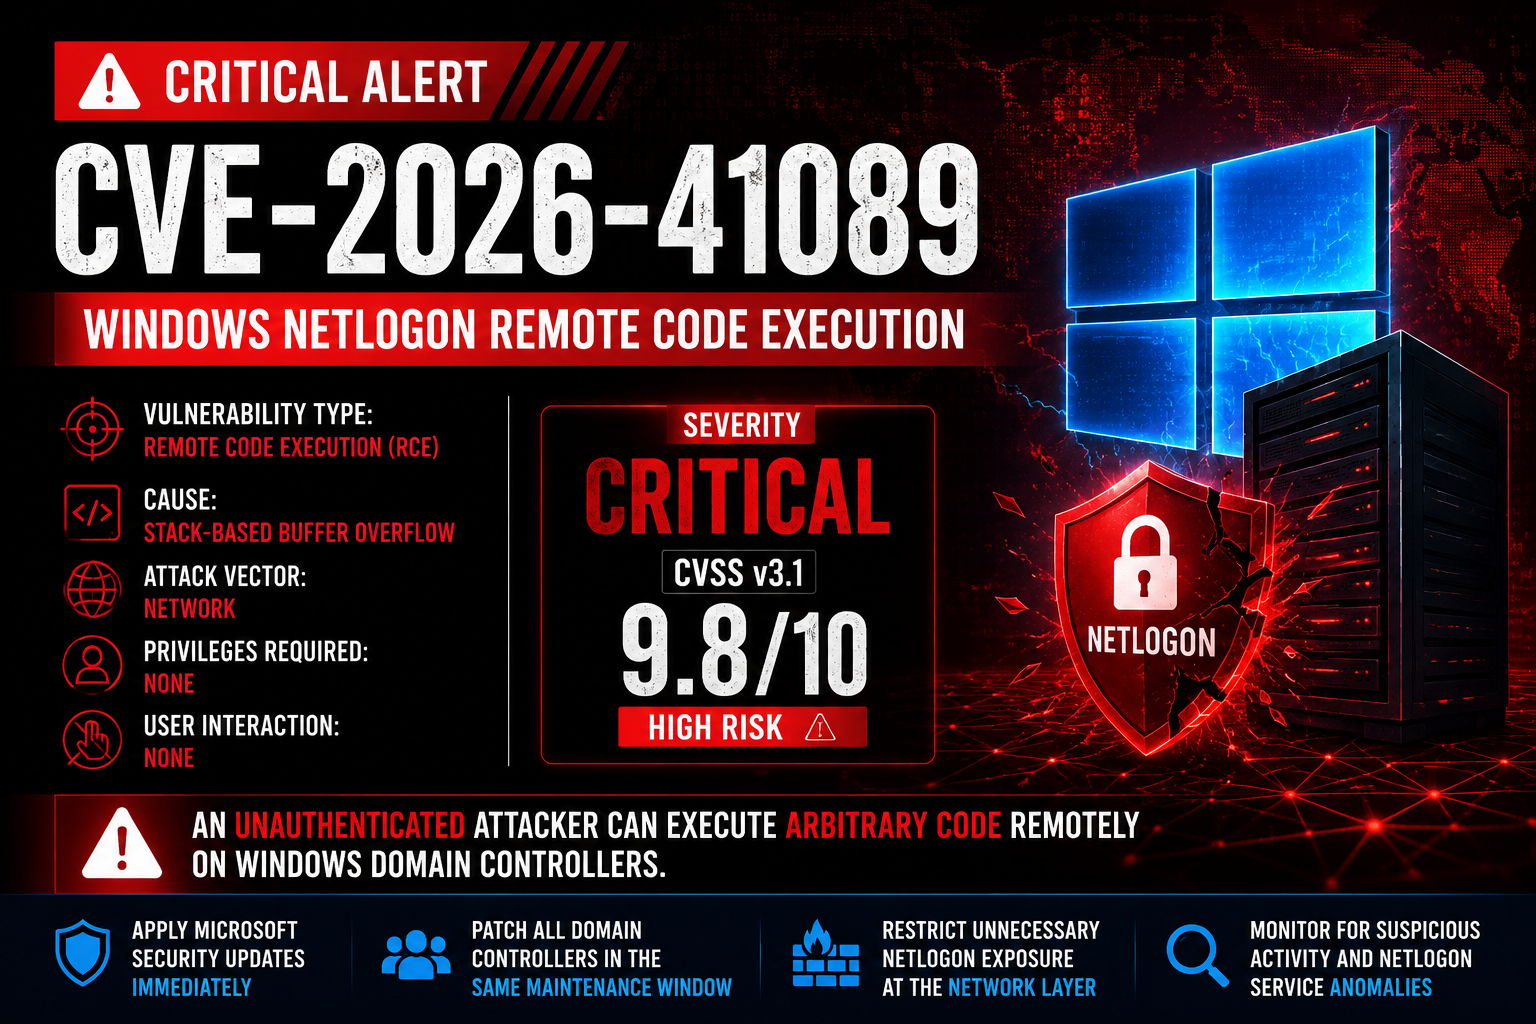 hydrasoft/cve-2026-41089-netlogon-rce
Technical analysis and Proof-of-Concept (PoC) for CVE-2026-41089, a critical unauthenticated Remote Code Execution (RCE) vulnerability in the Windows…
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 opensource-arrozconpollo191/cve-2026-41089-netlogon-rce
Scan Windows Domain Controllers for CVE-2026-41089 to detect unauthenticated remote code execution vulnerabilities in the Netlogon service.
 bariskizilkaya/cve-2022-20186_ctxz
Exploit for CVE-2022-20186 in Arm Mali kernel driver, achieving arbitrary kernel code execution from untrusted app domain to disable SELinux and gain…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…