

FolkPatch
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
android-securitymobile-securitypayload-development+3
1.3k
lyravoid/folkpatchRoot access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)

 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 snothin/ghostlock-s26
GhostLock (CVE-2026-43499) for the Galaxy S26
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
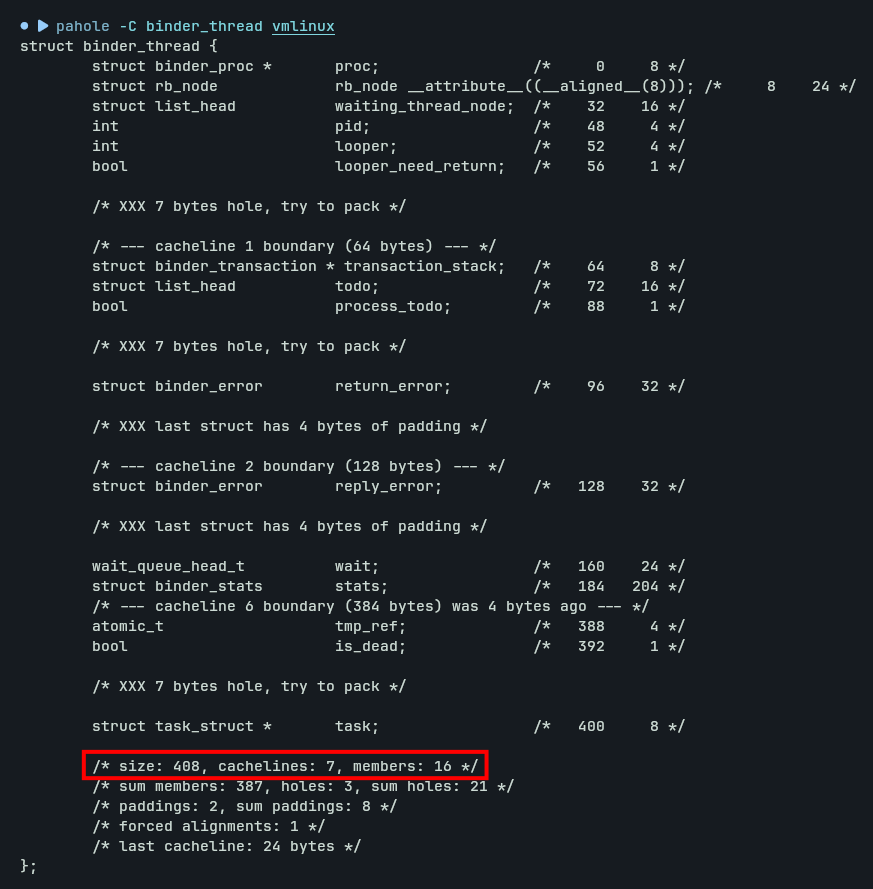 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 xiaobailovesstirring/cve-2026-0013-poc
CVE-2026-0013 Android EoP PoC - Compiled artifacts for security research (Derivative of inforcqb/cve-2026-0013-exploit)
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 camsshaft/ionstack-s22-cve-2026-43499
Android kernel exploit for Samsung Galaxy S22 that gains kernel-domain root via CVE-2026-43499, with SELinux permissive, device-specific kallsyms,…
 camsshaft/selinux-permissive-only-cve-2025-21479
This is an SELinux permissive version of the Cheese exploit also known as CVE-2025-21479 which affected the adreno kgsl on many devices including…
 petalrain224/cve-2026-43499-redmi-turbo5
Use CVE-2026-43499 on Redmi Turbo 5 to escalate privilege
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 soralis0912/cve-2026-43499-aristotle
Local privilege escalation exploit for Xiaomi XIG04 (Android 12) via CVE-2026-43499 kernel use-after-free. Data-only direct-root technique with MTE…