

Magisk
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
android-securitymobile-securityprivilege-escalation
topjohnwu/magiskAndroid customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 coactionbrittlemaidenhair51/cve-2026-42978-poc-research
Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
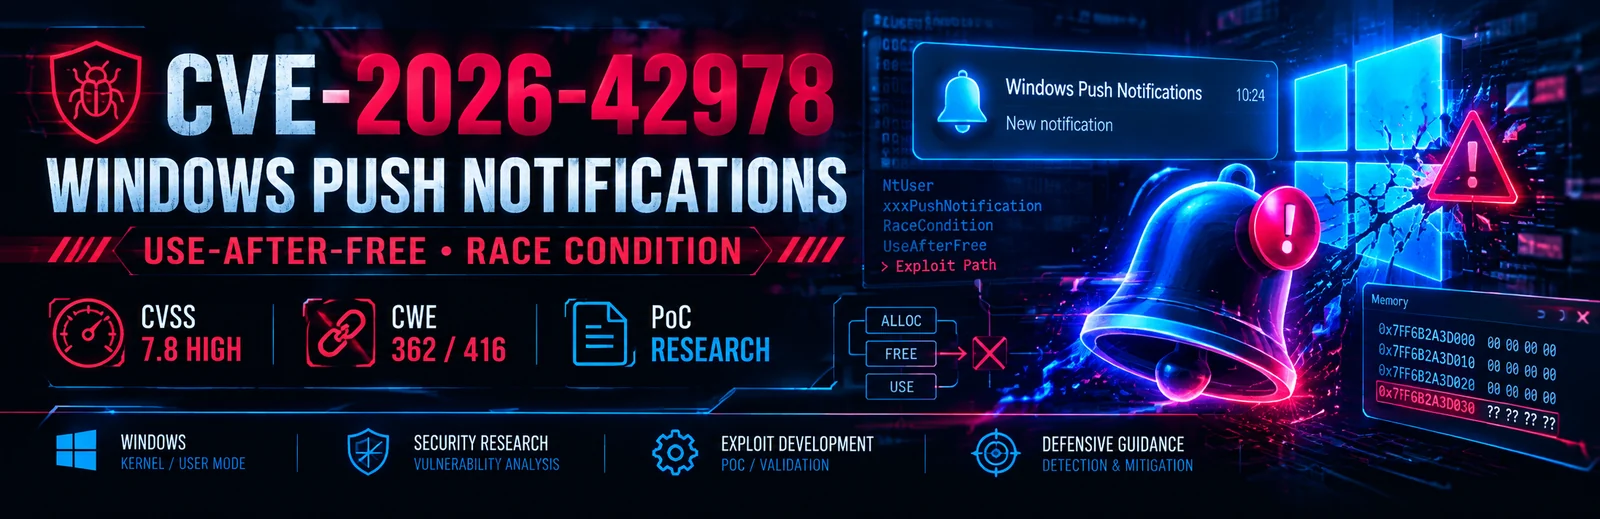 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 r3vpwnx/cve-2025-57819
Unauthenticated SQL injection to RCE exploit for FreePBX 16 Endpoint Manager (CVE-2025-57819). Demonstrates stacked queries to write a webshell via…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
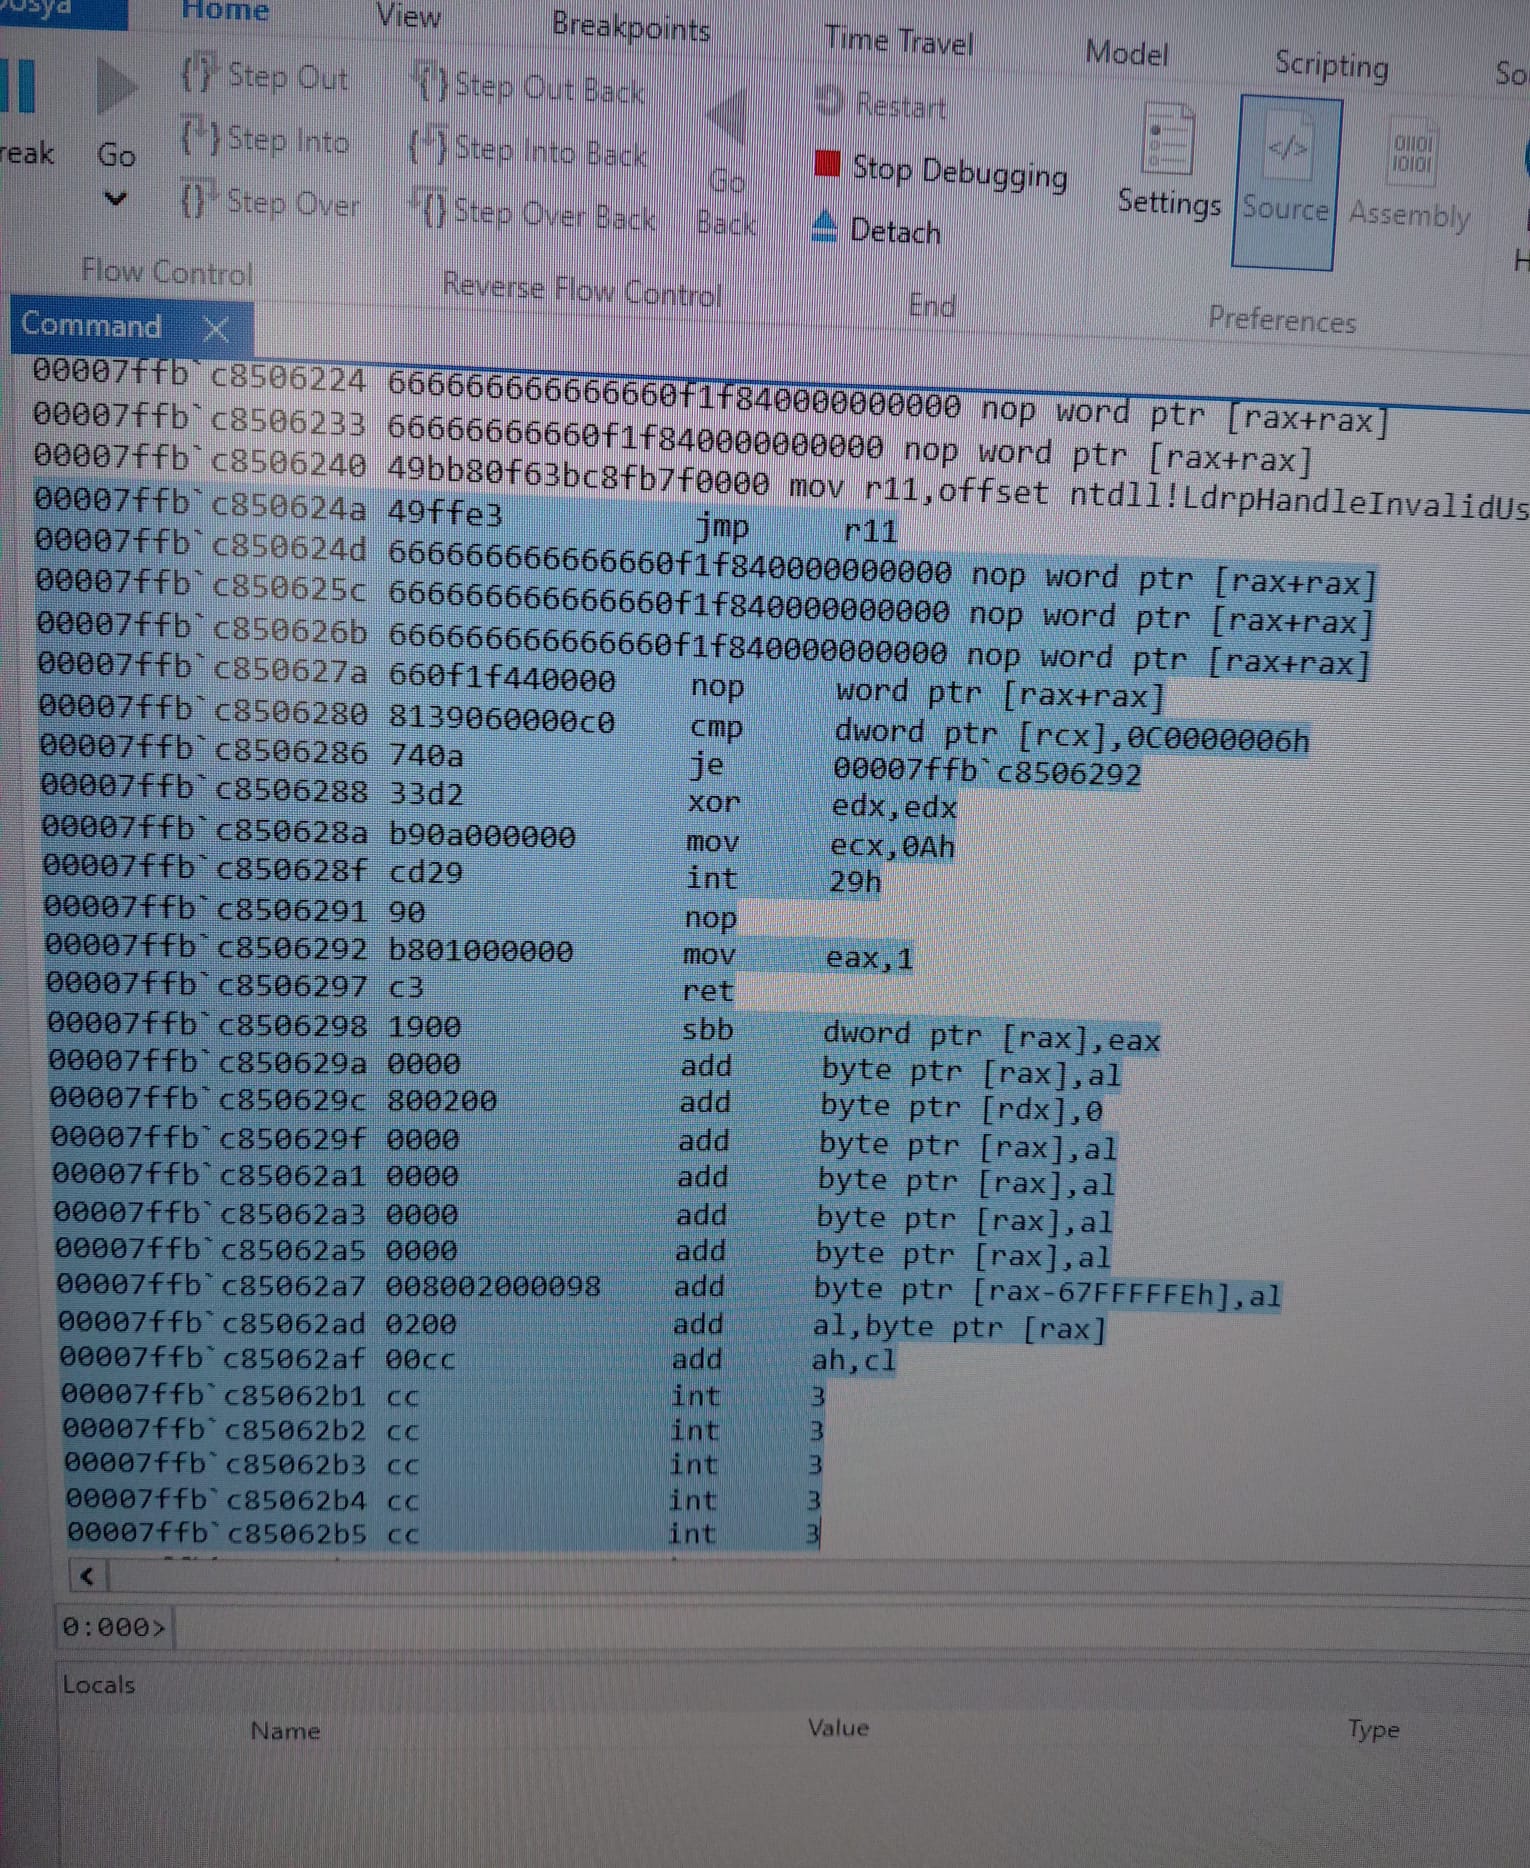 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 m8seven/cve-2026-11837-ansible-posix-authorized-key
CVE-2026-11837: local privilege escalation in the ansible.posix authorized_key module via symlink-following chown. Technical writeup; sibling of…
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 ryan2929/cve-2026-31431
Public exploit for a Linux kernel zero-day (CVE-2026-31431) enabling local privilege escalation to root on distributions since 2017. Includes a…
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…