

SUID3NUM
 anon-exploiter/suid3num
A standalone python script which utilizes python's built-in modules to enumerate SUID binaries, separate default binaries from custom binaries,…
exploitationinformation-gatheringpenetration-testing+2
678
anon-exploiter/suid3numA standalone python script which utilizes python's built-in modules to enumerate SUID binaries, separate default binaries from custom binaries,…
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
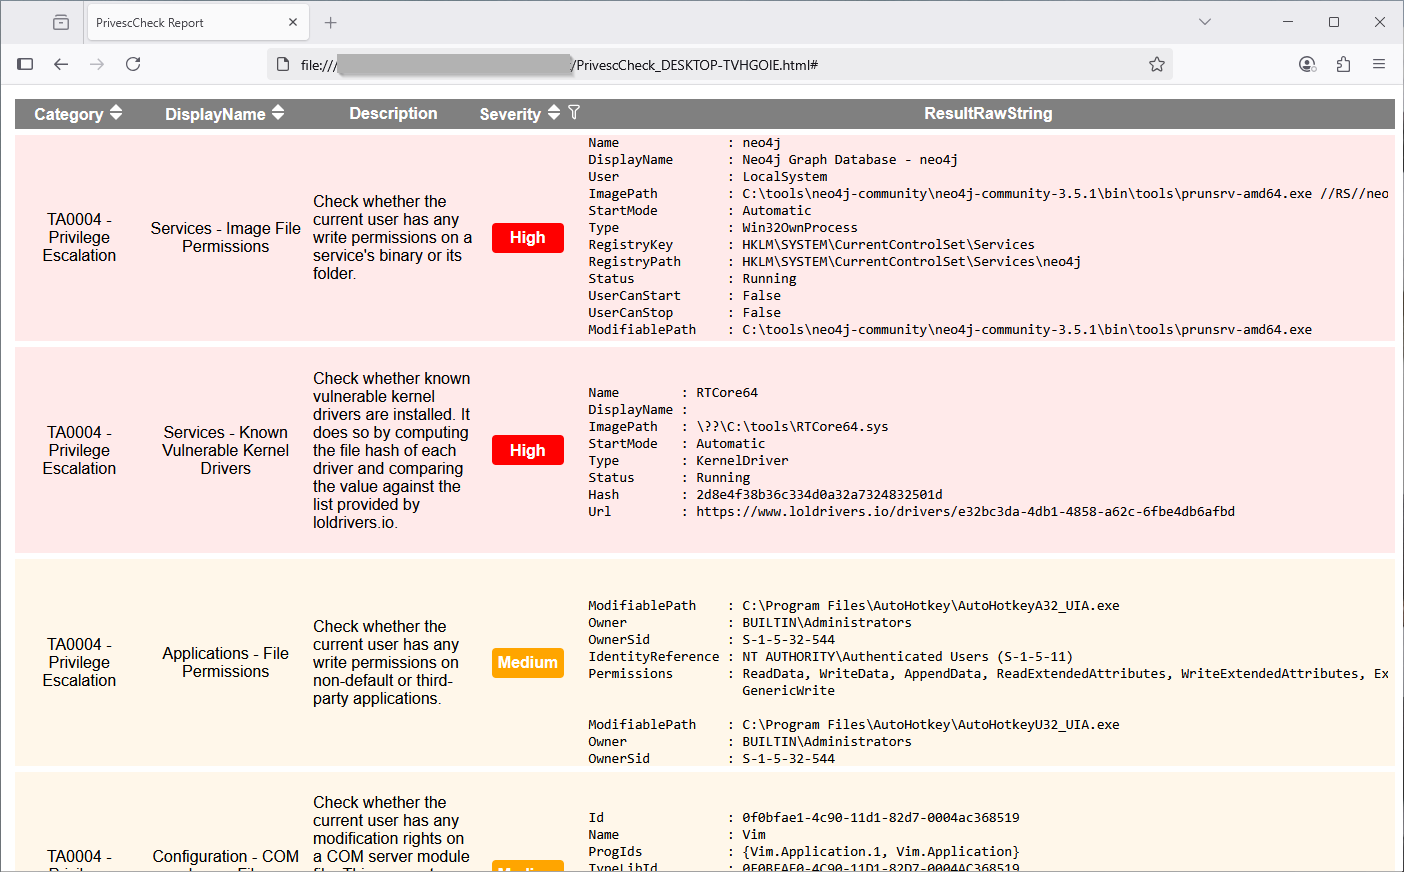 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 hika-sec/terminator_killer
Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT