

BloodHound
 specterops/bloodhound
Six Degrees of Domain Admin
defensive-toolsidentity-access-managementinformation-gathering+4
specterops/bloodhoundSix Degrees of Domain Admin
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 aish19siddiqua-commits/mtechweek_04
Documented penetration test on an isolated Metasploitable2 VM using Metasploit and Nmap, covering remote exploitation, privilege escalation, and…
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 niker-lixy/postex
Windows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…
 twosevenonet/edrchoker
A tool uses the QoS Policy (Pacer.sys) to throttle Endpoint Detection and Response (EDR) agents from connecting to the server.
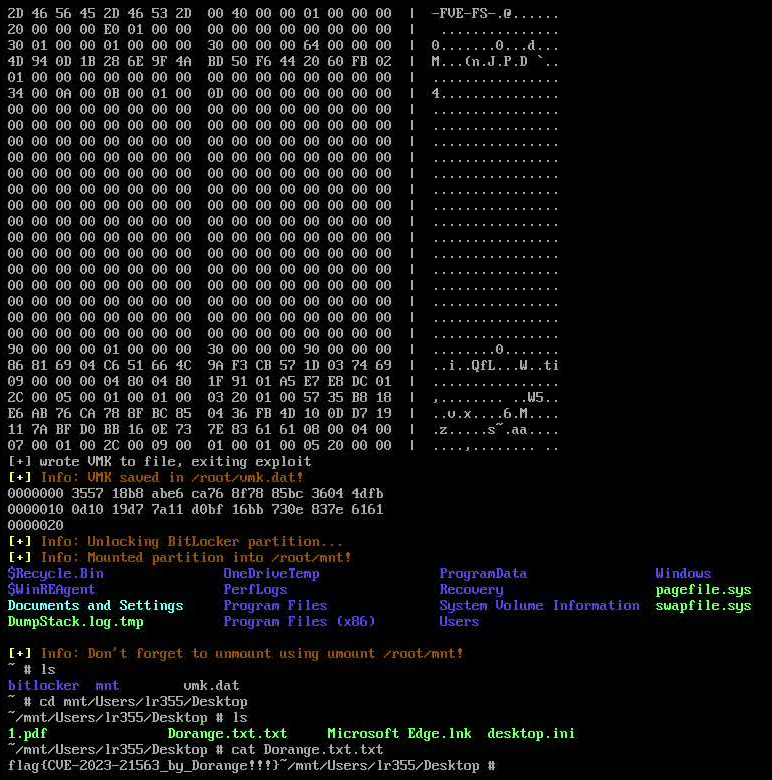 lr2006-robot/bitpixie
Cracking BitLocker encryption based on CVE-2023-21563 vulnerability
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
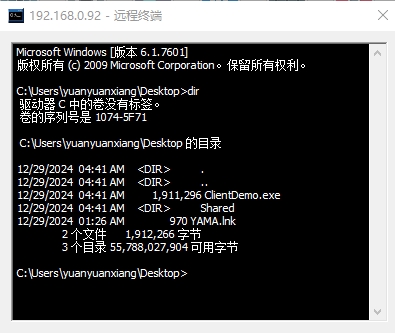 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
 var77/cve-2026-2005
PoC for CVE-2026-2005
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 rana-ali93/cve-2021-3156-sudo-buffer-overflow-linux
Red Team exploitation of CVE-2021-3156 (Baron Samedit) – Heap Buffer Overflow in Sudo leading to Local Privilege Escalation on Ubuntu 20.04
 zedocun/soc-investigation-powershell-edrfreeze
SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…