
PurplePanda
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
cloud-securityinformation-gatheringpenetration-testing+3
719
carlospolop/purplepandaIdentify privilege escalation paths within and across different clouds
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
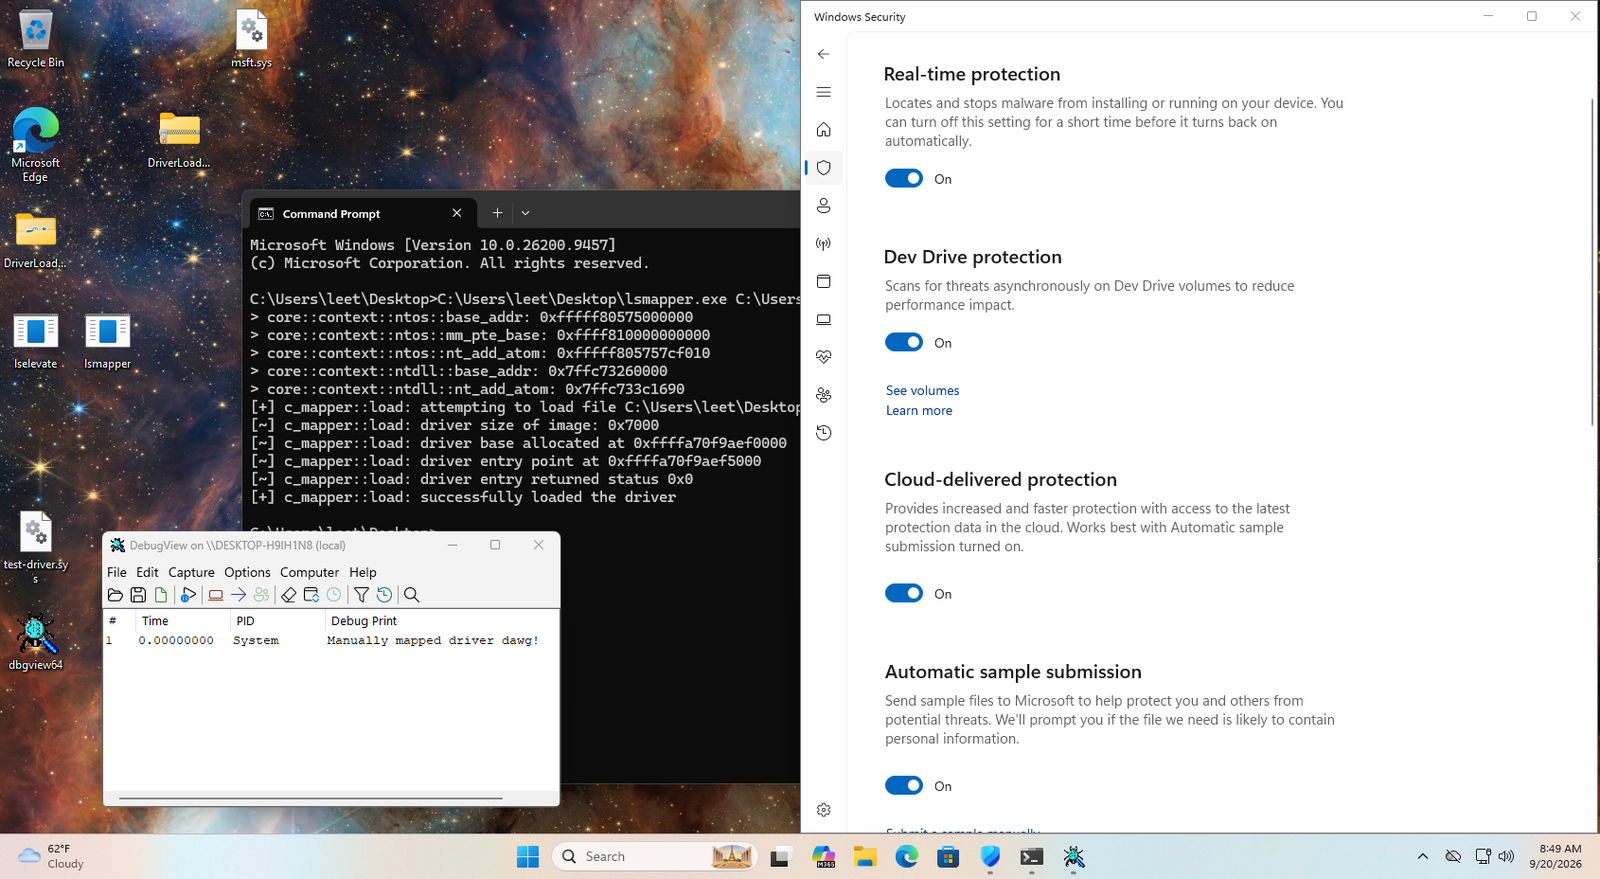 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 blacksnufkin/byovd
BYOVD research use cases featuring vulnerable driver discovery and reverse engineering methodology. (CVE-2025-52915, CVE-2025-1055, CVE-2026-3609,…
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 fuzzlove/sparstanboogie
Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…
 mariohy/cve_2026_31431_audit
A security auditing toolkit for CVE-2026-31431 vulnerability research
 azureadtrent/cve-2025-6018-and-cve-2025-6019-privilege-escalation
This is just a quick note on how to exploit these vulnerabilities to get root.
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
 dragosbanica/cve-2023-0386_poc
Proof-of-concept exploit for CVE-2023-0386, a Linux OverlayFS local privilege escalation vulnerability. Demonstrates how incorrect file capability…
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161
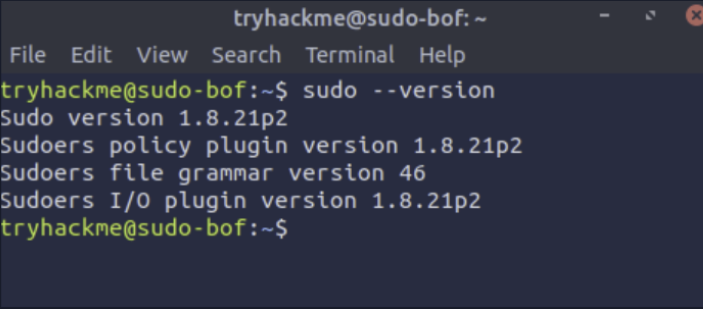 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
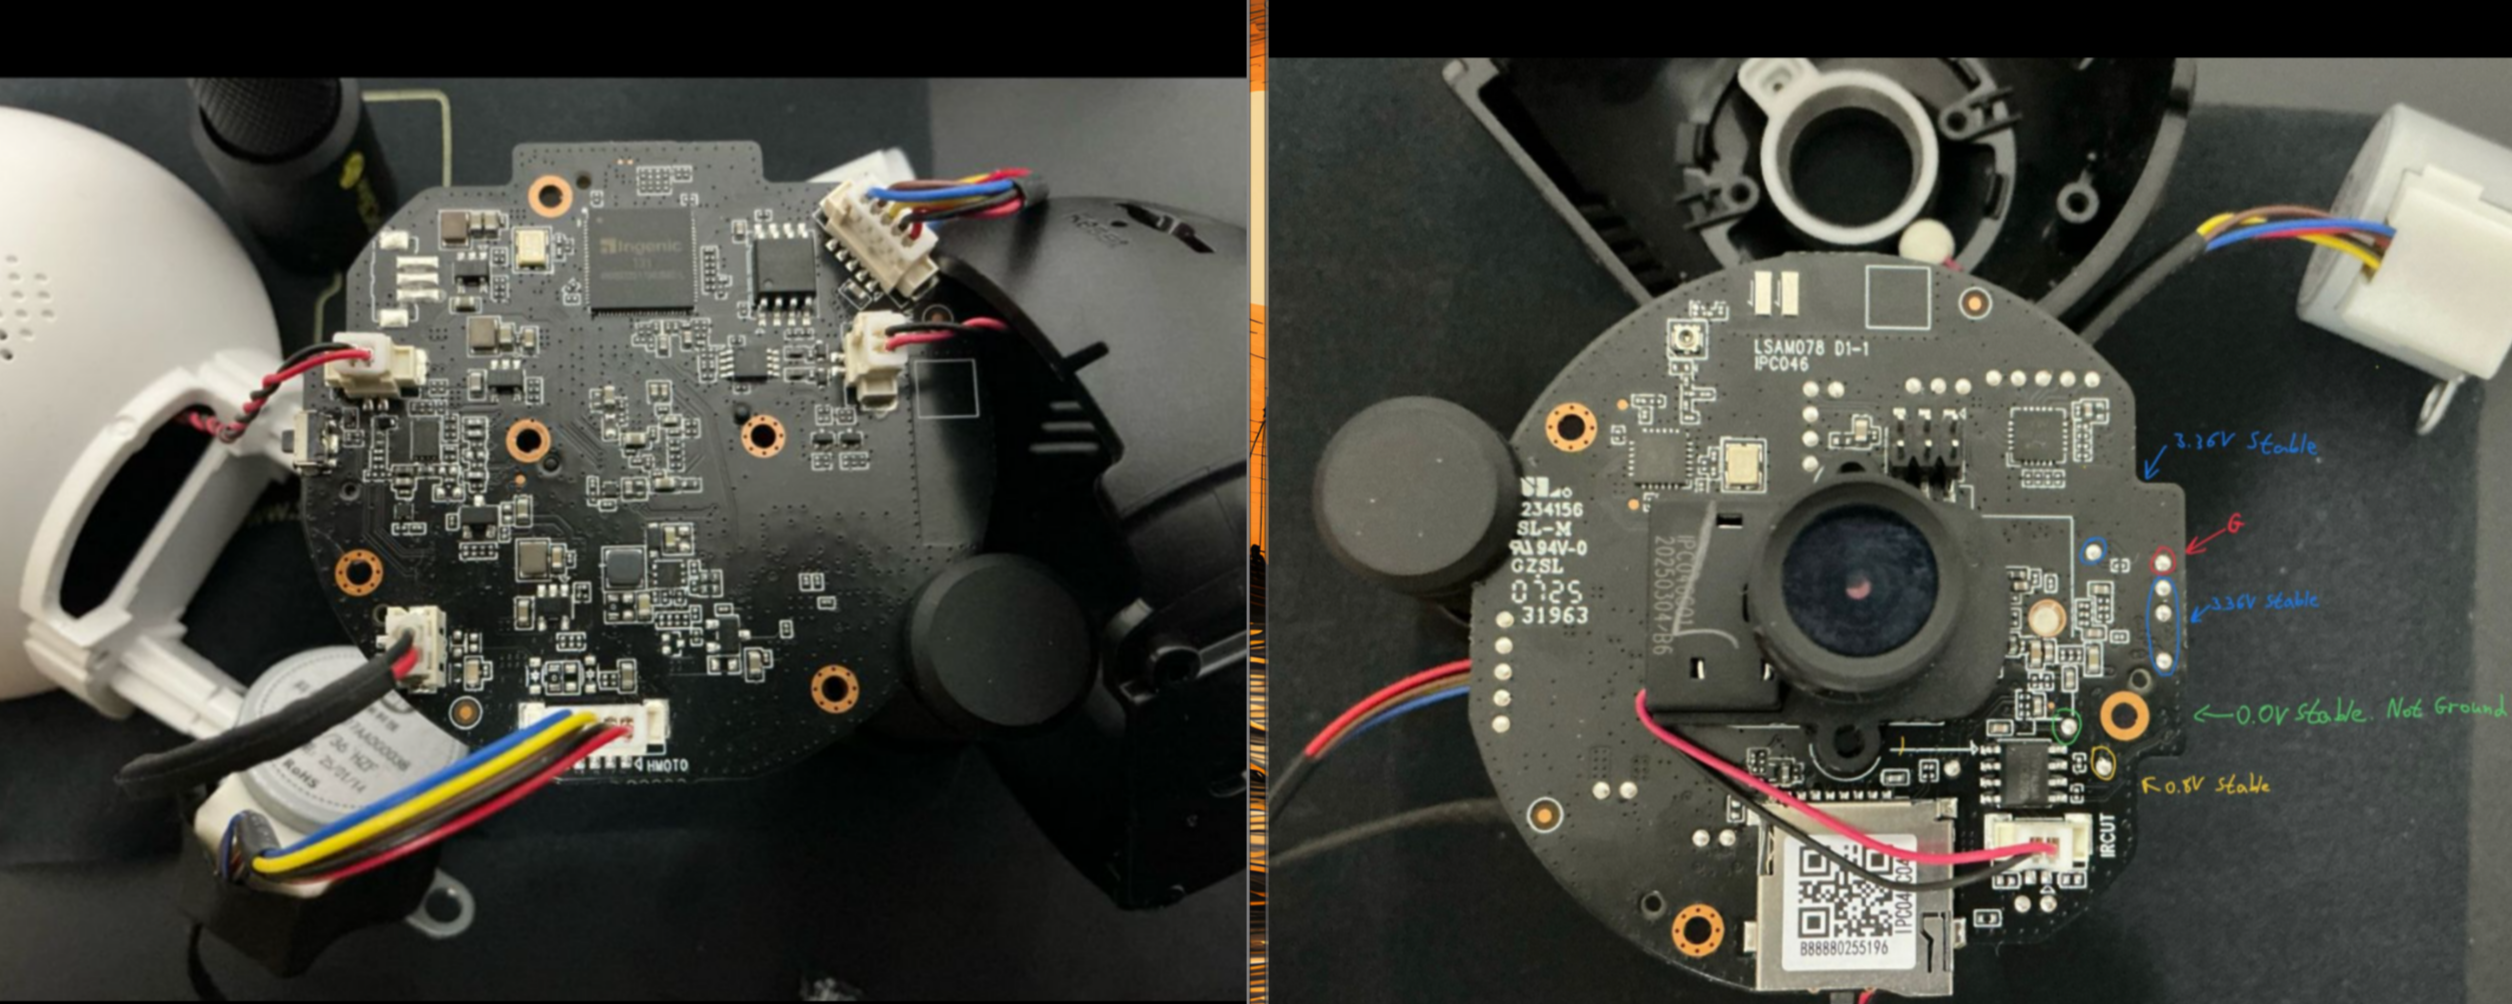 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…