
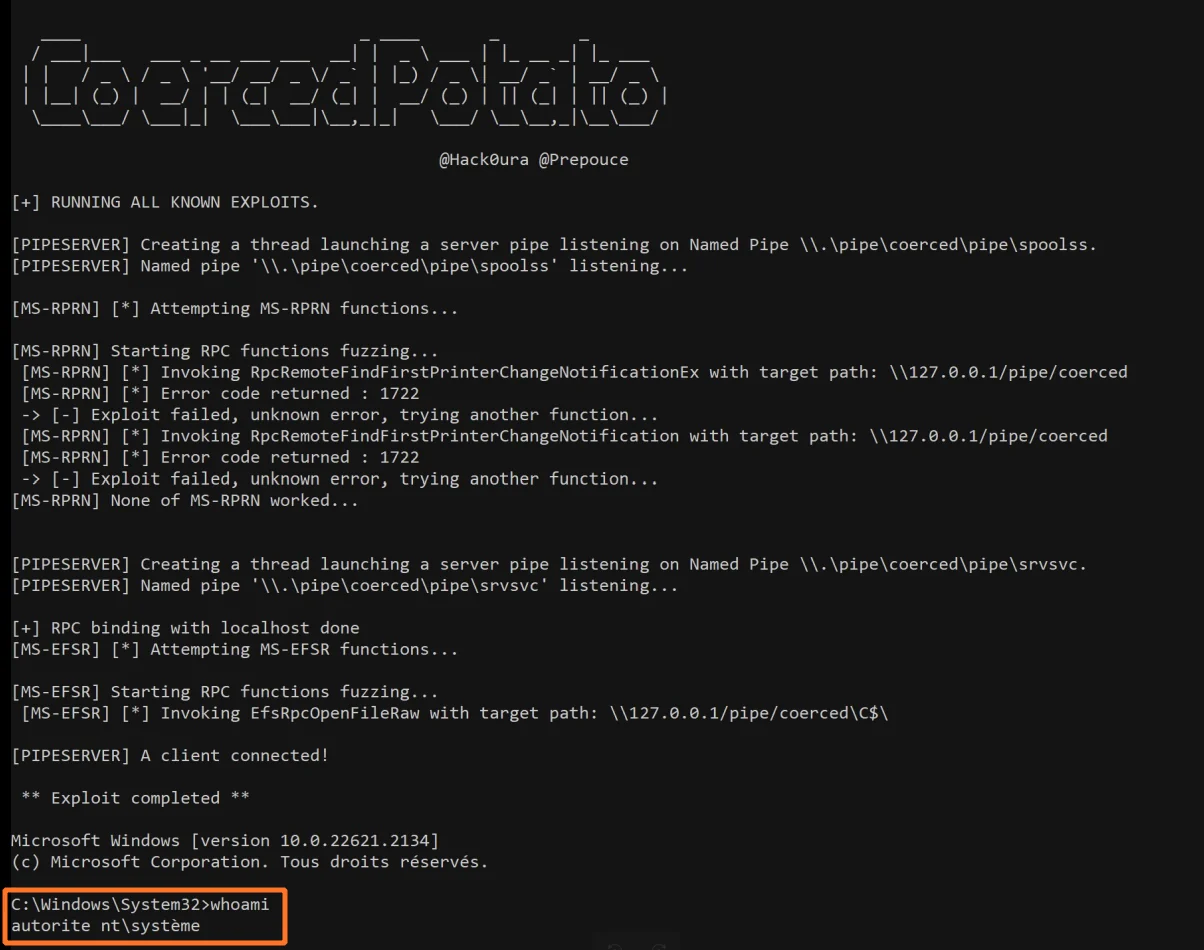
CoercedPotato
 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
exploitationpayload-developmentpenetration-testing+3
401
prepouce/coercedpotatoWindows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 constantinefedorov/review.cve-2021-3156
Python proof-of-concept exploit for CVE-2021-3156 (Baron Samedit), a sudoedit heap overflow enabling local privilege escalation to root on vulnerable…
 sysdopllc/vestacp-config-eval-rce
Security advisory: VestaCP <= 0.9.8-26 authenticated config-parser eval sinks -> root RCE (ancestor of HestiaCP GHSA-w3mx/cr7q, never disclosed for…
 zhangutah/security-research
Proof-of-concept C code and writeups for disclosed Linux kernel vulnerabilities, including per-CVE exploit sources and technical analysis.
 nt2dev/cve-2026-36213-poc
CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation
 hexbytee/freepbx-sqli-rce
Python proof-of-concept exploiting CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin creation, cron webshell deployment,…
 abraxas/plausible-editor-invite
Plausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid
 abraxas/vbox-guestctrl-copyfrom-dotdot
VirtualBox 7.2.20 - High - Local - File write - Guest Control copy-from DOTDOT
 abraxas/vbox-ovf-href-dest-escape
VirtualBox 7.2.20 - High - Local - File write - OVF href dest escape
 abraxas/vbox-ovf-nat-tftp-prefix
VirtualBox 7.2.20 - High - Local - File read - OVF NAT TFTP empty prefix
 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
 abraxas/pfsense-acb-restore-priv
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - ACB restore
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 abraxas/pfsense-uploadconfig
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - hidden uploadconfig
 abraxas/pfsense-wizard-uid0
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - wizard uid 0
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 ripits-sec/couchpotato
Windows privilege escalation tool that patches ETW and AMSI and uses indirect syscalls to abuse SeImpersonatePrivilege, escalating service accounts…