
pedit-cow
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
binary-exploitationexploitationpayload-development+2
theendofabbys/pedit-cowLinux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 r00t-byte/pwnkit-cve-2021-4034-lpe
PwnKit - polkit pkexec Local Privilege Escalation <= 0.105-31
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 0xf9b6a41ec/cve-2026-69328
Windows privilege escalation exploit that plants SprintCSP.dll in a user-writable HKLM PATH directory to hijack StorSvc and execute as SYSTEM.
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
 goldendivider/cve-2026-6471-postgres-logical-decoding-dlopen
Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
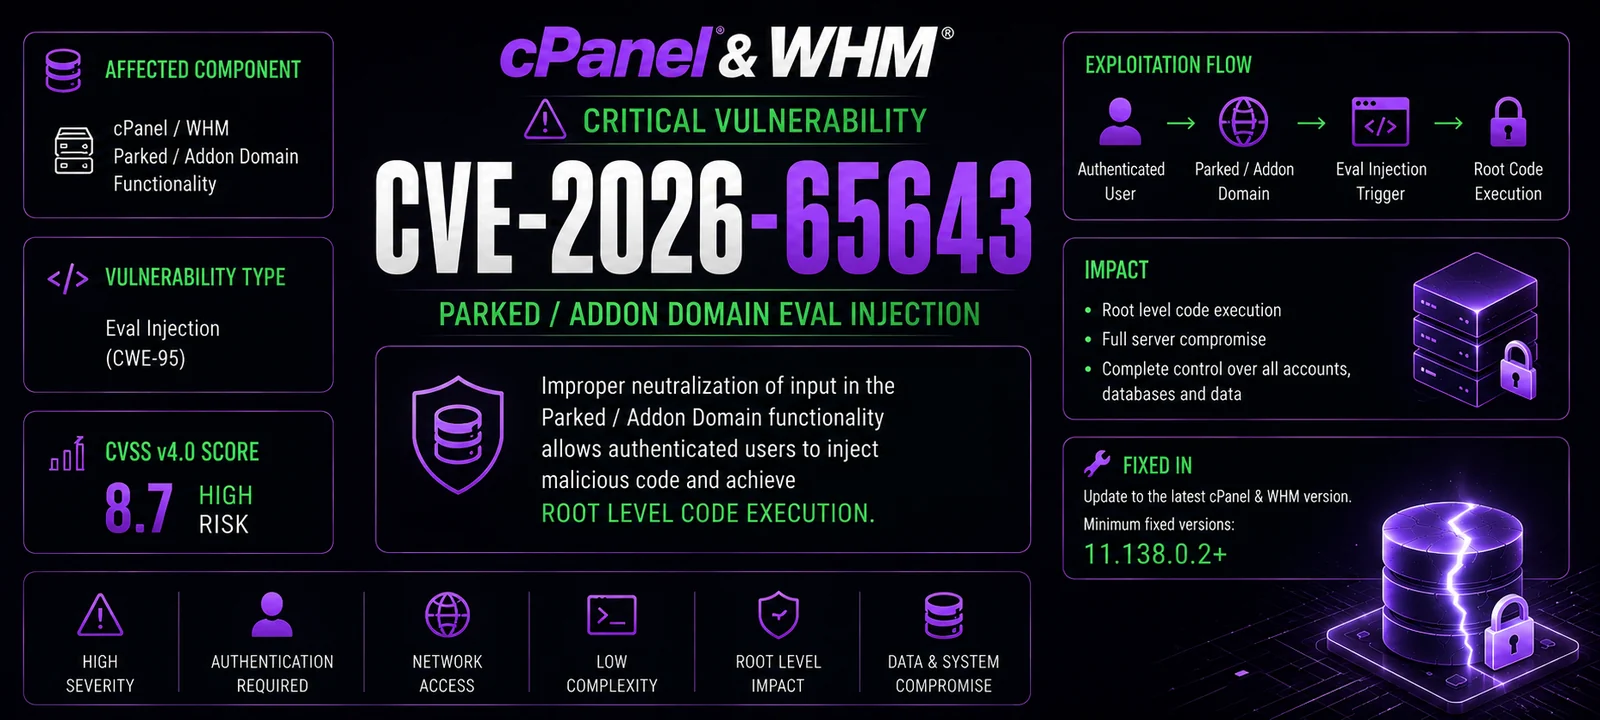 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 manizada/cifswitch
Proof-of-concept exploit for CVE-2026-46243, leveraging a fake NSS library and namespace manipulation to escalate privileges via cifs.upcall.
 vilasboasph/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV path manipulation.
 nikip72/cve-2021-4034
Statically linked implementation of the CVE-2021-4034 privilege escalation exploit, with encoded payload written to disk and no gcc dependency.
 lennertdefauw/cve-2026-24291
Obfuscated Windows privilege escalation exploit for CVE-2026-24291 that automatically creates a local administrator with generated credentials.
 drapl0n/pwnkit
USB Rubber Ducky payload that exploits CVE-2021-4034 to escalate privileges and spawn a root shell on Unix-like systems in under 10 seconds.
 aus-mate/cve-2021-4034-poc
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec. Compiles and runs a C payload to…
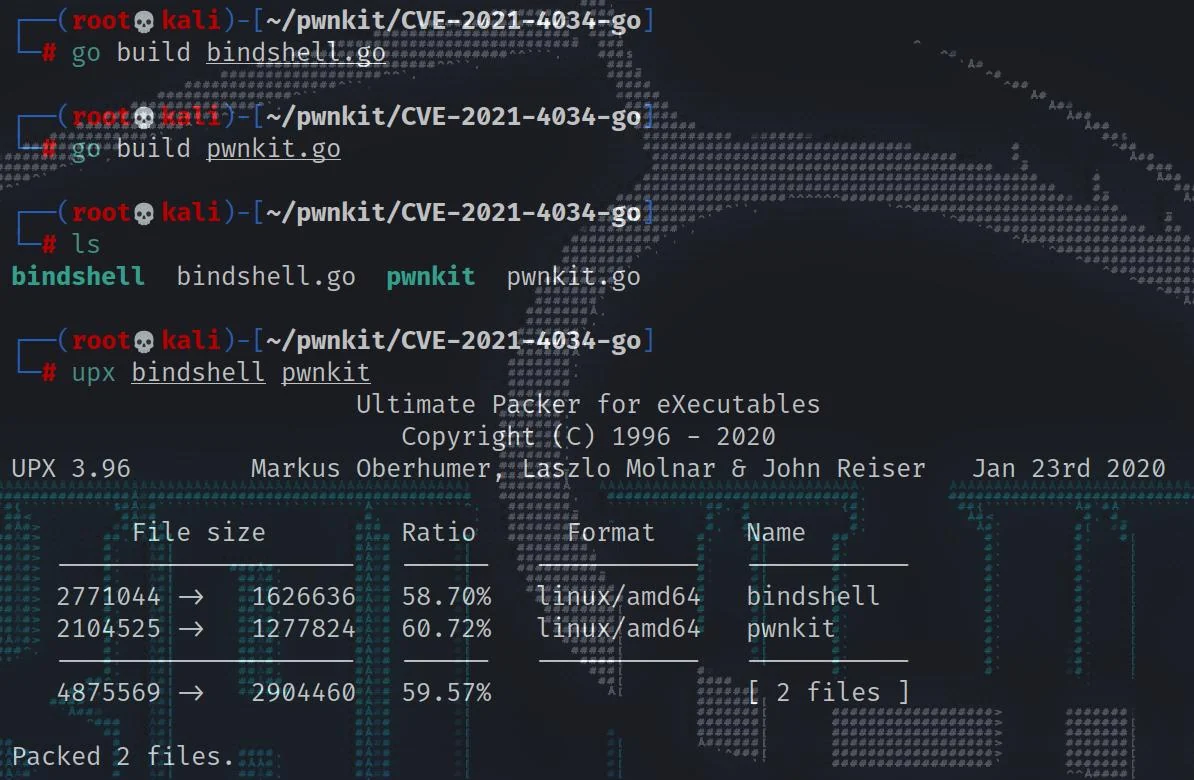 fdlucifer/pwnkit-go
A golang based exp for CVE-2021-4034 dubbed pwnkit (more features added......)
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…