
ns2jb
 pepsipu/ns2jb
Console jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…
embedded-systems-securityexploitationhardware-hacking+4
27
pepsipu/ns2jbConsole jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…
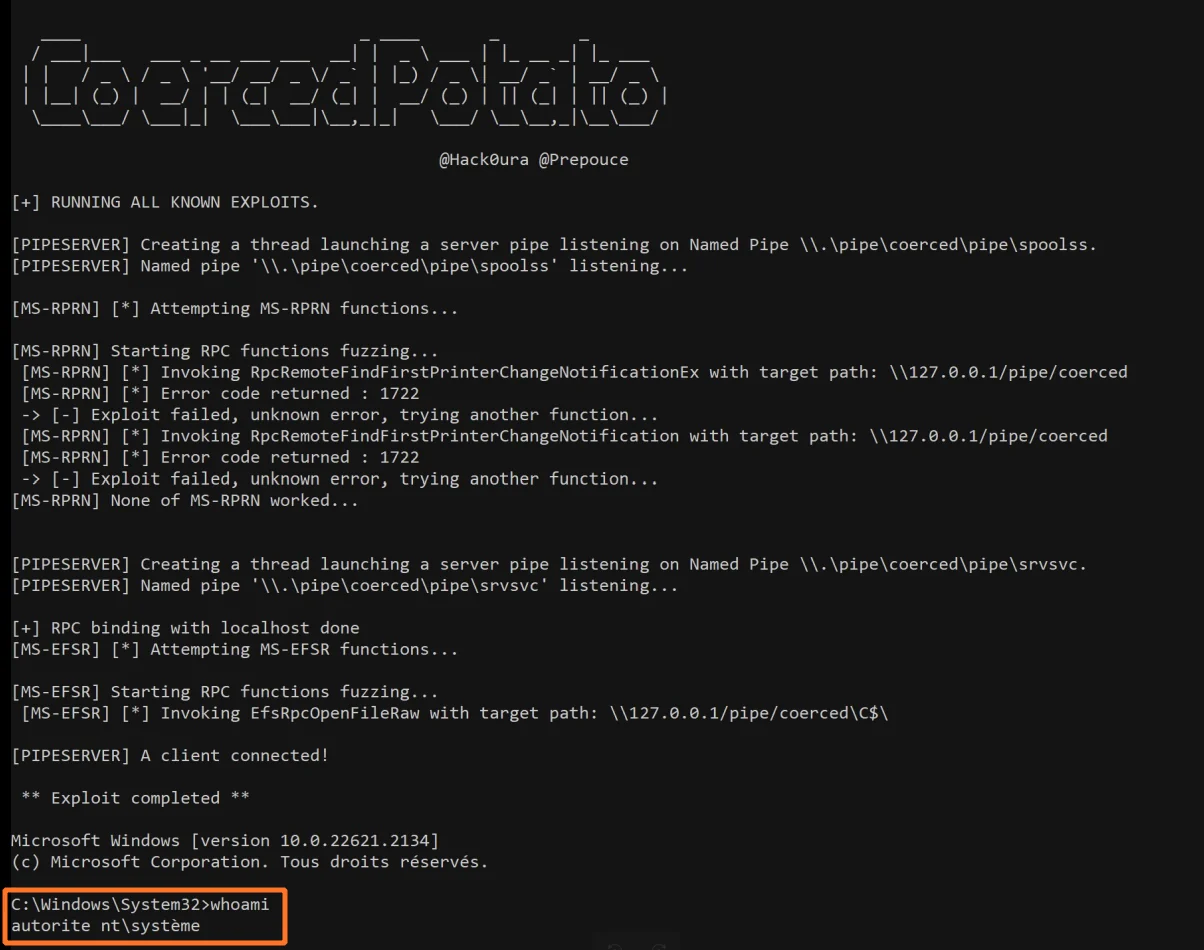
 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 blendin/3snake
Tool for extracting information from newly spawned processes
 capture0x/aws-pentest
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…
 abraxas/vbox-ovf-nat-tftp-prefix
VirtualBox 7.2.20 - High - Local - File read - OVF NAT TFTP empty prefix
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 abraxas/pfsense-api-unix-sock-noauth
pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT
 joda32/adit
Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.