

CVE-2026-63030
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
command-and-controlexploitationpayload-development+8
1
langz337/cve-2026-63030Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 chinaran0/cve-2026-59310-poc
Python PoC and exploit for CVE-2026-59310, a VMware vCenter syslog path traversal leading to unauthenticated root RCE via cron injection, with…
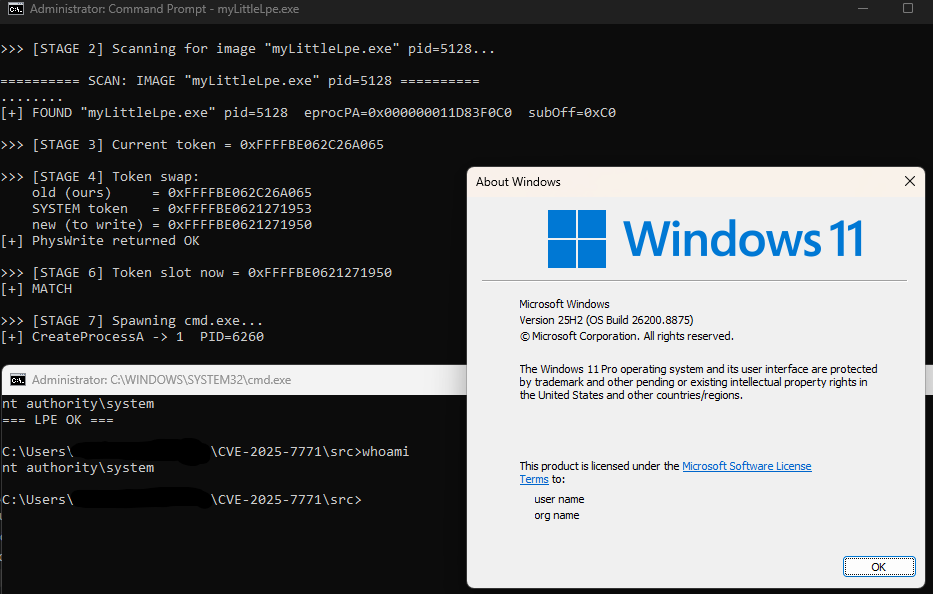 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 geozstevenzz/cve-2024-30804
Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
 rootxn/cve-2026-12793
Python PoC for CVE-2026-12793 in JetFormBuilder <= 3.6.2: unauthenticated privilege escalation leading to plugin upload and remote code execution,…
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 r00t-byte/pwnkit-cve-2021-4034-lpe
PwnKit - polkit pkexec Local Privilege Escalation <= 0.105-31
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 0xf9b6a41ec/cve-2026-69328
Windows privilege escalation exploit that plants SprintCSP.dll in a user-writable HKLM PATH directory to hijack StorSvc and execute as SYSTEM.
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
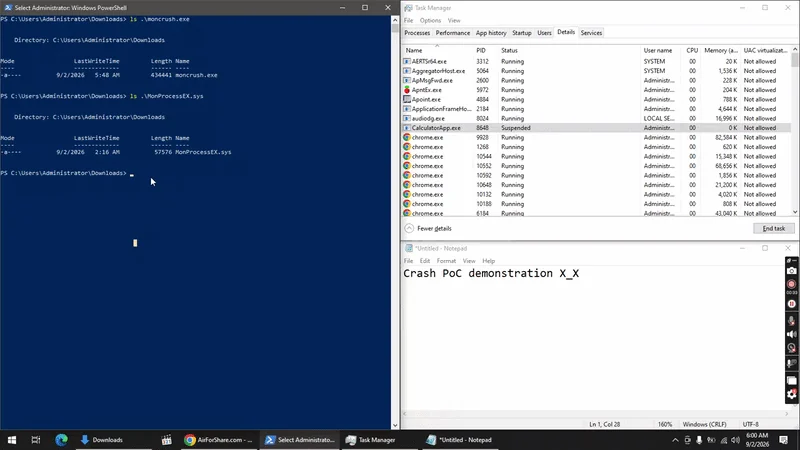 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
 goldendivider/cve-2026-6471-postgres-logical-decoding-dlopen
Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
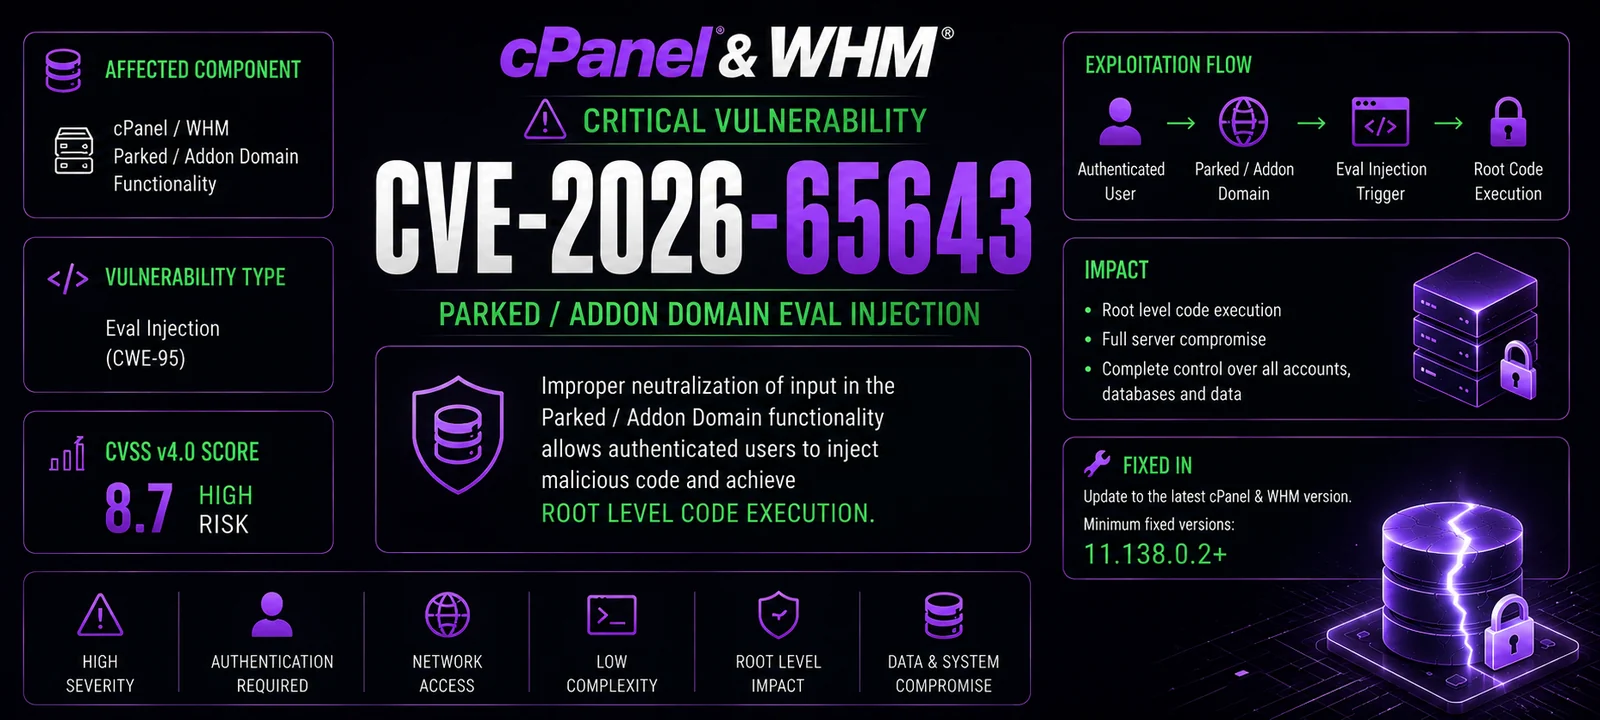 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here