

LocalStranger
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
binary-exploitationexploit-frameworkspayload-development+3
4
nbs32k/localstrangerPoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
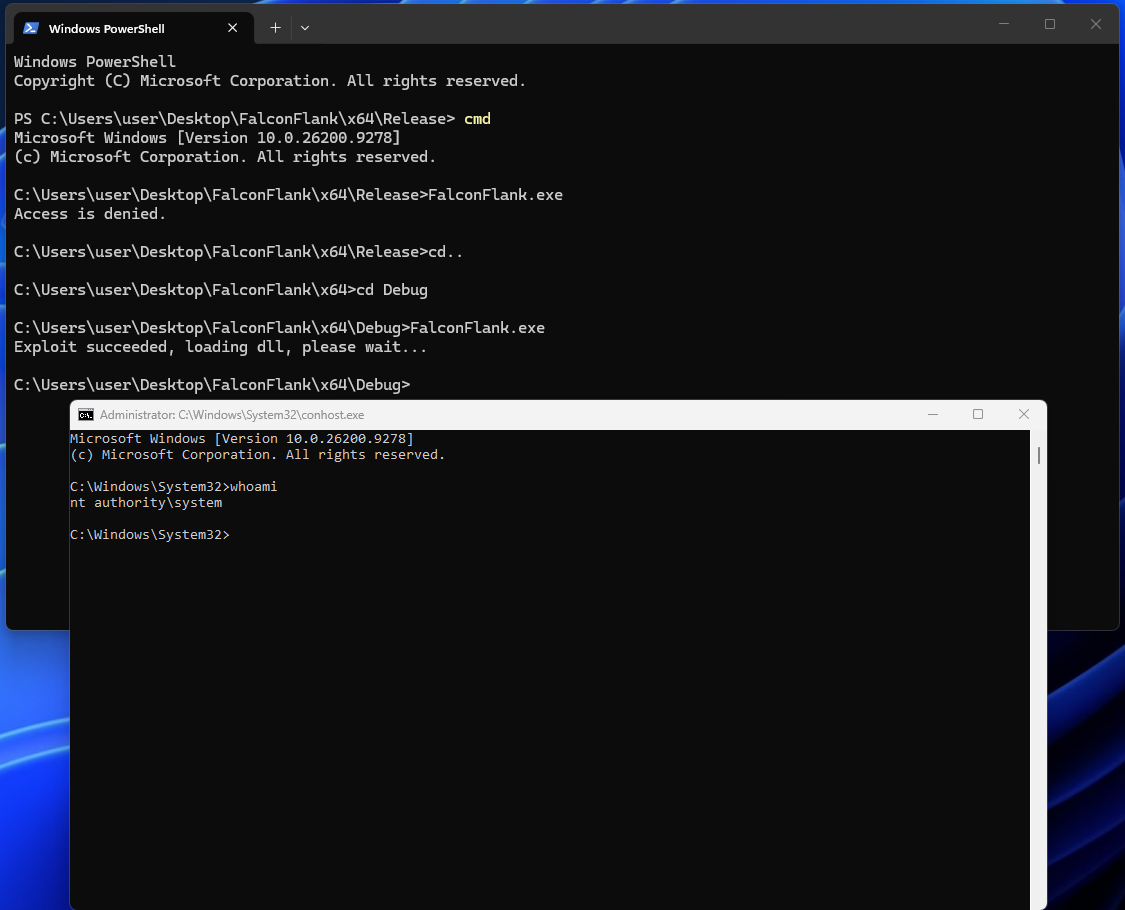 msnightmare/falconflank
Crowdstrike Falcon 0day Privilege Escalation Vulnerability
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
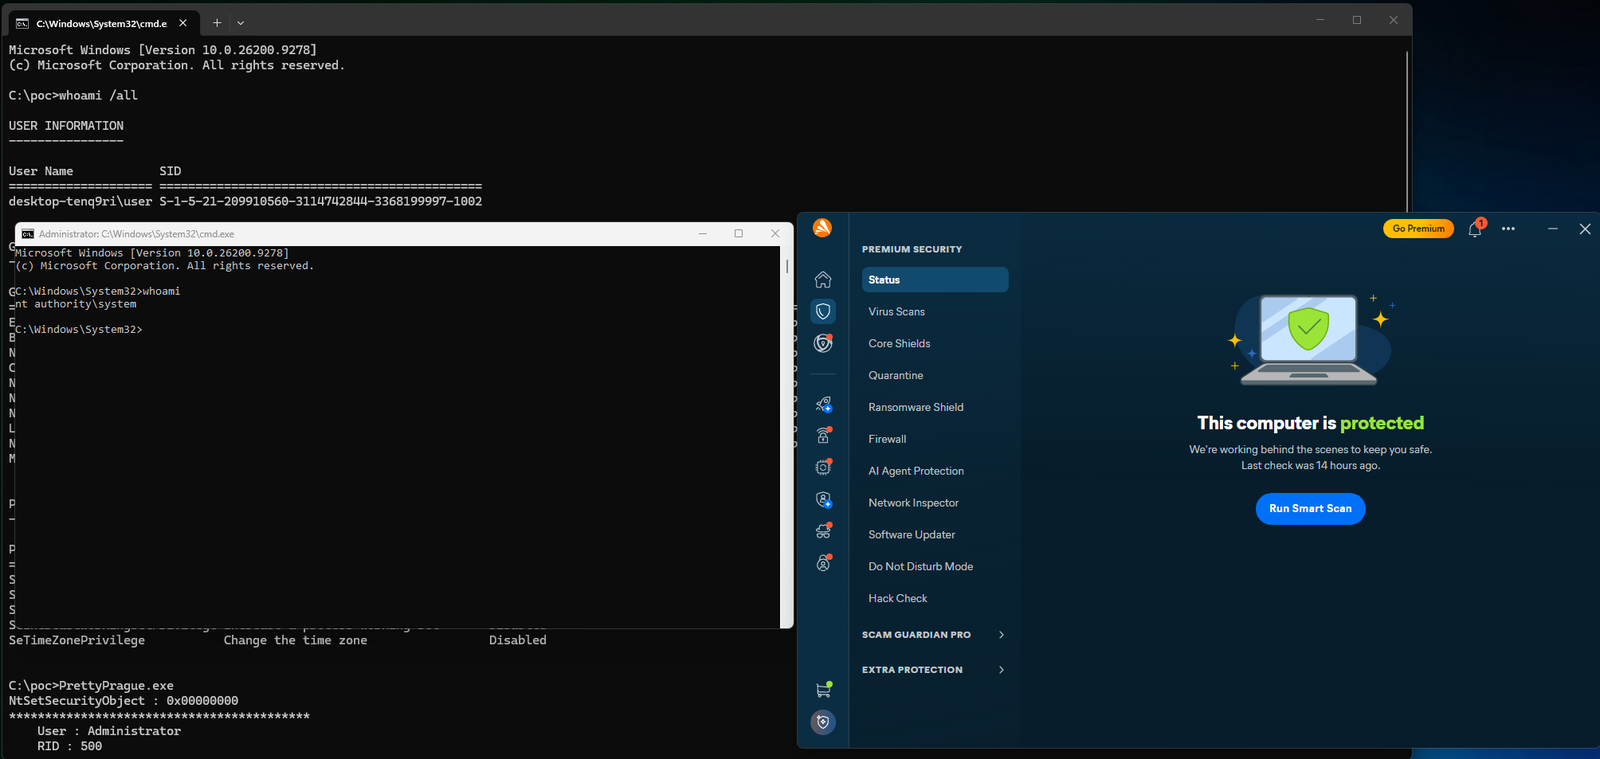 msnightmare/prettyprague
GenDigital Avast Antivirus ZeroDay Elevation of Privileges Vulnerability
 cyghtinc/cve-2024-30088-binary-lpe-privielege-escalation-cyght-toctou
Compiled proof-of-concept binary for local privilege escalation exploiting CVE-2024-30088, a TOCTOU vulnerability, targeting Windows systems.
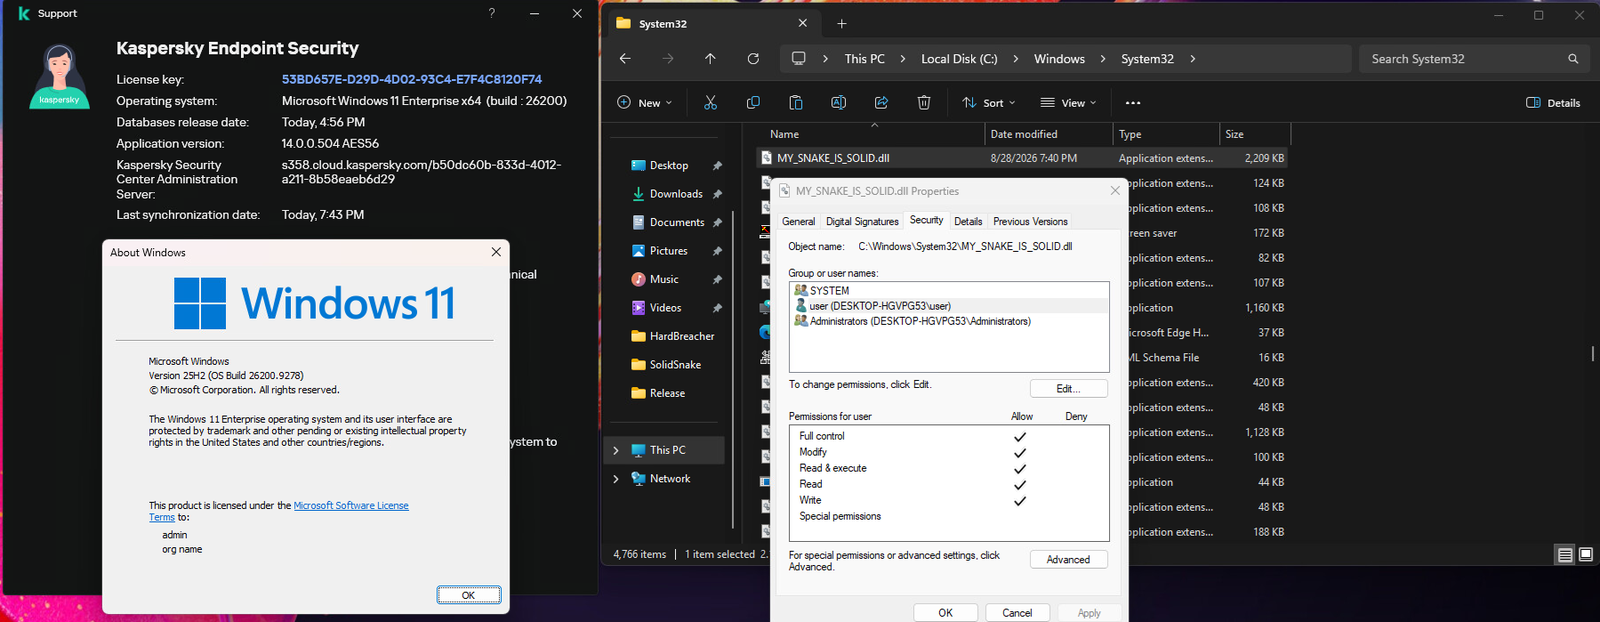 msnightmare/hardbreacher
Kaspersky Antivirus For Endpoint ZeroDay Elevation of Privileges Vulnerability
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
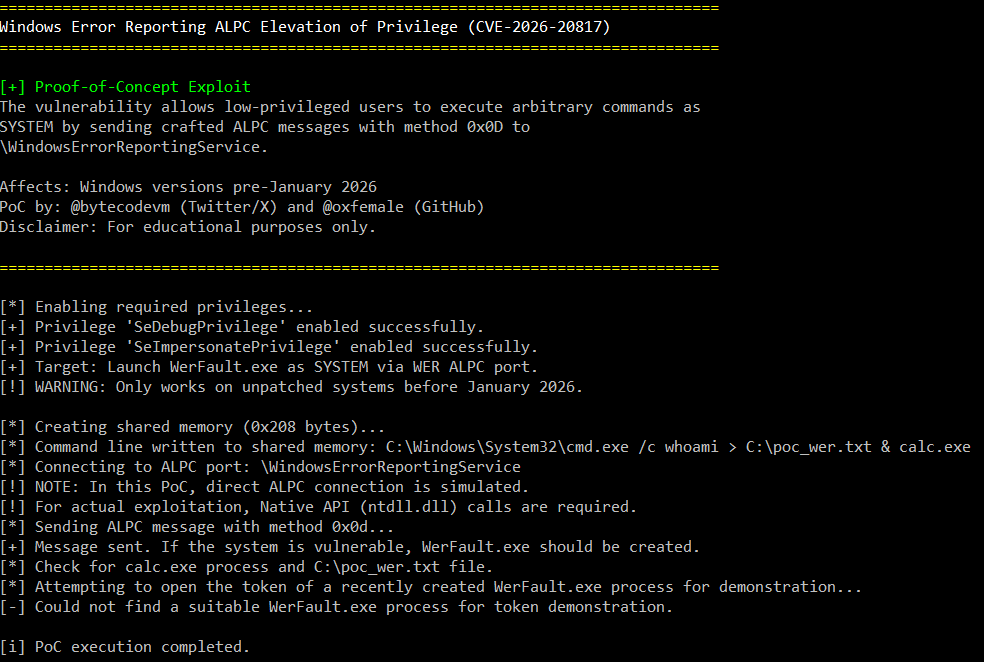 oxfemale/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 moiz-2x/cve-2025-24990_poc
Proof of Concept CVE-2025-24990 (Agere Systems's driver)
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 simoesctt/sctt-2026-33-0002-dwm-visual-field-singularity
Exploit research targeting Windows DWM to achieve local privilege escalation via a theoretical Visual-Field Singularity, bypassing graphics isolation…
 simoesctt/-sctt-2026-33-0002-dwm-visual-field-singularity
Weaponizes a Visual-Field Singularity in Windows Desktop Window Manager to achieve local privilege escalation to SYSTEM, bypassing Graphics Isolation…
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
 sfrdevelopment/windows-smb-vulnerability-framework-cve-2025-33073
Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…
 b1tbreaker/cve-2026-30332
Balena Etcher versions prior to v2.1.4 on Windows are affected by a Time-of-Check to Time-of-Use (TOCTOU) race condition in the temporary file…
 andrewtrube/cve-2021-1675
Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…