
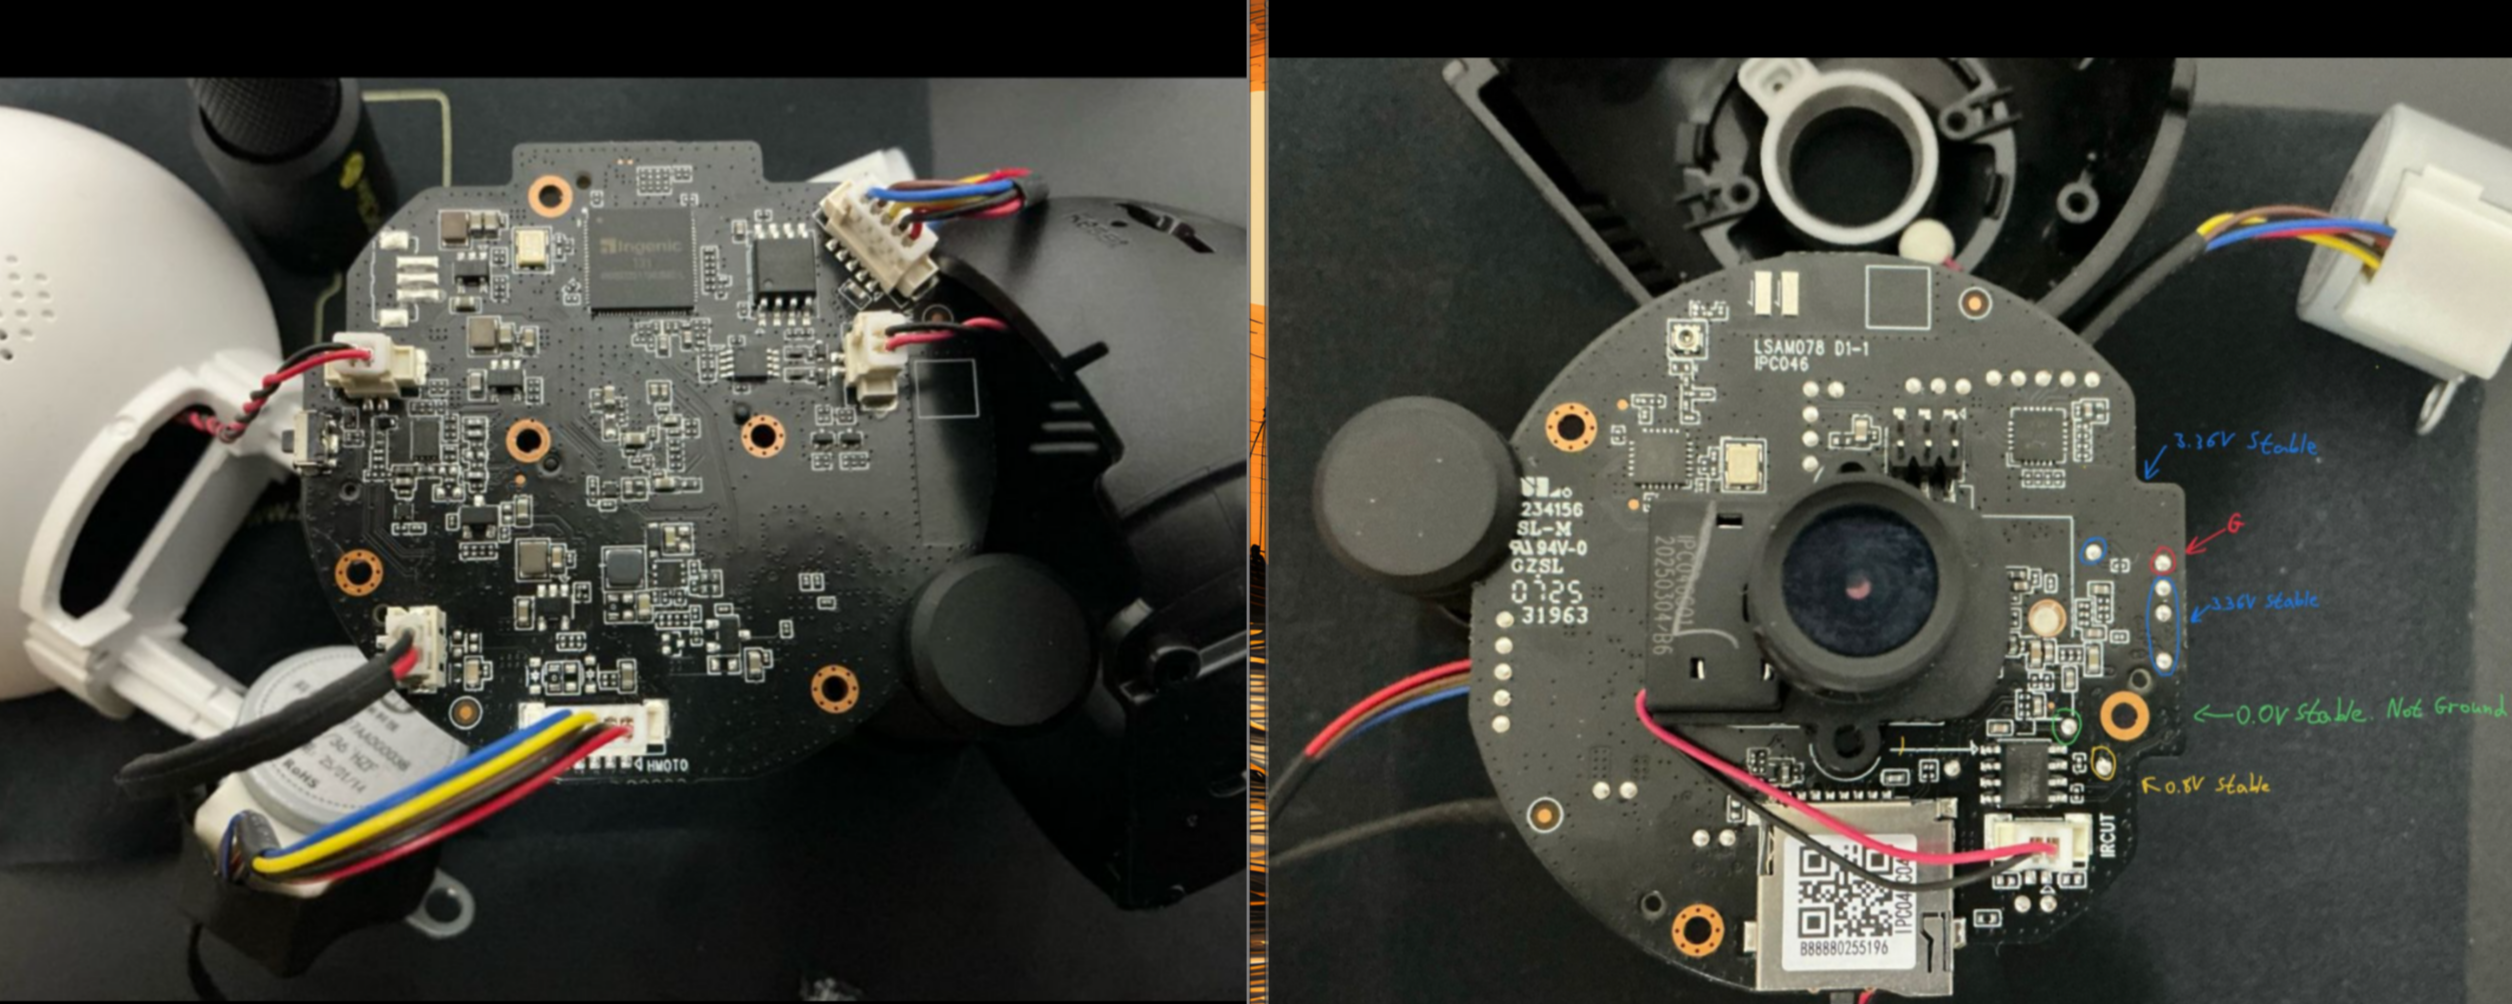
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
12
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
 george0papasotiriou/cve-2026-22015-serverless-function-environment-variable-injection-via-event
PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 bhathiya404/exploiting-stagefright-vulnerability-cve-2015-3864
Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…
 henryisnotavailable/cve-2025-27581
Exploit scripts for CVE-2025-27581
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
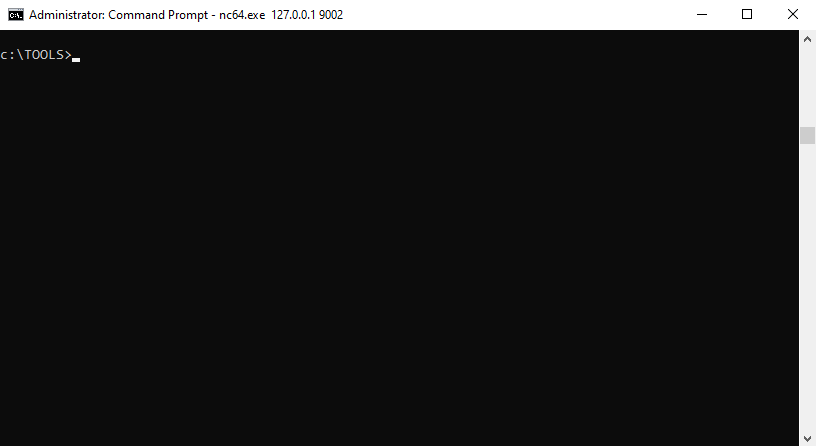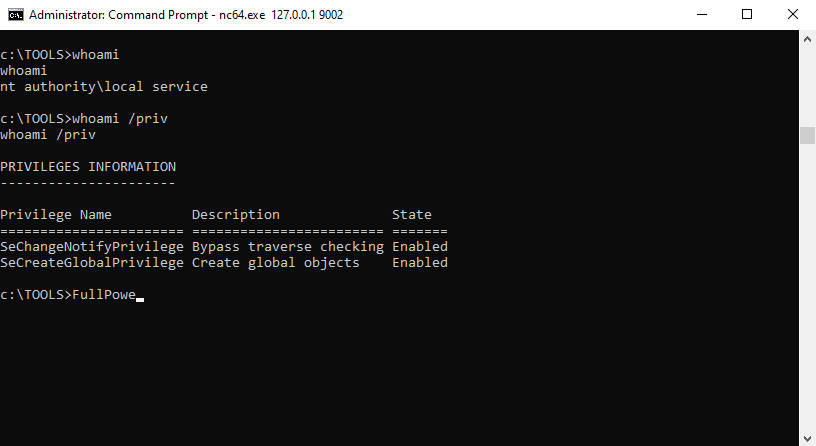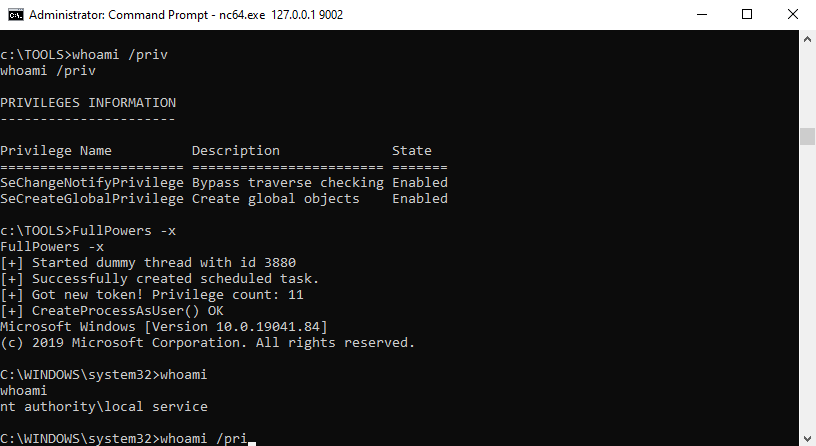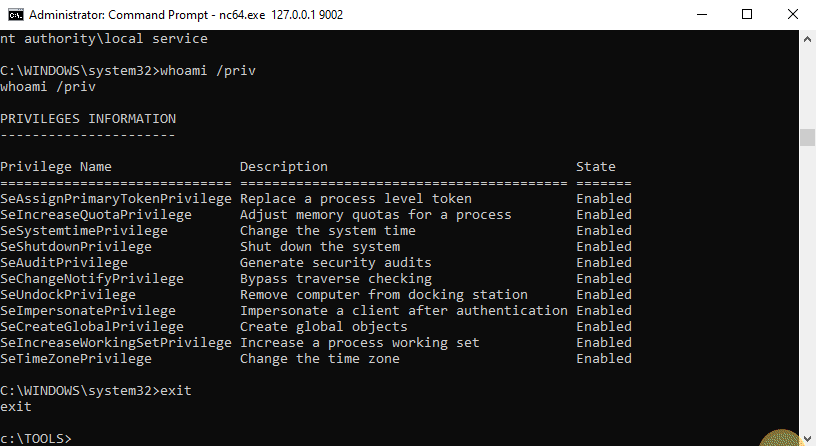 itm4n/fullpowers
Recover the default privilege set of a LOCAL/NETWORK SERVICE account
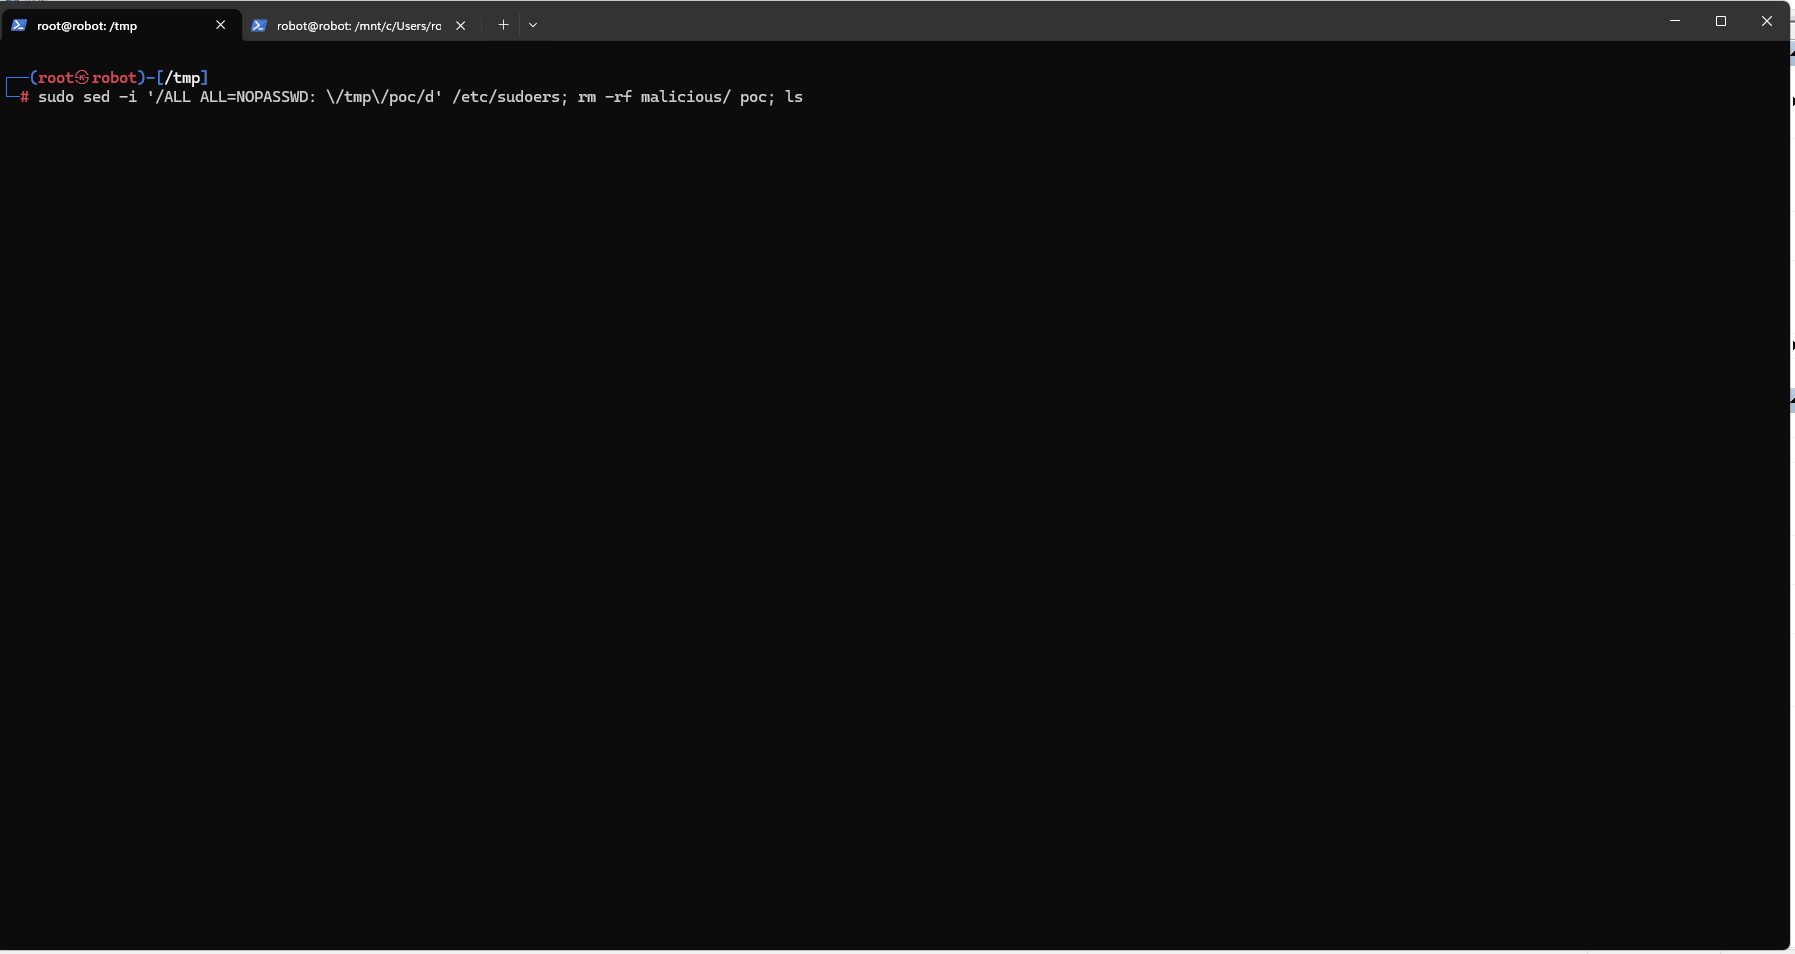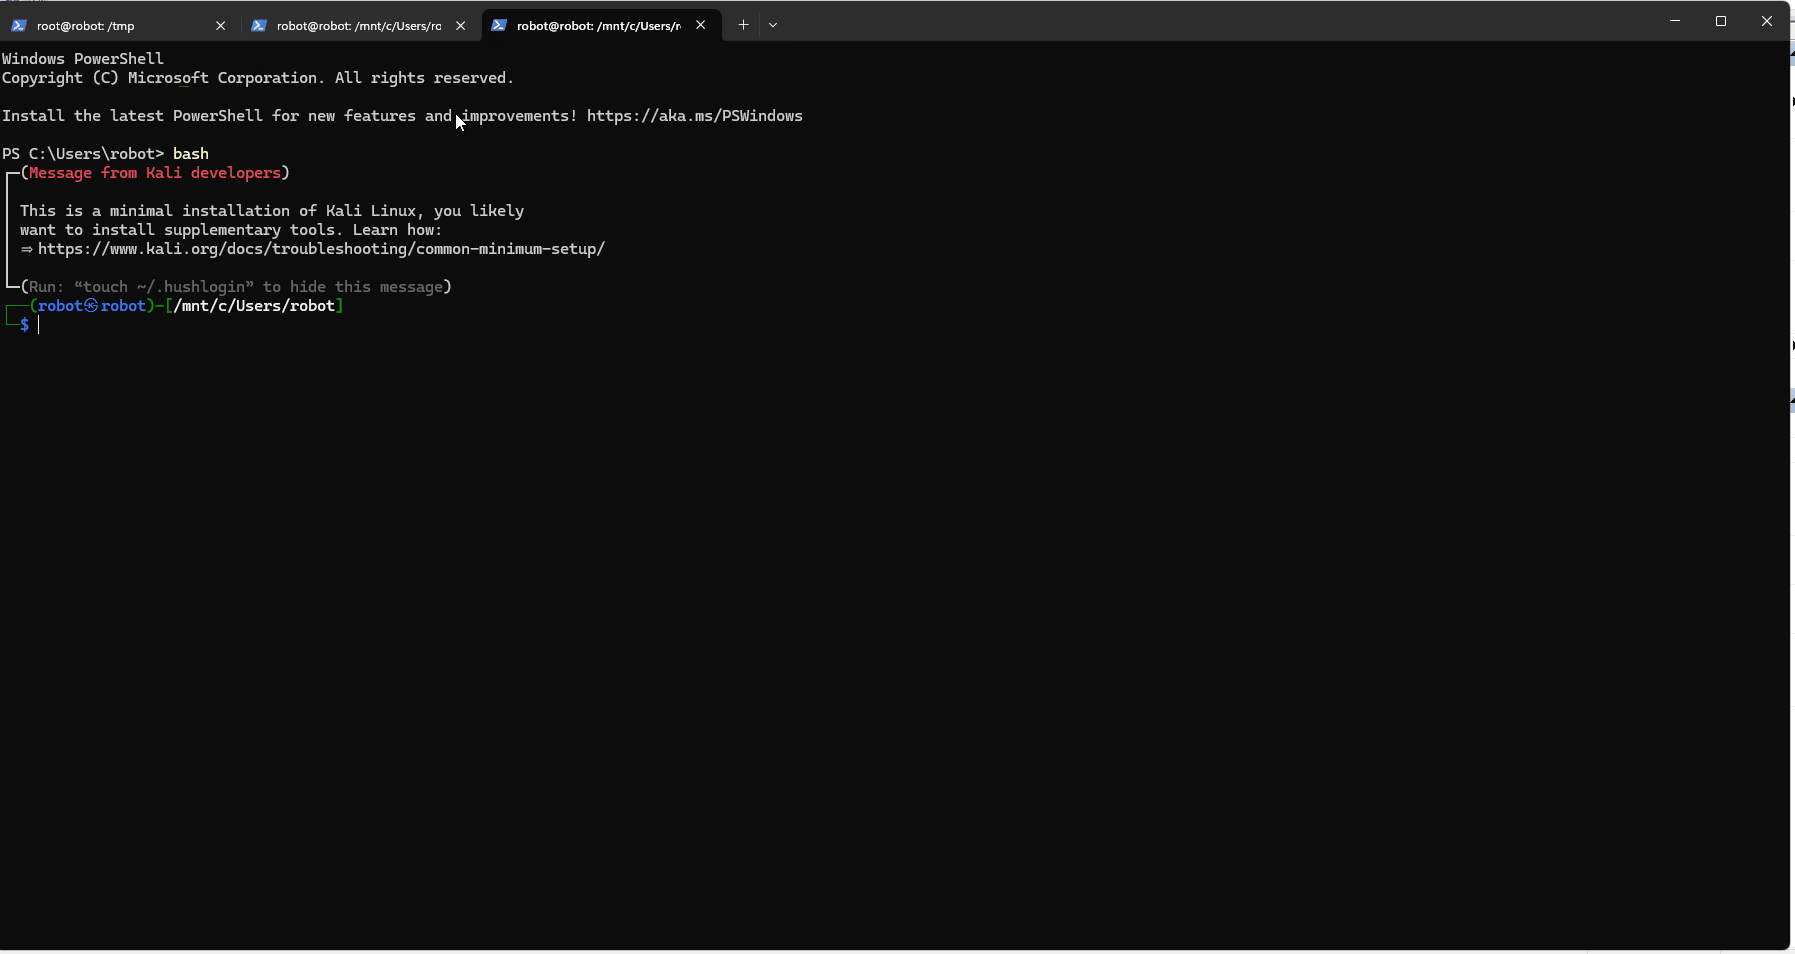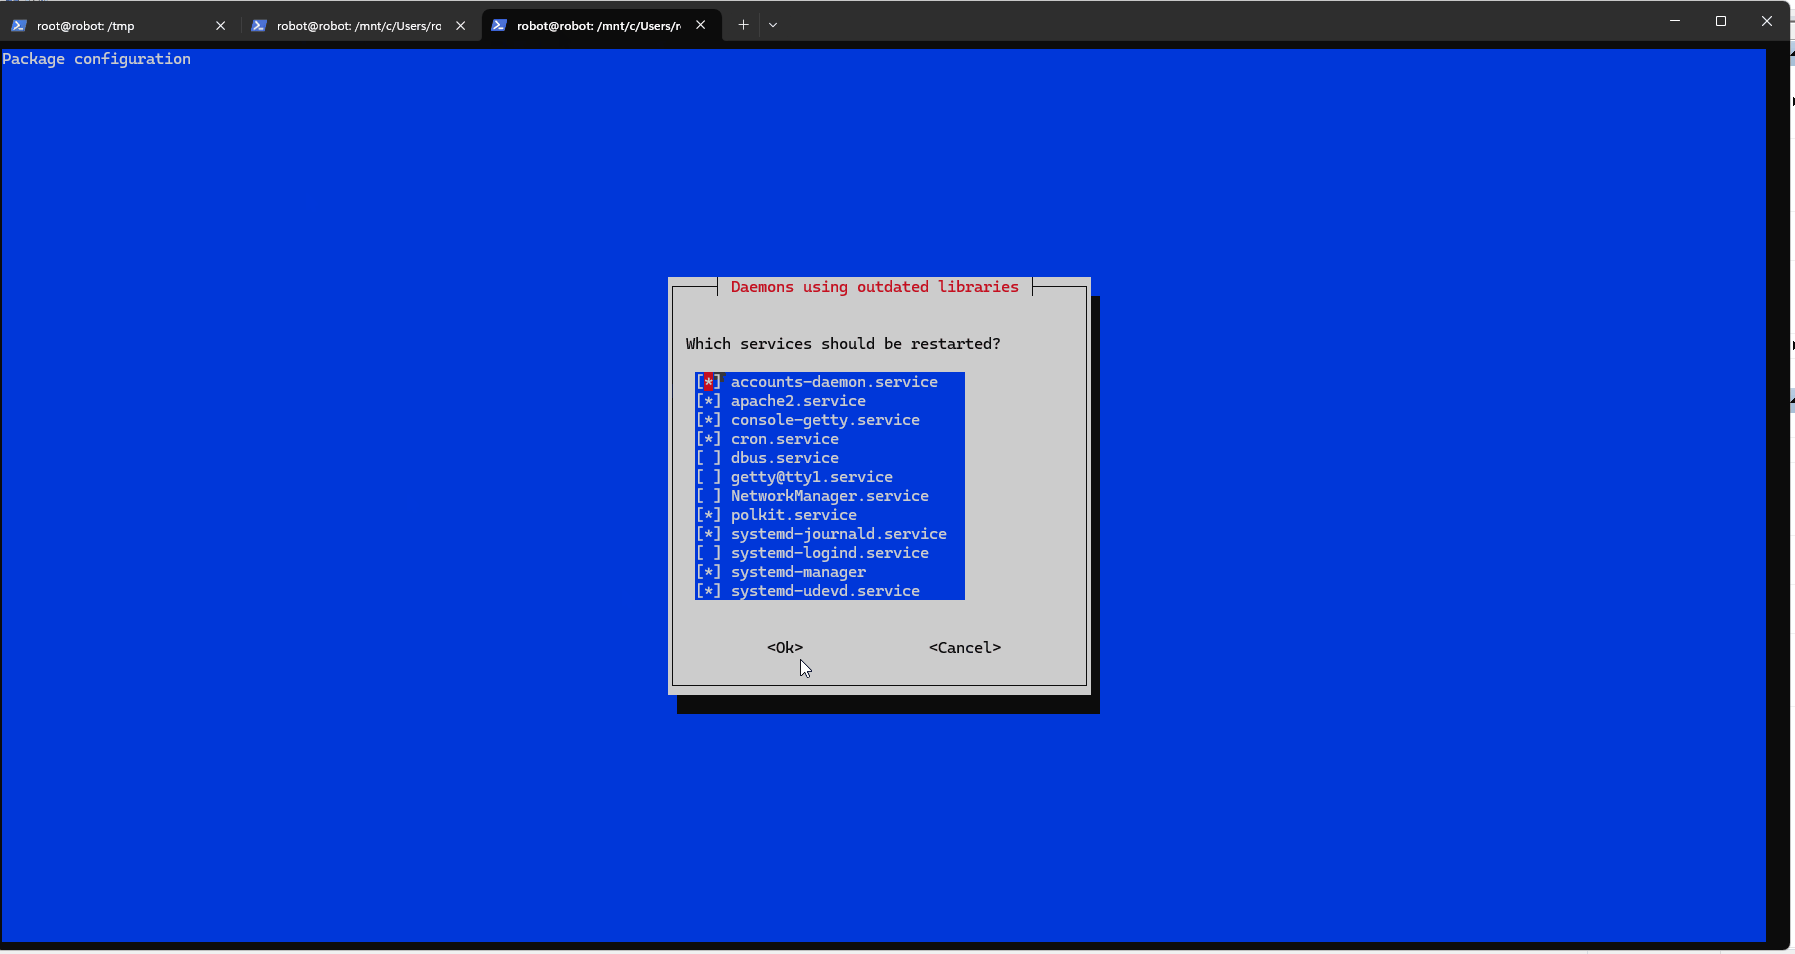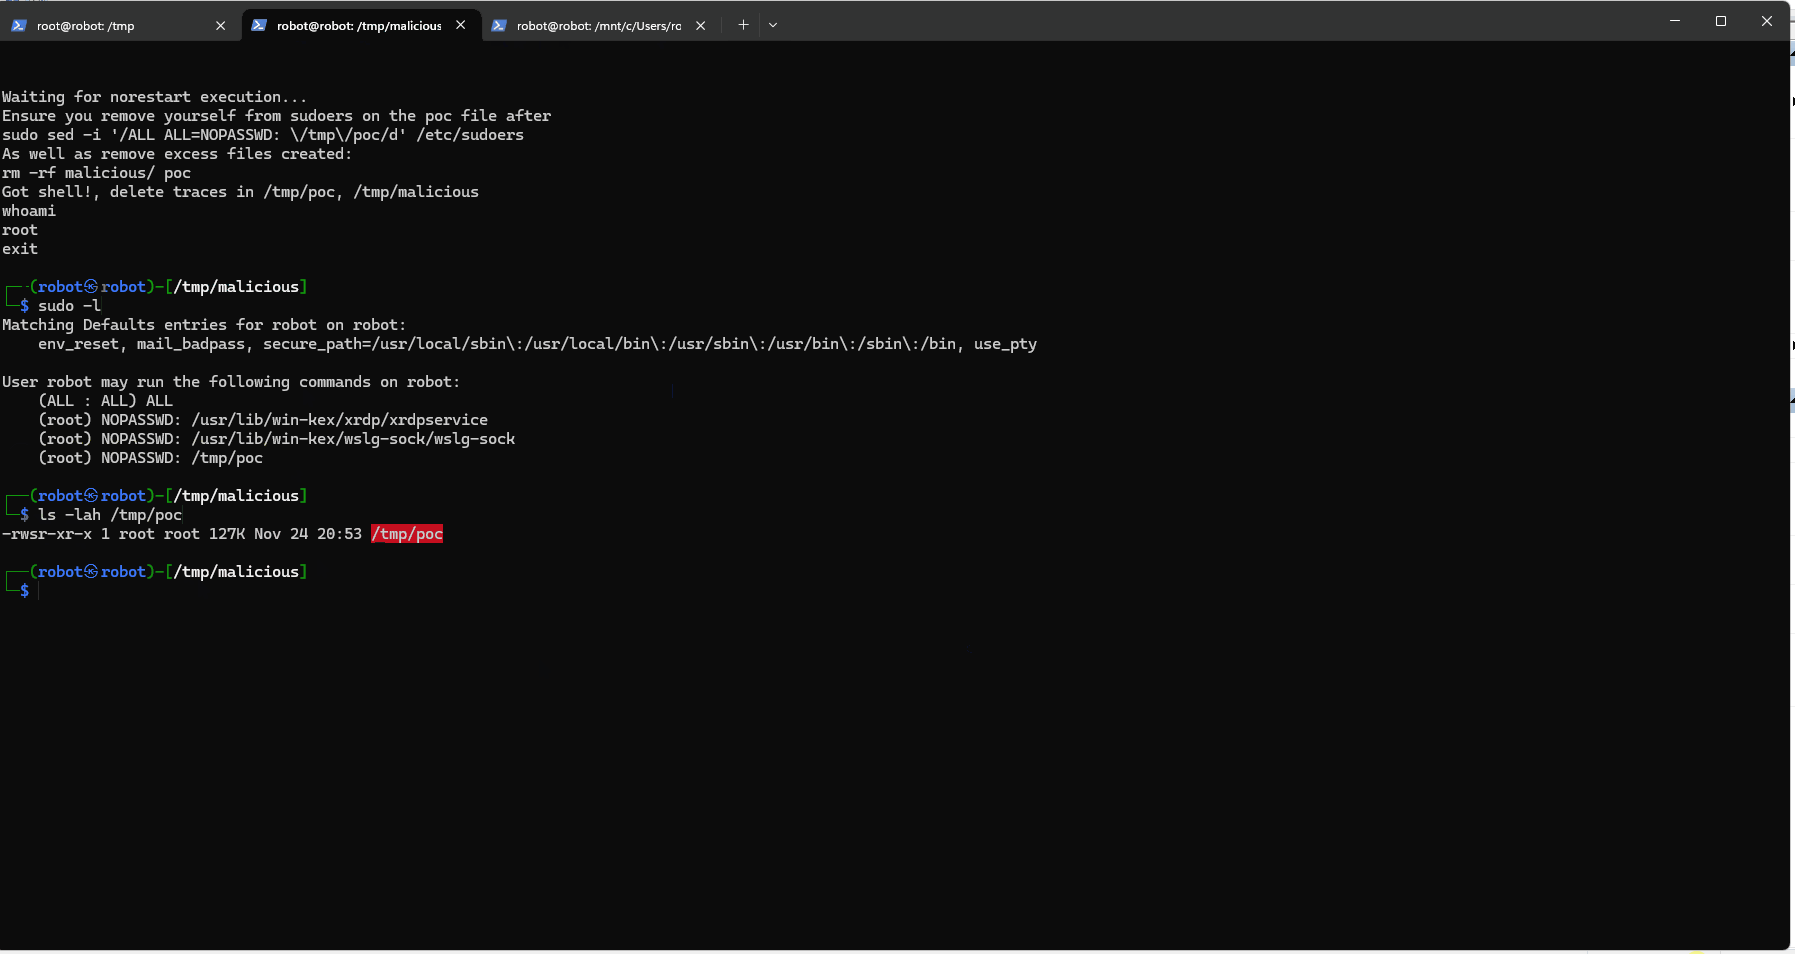 pentestfunctions/cve-2024-48990-poc-testing
Testing POC for use cases