

FolkPatch
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
android-securitymobile-securitypayload-development+3
1.3k
lyravoid/folkpatchRoot access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 specterops/bloodhound
Six Degrees of Domain Admin
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 blendin/3snake
Tool for extracting information from newly spawned processes
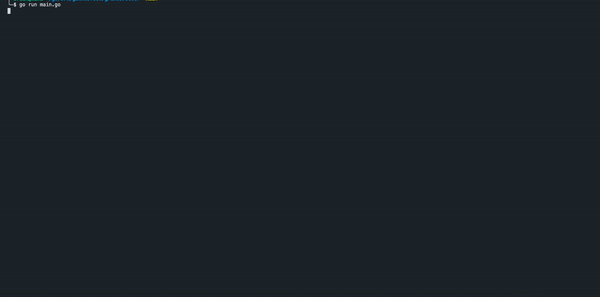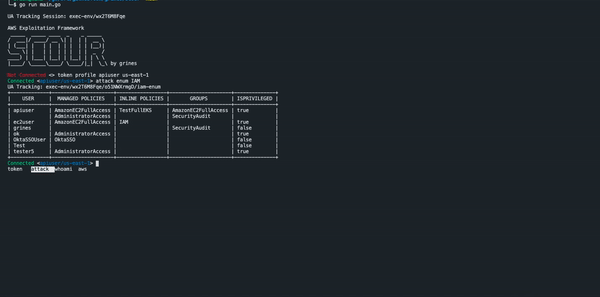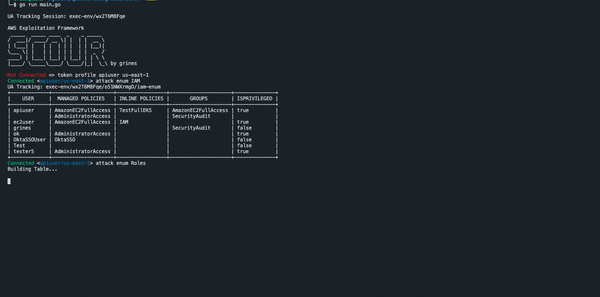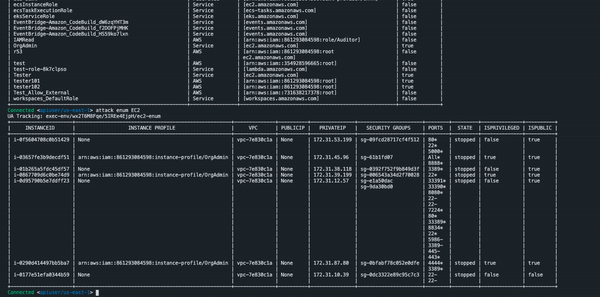 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 dragoqcc/cruciblec2
A C# Command & Control framework
 var77/cve-2026-2005
PoC for CVE-2026-2005
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE