
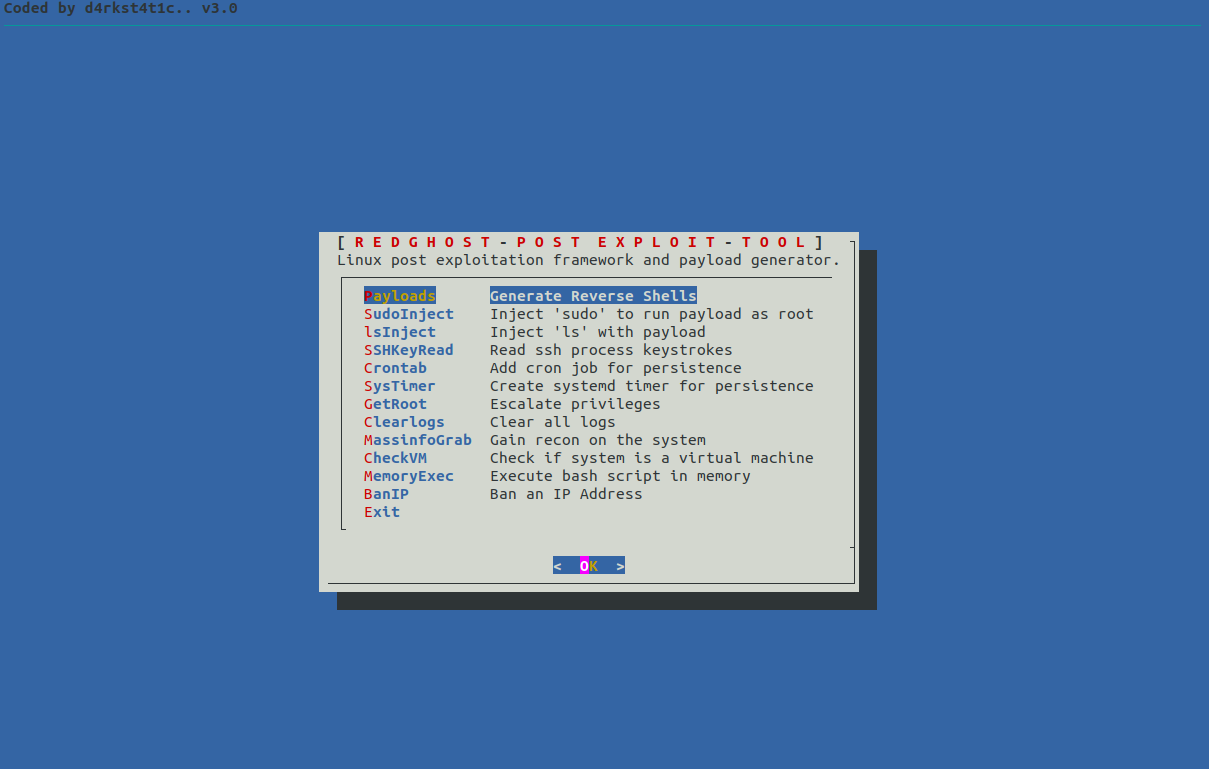
RedGhost
 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
command-and-controllateral-movementpayload-generation+5
541
d4rk007/redghostLinux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
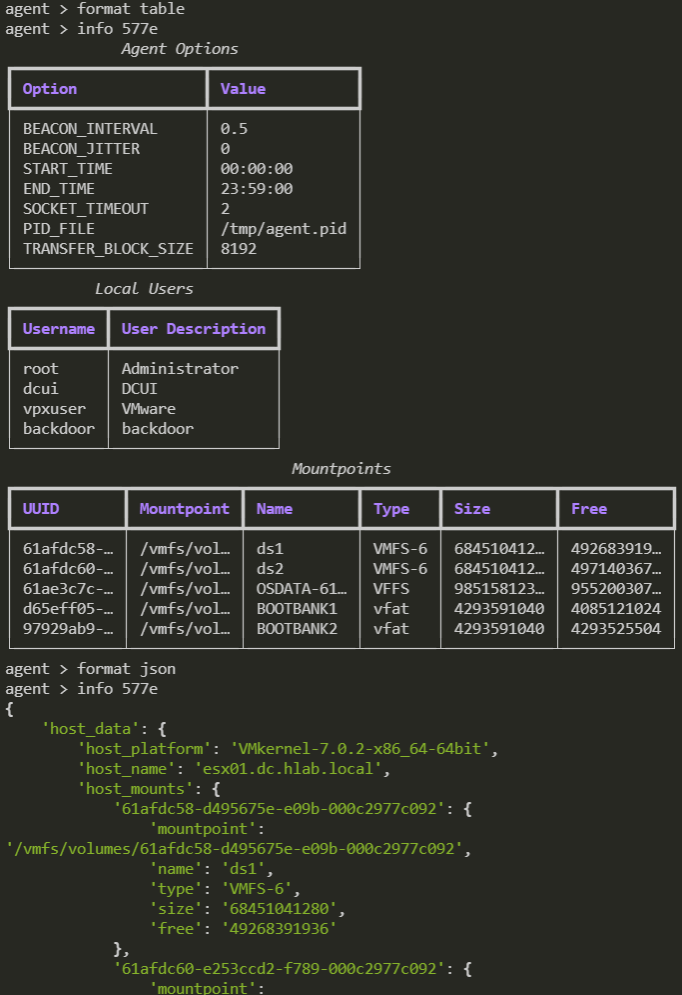 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 redsiege/persistassist
Fully modular persistence framework
 r3dw4n48m3d/cve-2021-3493-exploit
C-based local privilege escalation exploit for CVE-2021-3493, targeting OverlayFS in Linux kernels prior to 5.11. Provides compilation and usage…
 deoxykev/cve-2021-4034-rust
Rust implementation of the CVE-2021-4034 polkit pkexec local privilege escalation exploit, with build instructions and detection considerations.
 bekhzod0725/perl-cve-2013-1775
CVE-2013-1775 Exploit written in Perl
 smarttfoxx/copyfail
CVE-2026-31431 (Copy Fail) PoC - Linux kernel page cache corruption via authencesn AF_ALG + splice()
 jpmcb/pwnkit-go
Exploit for the PwnKit vulnerability, CVE-2021-4034, written in Go
 lanleft/cve-2022-2586
Local privilege escalation exploit for CVE-2022-2586 targeting Linux kernel 5.15.0-25 on Ubuntu 22.04, written in C and compiled with gcc.