
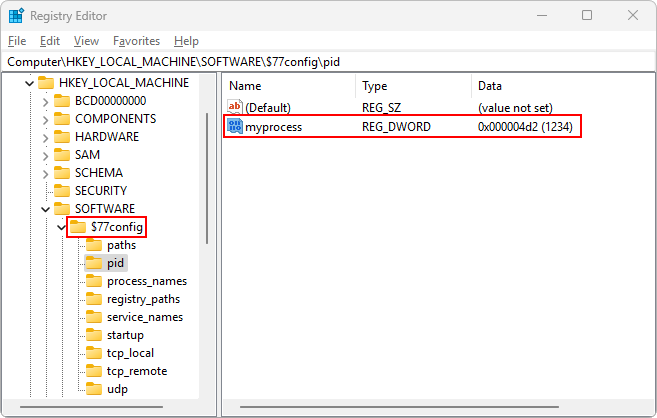
r77-rootkit
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k
bytecode77/r77-rootkitFileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
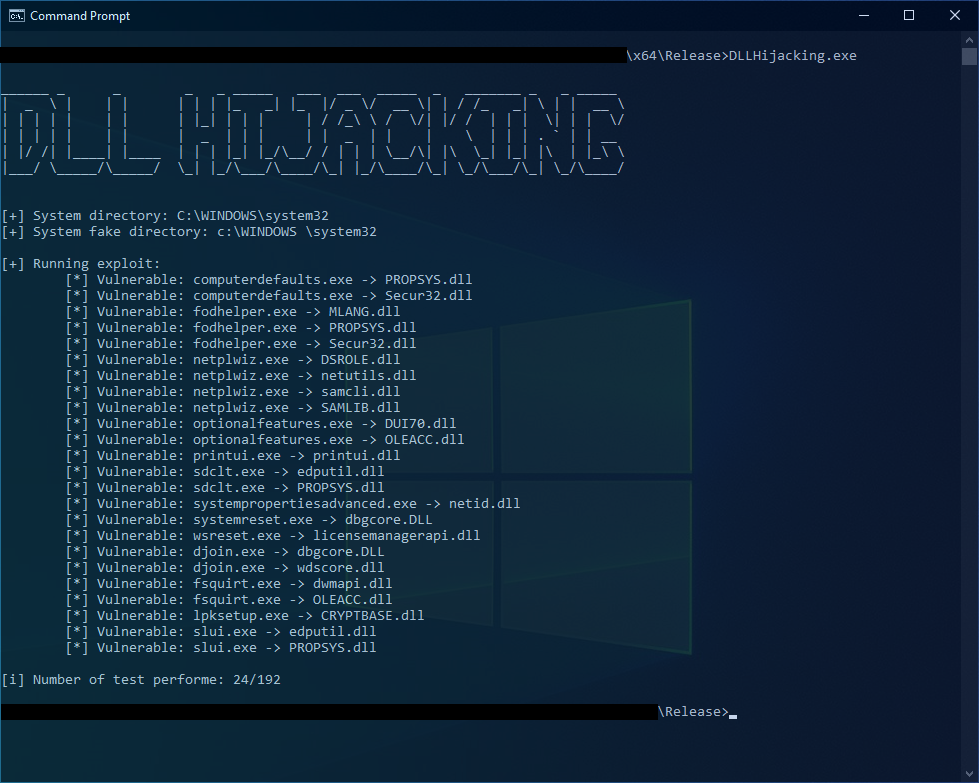 secuproject/dllhijackingscanner
This is a PoC for bypassing UAC using DLL hijacking and abusing the "Trusted Directories" verification.
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 initstring/uptux
Linux privilege escalation checks (systemd, dbus, socket fun, etc)
 mmiszczyk/cve-2024-33352
BlueStacks privilege escalation through VM backdooring
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
 and-oss/cve-2025-6019-exploit
exploit
 alexlee820/cve-2025-63946-tencent-pc-manager-eop
Proof-of-concept exploit for CVE-2025-63946, a local privilege escalation in Tencent PC Manager via symlink attacks on temporary directories,…
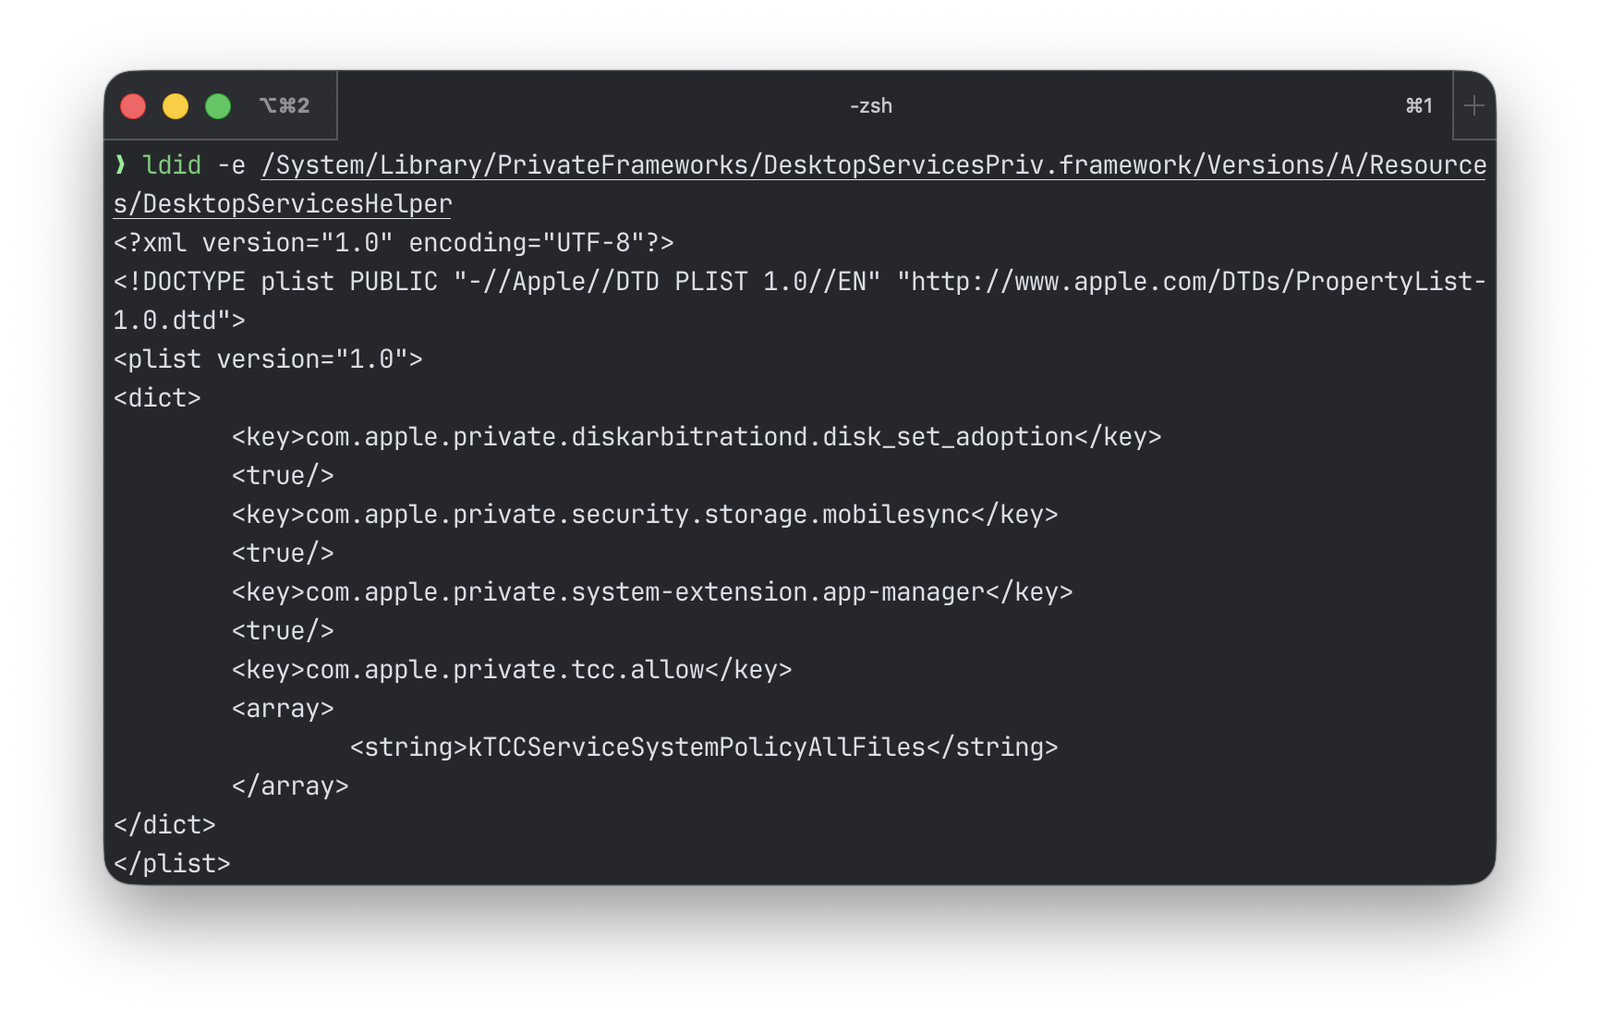 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
 alexlee820/cve-2025-63945-tencent-ioa-eop
Demonstrates a local privilege escalation vulnerability in Tencent iOA before 210.9.28693.62001 via symlink attacks on C:\Windows\Temp, enabling…
 al1ex/cve-2020-8635
Wing FTP Server 6.2.3 - Privilege Escalation