

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
11 results
FolkPatch preview

FolkPatch

GitHublyravoid/folkpatch

Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
android-securitymobile-securitypayload-development+3
1.3k
16 days ago
Anvil preview

Anvil

GitHubshellkraft/anvil

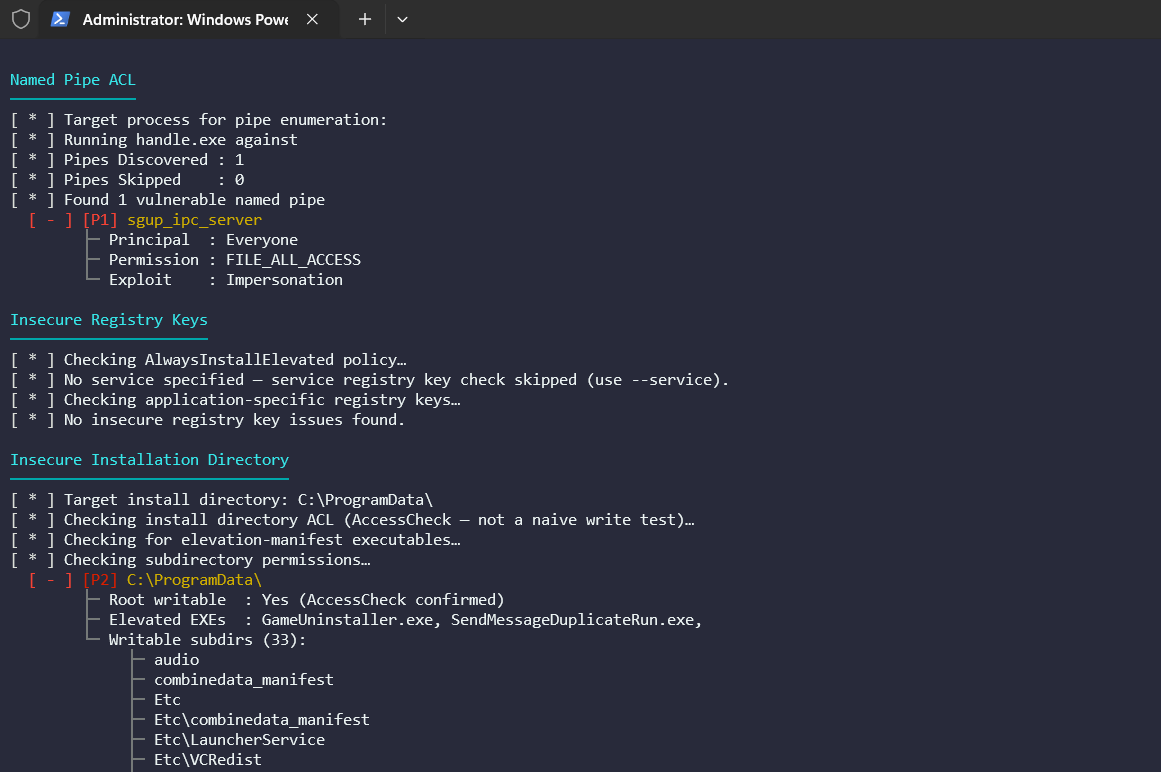
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
binary-analysisexploitationpenetration-testing+5
397 months ago
Evasor preview

Evasor

GitHubcyberark/evasor

A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
binary-analysisdefensive-toolspenetration-testing+3
3256 years ago
CVE-2025-50363_BXSS_CVE preview

CVE-2025-50363_BXSS_CVE

GitHub1h3ll/cve-2025-50363_bxss_cve

Proof-of-concept for a blind XSS vulnerability in Maid Hiring Management System v1.0, capturing admin session cookies via a crafted application form…
exploitationpenetration-testingphishing+3
1 year ago
msi-central_privesc preview

msi-central_privesc

GitHubnam3lum/msi-central_privesc

CVE-2022-38532 - Local Privilege Escalation vulnerability in MSI Center Application
binary-analysisexploitationpenetration-testing+3
71 year ago
Session-Persistence-After-Enabling-2FA-CVE-2025-60425 preview

Session-Persistence-After-Enabling-2FA-CVE-2025-60425

GitHubaakashtyal/session-persistence-after-enabling-2fa-cve-2025-60425

Detailed vulnerability report on Nagios Fusion session persistence after enabling 2FA, including CVE-2025-60425, affected versions, mitigation…
authenticationexploitationpenetration-testing+3
1 year ago
qu1ckr00t preview

qu1ckr00t

GitHubgrant-h/qu1ckr00t

A PoC application demonstrating the power of an Android kernel arbitrary R/W.
android-securitybinary-exploitationexploitation+2
4457 years ago
htb-ctf-walkthroughs preview

htb-ctf-walkthroughs

GitLabrootsecnz/htb-ctf-walkthroughs

Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
ctfeducationexploitation+6
8 months ago
PoCForCVE-2015-1528 preview

PoCForCVE-2015-1528

GitHubsecmob/pocforcve-2015-1528

I'll submit the poc after blackhat
android-securitybinary-exploitationexploitation+4
11611 years ago
WebminRCE-exploit preview

WebminRCE-exploit

GitHubgokul-ramesh/webminrce-exploit

CVE-2022-0824, CVE-2022-0829, File Manger privilege exploit
exploitationpenetration-testingprivilege-escalation+3
3 years ago
ThingsBoard-IoT-Platform-CVE-2024-55466 preview

ThingsBoard-IoT-Platform-CVE-2024-55466

GitHubcybsecsid/thingsboard-iot-platform-cve-2024-55466

Proof-of-concept for stored XSS in ThingsBoard IoT platform enabling privilege escalation via authentication token theft. Includes CVE-2024-55466…

exploitationpenetration-testingprivilege-escalation+3
1 year ago
