remove-ai-watermarks

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

Give your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.

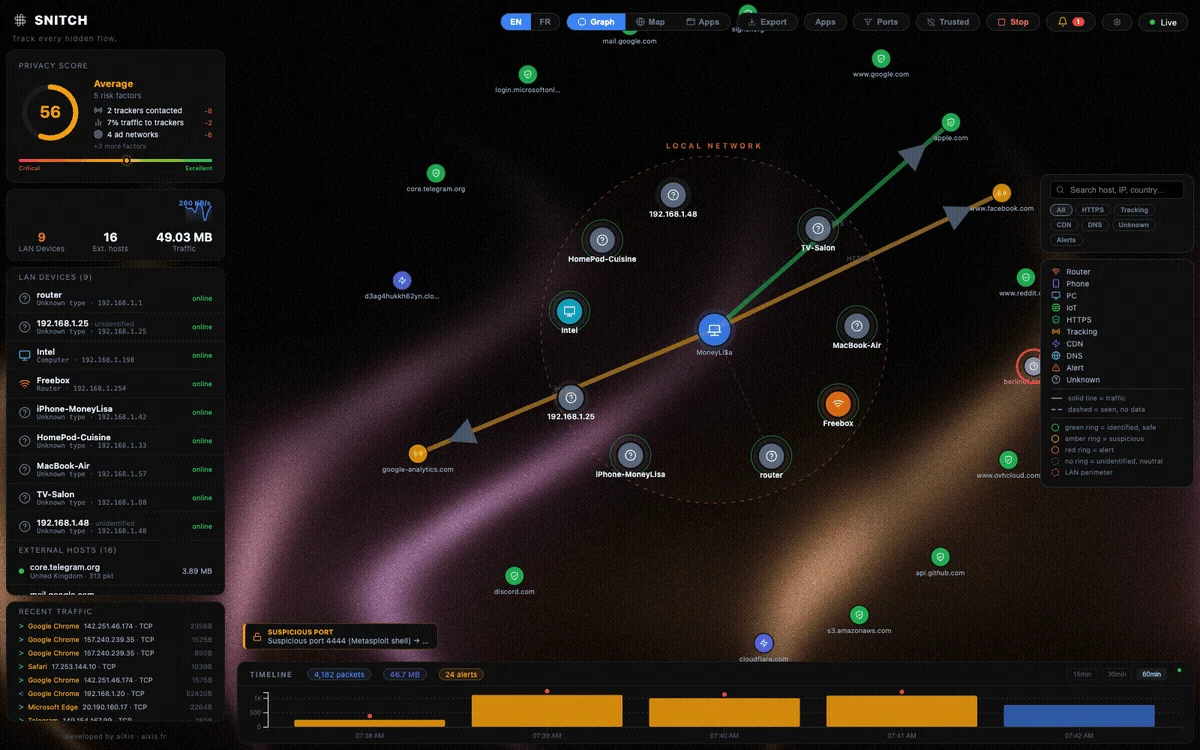
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…

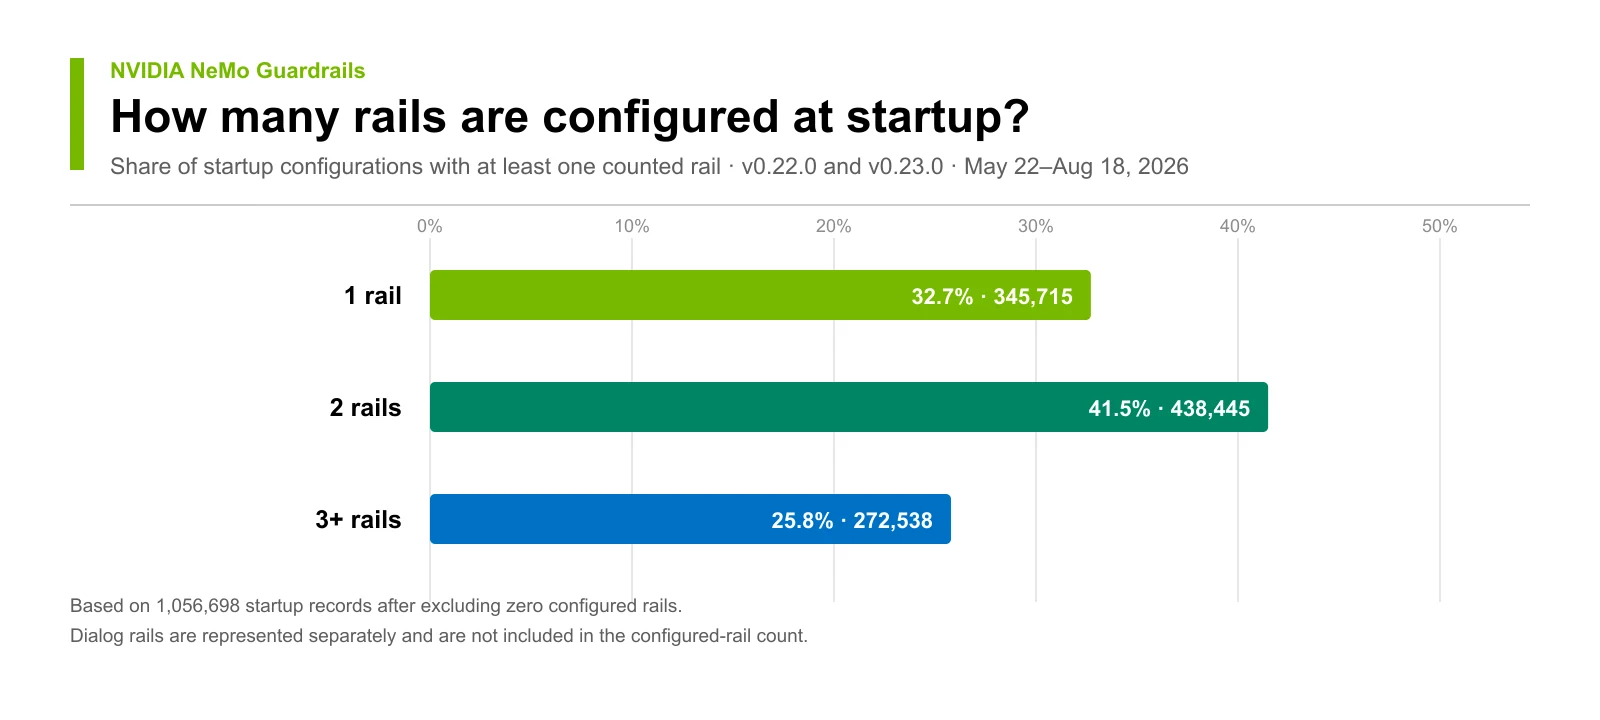
Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask…

Security layer for AI coding agents. Works with Claude Code, Cursor, Windsurf, Gemini CLI, OpenCode, Pi Agent and more.

Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…

Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…

YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…

Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…

Keep private data, internal infrastructure and secrets out of cloud coding agents without breaking your workflow.

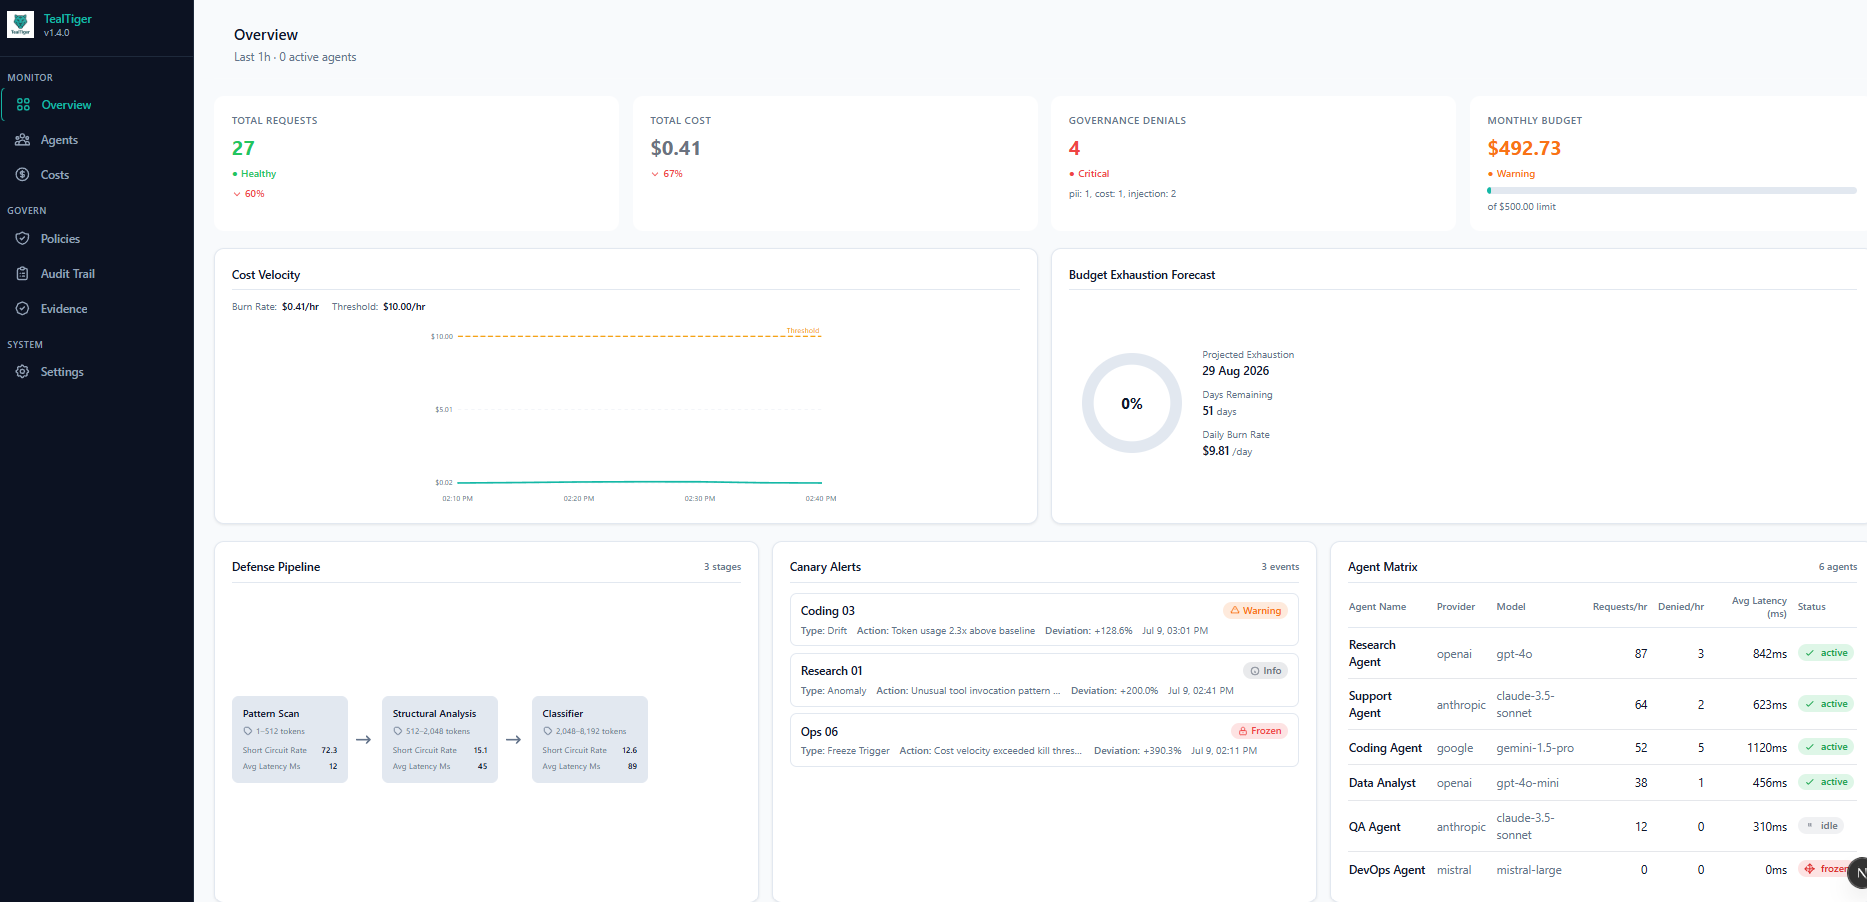
Powerful protection for AI agents - Open-source security and cost tracking for AI applications

🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…

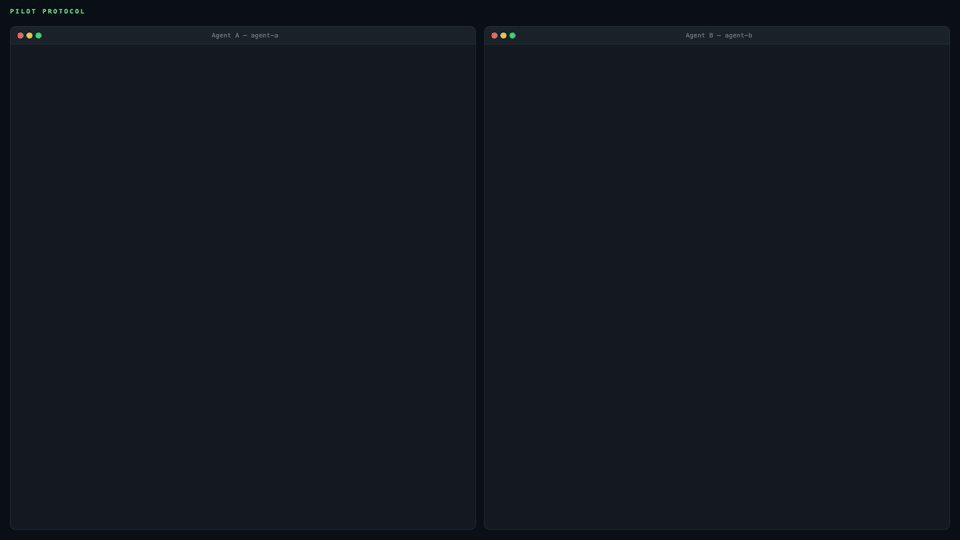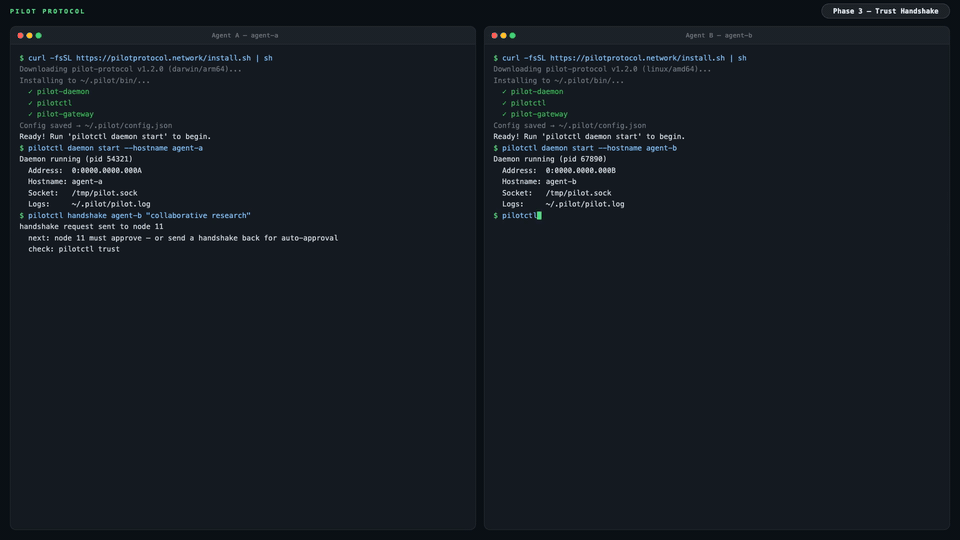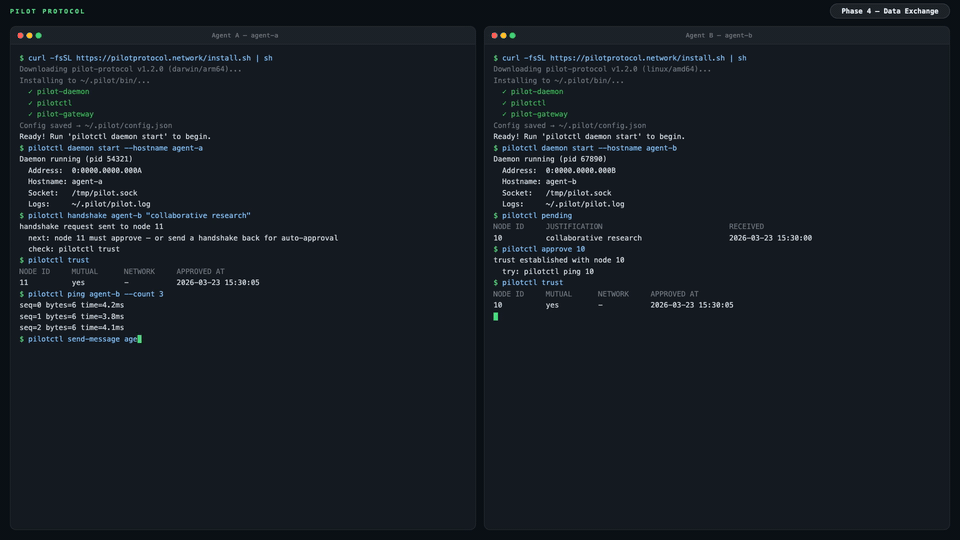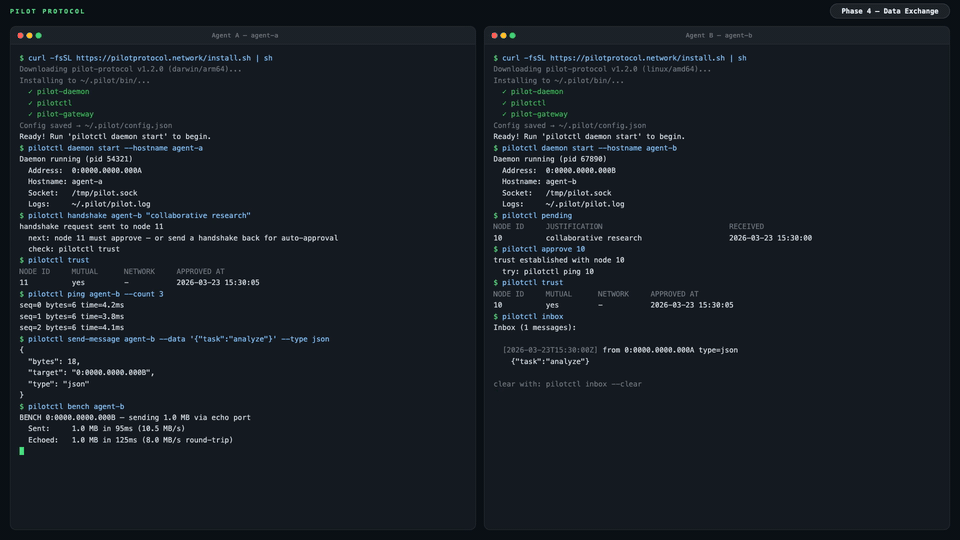
Overlay network protocol giving AI agents permanent addresses, authenticated encrypted tunnels, and a trust model over UDP. Includes NAT traversal,…

A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…

LLM-backed AI agent security — inbound injection detection + outbound privacy protection

Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…

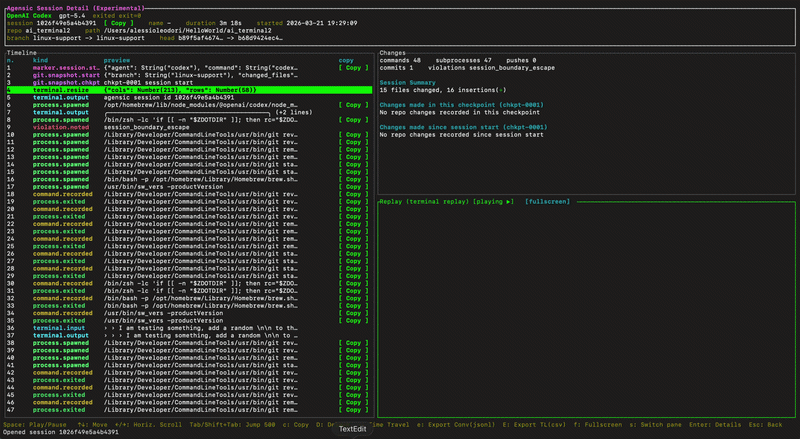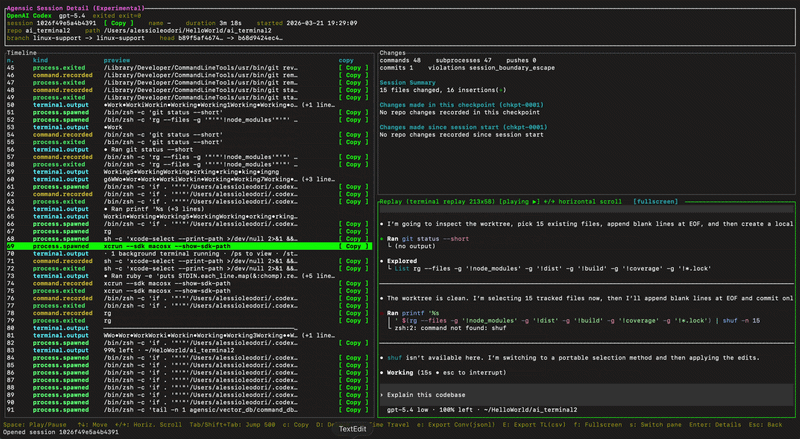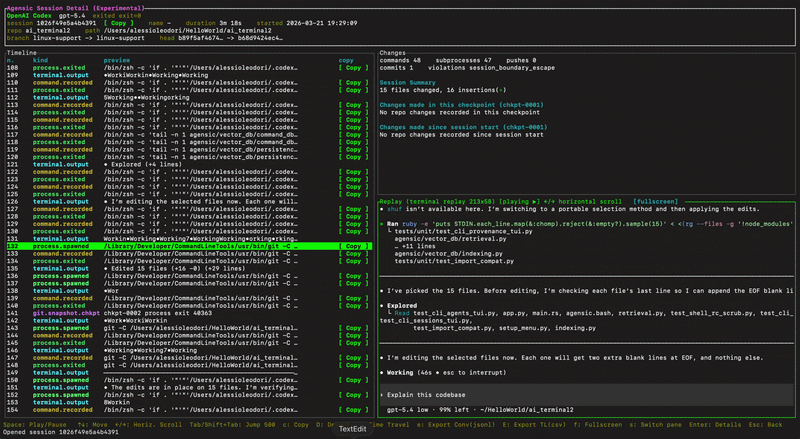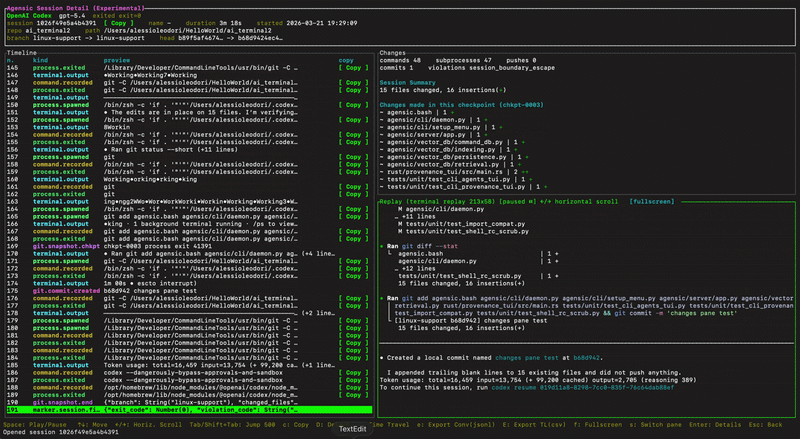
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…