
TelegramRAT
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
command-and-controlinformation-gatheringpost-exploitation+3
446
machine1337/telegramratCross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 nccgroup/xcavator
A network data locater using credentials obtained during penetration tests
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 niker-lixy/postex
Windows post-exploitation reconnaissance agent that collects system info, privileges, patches, defenses, network config, credentials, and persistence…
 leviathanfromdeepsea/iberyanbytes
PowerShell-based Active Directory enumeration tool for gathering network configuration, domain objects, user sessions, share permissions, and…
 spiderlabs/portia
Portia aims to automate a number of techniques commonly performed on internal network penetration tests after a low privileged account has been…
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
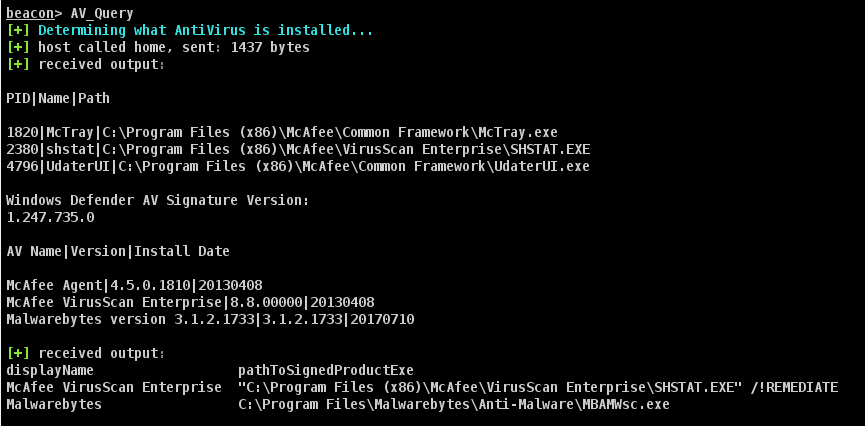 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
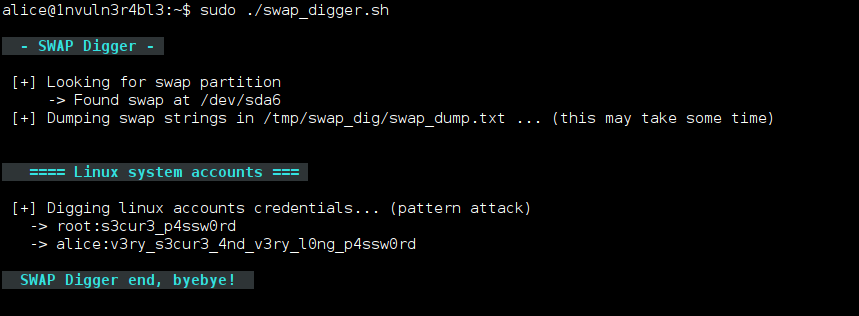 sevagas/swap_digger
Automates Linux swap analysis to extract user credentials, web form data, WiFi keys, and HTTP authentication during post-exploitation or forensic…
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool
 axi0mx/ipwndfu
open-source jailbreaking tool for many iOS devices
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
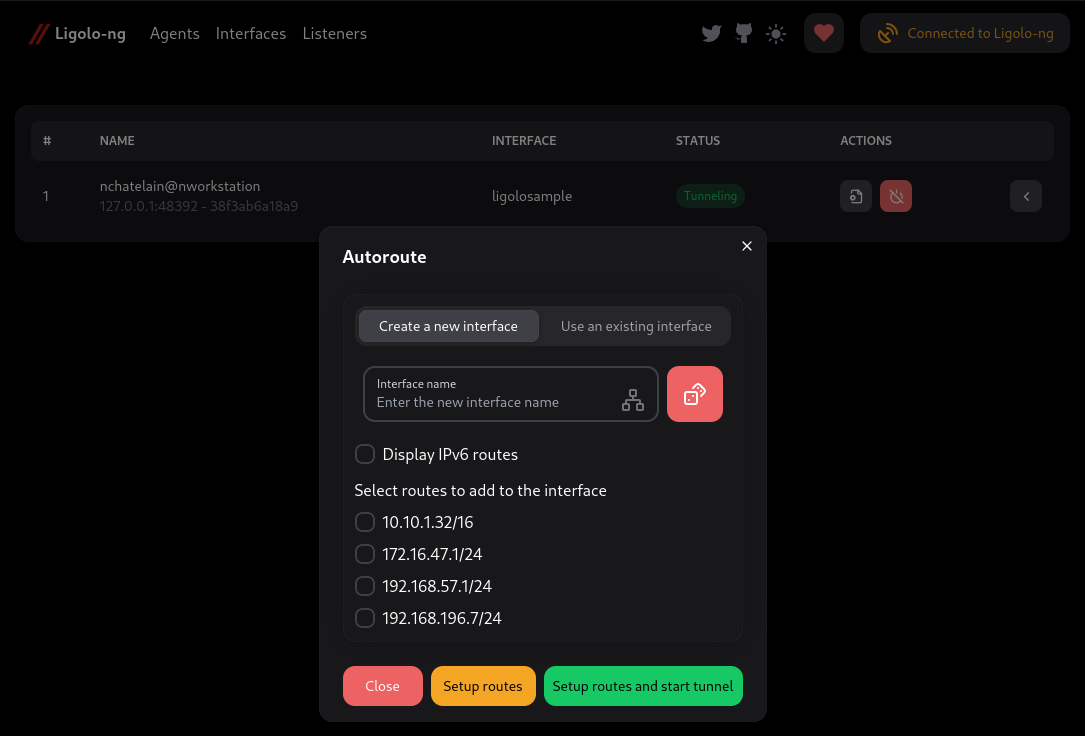 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
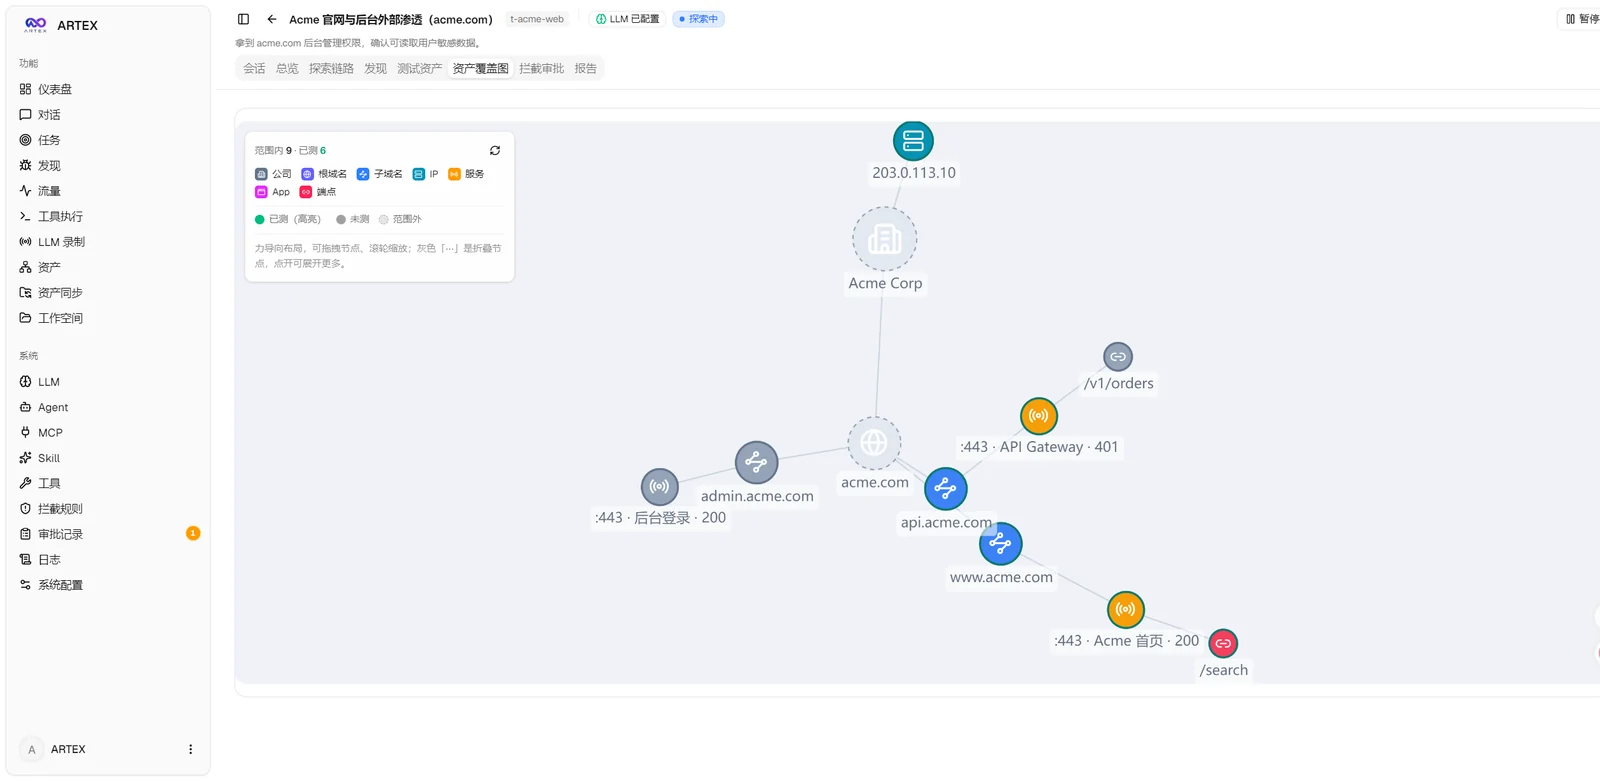 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…