
pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
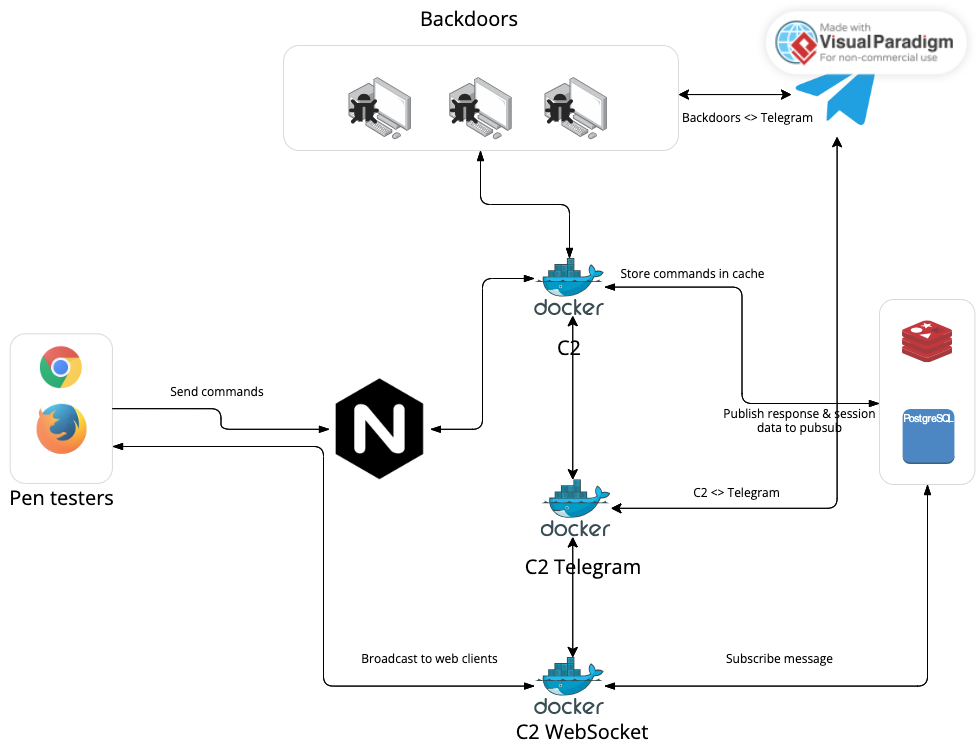 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 schich/lucky-spark
A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
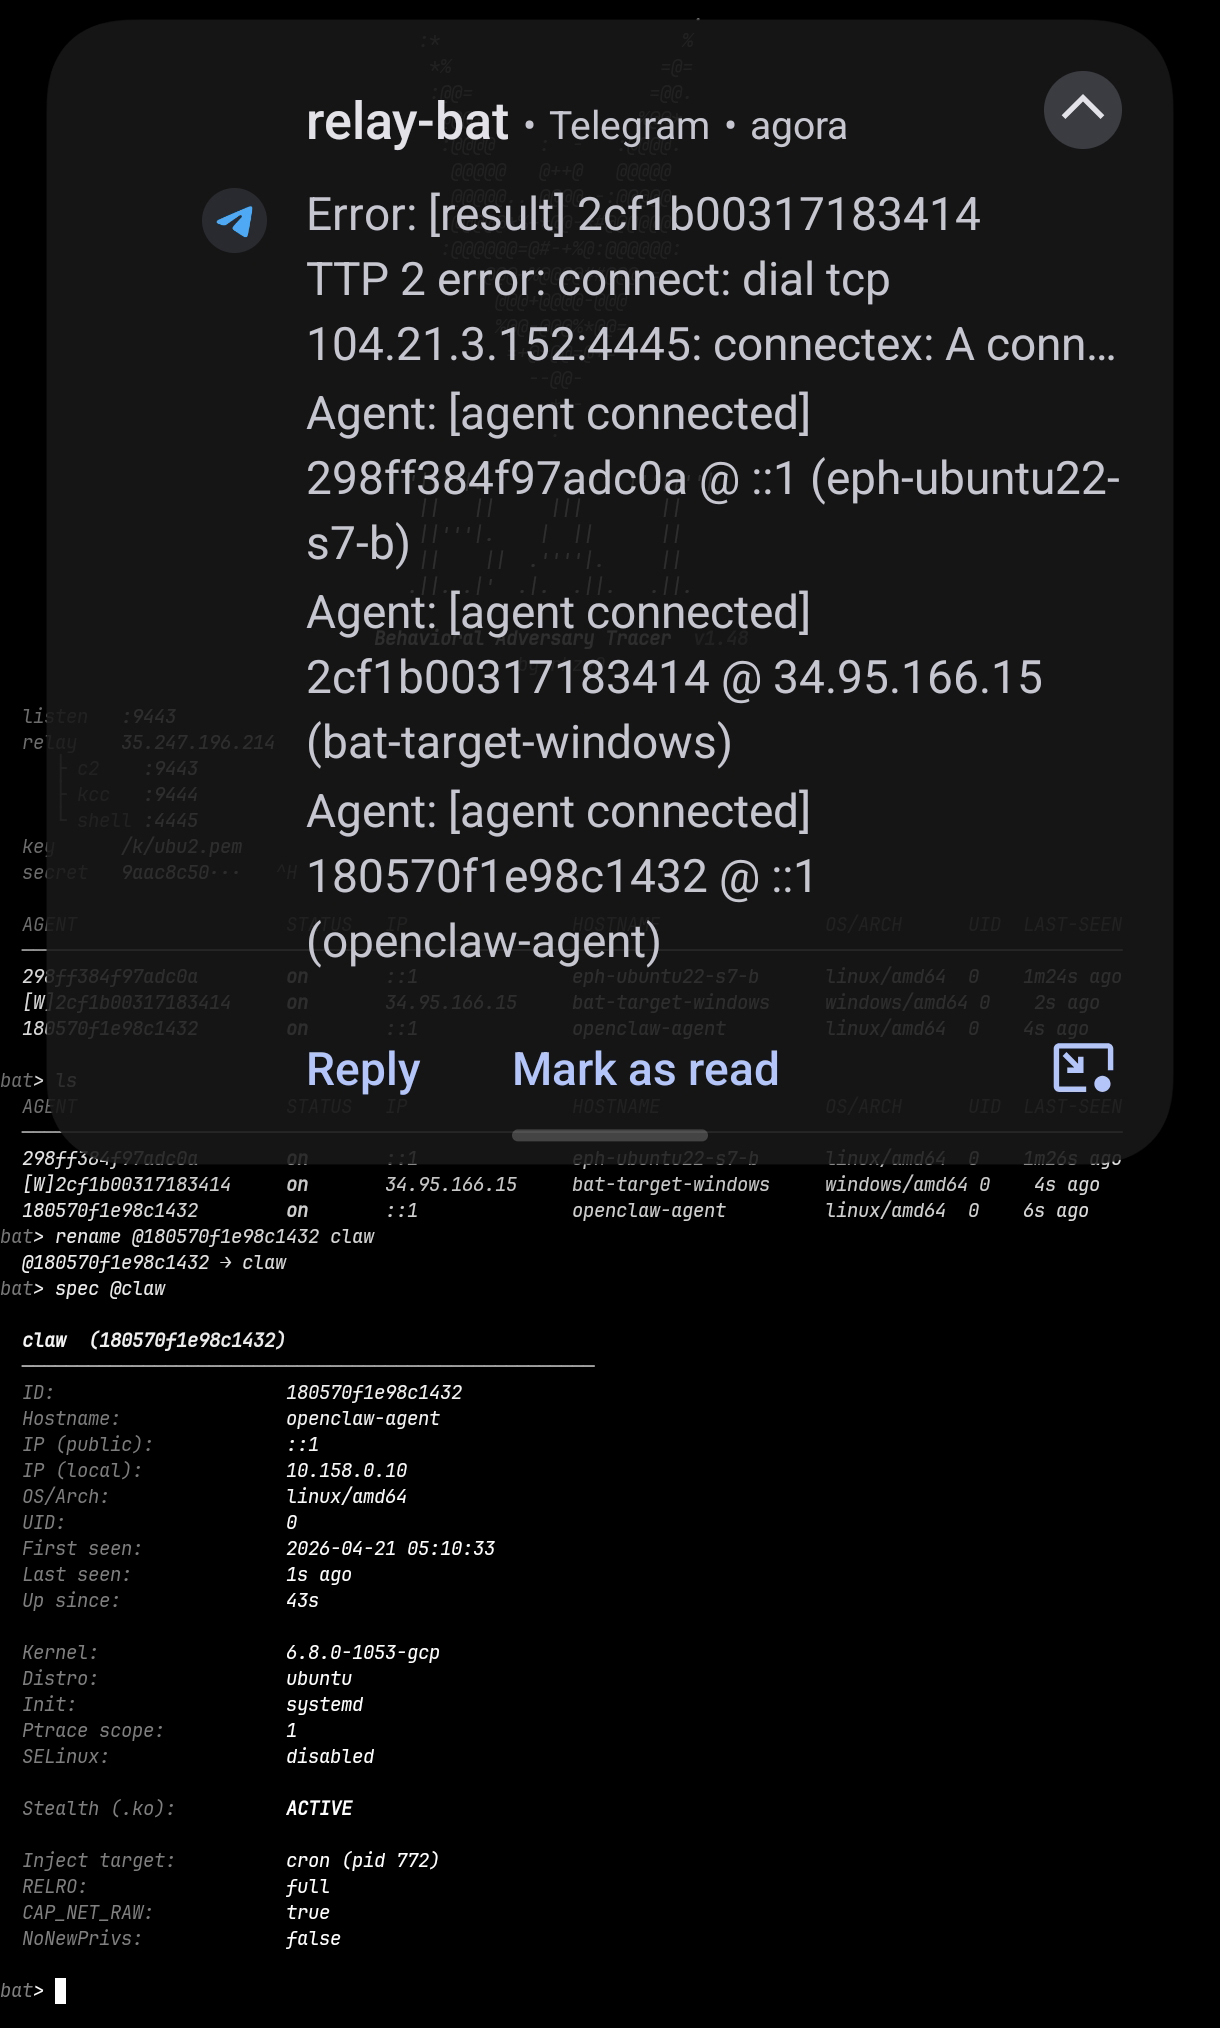 rhzv0/bat
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…
 faizanali8232/cve-exploit-research-development
A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…
 bishopfox/sliver
Adversary Emulation Framework
 ldpreload/blacklotus
BlackLotus UEFI Windows Bootkit
 epinna/weevely3
Weaponized web shell
 joelgmsec/autordpwn
The Shadow Attack Framework
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 hackersatyamrastogi/n8n-exploit-cve-2025-68613-n8n-god-mode-ultimate
n8n God Mode Ultimate - CVE-2025-68613 Scanner v1.0.0 ║ ║ Workflow Automation Remote Code Execution
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques