

teletunnel
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
command-and-controldata-exfiltrationids-ips-evasion+7
43
mhdgning131/teletunnelBypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
 tomiwa-ot/telegram-c2
Control a system remotely via telegram
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
 ricardojoserf/covert-control
Google Drive, OneDrive and Youtube as covert-channels - Control systems remotely by uploading files to Google Drive, OneDrive, Youtube or Telegram
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 xsanflip/begal-c2
Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram
 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks
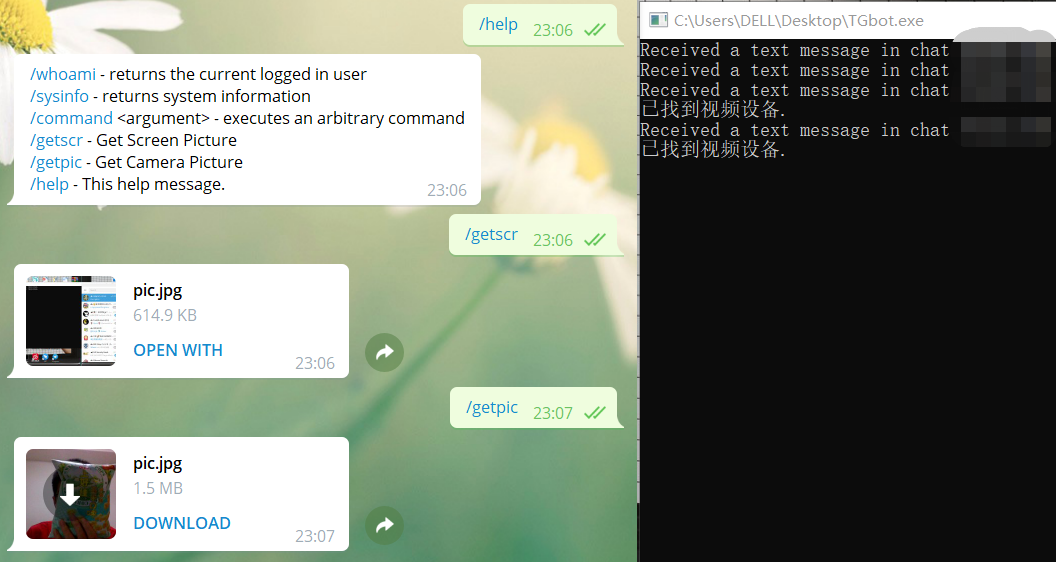 sf197/telegra_csharp_c2
Command and Control for C# Writing
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server