

hayduk
 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
exploit-frameworksnetwork-mappingpenetration-testing-frameworks+3
10
jolovicdev/haydukGraphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 kingofthenops/cookie-monster
BOF-based tool to extract browser cookies and credentials from Chrome, Edge, and Firefox via handle duplication and fileless download, with offline…
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
 0x09al/browser-c2
Post Exploitation agent which uses a browser to do C2 operations.
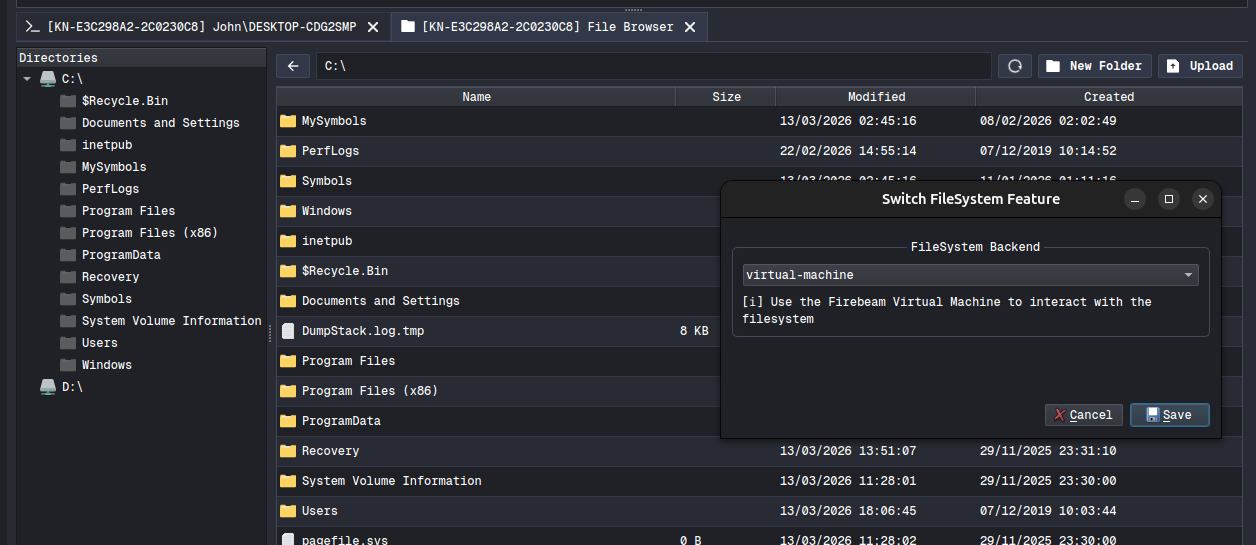 infinitycurvelabs/vm-filesystem
Filesystem interaction via firebeam virtual machine execution
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
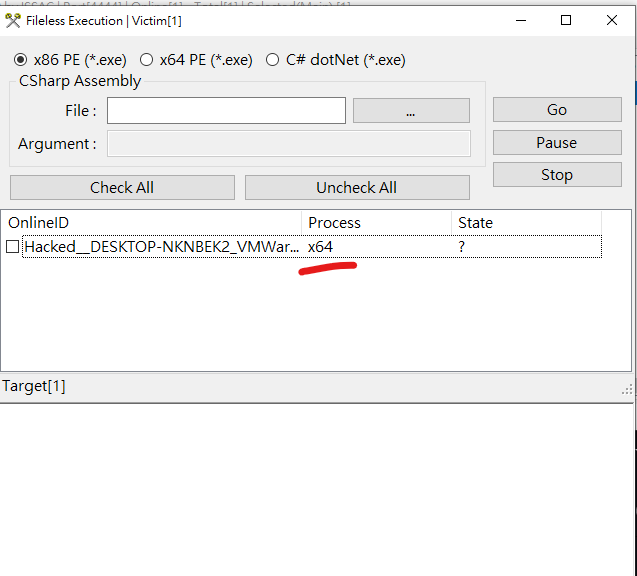 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 powershellempire/powertools
Collection of offensive PowerShell projects for reconnaissance, privilege escalation, and post-exploitation during penetration testing engagements.
 entysec/hatsploit
Modular penetration testing platform that enables you to write, test, and execute exploit code.
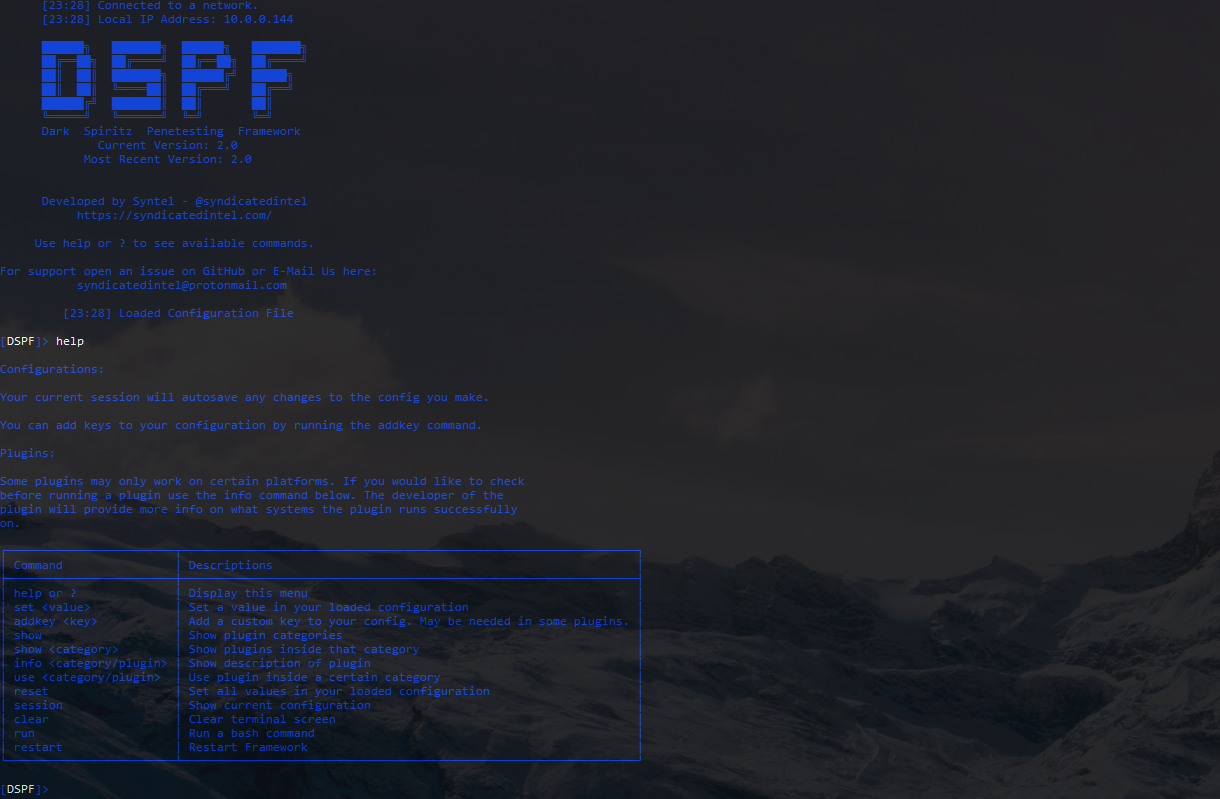 m4cs/darkspiritz
🌔 Official Repository for DarkSpiritz Penetration Framework | Written in Python 🐍
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
 viralmaniar/peekaboo
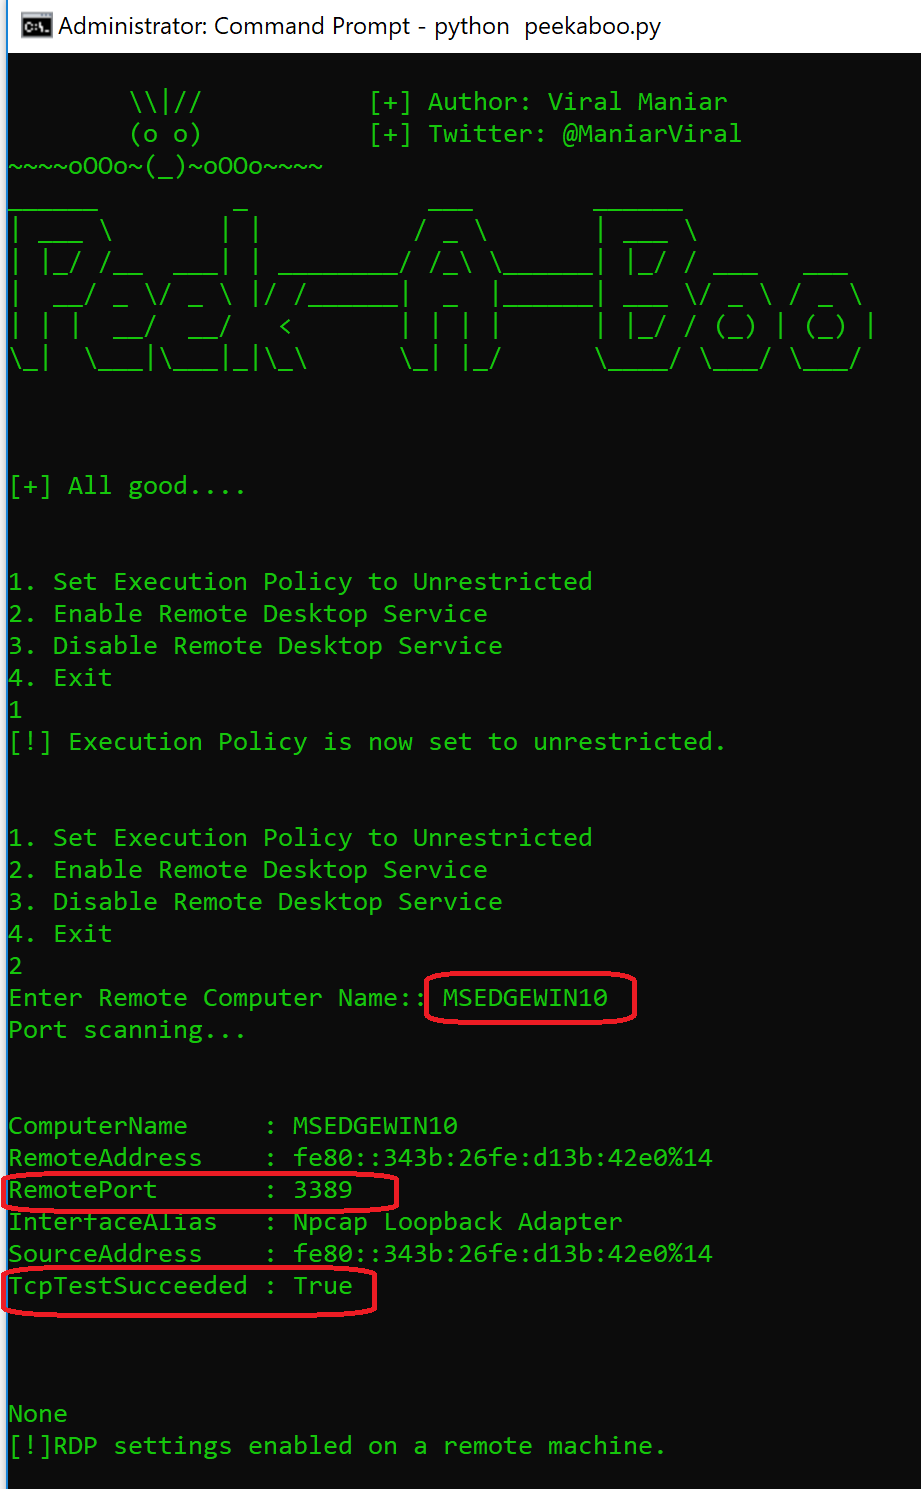
PeekABoo tool can be used during internal penetration testing when a user needs to enable Remote Desktop on the targeted machine. It uses PowerShell…
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers