
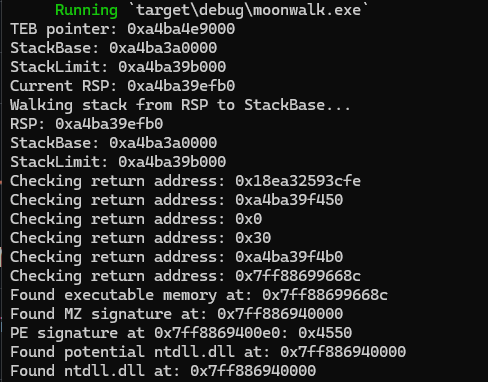
moonwalk
 teach2breach/moonwalk
find dll base addresses without PEB WALK
binary-analysiseducationpayload-development+2
teach2breach/moonwalkfind dll base addresses without PEB WALK
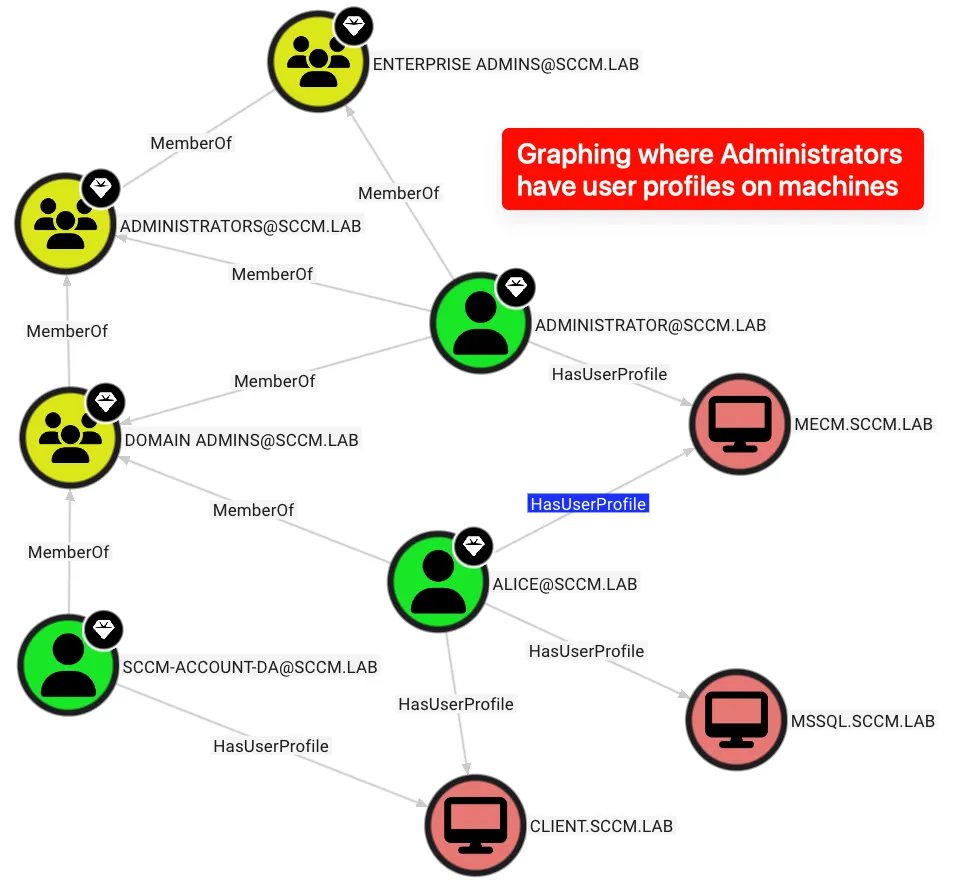 m4lwhere/profilehound
ProfileHound - BloodHound OpenGraph collector for user profiles stored on domain machines. Make informed decisions about looting secrets by…
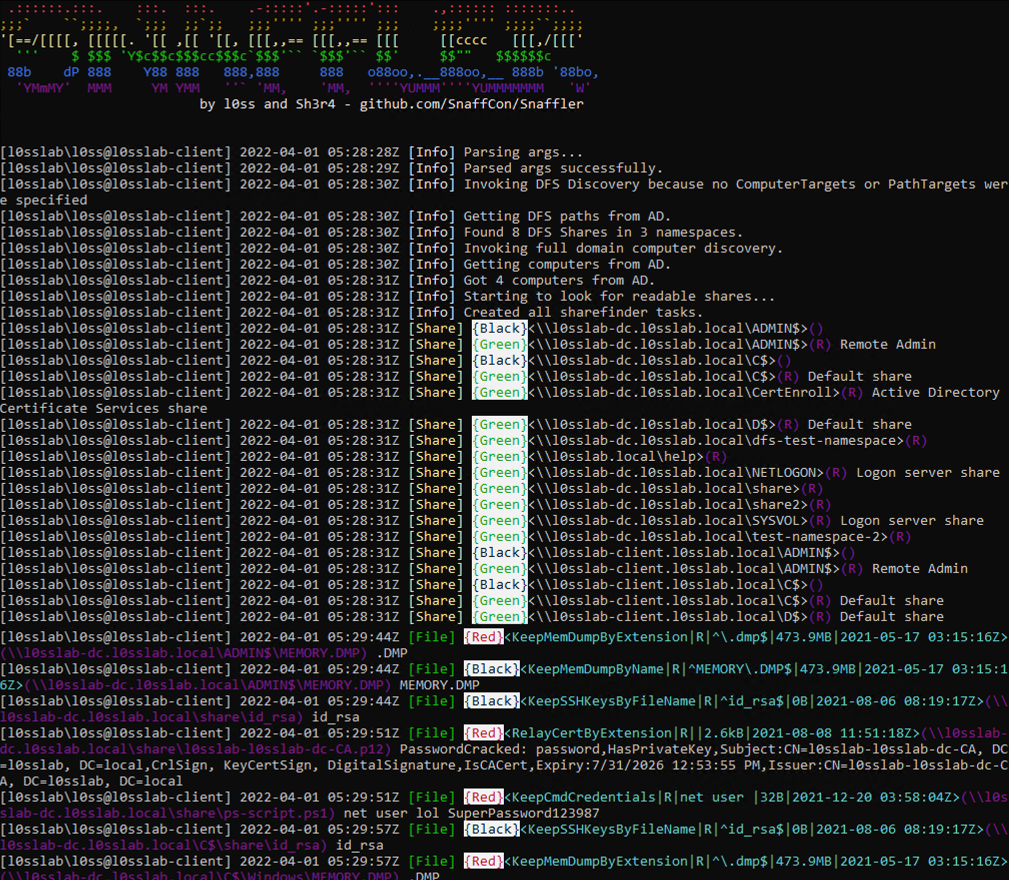 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
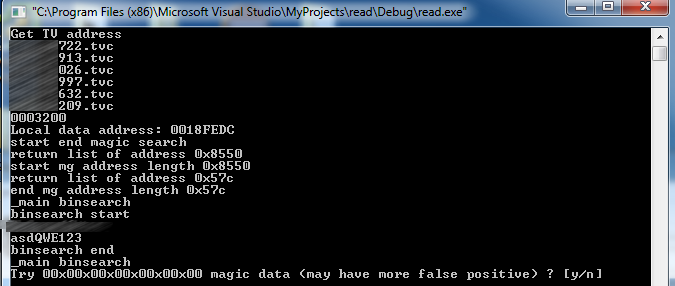 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 fortra/nanodump
The swiss army knife of LSASS dumping
 gabriellandau/edrsandblast-godfault
EDRSandblast-GodFault