
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
113 results
Lilith preview

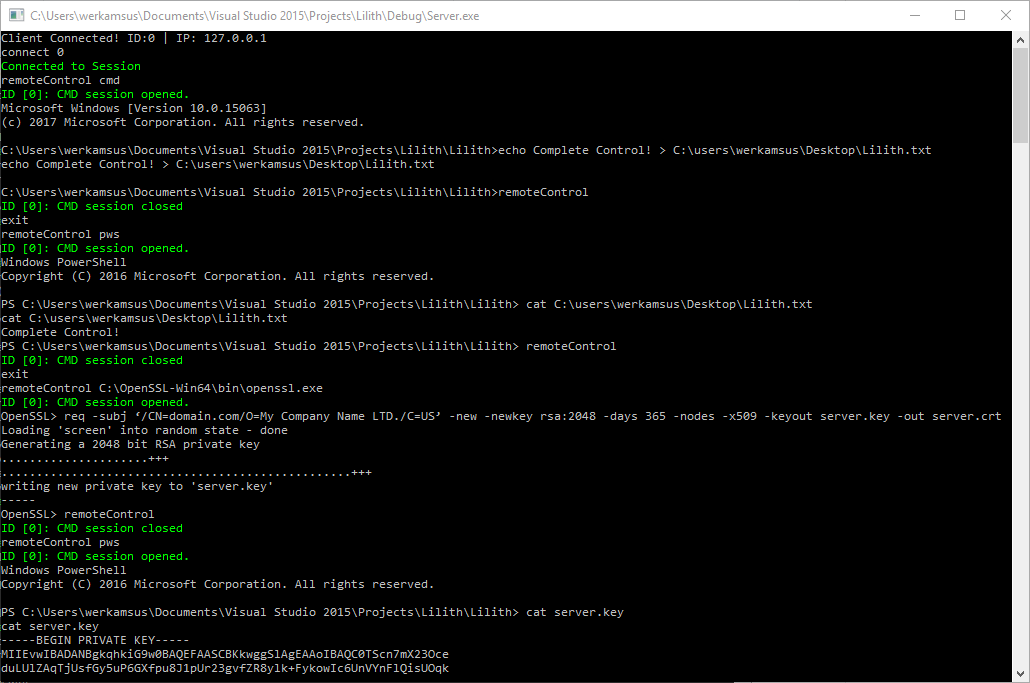
Lilith

GitHubwerkamsus/lilith

Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++

command-and-controlpayload-generationpenetration-testing+4
750
6 years ago
defcon33_silence_kill_edr preview

defcon33_silence_kill_edr

GitHubarosenmund/defcon33_silence_kill_edr

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

adversarial-attackeducationlabs-practice+6
3491 year ago
exploitation-course preview

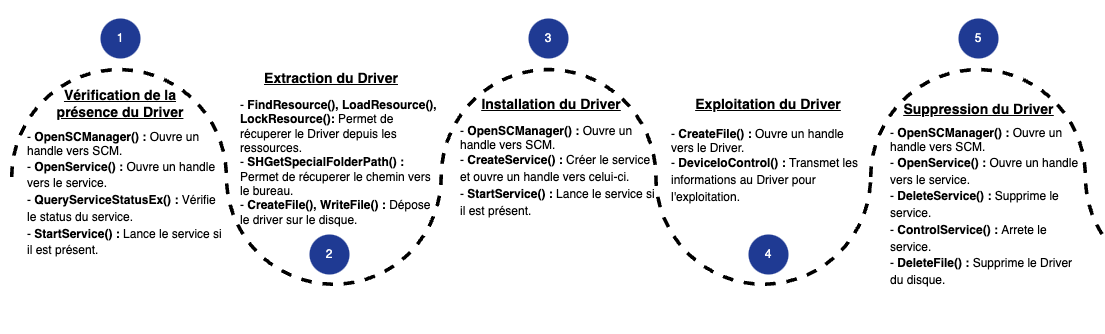
exploitation-course

GitHubashemery/exploitation-course

Offensive Software Exploitation Course
binary-exploitationeducationexploitation+7
2.5k3 years ago
BYOVD-DriverKiller preview

BYOVD-DriverKiller

GitHubalex3o/byovd-driverkiller

Driver Reverse & Exploitation

binary-analysiseducationexploitation+3
831 year ago
CVE-2016-2067 preview

CVE-2016-2067

GitHubhhj4ck/cve-2016-2067

GPU IOMMU DMA exploit for Android devices that overwrites vdso.so with shellcode to escalate privileges and spawn a reverse root shell on Nexus 6p.
android-securitybinary-exploitationexploitation+5
75 years ago
CyberStrikeAI preview

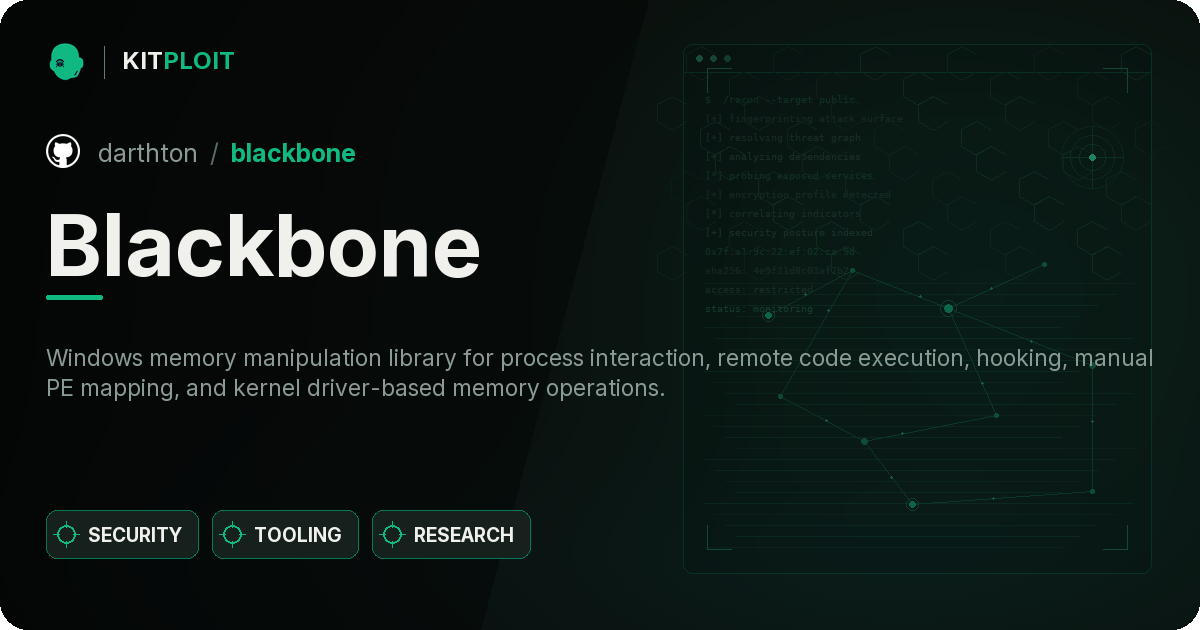
CyberStrikeAI

GitHubed1s0nz/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
6.6k1 day ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
Ghost preview

Ghost

GitHubentysec/ghost

Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
android-securityexploitationpenetration-testing+2
3.4k10 months ago
PowerShell-Suite preview

PowerShell-Suite

GitHubfuzzysecurity/powershell-suite

My musings with PowerShell
binary-analysisdebuggersforensics+5
2.7k4 years ago
androrat preview

androrat

GitHubdesignativedave/androrat

Remote Administration Tool for Android devices

android-securitycommand-and-controldata-exfiltration+9
1.6k13 years ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
binary-analysiscurated-resourcesids-ips-evasion+3
2.2k5 months ago
the-backdoor-factory preview

the-backdoor-factory

GitHubsecretsquirrel/the-backdoor-factory

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
binary-exploitationexploitationmalware-analysis+6
3.4k2 years ago
OffensiveCSharp preview

OffensiveCSharp

GitHubmatterpreter/offensivecsharp

Collection of Offensive C# Tooling
binary-analysiscode-analysisexploitation+7
1.5k3 years ago
COFFLoader preview

COFFLoader

GitHubtrustedsec/coffloader

Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
binary-analysispayload-developmentpenetration-testing+2
6524 days ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHub7etsuo/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
binary-analysiscurated-resourcesmalware-analysis+3
1.5k1 year ago
Win32_Offensive_Cheatsheet preview

Win32_Offensive_Cheatsheet

GitHubmatthieu-hackwitharts/win32_offensive_cheatsheet

Win32 and Kernel abusing techniques for pentesters

binary-analysiscurated-resourceseducation+8
9823 years ago
DarkWidow preview

DarkWidow

GitHubreveng007/darkwidow

Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
binary-analysiseducationexploitation+6
8137 months ago
BetterAndroRAT preview

BetterAndroRAT

GitHubmwsrc/betterandrorat

Android Remote Access Trojan

android-securitycommand-and-controldata-exfiltration+8
5459 years ago
Previous1234567Next