
SharpZipRunner
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
exploitationpayload-developmentpayload-generation+3
jfmaes/sharpziprunnerExecutes position independent shellcode from an encrypted zip
 blacksnufkin/ghostdriver
yet another AV killer tool using BYOVD
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
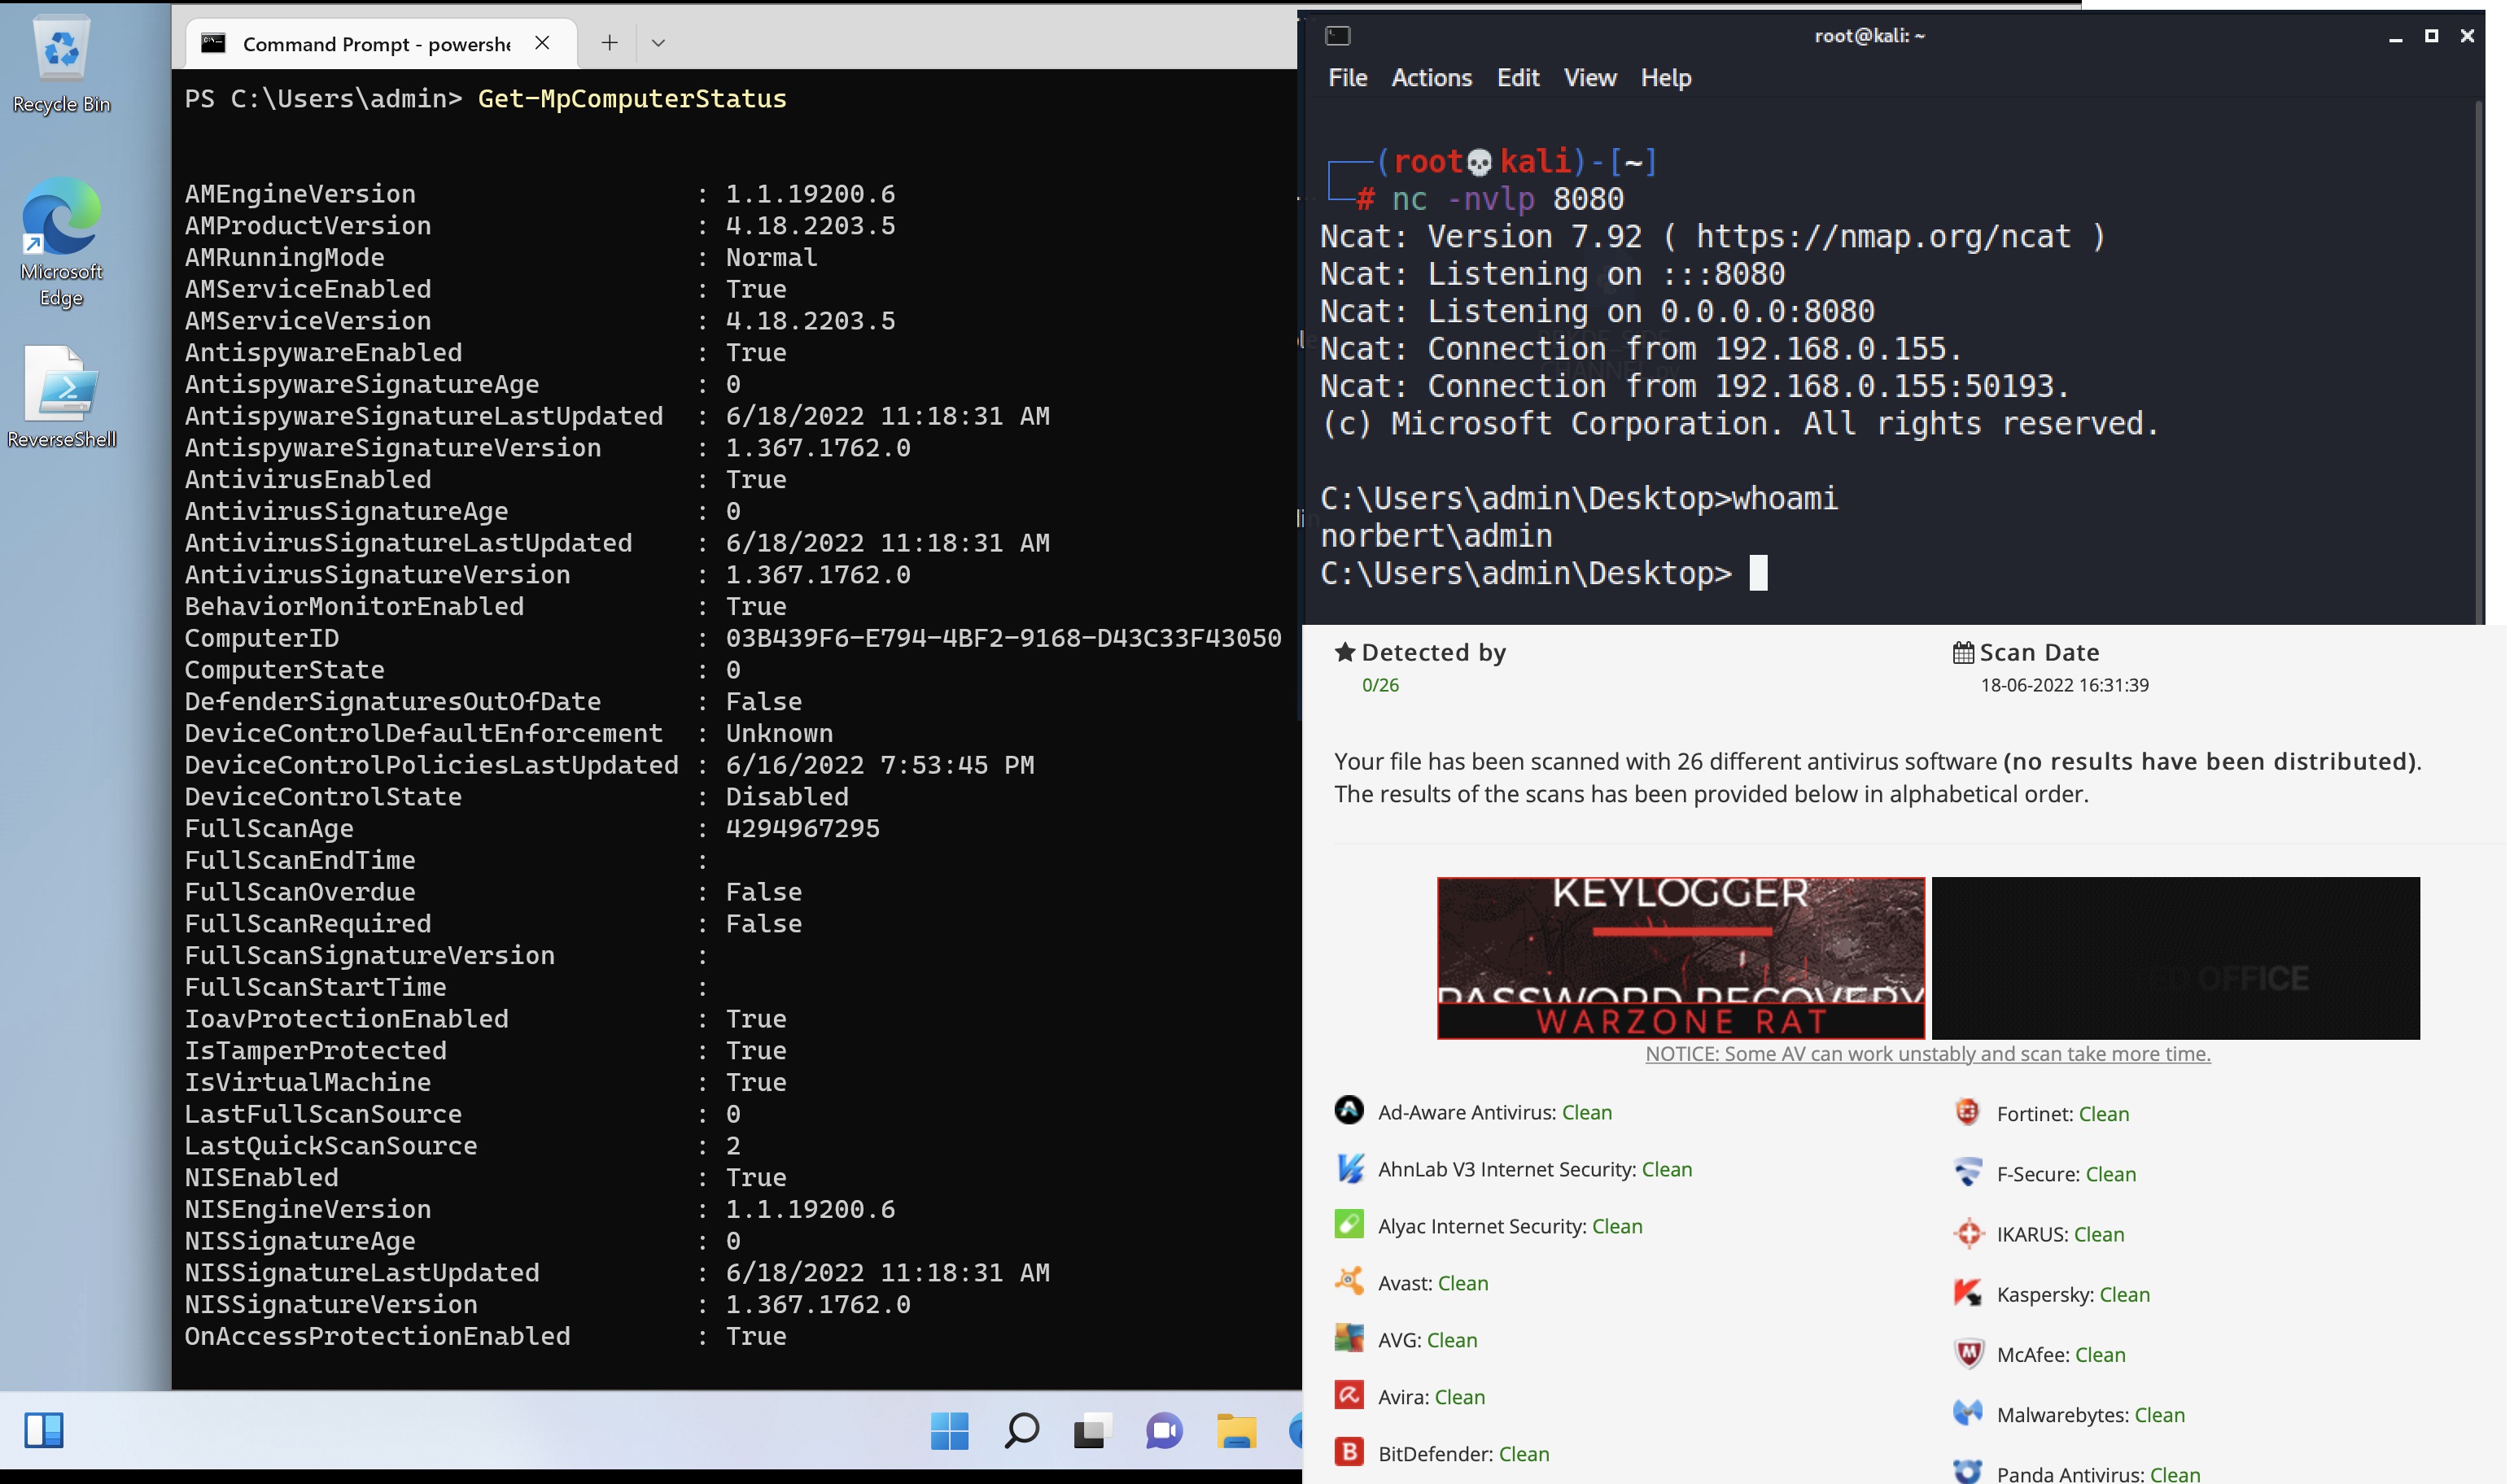 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
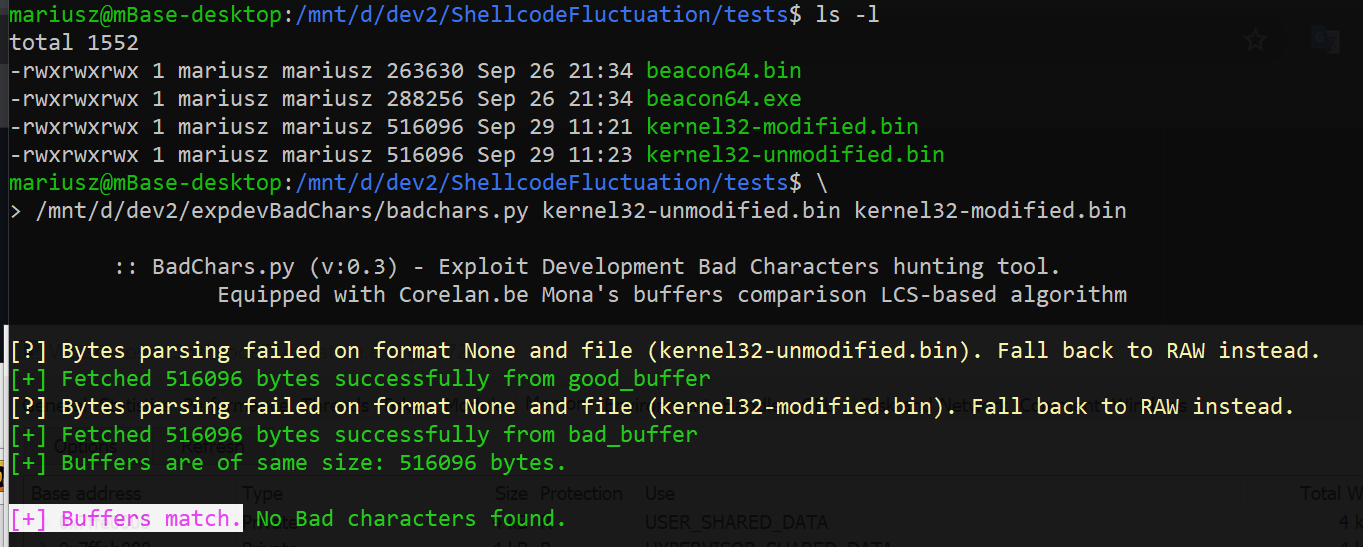 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
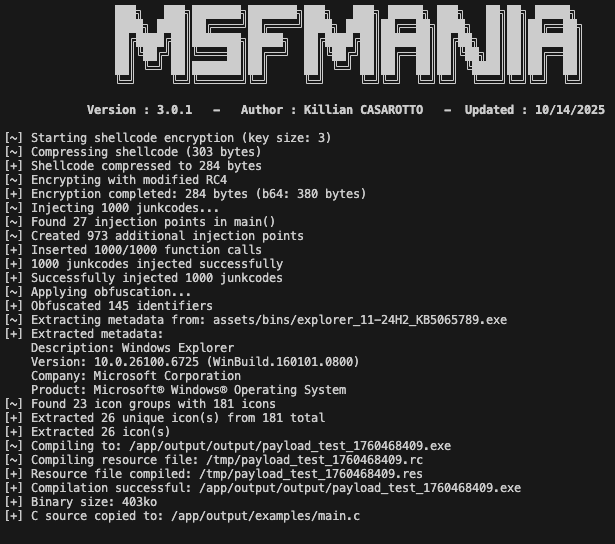 lepotekil/msfmania
Python AV Evasion Tools
 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 leviathanfromdeepsea/iberyanbytes
PowerShell-based Active Directory enumeration tool for gathering network configuration, domain objects, user sessions, share permissions, and…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 tennc/webshell
This is a webshell open source project
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 cracked5pider/stardust
A modern 32/64-bit position independent implant template